> ## Documentation Index
> Fetch the complete documentation index at: https://cloud-architect.ipoint-labs.com/llms.txt
> Use this file to discover all available pages before exploring further.
# Challenge - How to Encrypt an S3 bucket using AWS KMS and monitor the activities with CloudTrail
> Hands-on lab · 30m
Launch this lab in the IP Lab Portal, then follow the steps below in the AWS console.
Open IP Lab Portal
## Overview
#### Prerequisites
1. Good knowledge of AWS service
* S3
* KMS
* CloudTrail
2. Laptop/Desktop
3. Internet Browser
4. Internet connection
#### Challenge Instructions
1. **Region :** Make Sure To Use **Us-East-1** Region To Create All The Resources.
2. You Will Be Provided With The Requirements Of The Challenge. If You Are New To AWS Cloud, We Recommend You Go Through Our Hands-On Labs Before Taking This Challenge.
3. **Challenge Duration:** 90 Min
#### How to submit the challenge
1. After Building The Infrastructure, Click On The **Validation** Button, To Validate If You Have Built The Required Infrastructure And Completed The Challenge Successfully.
2. Validation Status:
* **Success** - You Have Completed The Challenge Successfully.
* **Failed** - You Have Failed To Complete The Challenge.
3. Once You Have Successfully Validated The Challenge, Click On **End Lab** Button To End The Challenge.
#### Launching Challenge Environment
1. To Launch The Challenge Environment, Click On The **Start Challenge** Button.
2. Please Wait Until The Cloud Environment Is Provisioned. It Will Take Less Than A Minute To Provision.
3. Once The Challenge Is Started, You Will Be Provided With **IAM User Name, Password, Access Key,** and **Secret Access Key**.
> **Note :** You Can Only Start One Challenge At Any Given Time
## Lab guide
#### Sign in to AWS Management Console
1. Click On The **Open Console** Button, And You Will Get Redirected To AWS Console In A New Browser Tab.
2. On The AWS Sign-In Page, Leave The Account ID As Default. Never Edit/Remove The 12 Digit Account ID Present In The AWS Console. Otherwise, You Cannot Proceed With The Challenge.
3. Now Copy Your **User Name** and **Password** In The Lab Console To The **IAM Username and Password** In AWS Console And Click On The **Sign In** Button.
4. Once Signed In To The AWS Management Console, Make The Default AWS Region As **US East (N. Virginia) Us-East-1**.
#### Cloud Challenge Details
In This Challenge, Your AWS Compute Skills Are Put To The Test. You'll Be Given A Requirement And You Have To Reach It Using Your Knowledge Of S3, KMS and CloudTrail. Which Will Be Used In This Challenge. This Challenge Will Help You Understand The Real-Time Scenarios.
#### Architecture Diagram
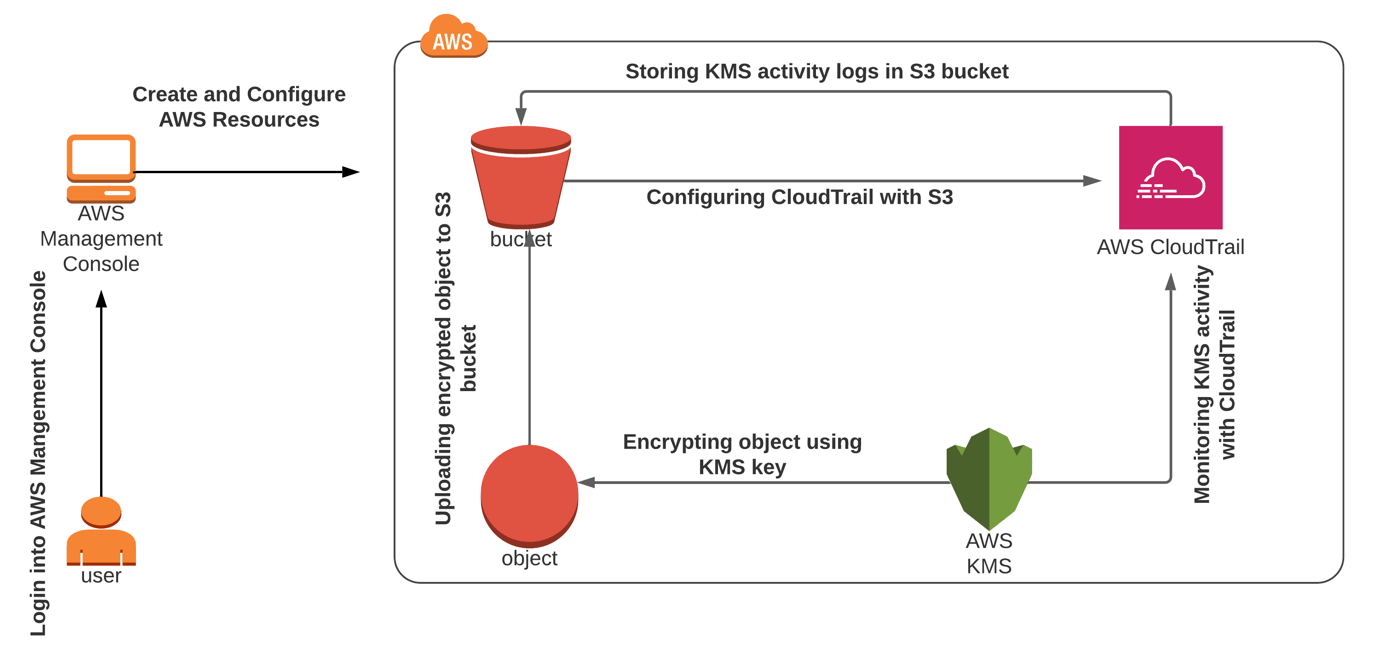 **A XYZ company, a leading cloud-based services provider, is committed to ensuring the security and integrity of its data stored on the AWS cloud platform. As part of their ongoing efforts to enhance data security, XYZ Corporation has decided to implement robust encryption mechanisms for their sensitive data stored in Amazon S3 buckets. Additionally, they aim to monitor and track any encryption-related activities for compliance and auditing purposes. Your task is to architect and implement a secure data encryption solution using AWS Key Management Service (KMS) and monitor Key Management Service (KMS) activity using AWS CloudTrail logs.**
1. Create a customer-managed KMS key with the following settings:
* Key type: **Symmetric**
* Key usage: **Encrypt and Decrypt**
2. Create an S3 bucket with the following settings:
* Object ownership: **ACLs enabled, Object writer as the Object owner**
3. Create a CloudTrail trail with the following settings:
* Trail name: **whiz-kms-trails**
* Storage location: Select existing S3 bucket
* Log file SSE-KMS encryption: Unchecked
* Event type: Management events (Read and Write), Data events (Read and Write for specific S3 bucket)
4. Upload an object to the S3 bucket.
5. Encrypt the object using the KMS key (whiz-kms-key) created earlier.
6. Attempt to access the encrypted object and troubleshoot access issues.
7. Analyze CloudTrail logs in the S3 bucket related to KMS encryption operations.
8. Click On The **Validate** To Complete The Challenge.
#### End Challenge
1. Sign Out Of The AWS Account.
2. You Have Successfully Completed The Challenge.
3. Click On **End Challenge** Button From IP Lab Portal Labs Console And Wait Till The Process Gets Completed.
## What gets checked
When you press **Check my work**, the platform verifies each of these:
* **Check Cloudtrail logs** — Check whether cloudtrail log is created or not
* **Create KMS Customer Managed Key** — Check whether Customer managed key created or not
* **Create Public AWS S3 Bucket** — Check whether a Public S3 Bucket created or not
## Related help
* [FAQs and Troubleshooting](/aws-saa/support/faqs-and-troubleshooting)
This documentation is built and hosted on [Mintlify](https://mintlify.com), a developer documentation platform.