> ## Documentation Index
> Fetch the complete documentation index at: https://cloud-architect.ipoint-labs.com/llms.txt
> Use this file to discover all available pages before exploring further.
# Peer VPC with Transit Gateway and its components using Terraform
> Hands-on lab · 45m
Launch this lab in the IP Lab Portal, then follow the steps below in the AWS console.
Open IP Lab Portal
## Overview
### Lab Details
1. This lab walks you through how to peer VPC with Transit Gateway using terraform. You will be creating 2 VPC with a public and private subnet. Launch EC2 Instances in both of the VPC and establish peering between them.
2. You will be using the Transit gateway attachment to add VPC and add the entry in the route table. Then you will use SSH into the private EC2 from the public EC2 instance.
3. Duration: **45 minutes**
4. AWS Region: **US East (N. Virginia) us-east-1.**
### Introduction
#### What is a Transit gateway?
* The AWS Transit Gateway helps you connect multiple VPCs and on-premises networks through a central hub. It simplifies your network with VPCs and on-premises connections and solves the problem of complex peering relationships.
* With VPC peering using the Transit gateway, your data is always encrypted and no longer uses the public internet for communication.
* Benefits of using Transit gateway:
* Easy to connect
* Full control
* Greater security
* Multicast feature
* Reasons to use Transit gateway over VPC peering:
* VPC peering does not support transitive peering, meaning you can only peer two VPC at a time.
* To peer your VPC with an on-premise network, you can not use VPC peering. Transit gateway supports connecting on-premise networks.
* Transit gateway limits:
* Per transit gateway, you can have 20 transit gateway route tables.
* Per transit gateway, you can have 10000 routes.
* Per transit gateway, there can be 50 transit gateway attachments.
* Per VPC, you can have 5 unique transit gateways.
#### How Transit gateway can help you simplify your network?
* Transit Gateway acts as a cloud router that supports connecting with the following resources:
* Amazon VPC
* VPN Connection having Customer Gateway
* AWS Direct Connect Gateway
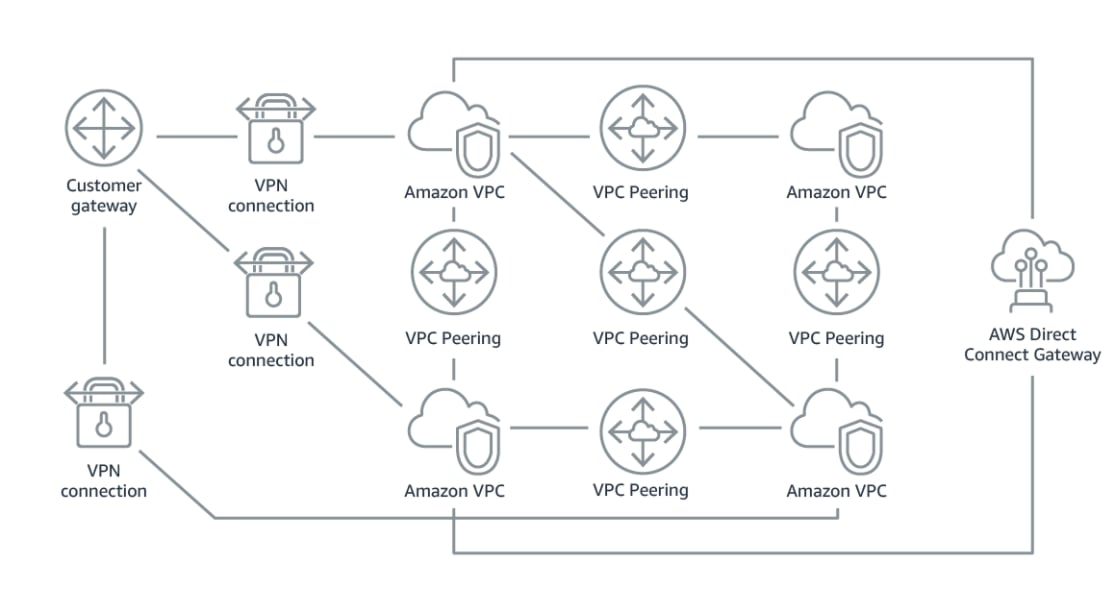
##### Without Transit Gateway:
* VPC peering can have only one-to-one relationship between two VPCs. The complexity increases as you scale the number of connections.
* Maintenance of the route table is another big challenge when you are scaling, you must keep the route table having routes to VPC and connection with the on-premise network using a separate network gateway for each new connection.
 ##### With Transit Gateway:
* To interconnect Amazon VPC with an on-premise network, we can use Transit Gateway.
* The network is standardized and easily scalable. With Transit Gateway, you have one place to manage and monitor the number of active connections for each network.
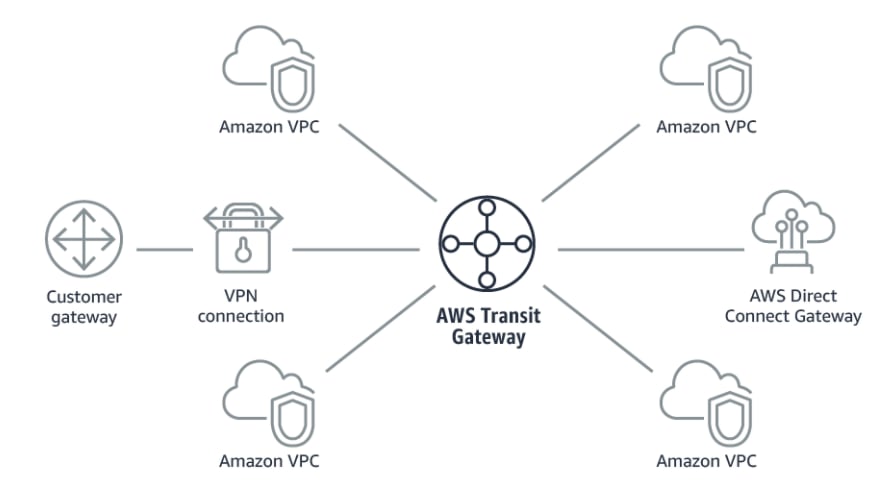 * Since connecting to an on-premise network is not possible virtually, In this lab, you will learn how to create a Transit gateway and use it to peer VPC.
#### Transit gateway use cases
* Applications can be delivered around the world.
* Move your network design from Multi-AZ to Multi-region.
* Scale quickly and respond to spikes in traffic smoothly.
* Connect to all types of networks in one place.
### Task Details
1. Sign into the AWS Management Console.
2. Setup Visual Studio Code
3. Create a Variable file
4. Create the key pair from EC2 Console
5. Create the First VPC in main.tf file
6. Create a Public subnet in First VPC
7. Create Internet Gateway and Route Table
8. Create a Security group for EC2 in main.tf file
9. Launch an EC2 instance in the First VPC
10. Create a Second VPC
11. Create a Private subnet in Second VPC
12. Create a Security Group for Second VPC
13. Launch an EC2 instance in the Second VPC
14. Create a Transit Gateway
15. Create two Transit gateway attachment for VPCs created
16. Add the routes in the route table
17. Create Output File
18. Confirm the installation of Terraform by checking the version
19. Apply terraform configurations
20. Test the connectivity between two VPCs
21. Delete AWS Resources
### Launching Lab Environment
1. To launch the lab environment, Click on the **Start Lab** button.
2. Please wait until the cloud environment is provisioned. It will take less than a minute to provision.
3. Once the Lab is started, you will be provided with **IAM username**, **Password**, **Access** **Key**, and **Secret** **Access** **Key**.
> **Note** : You can only start one lab at any given time
## Lab guide
#### Lab Steps
#### Task 1: Sign in to AWS Management Console
1. Click on the **Open Console** button, and you will get redirected to AWS Console in a new browser tab and it will be Logged in Successfully.
2. On the AWS Console, in the search bar search for **IAM** and click on it.
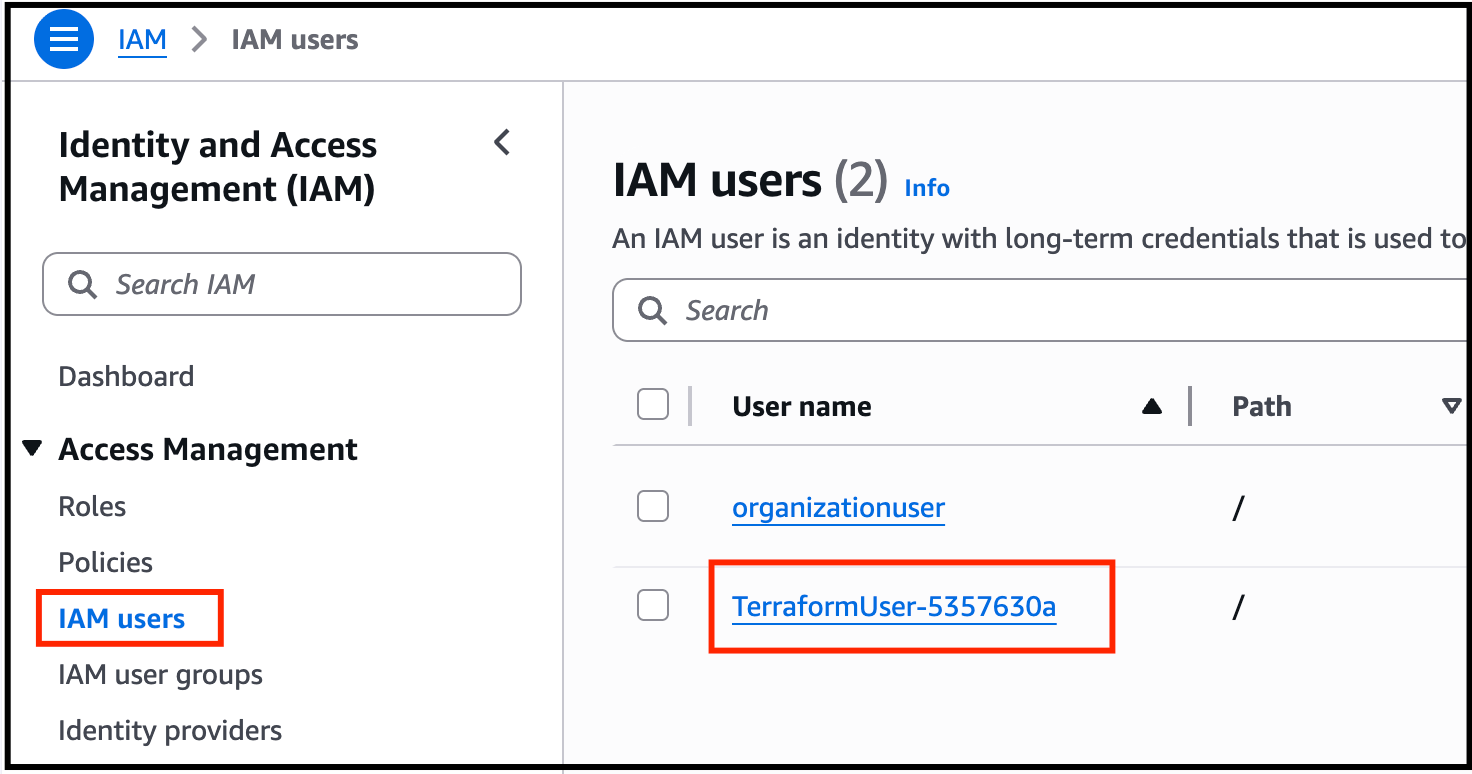
3. Then Click on **IAM Users** and select **TerraformUser-XXXXX**
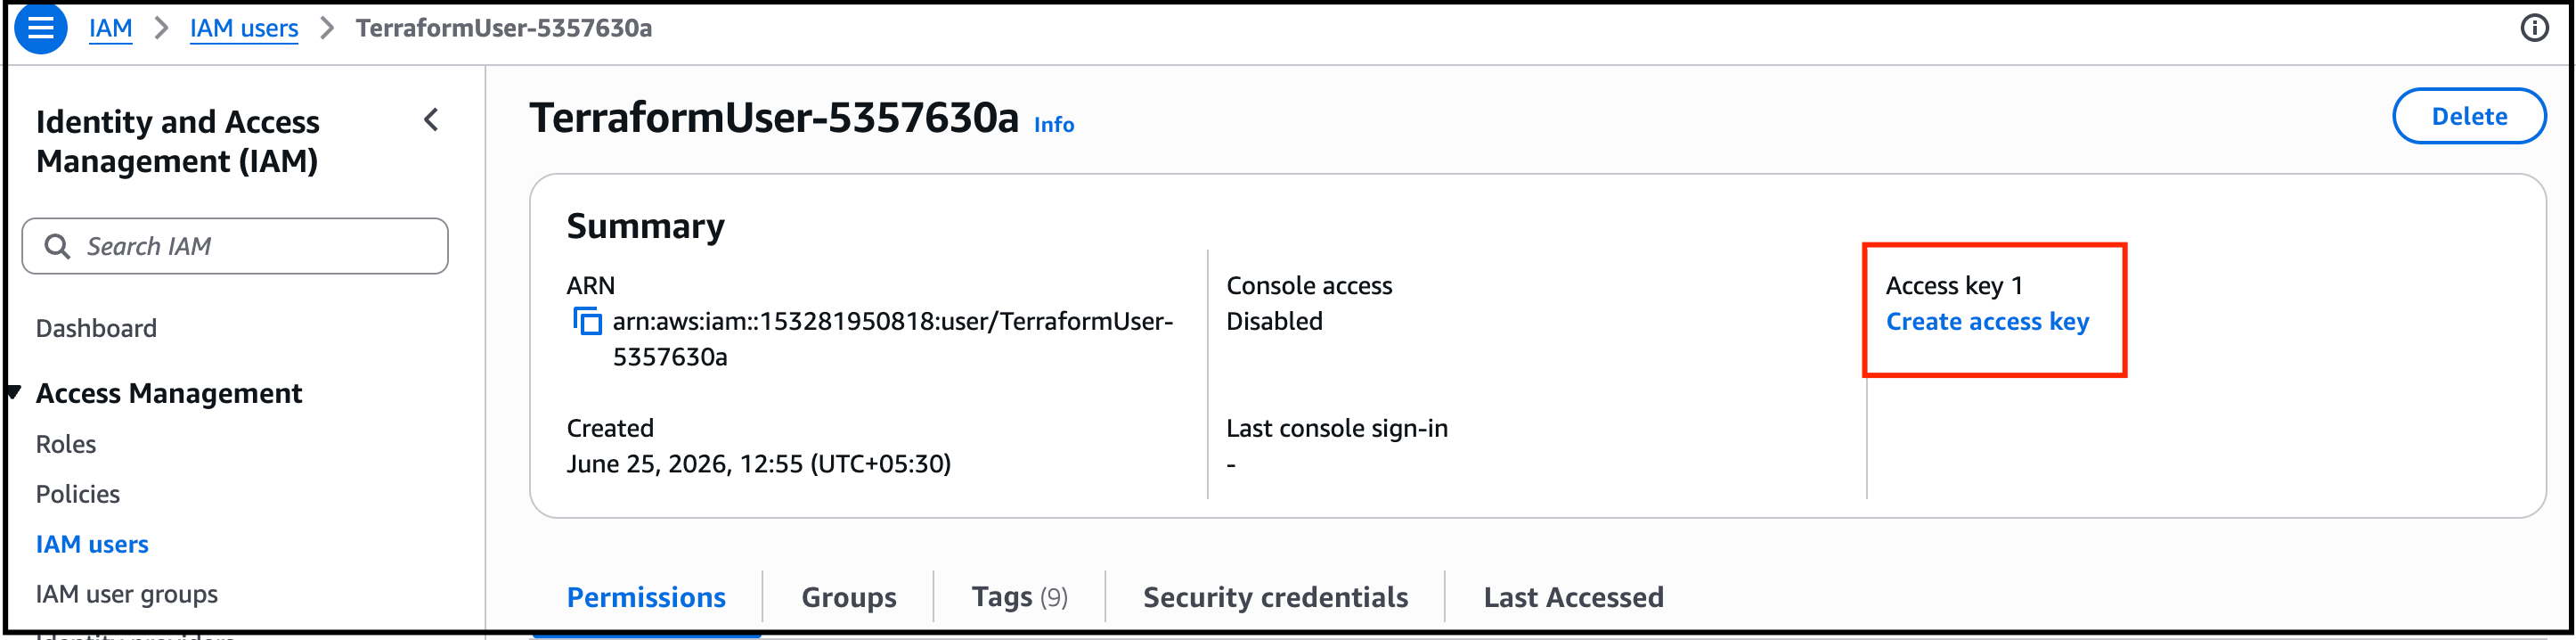
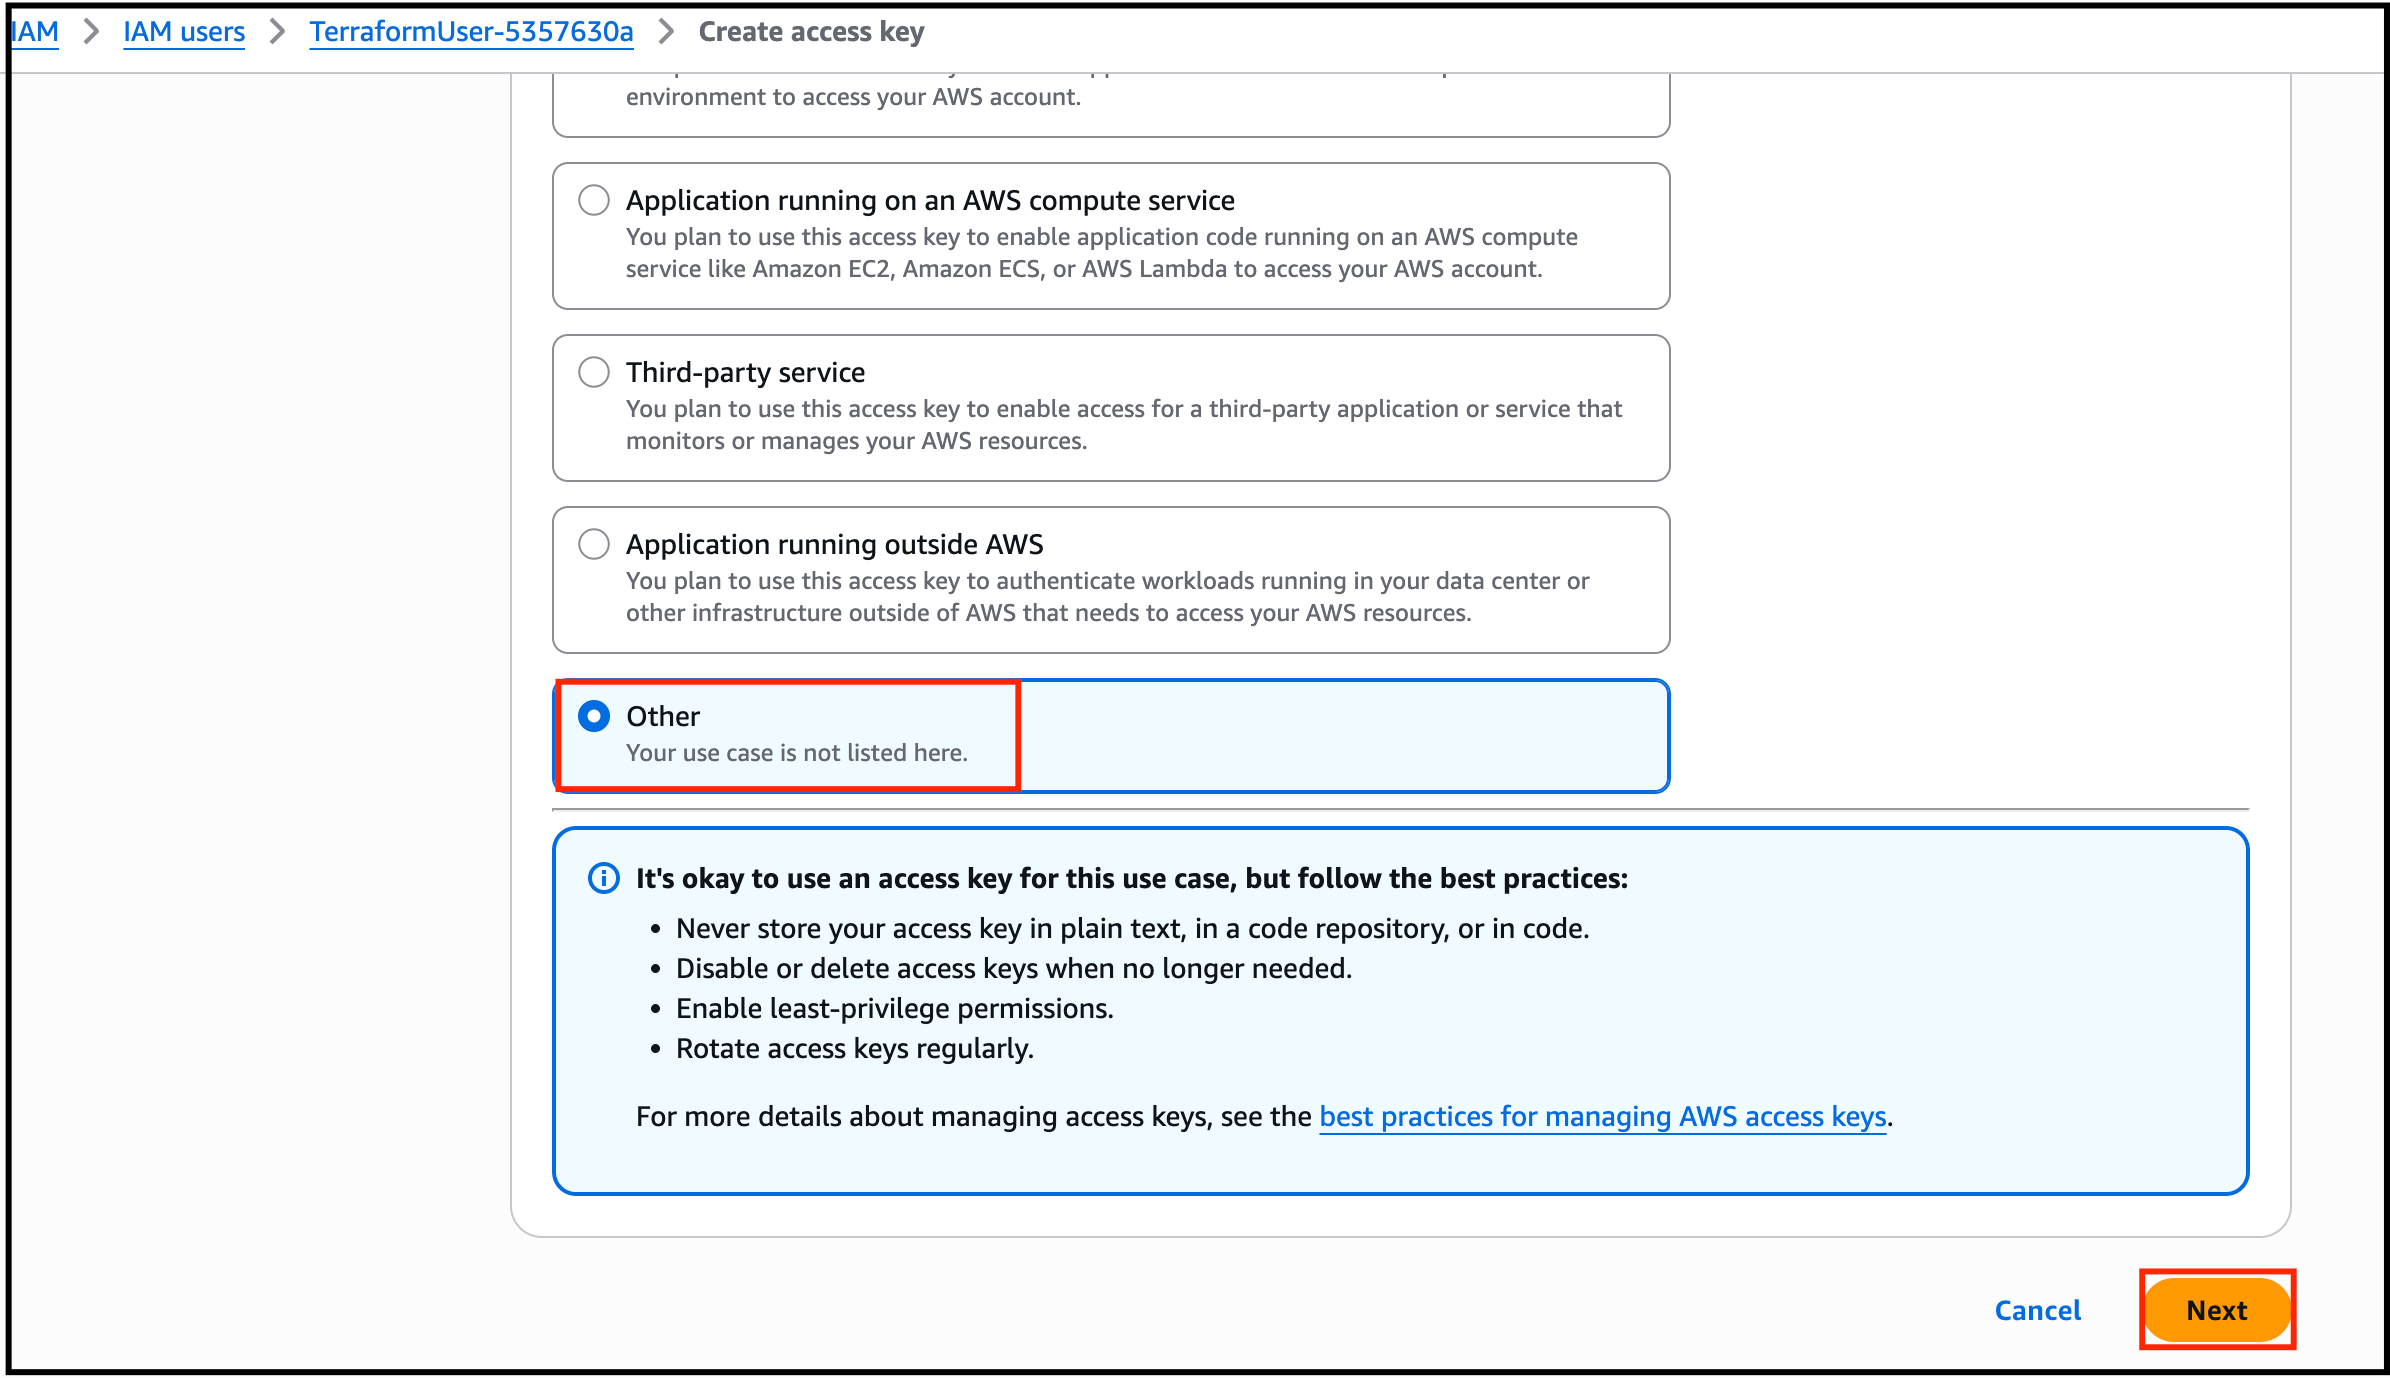
 4. Click on **Create Access Key**.
 5. Choose **Other**, Click on **Next** and click on **Create Access Key.**
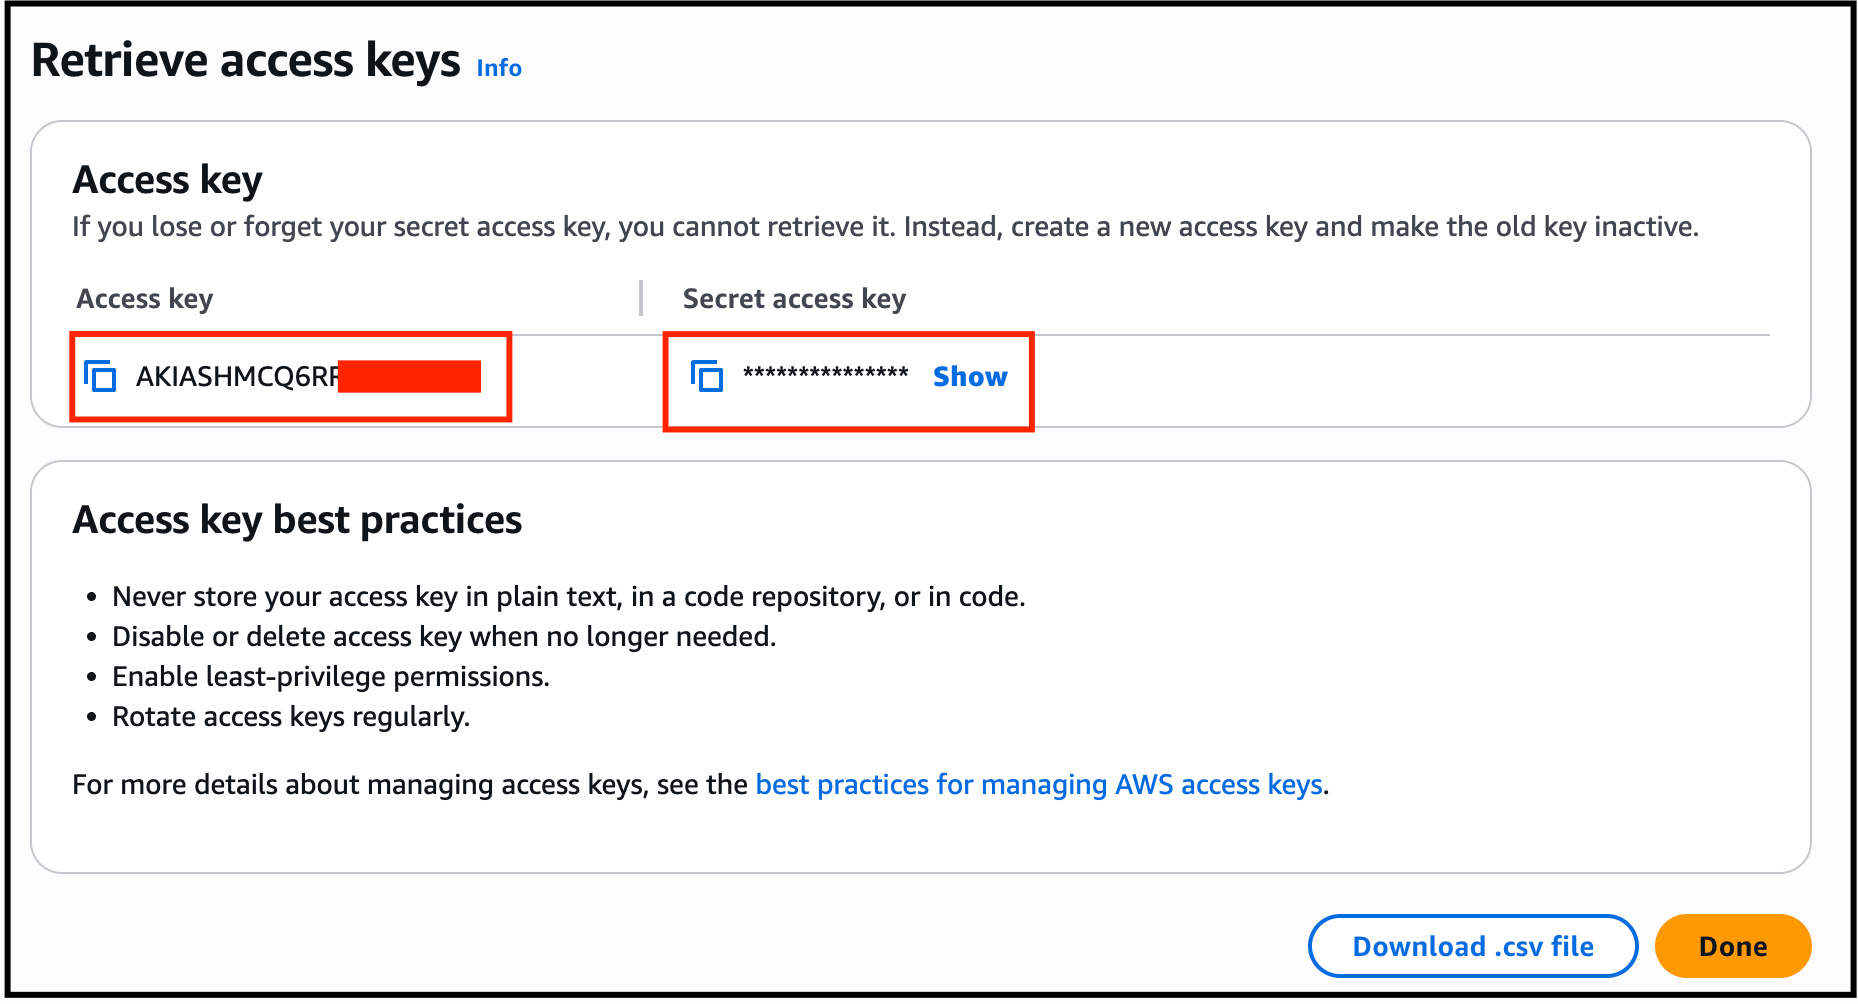
 6. Your **Access and Secret key** will get Created. Make a note of it for later use.
 #### Task 2: Setup Visual Studio Code
1. Open the visual studio code.
2. If you have already installed and using Visual studio code, open a new window.
3. A new window will open a new file and release notes page (only if you have installed or updated Visual Studio Code recently). Close the Release notes tab.
4. Open Terminal by selecting View from the Menu bar and choose Terminal.
5. It may take up to 2 minutes to open the terminal window.
6. Once the terminal is ready, let us navigate to the Desktop.
```
cd Desktop
```
7. Create a new folder by running the below command.
```
mkdir task_13081
```
8. Change your present working directory to use the newly created folder by running the below command:
```
cd task_13081
```
9. Get the location of the present working directory by running the below command:
```
pwd
```
10. Note down the location, as you will open the same in the next steps.
11. Now click on the first icon Explorer present on the left sidebar.
12. Click on the button called Open folder and navigate to the location of folder **task\_13081**.
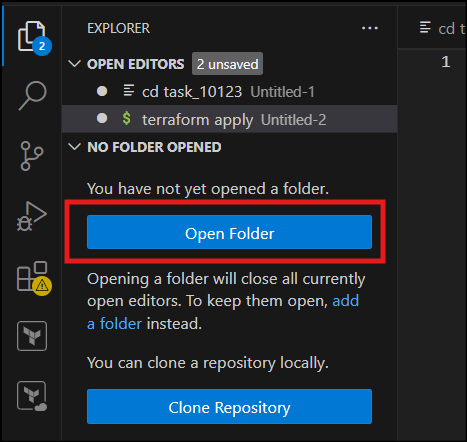 13. (Optional) Click on Authorize button for allowing Visual Studio Code to use the task\_13081 folder. This will only be asked when you have been using Visual Studio code for a while as you are allowing a new folder to be accessed by VSC.
14. Visual Studio Code is now ready to use.
#### Task 3: Create a variable file
In this task, you will create variable files where you will declare all the global variables with a short description and a default value.
1. To create a variable file, expand the folder **task\_13081** and click on the **New** **File** icon to add the file.
2. Name the file as **variables.tf** and press **Enter** to save it.
3. **Note:** Don't change the location of the new file, keep it default, i.e. inside the **task\_13081** folder\*\*.\*\*
4. Paste the below contents in **variables.tf** file.
```plaintext theme={null}
variable "access_key" {
description = "Access key to AWS console"
}
variable "secret_key" {
description = "Secret key to AWS console"
}
variable "region" {
description = "AWS region"
}
```
5. In the above content, you are declaring a variable called, access\_key, secret\_key, and region with a short description of all 3.
6. After pasting the above contents, save the file by pressing **ctrl + S**.
7. Now expand the folder **task\_13081** and click on the **New File** icon to add the file.
8. Name the file as **terraform.tfvars** and press **Enter** to save it.
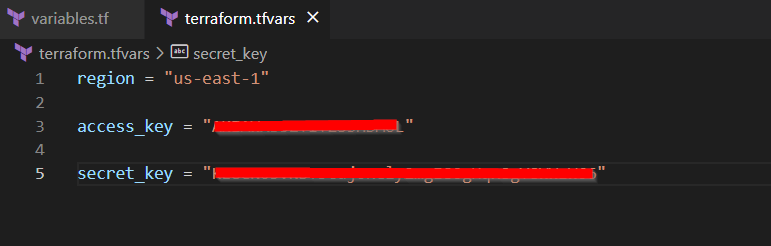
9. Paste the below content into the **terraform.tfvars** file.
```plaintext theme={null}
region = "us-east-1"
access_key = ""
secret_key = ""
```
10. In the above code, you are defining the dynamic values of variables declared earlier.
11. Replace the values of access\_key and secret\_key by copying from the lab page.
12. After replacing the values of access\_key and secret\_key, save the file by pressing Ctrl + S.
 #### Task 4: Create the key pair from EC2 Console
Navigate to **EC2 Console** and on the left bottom under Network & Security Click on **Key Pairs**
1. Click on Create Key Pair and Enter **MySSHKey.**
2. Select Key Pair type as **RSA**
3. Private key format as **.pem** and click on **Create Key Pair.**
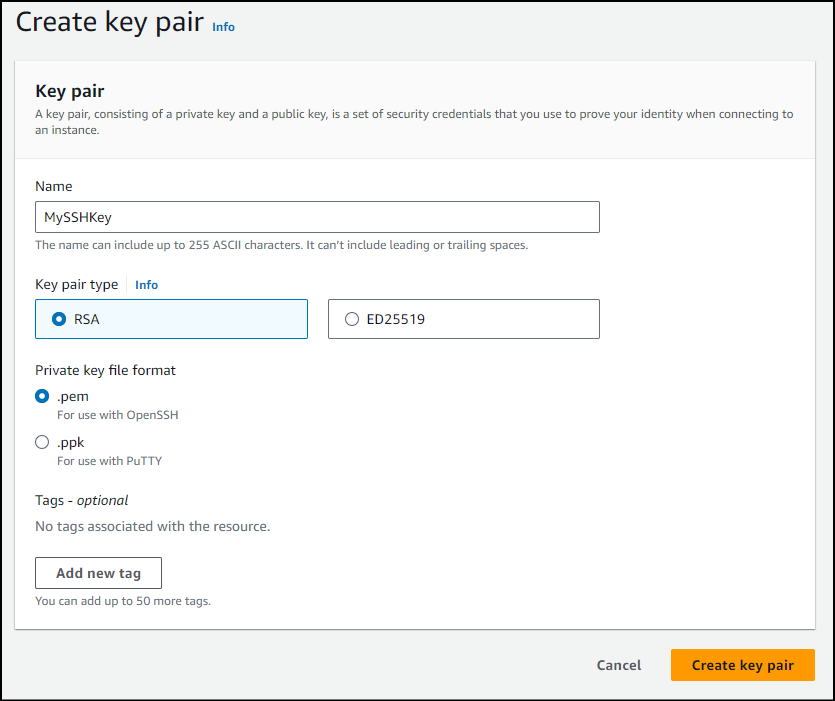 4. **MySSHKey** will be created.
#### Task 5: Create the first VPC in main.tf file
In this task, you will create a **main.tf** file where you will add details of the provider and resources.
1. To create a **main.tf** file, expand the folder **task\_13081** and click on the **New** **File** icon to add the file.
2. Name the file as **main.tf** and press **Enter** to save it.
3. Paste the below content into the **main.tf** file.
```plaintext theme={null}
provider "aws" {
region = var.region
access_key = var.access_key
secret_key = var.secret_key
}
```
4. In the above code, you are defining the provider as aws.
5. Next, we want to tell Terraform to create a first VPC
6. To create an First VPC Paste the below content into the **main.tf** file after the provider.
```plaintext theme={null}
# Create first VPC
resource "aws_vpc" "first_vpc" {
cidr_block = "10.0.0.0/24"
enable_dns_support = true
enable_dns_hostnames = true
tags = {
Name = "First_VPC"
}
}
```
#### Task 6: Create a Public subnet in First VPC
In this task, we are going to create a public subnet within the first VPC. The public subnet will be used for launching an EC2 instance that will be accessible over the internet.
1. To create a public subnet in first vpc add another block of code just below the vpc creation into the **main.tf** file.
```plaintext theme={null}
# Create public subnet for first VPC
resource "aws_subnet" "public_subnet_first_vpc" {
vpc_id = aws_vpc.first_vpc.id
cidr_block = "10.0.0.0/25"
availability_zone = "us-east-1a"
tags = {
Name = "Public_subnet_first_VPC"
}
}
```
2. Save the file by pressing **Ctrl + S.**
#### Task 7: Create Internet Gateway and Route Table
In this task, you will create a Internet Gateway and Route table in main.tf file
1. To create a Internet Gateway and Route Table add another block of code just below the public subnet code into the **main.tf** file
```plaintext theme={null}
# Create Internet Gateway
resource "aws_internet_gateway" "igw" {
vpc_id = aws_vpc.first_vpc.id
tags = {
Name = "IGW"
}
}
# Create Public Route Table and attach to Internet Gateway
resource "aws_route_table" "public_rt" {
vpc_id = aws_vpc.first_vpc.id
route {
cidr_block = "0.0.0.0/0"
gateway_id = aws_internet_gateway.igw.id
}
tags = {
Name = "PublicRT"
}
}
# Associate Public Subnet with Public Route Table
resource "aws_route_table_association" "public_subnet_association" {
subnet_id = aws_subnet.public_subnet_first_vpc.id
route_table_id = aws_route_table.public_rt.id
}
```
#### Task 8: Create a Security group for EC2 in main.tf file
In this task, you will create a Security group EC2 instance in main.tf file
1. To create a security group Paste the below content into the **main.tf** file after the route table association.
```plaintext theme={null}
# Create Security Group for EC2
resource "aws_security_group" "ec2sg" {
name = "whiz_sg"
description = "whizlabssecuritygroup"
vpc_id = aws_vpc.first_vpc.id
ingress {
from_port = 22
to_port = 22
protocol = "tcp"
cidr_blocks = ["0.0.0.0/0"]
}
ingress {
from_port = 80
to_port = 80
protocol = "tcp"
cidr_blocks = ["0.0.0.0/0"]
}
ingress {
from_port = 443
to_port = 443
protocol = "tcp"
cidr_blocks = ["0.0.0.0/0"]
}
egress {
from_port = 0
to_port = 0
protocol = "-1"
cidr_blocks = ["0.0.0.0/0"]
}
tags = {
Name = "whiz_sg"
}
}
```
2. Save the file by pressing **Ctrl + S**.
#### Task 9: Launch an EC2 instance in the First VPC
In this task, we are going to launch an EC2 instance in the first VPC's public subnet. This EC2 instance will be used to test the connectivity between the VPCs after peering them using the Transit Gateway.
1. To Launch an EC2 Instance add another block of code just below the security group code into the **main.tf** file
```plaintext theme={null}
# Create EC2 instance in the first VPC
resource "aws_instance" "first_vpc_ec2" {
ami = "ami-0b09ffb6d8b58ca91"
instance_type = "t2.micro"
key_name = "MySSHKey" # Make sure you use the same key pair that you created earlier
vpc_security_group_ids = [aws_security_group.ec2sg.id]
subnet_id = aws_subnet.public_subnet_first_vpc.id
iam_instance_profile = "ContainerInstanceEC2Role"
associate_public_ip_address = true
user_data = <<-EOF
#!/bin/bash
sudo su
dnf update -y
dnf install httpd -y
systemctl start httpd
systemctl enable httpd
echo "
Welcome to IP Lab Portal Public Server
" > /var/www/html/index.html
EOF
tags = {
Name = "First_VPCs_EC2"
}
}
```
#### Task 10: Create a Second VPC
In this task, we are going to create the second VPC, which will be the other VPC that is peered with the first VPC using the Transit Gateway.
1. To create an Second VPC Paste the below content into the **main.tf** file after the EC2 creation.
```plaintext theme={null}
# Create Second VPC
resource "aws_vpc" "second_vpc" {
cidr_block = "20.0.0.0/24"
enable_dns_support = true
enable_dns_hostnames = true
tags = {
Name = "Second_VPC"
}
}
```
#### Task 11: Create a Private subnet in Second VPC
In this task, we are going to create a private subnet within the second VPC. The private subnet will be used for launching an EC2 instance that will not have direct internet connectivity.
1. To create a private subnet in first vpc add another block of code just below the vpc creation into the **main.tf** file.
```plaintext theme={null}
# Create private subnet for second VPC
resource "aws_subnet" "private_subnet_second_vpc" {
vpc_id = aws_vpc.second_vpc.id
cidr_block = "20.0.0.0/25"
availability_zone = "us-east-1a"
}
```
#### Task 12: Create a Security group for Second VPC
In this task, you will create a Security group EC2 instance in main.tf file
1. To create a security group Paste the below content into the **main.tf** file after the private subnet creation.
```plaintext theme={null}
# Create second Security Group for EC2
resource "aws_security_group" "privateec2sg" {
name = "whiz_sg2"
description = "whizlabssecuritygroup"
vpc_id = aws_vpc.second_vpc.id
ingress {
from_port = 22
to_port = 22
protocol = "tcp"
cidr_blocks = ["0.0.0.0/0"]
}
egress {
from_port = 0
to_port = 0
protocol = "-1"
cidr_blocks = ["0.0.0.0/0"]
}
tags = {
Name = "whiz_sg"
}
}
```
2. Save the file by pressing **Ctrl + S**.
#### Task 13: Launch an EC2 instance in Second VPC
In this task, we are going to launch an EC2 instance in the Second VPC's private subnet. This EC2 instance will be used to test the connectivity between the VPCs after peering them using the Transit Gateway.
To Launch an EC2 Instance add another block of code just below the security group code into the **main.tf** file
```plaintext theme={null}
# Create EC2 instance in the second VPC
resource "aws_instance" "second_vpc_ec2" {
ami = "ami-0b09ffb6d8b58ca91"
instance_type = "t2.micro"
key_name = "MySSHKey"
vpc_security_group_ids = [aws_security_group.privateec2sg.id]
subnet_id = aws_subnet.private_subnet_second_vpc.id
associate_public_ip_address = false
user_data = <<-EOF
#!/bin/bash
sudo su
dnf update -y
dnf install httpd -y
systemctl start httpd
systemctl enable httpd
echo "Welcome to IP Lab Portal Private Server
" > /var/www/html/index.html
EOF
tags = {
Name = "Second_VPCs_EC2"
}
}
```
#### Task 14: Create a Transit Gateway
In this task, we are going to create a Transit Gateway, which acts as a central hub for connecting multiple VPCs and on-premises networks. The Transit Gateway simplifies the network architecture and facilitates the peering between VPCs.
1. To create a private subnet in first vpc add another block of code just below the ec2 creation into the **main.tf** file.
```plaintext theme={null}
# Create EC2 Transit Gateway
resource "aws_ec2_transit_gateway" "demo_tg" {
description = "TG for peering two VPCs"
tags = {
Name = "DemoTG"
}
}
```
#### Task 15: Create two Transit gateway attachment for the VPCs created
In this task, we are going to create two Transit Gateway attachments, one for each of the VPCs created. These attachments establish the peering between the VPCs and the Transit Gateway.
1. To create a private subnet in first vpc add another block of code just below the transit gateway into the main.tf file.
```plaintext theme={null}
# Attach first VPC to the Transit Gateway
resource "aws_ec2_transit_gateway_vpc_attachment" "first_vpc_tga" {
transit_gateway_id = aws_ec2_transit_gateway.demo_tg.id
vpc_id = aws_vpc.first_vpc.id
subnet_ids = [aws_subnet.public_subnet_first_vpc.id]
}
```
```plaintext theme={null}
# Attach second VPC to the Transit Gateway
resource "aws_ec2_transit_gateway_vpc_attachment" "second_vpc_tga" {
transit_gateway_id = aws_ec2_transit_gateway.demo_tg.id
vpc_id = aws_vpc.second_vpc.id
subnet_ids = [aws_subnet.private_subnet_second_vpc.id]
}
```
#### Task 16: Add the routes in the route table
1. To create a private subnet in first vpc add another block of code just below the tranist gateway attachment creation into the **main.tf** file.
```plaintext theme={null}
resource "aws_route" "first_vpc_route_to_second_vpc" {
route_table_id = aws_route_table.public_rt.id
destination_cidr_block = aws_vpc.second_vpc.cidr_block
transit_gateway_id = aws_ec2_transit_gateway.demo_tg.id
}
```
```plaintext theme={null}
resource "aws_route" "second_vpc_route_to_first_vpc" {
route_table_id = aws_vpc.second_vpc.main_route_table_id
destination_cidr_block = aws_vpc.first_vpc.cidr_block
transit_gateway_id = aws_ec2_transit_gateway.demo_tg.id
}
```
#### Task 17: Create Output File
1. In this task, you will create an **output.tf** file where you add details of the output you want to display.To create an output.tf file, expand the folder **task\_13081** and click on the New File icon to add the file.
2. Name the file as **output.tf** and press Enter to save it.Paste the below content into the **output.tf** file.
```plaintext theme={null}
# Output the First VPC ID
output "first_vpc_id" {
description = "The ID of the First VPC"
value = aws_vpc.first_vpc.id
}
# Output the Second VPC ID
output "second_vpc_id" {
description = "The ID of the Second VPC"
value = aws_vpc.second_vpc.id
}
# Output the Public Subnet ID in the First VPC
output "public_subnet_first_vpc_id" {
description = "The ID of the public subnet in the First VPC"
value = aws_subnet.public_subnet_first_vpc.id
}
# Output the Private Subnet ID in the Second VPC
output "private_subnet_second_vpc_id" {
description = "The ID of the private subnet in the Second VPC"
value = aws_subnet.private_subnet_second_vpc.id
}
# Output the Internet Gateway ID
output "internet_gateway_id" {
description = "The ID of the Internet Gateway for the First VPC"
value = aws_internet_gateway.igw.id
}
# Output the Route Table ID
output "public_route_table_id" {
description = "The ID of the public route table for the First VPC"
value = aws_route_table.public_rt.id
}
# Output the Security Group ID for the Public EC2 instance
output "public_ec2_sg_id" {
description = "The ID of the Security Group for the public EC2 instance"
value = aws_security_group.ec2sg.id
}
# Output the Security Group ID for the Private EC2 instance
output "private_ec2_sg_id" {
description = "The ID of the Security Group for the private EC2 instance"
value = aws_security_group.privateec2sg.id
}
# Output the Public EC2 Instance ID
output "public_ec2_instance_id" {
description = "The ID of the public EC2 instance"
value = aws_instance.first_vpc_ec2.id
}
# Output the Public EC2 Instance Public IP
output "public_ec2_instance_public_ip" {
description = "The Public IP address of the public EC2 instance"
value = aws_instance.first_vpc_ec2.public_ip
}
# Output the Private EC2 Instance ID
output "private_ec2_instance_id" {
description = "The ID of the private EC2 instance"
value = aws_instance.second_vpc_ec2.id
}
# Output the Transit Gateway ID
output "transit_gateway_id" {
description = "The ID of the Transit Gateway"
value = aws_ec2_transit_gateway.demo_tg.id
}
# Output the Transit Gateway Attachment ID for the First VPC
output "transit_gateway_attachment_first_vpc_id" {
description = "The ID of the Transit Gateway attachment for the First VPC"
value = aws_ec2_transit_gateway_vpc_attachment.first_vpc_tga.id
}
# Output the Transit Gateway Attachment ID for the Second VPC
output "transit_gateway_attachment_second_vpc_id" {
description = "The ID of the Transit Gateway attachment for the Second VPC"
value = aws_ec2_transit_gateway_vpc_attachment.second_vpc_tga.id
}
```
#### Task 18: Confirm the installation of Terraform by checking the version
1. In the Visual Studio Code, open Terminal by selecting **View** from the Menu bar and choose **Terminal**.
2. If you are not in the newly created folder change your present working directory by running the below command.
```
cd task_13081
```
3. To confirm the installation of Terraform, run the below command to check the version:
```
terraform version
```
4. If you are getting output as command not found: terraform, this means that terraform is not installed on your system, To install terraform follow the official guide link provided in the Prerequisite section above.
#### Task 19: Apply terraform configurations
1. Initialize Terraform by running the below command,
```
terraform init
```
 > **Note:** terraform init will check for all the plugin dependencies and download them if required, this will be used for creating a deployment plan
2. To generate the action plans run the below command,
```
terraform plan
```
3. To create all the resources declared in main.tf configuration file, run the below command:
```
terraform apply
```
4. Approve the creation of all the resources by entering **yes**.
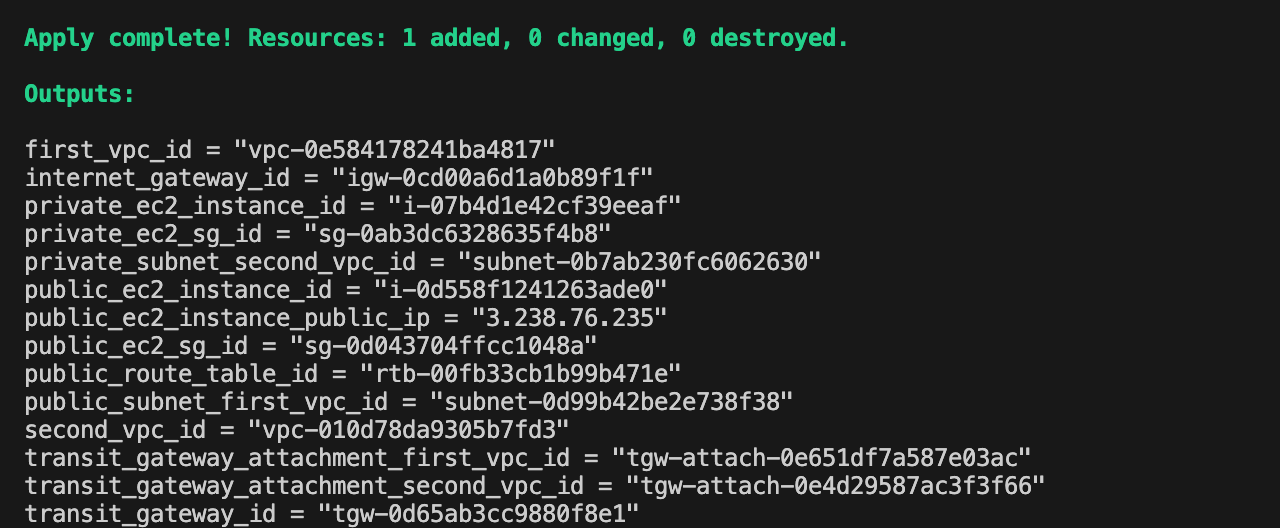 5. It may take up to 2-5 minutes for the terraform apply command to create the resources.
6. Id’s of all the resources created by terraform will be visible there.
#### Task 20 : Test the connectivity between two VPCs
In this task, we are going to test the connectivity between the EC2 instances in both VPCs. This step confirms that the VPCs have been successfully peered using the Transit Gateway, and the EC2 instances can communicate with each other.
1. You have copied the IPv4 Public IP of the EC2 instance created in the **First VPC**.
2. Please follow the steps for **Session manager** to connect into **First\_VPCs\_EC2**
* Select **First\_VPCs\_EC2** and click on **Connect button.**
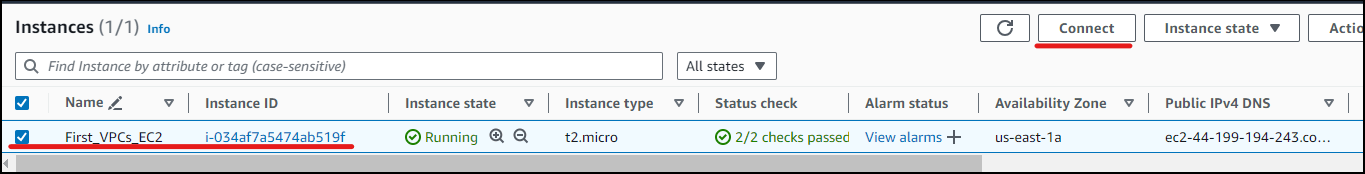 3. Go to **Session Manager** and click **Connect**
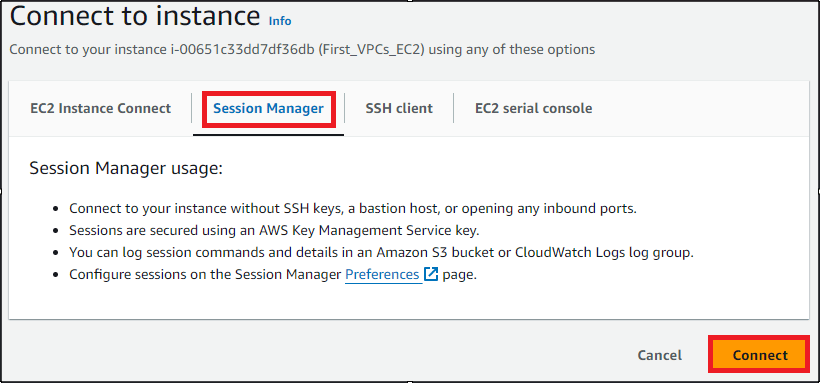 4. Once you have successfully connected in to EC2, run the following commands :
* Switch to root user :
```
sudo su
```
* Update server repository :
```
yum update -y
```
5. Now we need to copy the .pem key of the EC2 instance created.
* Create a file :
```
vi MySSHKey.pem
```
 * Open the .pem key of EC2 **MySSHKey** in your local editor and paste it in the terminal file.
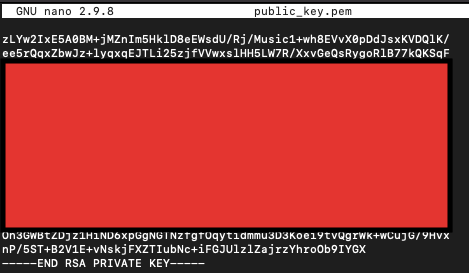 * Press **:wq**
* File Name : No changes, press **\[Enter]** key in your keyboard
6. Change the .pem key permission
```
chmod 400 MySSHKey.pem
```
7. SSH into the Private EC2 **MySSHKey**
```
ssh ec2-user@ -i ec2_ssh_key.pem
```
* Copy the Private IP of **First\_VPCs\_EC2**
* Example : **ssh ec2-user\@20.0.0.11 -i MySSHKey.pem**
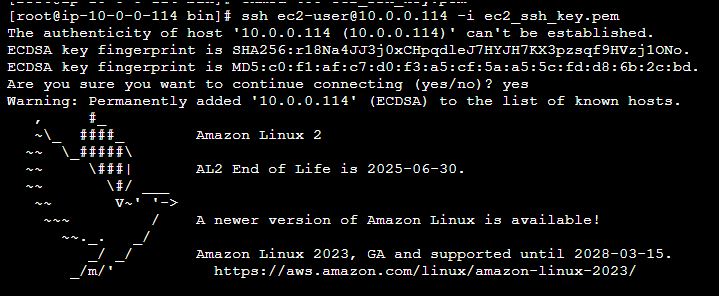
8 . If the connection prompts a message to confirm connect enter **yes**
 9. As you can see the IP address is changed to private ec2 private IP 30.0.1.154
 ##### Task 21: Delete AWS Resources
1. To delete the resources, open Terminal again.
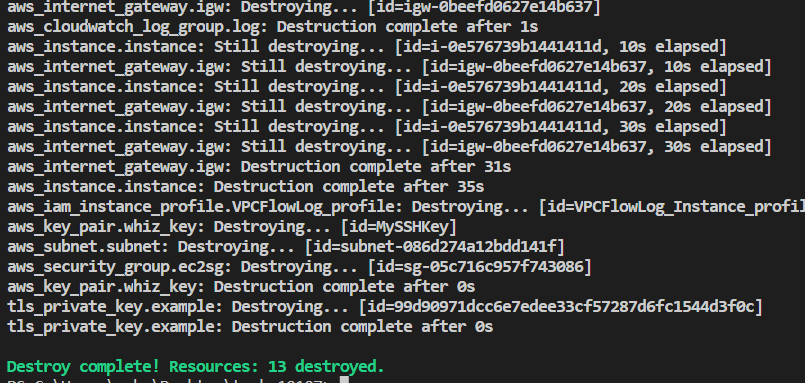
2. Run the below command to delete all the resources.
```
terraform destroy
```
3. Approve the creation of all the resources by entering **yes**. You can see the **Destroy complete!** message.
 > ##### Do You Know?
>
> With Transit Gateway, you can easily add or remove VPC connections as your network grows or changes, without impacting existing connections. It provides a flexible and scalable solution for interconnecting VPCs and simplifies network administration, routing, and security.
### Completion and Conclusion
1. You have successfully created a VPC with a public subnet & internet gateway and Launched an EC2 instance.
2. You have successfully created a VPC with a private subnet and Launched an EC2 instance.
3. You have successfully created the Transit gateway.
4. You have successfully created the Transit gateway attachments for both the VPC’s.
5. You have successfully tested the connectivity of VPC after peering using the Transit gateway.
### End Lab
1. Sign out of AWS Account.
2. You have successfully completed the lab.
3. Once you have completed the steps, click on **End Lab** from the IP Lab Portal dashboard.
## What gets checked
When you press **Check my work**, the platform verifies each of these:
* **Launch an EC2 Instance** — Check whether an EC2 Instance is launched or not.
* **Create VPC Transit Gateway** — Check whether a Transit Gateway is created with status Available or not.
* **Create VPC Transit Gateway Attachment** — Check whether a Transit Gateway Attachment is created with Resource Type VPC and status Available or not.
This documentation is built and hosted on [Mintlify](https://mintlify.com), a developer documentation platform.