> ## Documentation Index
> Fetch the complete documentation index at: https://cloud-architect.ipoint-labs.com/llms.txt
> Use this file to discover all available pages before exploring further.
# Find vulnerabilities on Inspector2 using Lambda scanning
> Hands-on lab · 45m
Launch this lab in the IP Lab Portal, then follow the steps below in the AWS console.
Open IP Lab Portal
## Overview
#### Lab Details
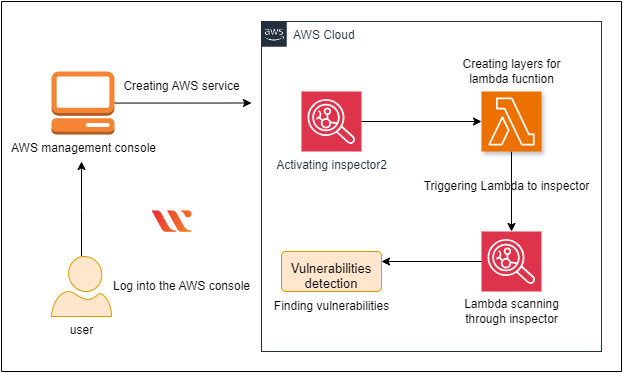
1. The lab involves creating an inspector and lambda function
2. Trigging the lambda function to scan the inspector to finding the vulnerabilities
3. Duration: **1 hour**
4. AWS Region: **US East (N. Virginia) us-east-1**
#### Introduction
1. Amazon Inspector is a service provided by Amazon Web Services (AWS) that helps you to automatically assess the security and compliance of your AWS resources, including AWS Lambda functions.
2. It performs security assessments by analyzing your resources and identifying potential vulnerabilities and deviations from best practices.
3. Learn how to navigate the Amazon Inspector console to view detailed findings of scanned Lambda functions, including CVE identifiers and severity ratings.
4. Inspector v2 integrates seamlessly with AWS services such as EC2, ECR, and Lambda, allowing for continuous vulnerability assessment and management.
5. In this lab, you will learn how to scan your AWS Lambda functions using Amazon Inspector
#### Architecture Diagram
 #### Task Details
1. Sign in to AWS Management Console
2. Creating an inspector2 and activating it
3. Creating a lambda function and the layers
4. Triggering the lambda function
5. Scanning the lambda function to check the vulnerabilities
#### Launching Lab Environment
1. To Launch the lab Environment, Click On The **Start Lab** Button.
2. Please Wait Until The Cloud Environment Is Provisioned. It Will Take Less Than A Minute To Provision.
3. Once The lab Is Started, You Will Be Provided With **IAM User Name, Password, Access Key, And Secret Access Key**.
> **Note :** You can only start one guided lab at any given time
## Lab guide
#### Lab Steps
#### Task 1: Sign in to AWS Management Console
1. Click On The **Open Console** Button, And You Will Get Redirected To AWS Console In A New Browser Tab.
2. On The AWS Sign-In Page, Leave The Account ID As Default. Never Edit/Remove The 12 Digit Account ID Present In The AWS Console. Otherwise, You Cannot Proceed With The Lab.
3. Now Copy Your **User Name** And **Password** In The Lab Console To The **IAM Username And Password** In AWS Console And Click On The **Sign In** Button.
4. Once Signed In To The AWS Management Console, Make The Default AWS Region As **US East (N. Virginia) Us-East-1**.
#### Task 2: Enable Amazon Inspector for your AWS Account
1. In the AWS console, search for **Amazon Inspector** and click on it.
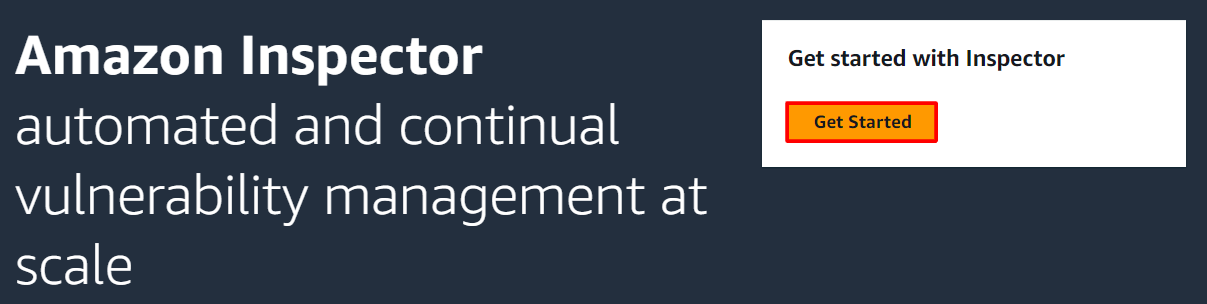
2. Click on **Get started**.
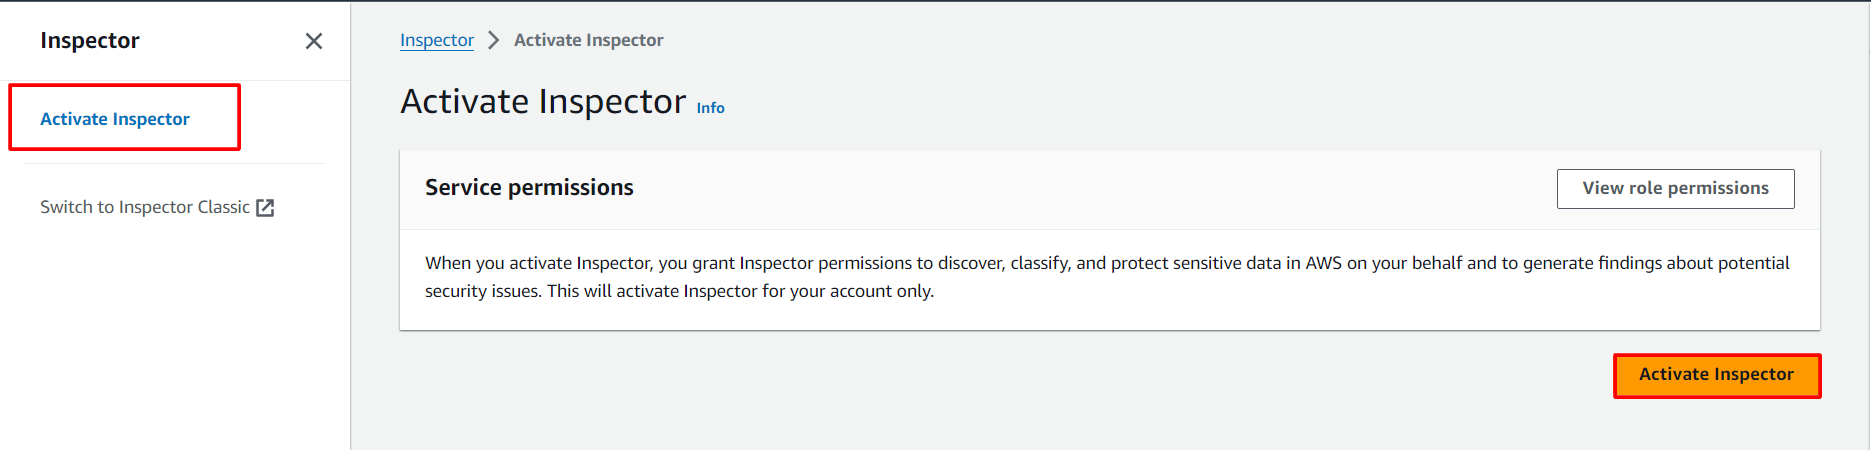
 3. And you will be able to see **Activate Inspector**.
4. Click on the **Activate Inspector**
 5. In the left-side dashboard, scroll down and click on **Account management**.
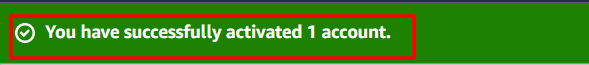
6. Click on the **Activate** button.
7. Check AWS Lambda Standard scanning.
* **Lambda standard scanning** — With this option enabled, Amazon Inspector only scans for package dependencies in your Lambda functions and associated layers.
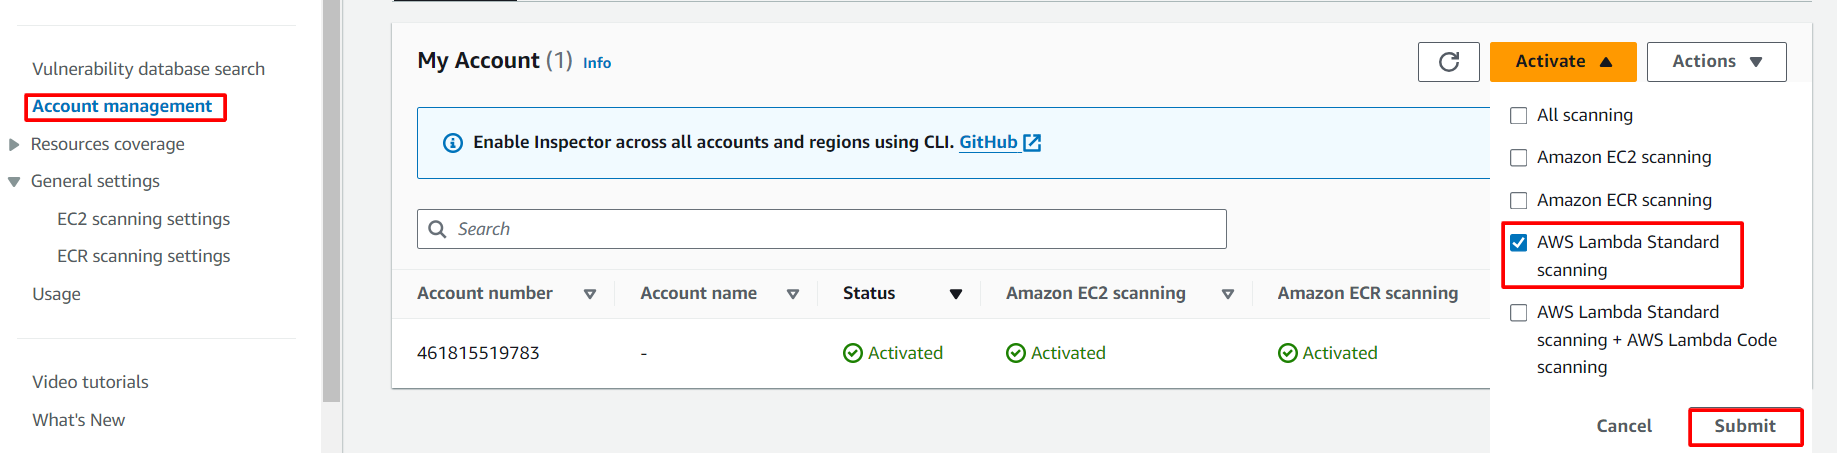 8. Click on **Submit**.
 #### Task 3: Create a Lambda Function
1. Make sure you are in the **US East (N. Virginia)** region.
2. Go to the **Services menu** and click on **Lambda** under **Compute section**.
3. Click on the **Create a function** button.
4. Choose Author from scratch
* Function name : **testing\_lambda**
* Runtime : Select **Python 3.11**
5. Expand **Change default execution role** select **use an existing role** and select **Lambda\_role** from the drop-down.
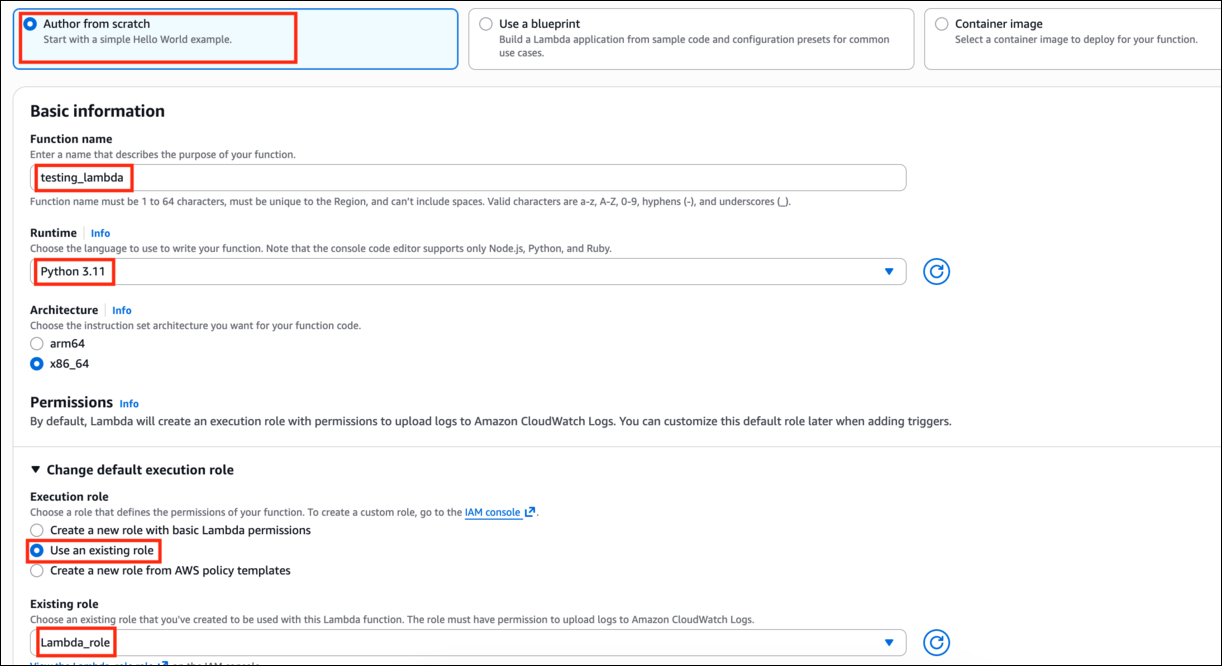 6. Click on the **Create function** button.
7. If you scroll down a little bit, you can see the Code source section. Here we are going to replace the python function code.
8. Remove the existing code in AWS lambda\_function.py. Copy the below code and paste it into your **lambda\_function.py** file.
```
import json
import os
import paramiko
def lambda_handler(event, context):
print("Hello world")
os.system("ssh -h")
```
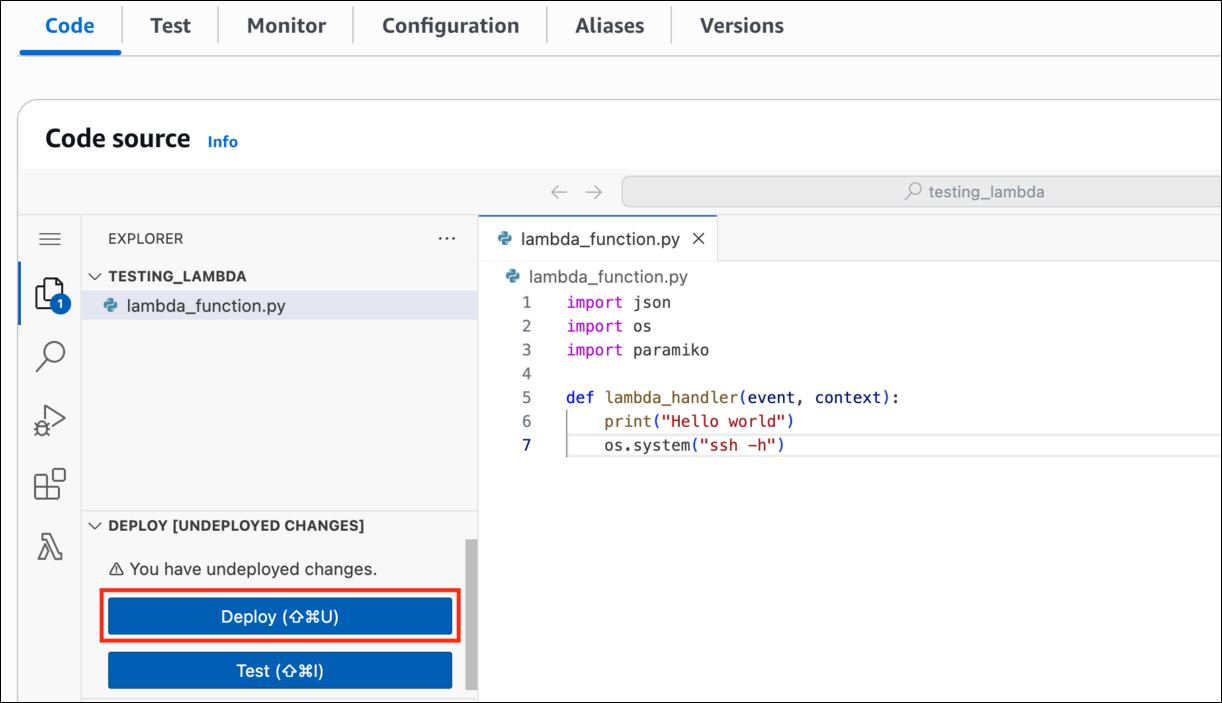 9. click on **Deploy** button.
#### Task 4: Creating Layers for Lambda function
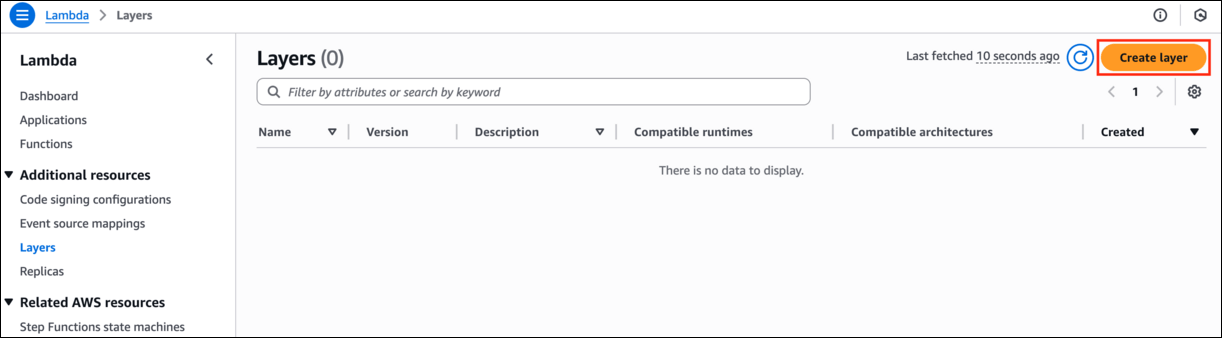
1. In the Lambda console, click on the **Layers** section in the left-hand navigation pane
2. Click on the **Create Layer** button.
 3. Layer name: **paramiko\_layer**
4. Description: Creating a paramiko layer for the lambda function
5. Click on the below link to download the zip file to upload in the layers.
* [Paramiko\_layer](https://labresources.whizlabs.com/201bee982ab8b39f7f533332ebef383c/paramiko-test.zip)
6. Compatible architectures: **x86\_64**
7. Runtime: **python 3.11**
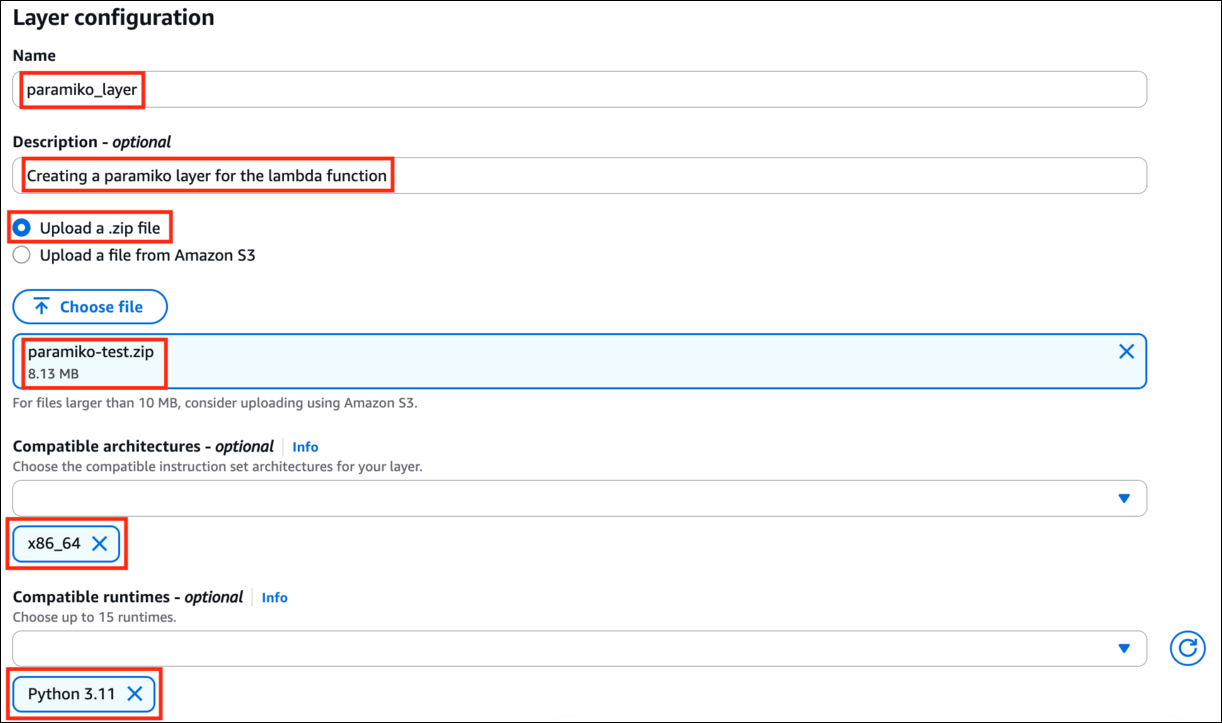 8. Click on the **Create** button.
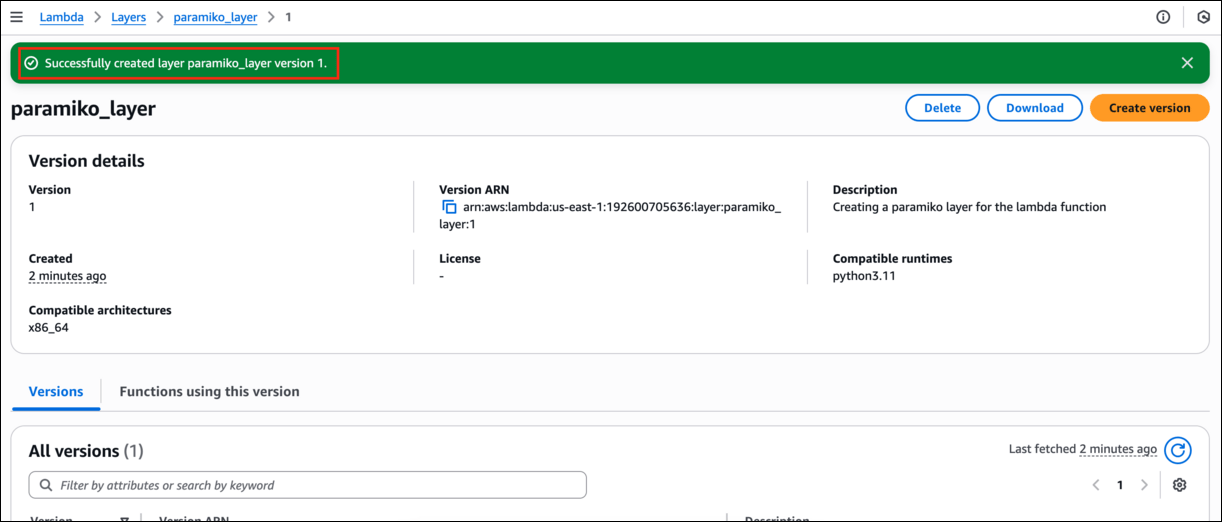 #### Task 5: Adding the layers to the lambda function
1. In the Lambda console, click on the **function** you created earlier.
2. In the **Code** section, scroll down to the **Layers** section.
3. Click on the **Add Layer** button.
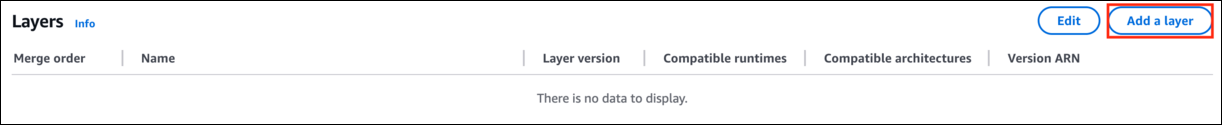 4. Go to the **Custom Layers** section.
5. Under the custom layers dropdown, choose the Paramiko layer you created earlier.
6. Click on the **version dropdown** and select the appropriate version.
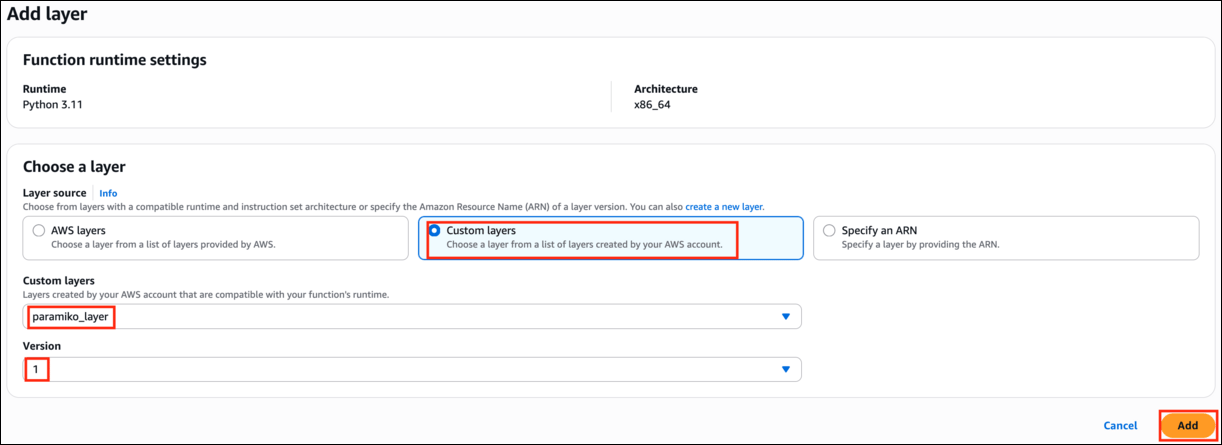 7. Click the **Add** button.
8. After creating the layer scroll it will look like these.
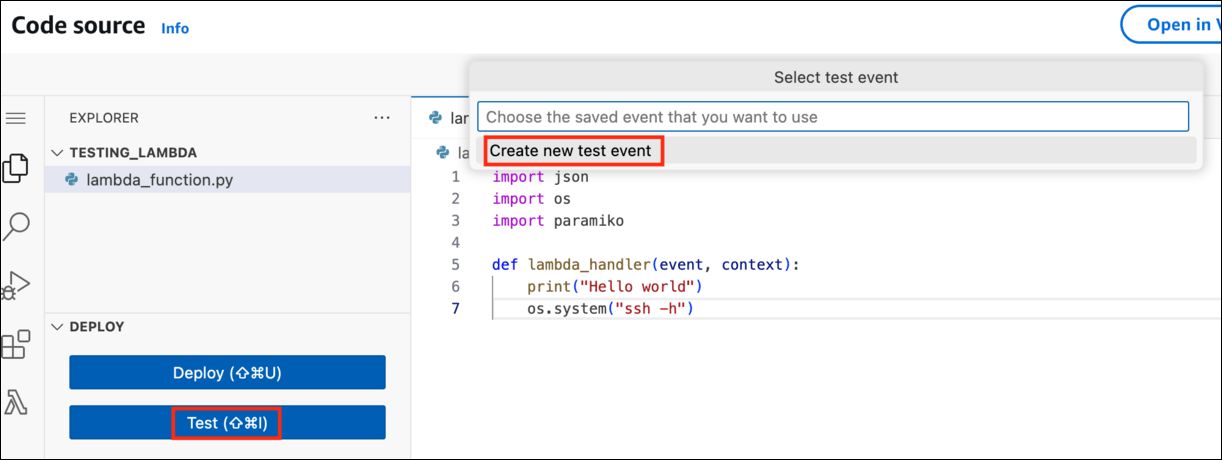
 9. Now, go back to your Lambda function and click the **Test** button and click **Create new test event**.
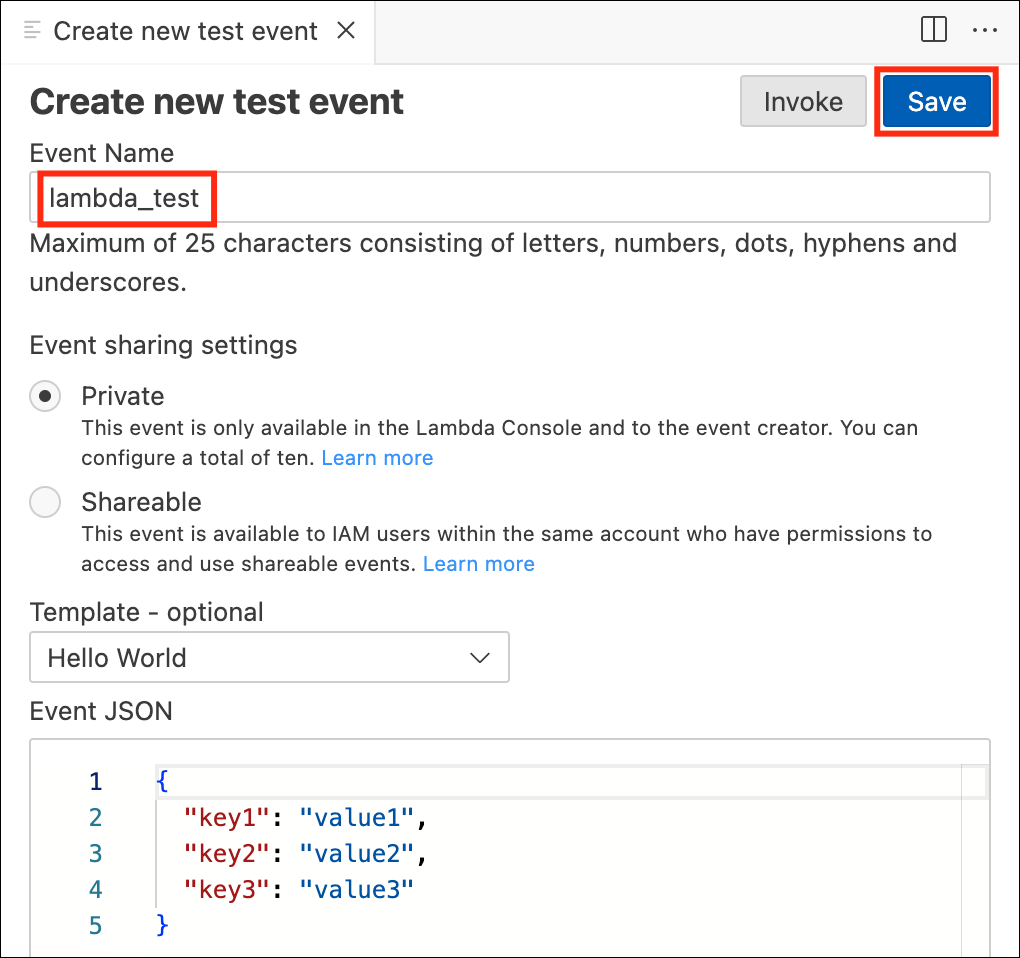
 10. Enter the name as **lambda\_test** and click **Save**.
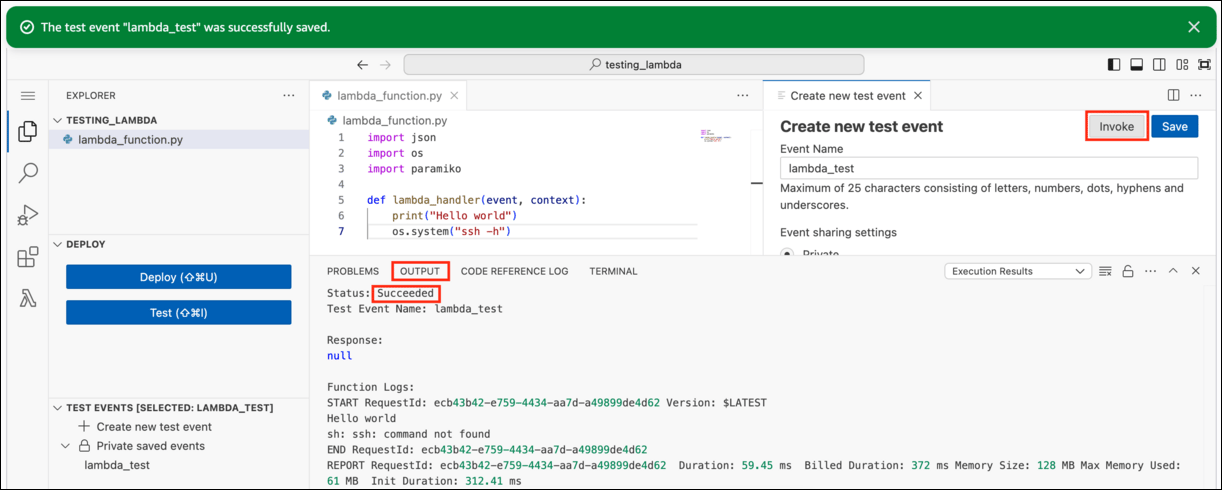
 11. Now click **Invoke** button. It will trigger the Inspector Lambda scanning.
 #### Task 6: Finding the vulnerability for the Lambda function
1. Go back to the **Inspector** console.
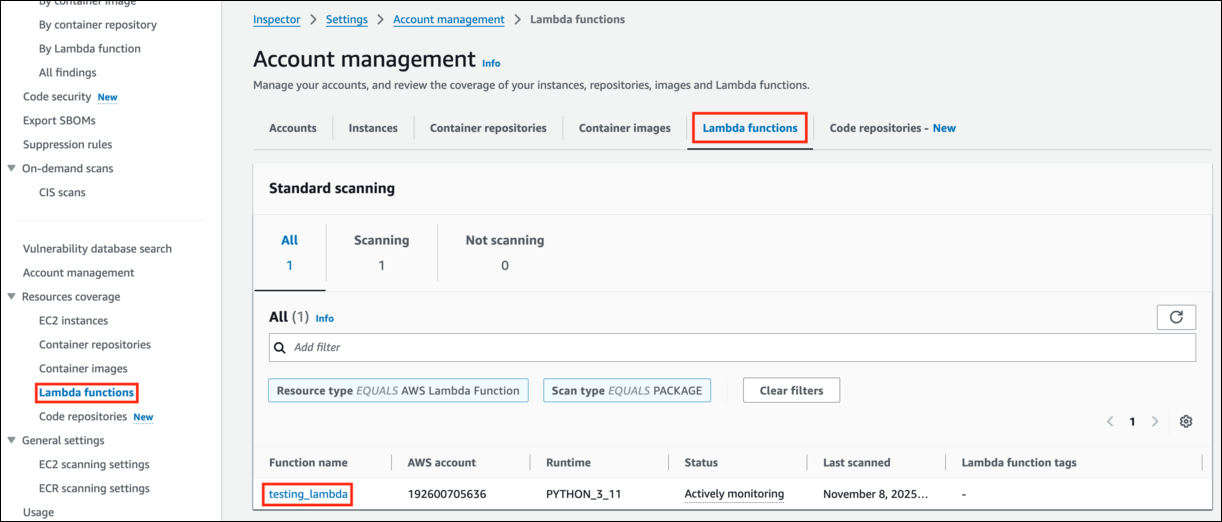
2. Scroll down and click on **Resources coverage** from the left panel.
3. Click on the **Lambda functions** to see the status of the scanning.
 4. Now click **Findings** from the left panel and click **By Lambda function**.
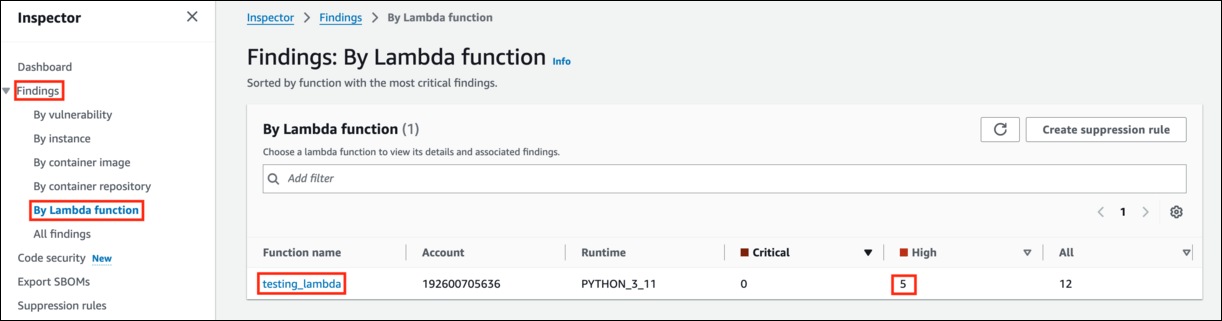 5. Click on the **testing\_lambda** and scroll down, you will be able to see the different CVE names.
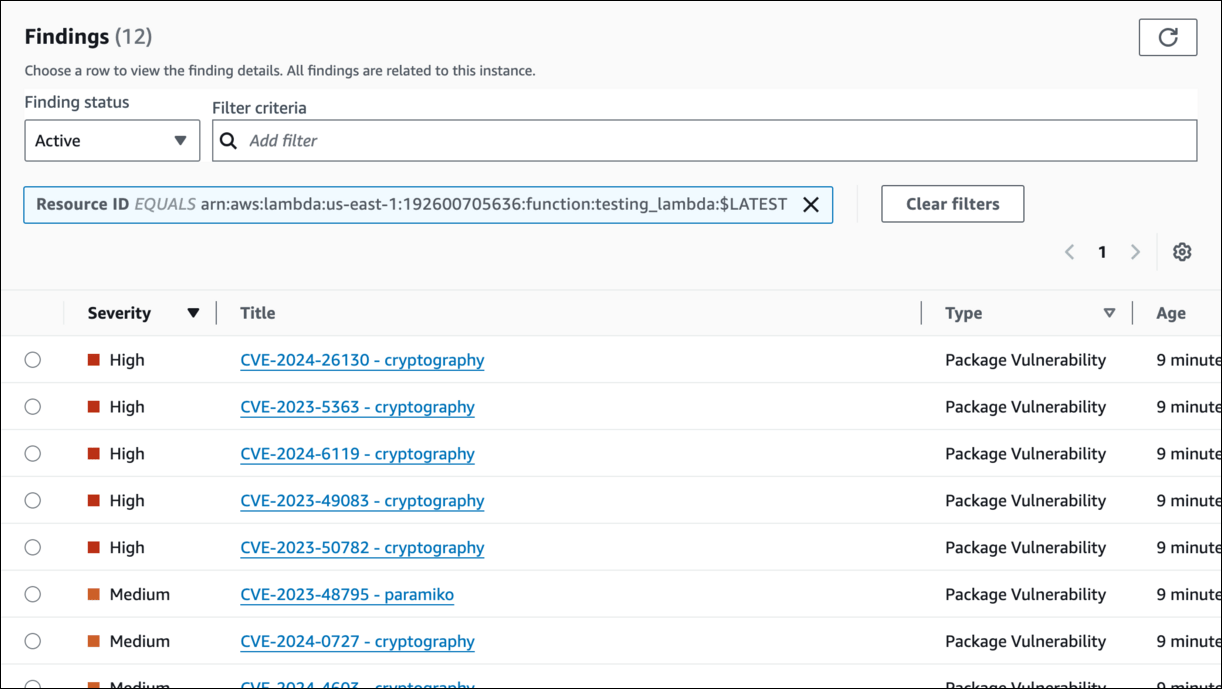 6. Click on any **CVE title** to see the findings details.
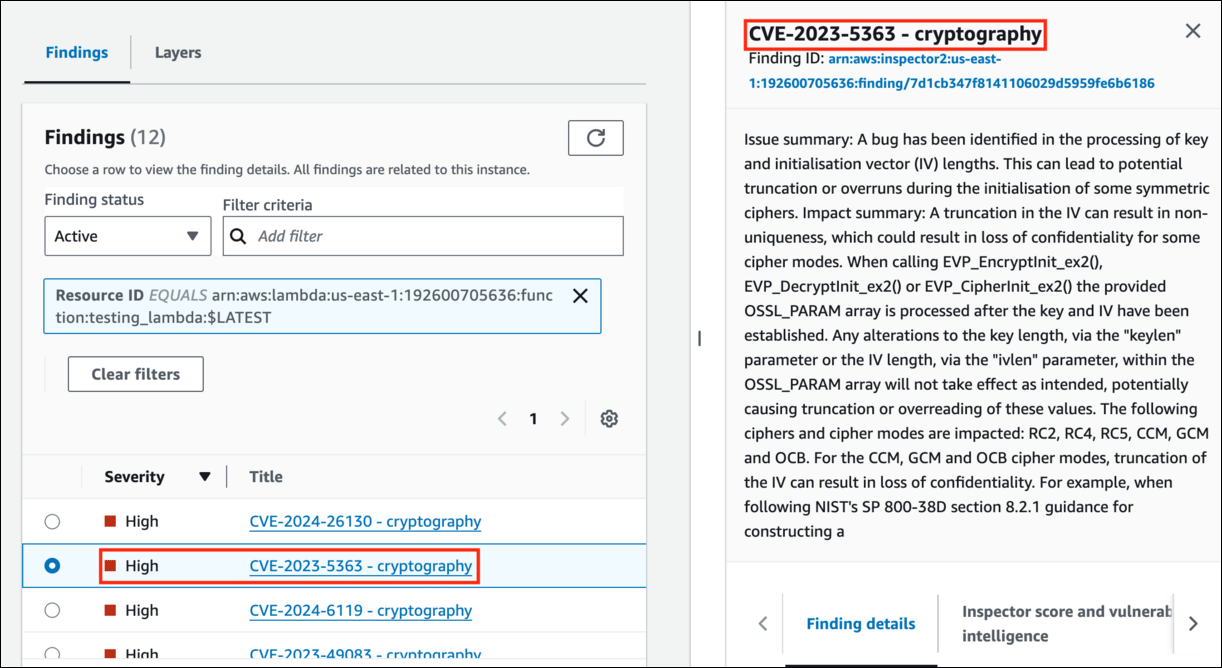 7. Scroll down CVE tab to see more details.
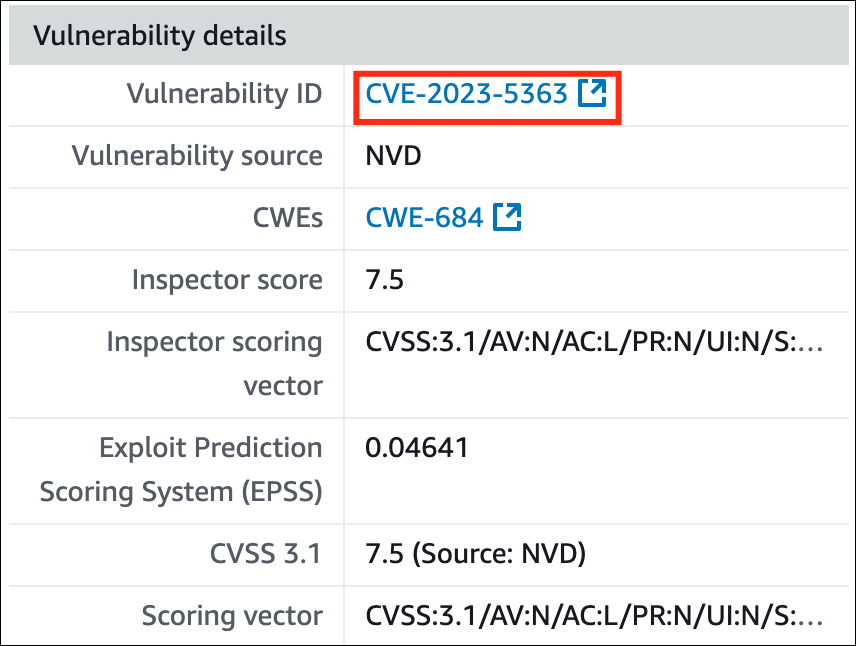
8. In Vulnerability details click on the Vulnerability ID to see the National vulnerability database.
**National vulnerability database:**
* **Government Repository:** Managed by the U.S. National Institute of Standards and Technology (NIST).
* **Vulnerability Information:** Contains detailed data on known software vulnerabilities.
* **CVE Identifiers:** Uses Common Vulnerabilities and Exposures (CVE) identifiers for each vulnerability.
* **Severity Ratings:** Provides severity scores using the Common Vulnerability Scoring System (CVSS).
* **Impact Analysis:** Describes potential impacts on confidentiality, integrity, and availability.
* **Remediation Guidance:** Offers recommendations for fixing or mitigating vulnerabilities.
* **Search Tools:** Includes tools for searching and analyzing vulnerabilities.
 > **Do you know?**
> Amazon Inspector for Lambda functions provides advanced security features, including dependency vulnerability scanning, Lambda layer analysis, and environment variable inspection. It enforces least privilege, checks runtime policies for compliance, and evaluates network accessibility to prevent public exposure. Inspector also maps findings to compliance frameworks like PCI-DSS, HIPAA, and GDPR, ensuring regulatory adherence for serverless applications.
#### Completion and Conclusion
1. You Have Successfully logged into AWS console.
2. You Have Successfully created inspector2.
3. You Have Successfully created lambda.
4. You Have Successfully triggered the lambda scanning.
5. You Have Successfully found the vulnerability using lambda scanning.
#### End Lab
1. **Sign Out** Of AWS Account.
2. You Have Successfully Completed The Lab.
3. Once You Have Completed The Steps, Click On **End Lab** From Your IP Lab Portal And Wait Till The Process Gets Completed.
## What gets checked
When you press **Check my work**, the platform verifies each of these:
* **Create an AWS Lambda Function** — Check whether a Lambda Function is created or not
* **Check Lambda Findings in InspectorV2** — Check whether lambda findings are present or not
## Related help
* [FAQs and Troubleshooting](/aws-saa/support/faqs-and-troubleshooting)
This documentation is built and hosted on [Mintlify](https://mintlify.com), a developer documentation platform.