> ## Documentation Index
> Fetch the complete documentation index at: https://cloud-architect.ipoint-labs.com/llms.txt
> Use this file to discover all available pages before exploring further.
# Understanding CloudFront Origin Groups
> Hands-on lab · 30m
Launch this lab in the IP Lab Portal, then follow the steps below in the AWS console.
Open IP Lab Portal
## Overview
### Lab Details
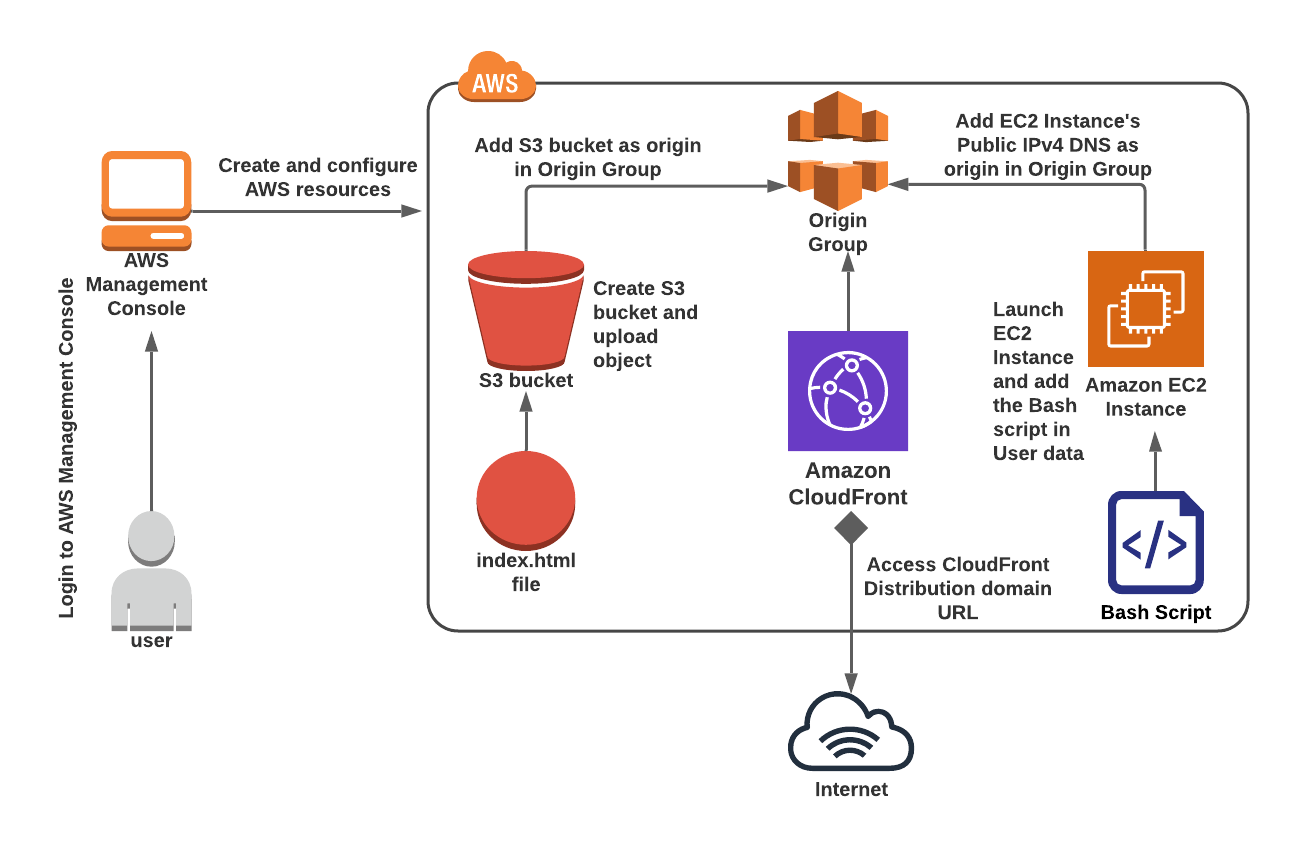
1. This lab walks you through the steps to create and configure an Amazon CloudFront distribution with origins from an EC2 instance and an S3 bucket.
2. Duration: **90 minutes**
3. AWS Region: **US East (N. Virginia) us-east-1.**
### Introduction
#### What is CloudFront?
* Amazon CloudFront is a content delivery network (CDN) offered by AWS.
* It provides a globally-distributed network of proxy servers that cache content closer to end-users.
* CDN improves access speed by reducing latency and minimizing the number of internet hops required to retrieve content.
* CloudFront works on a pay-as-you-go basis, allowing users to scale their content delivery as needed.
* It integrates with various origin servers, such as Amazon S3 and Amazon EC2, where the content is stored.
* When a request is made for content, CloudFront delivers it from the nearest edge server, reducing latency and improving performance.
* It supports both "Progressive" and "Streaming" delivery of content, allowing for optimized video streaming and dynamic content acceleration.
* CloudFront can be used to distribute web content, videos, software downloads, and other bulky media.
### Architecture Diagram
 ### Task Details
1. Sign in to the AWS Management Console.
2. Create S3 Bucket
3. Upload a file to an S3 bucket
4. Make the objects publicly accessible
5. Creating CloudFront Distribution
6. Launching an EC2 Instance
7. Add EC2 as the Origin and create Origin Group
8. Test the Origin group
9. Deleting AWS Resources.
### Launching Lab Environment
1. To launch the lab environment, Click on the **Start Lab** button.
2. Please wait until the cloud environment is provisioned. It will take less than a minute to provision.
3. Once the Lab is started, you will be provided with **IAM user name**, **Password**, **Access** **Key**, and **Secret** **Access** **Key**.
> **Note** : You can only start one lab at any given time
## Files you need
Download these before you start — the lab cannot be completed without them.
* [Download File](/images/saa-files/understanding-cloudfront-origin-groups/download-file.html)
## Lab guide
### Lab Steps
#### Task 1: Sign in to AWS Management Console
1. Click on the **Open Console** button, and you will get redirected to AWS Console in a new browser tab.
2. On the AWS sign-in page,
* Leave the Account ID as default. Never edit/remove the 12-digit Account ID present in the AWS Console. Otherwise, you cannot proceed with the lab.
* Now copy your **Username** and **Password** in the Lab Console to the **IAM Username and Password** in AWS Console and click on the **Sign-in** button.
3. Once Signed In to the AWS Management Console, make the default AWS Region as **US East (N. Virginia) us-east-1.**
#### Task 2: Create S3 Bucket
1. Make sure you are in the **US East (N. Virginia) us-east-1** Region.
2. Navigate to the **Services** menu at the top. Click on **S3** in the **Storage** section.
3. In the S3 dashboard, click on the **Create bucket** button and fill in the bucket details.
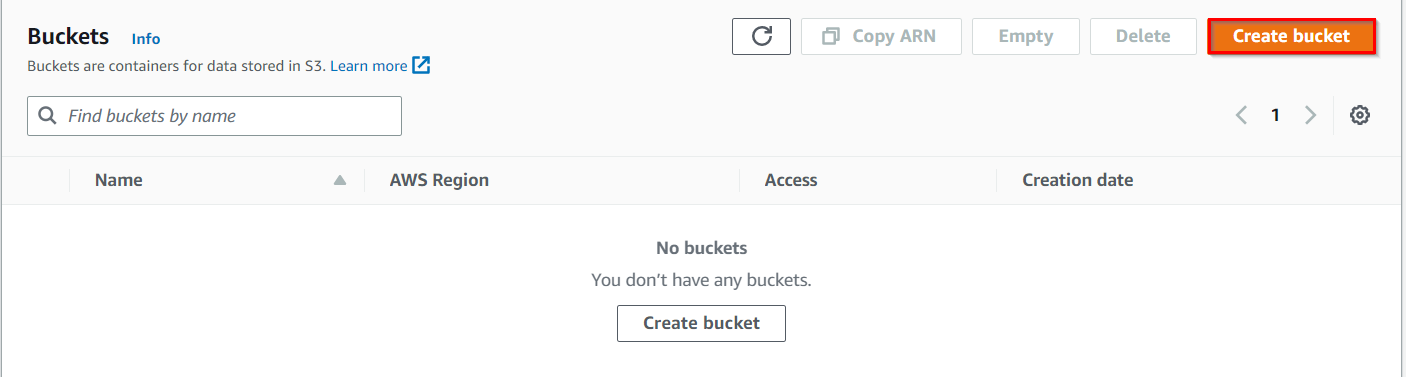 * Bucket name: Enter **whizlabs1234567**
* **Note:** S3 Bucket names are globally unique, choose a name that is available.
* Region: Select **US East (N. Virginia) us-east-1.**
* Object Ownership: **ACLs disabled**
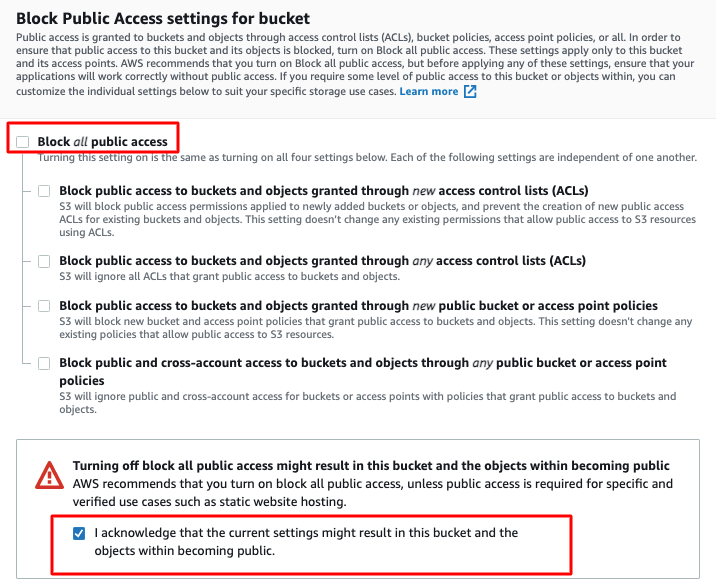
* Scroll down to **Block Public Access settings for bucket** and **Uncheck** the **Block all Public Access** and **acknowledge** the change.
 * No need to change anything further, just click on the **Create bucket** button.
#### Task 3: Upload a file to an S3 bucket
1. Enter the S3 bucket by clicking on your bucket name.
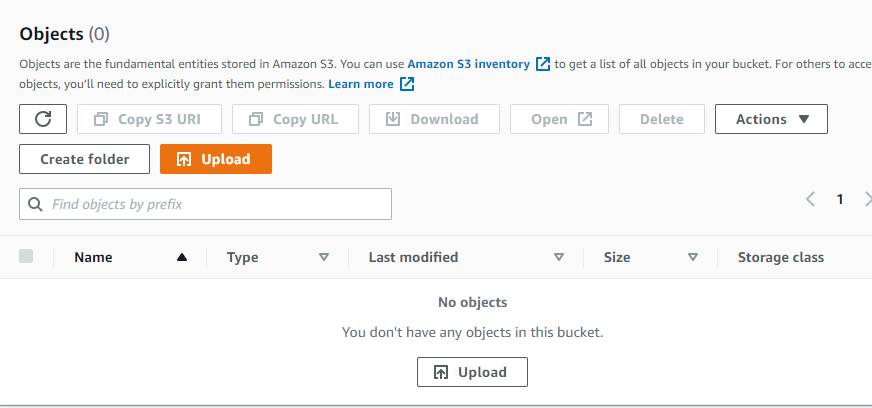 2. Download our sample index.html file from [**here**](https://labresources.whizlabs.com/1b04ccccd92a080ad0ed3fa9a8add0cc/index.html).
3. To upload a file to our S3 bucket,
* Click on **Upload**.
* Click on **Add files**.
* Browse for your local image or the image we provided and select it.
* Click on the **Upload** button.
* You can watch the progress of the upload from within the transfer panel at the bottom of the screen.
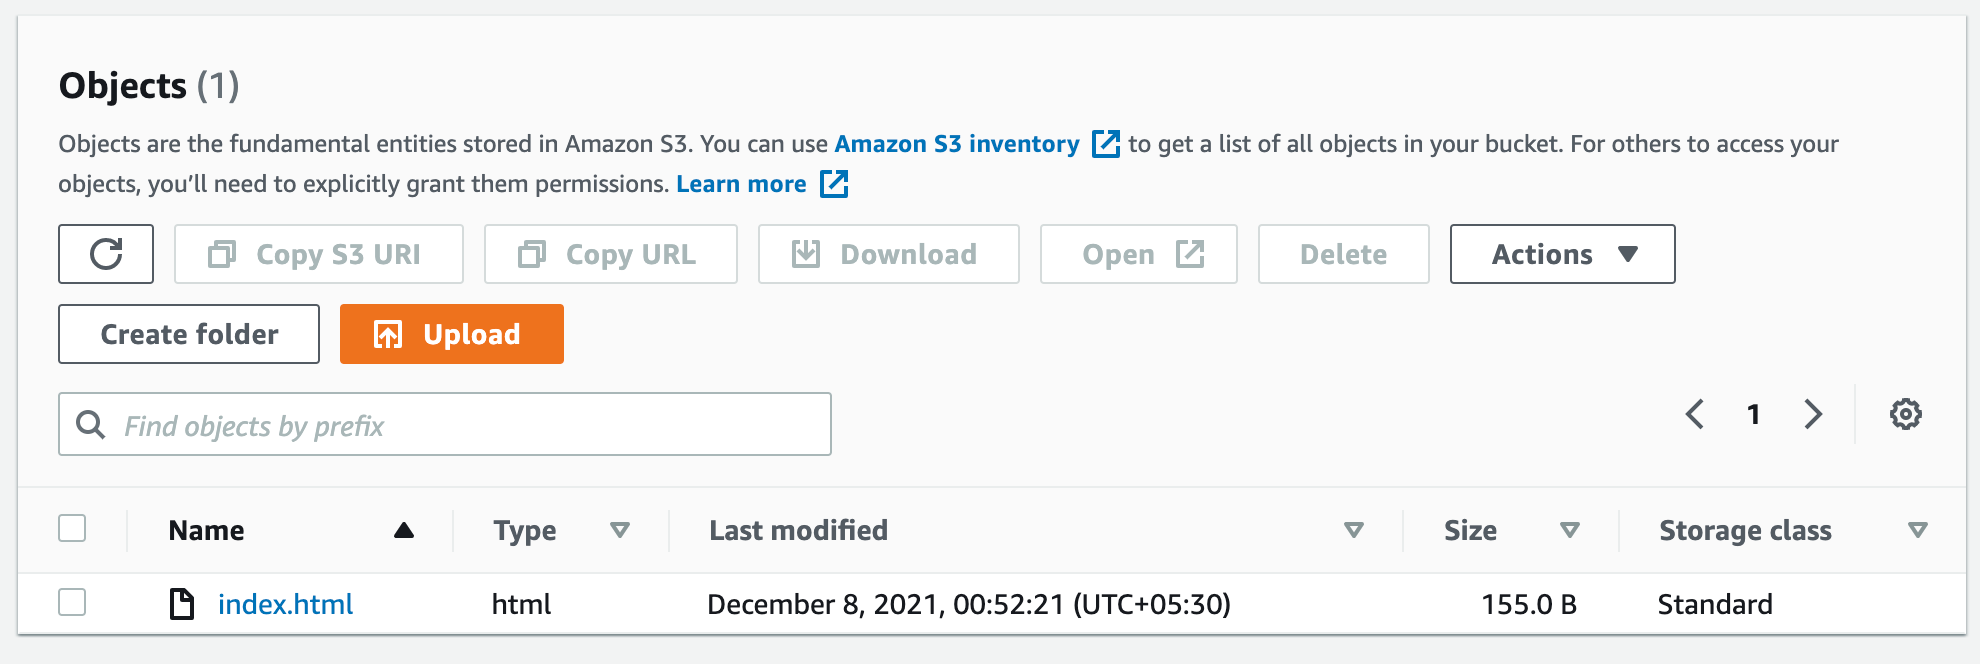
* Once your file has been uploaded, click on **Close** and you can see an object in the bucket.
* **Note: Uploading files other than index.html will result in validation failure. Please upload the same index.html file only.**
 #### Task 4: Make the objects publicly accessible
In this task, we are going to configure the permissions of the S3 bucket to allow public access to the uploaded objects. This step ensures that the content stored in the S3 bucket can be accessed by CloudFront and served to end-users.
1. Click the **Permissions** tab to configure your bucket.
* In the **Permissions** tab, **Edit** the **Bucket Policy**.
* You will be able to see a Blank policy editor.
* Before creating the policy, you will need to copy the **ARN** (Amazon Resource Name) of your bucket.
* Copy the **ARN** of your bucket to the clipboard. It is displayed at the top of the policy editor. It looks like **ARN:“arn:aws:s3:::your-bucket-name**".
* In the policy below, update the bucket ARN on the Resource key-value and copy the policy code.
2. Copy the bucket policy.
```plaintext theme={null}
{
"Id": "Policy1",
"Version": "2012-10-17",
"Statement": [
{
"Sid": "Stmt1",
"Action": [
"s3:GetObject"
],
"Effect": "Allow",
"Resource": "replace-this-string-with-your-bucket-arn/*",
"Principal": "*"
}
]
}
```
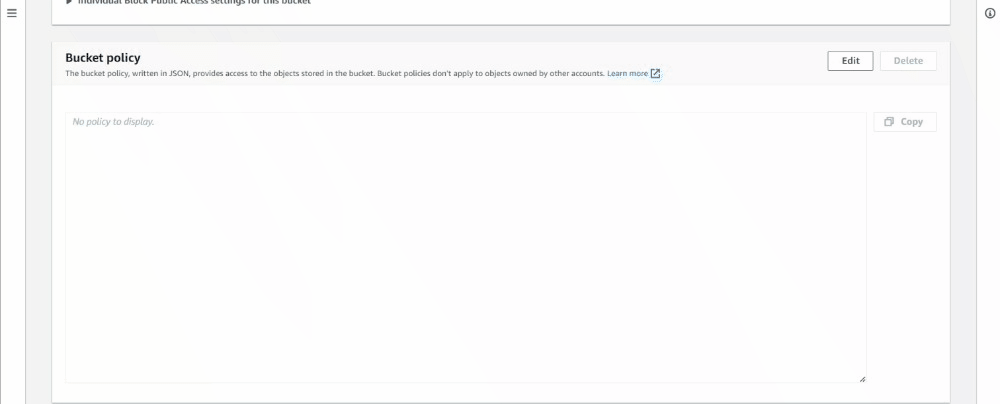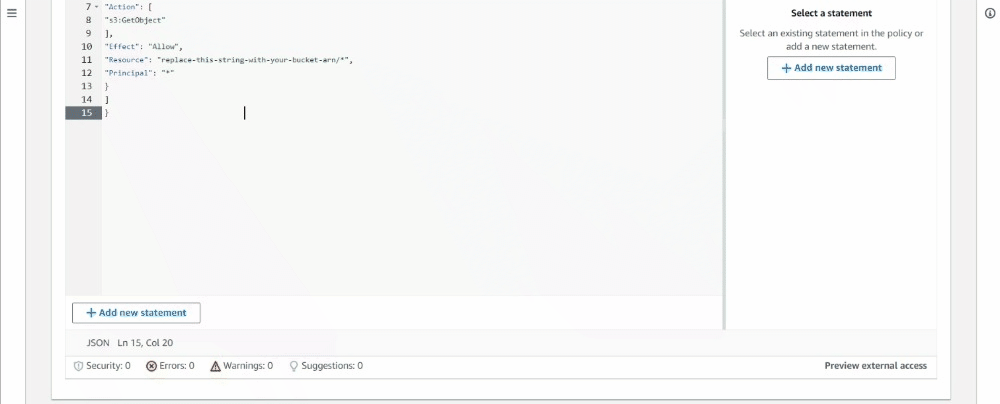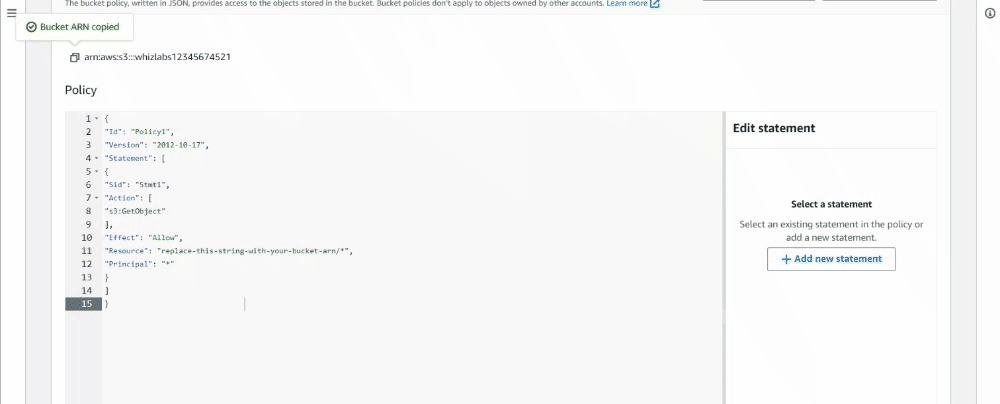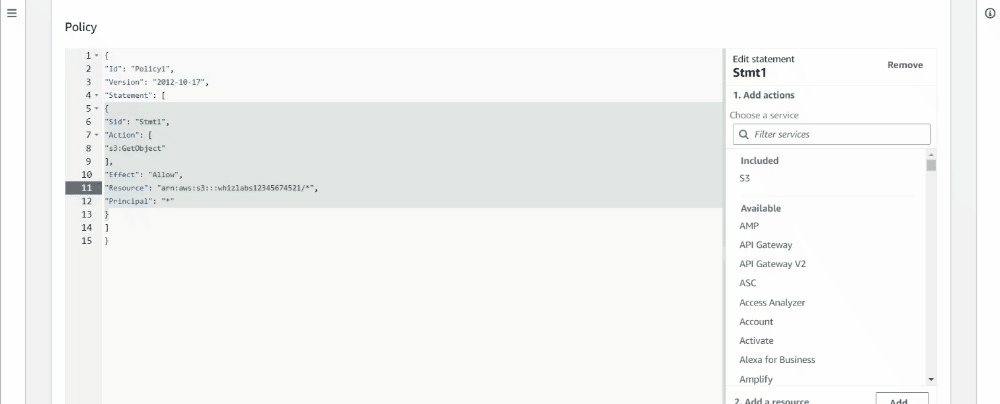 3. Click on **Save changes**.
#### Task 5: Creating CloudFront Distribution
1. Select **CloudFront** under **Networking and Content Delivery** from the **Services** menu.
2. Navigate to the left side and select **Distributions** tab.
3. Now click on the **Create distribution** button.
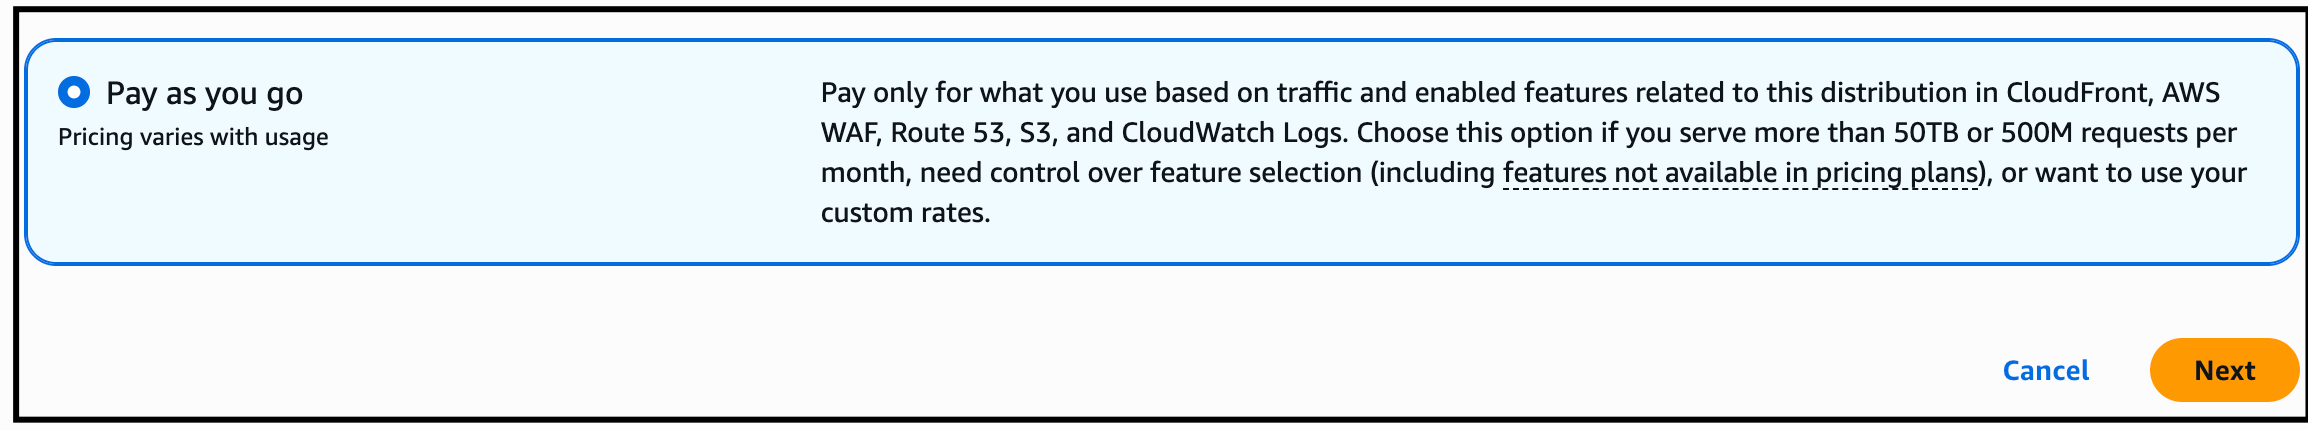
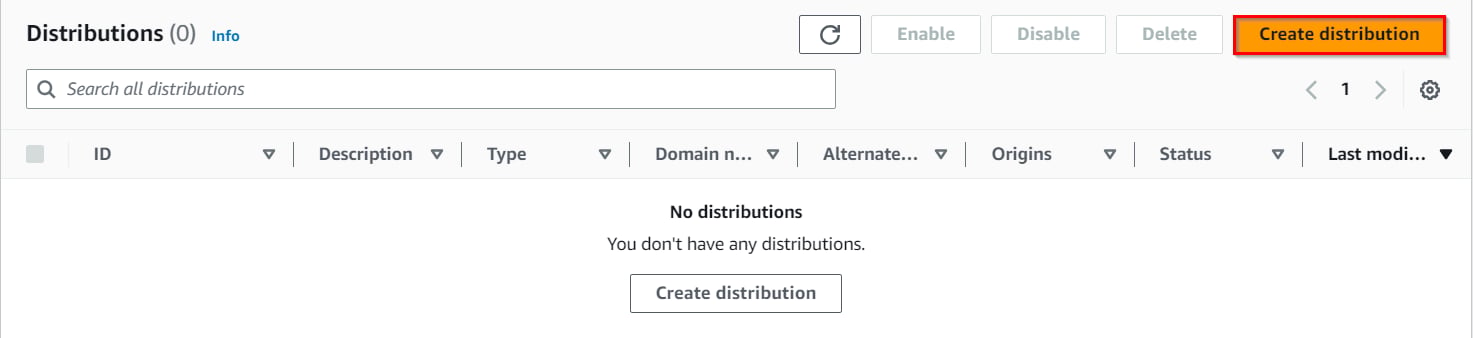 Choose a plan, select **Pay as you go,** click on **Next.**
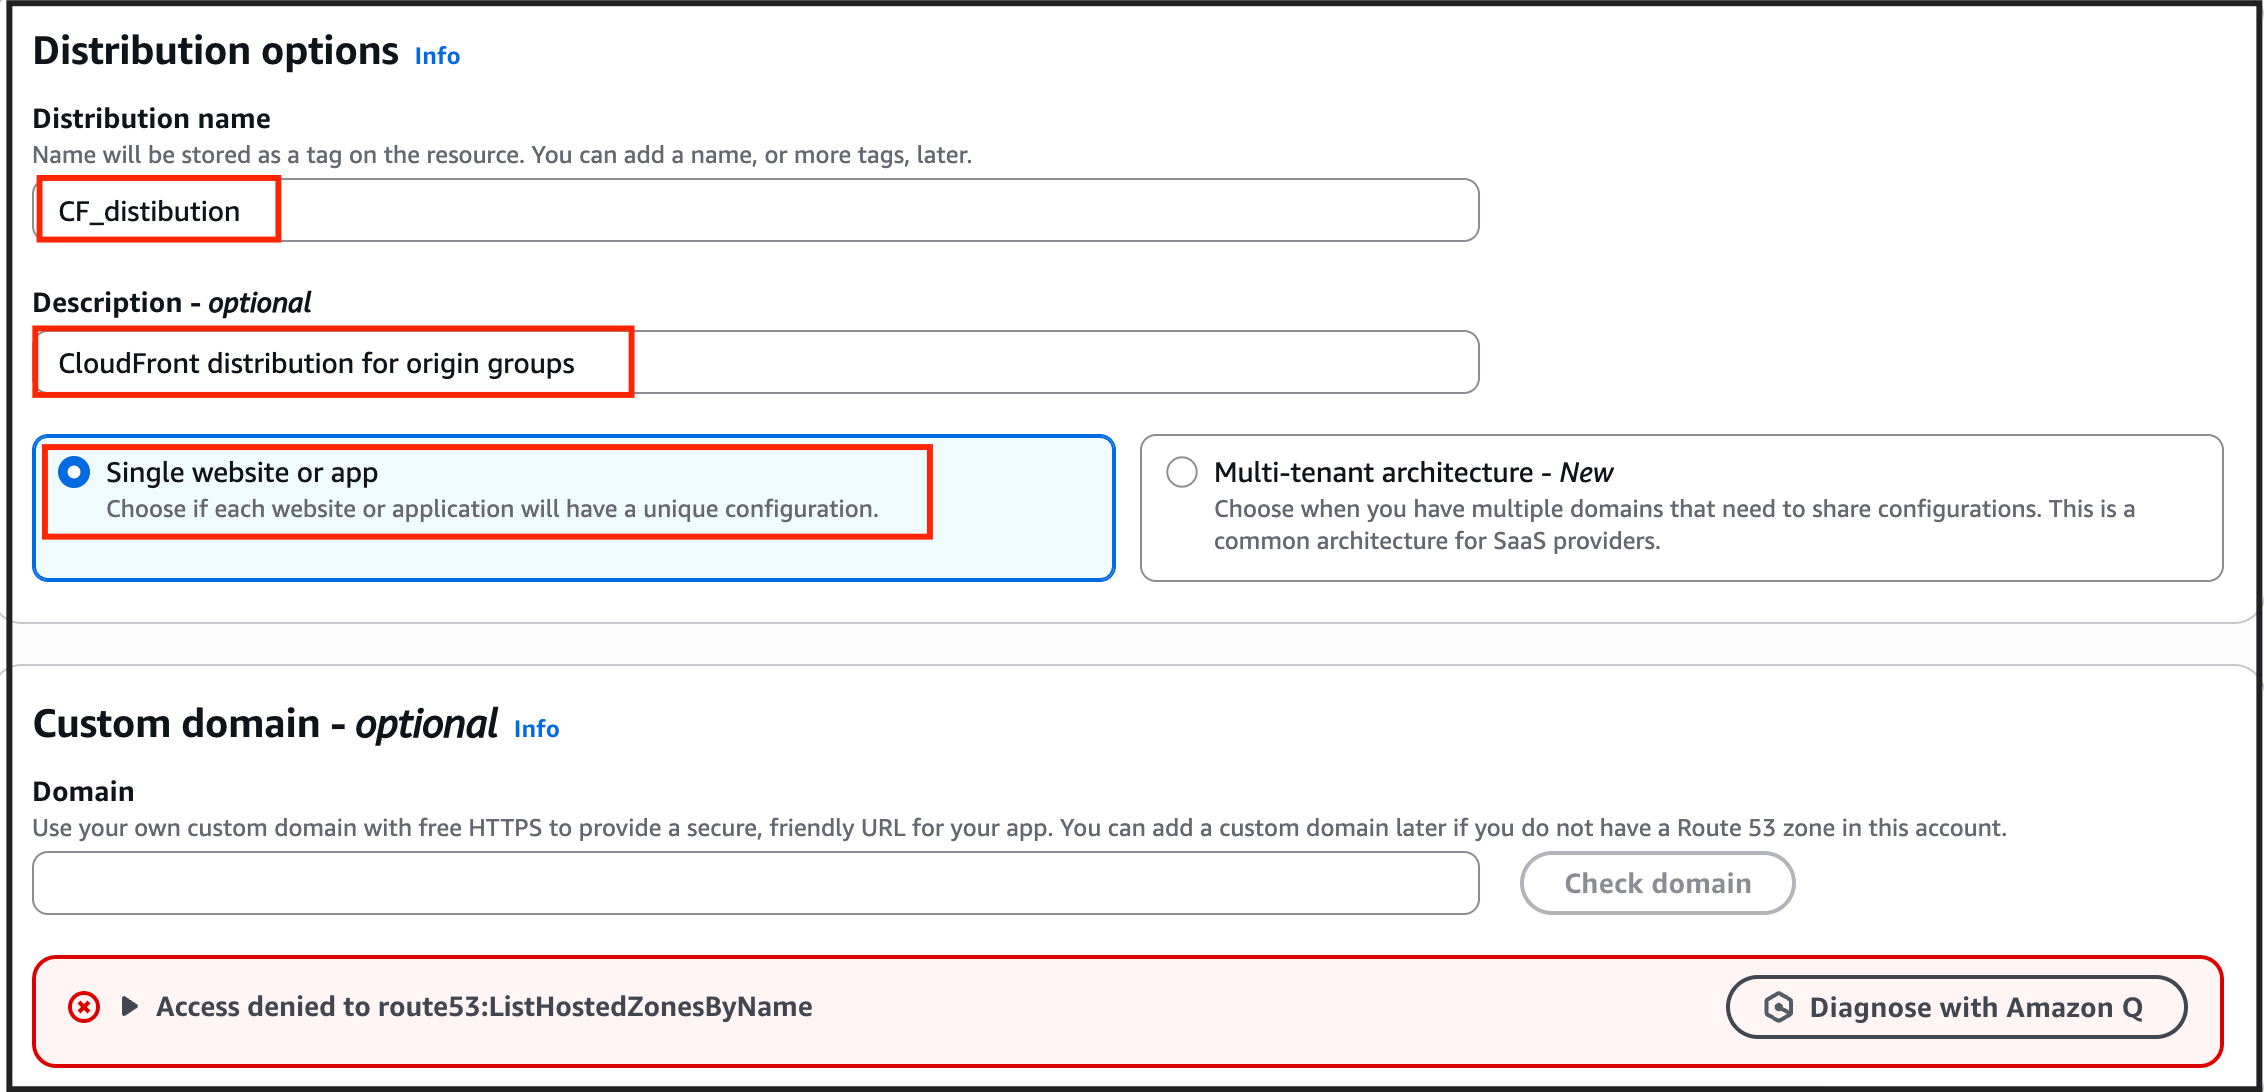
 4. Now, configure the distribution as follows
Under Distribution options,
* Distribution name : **CF\_Distribution**
* Description : CloudFront distribution for origin groups
* Choose : Single website or app
* Custom domain : optional leave it.
 * Click on the **Next** button.
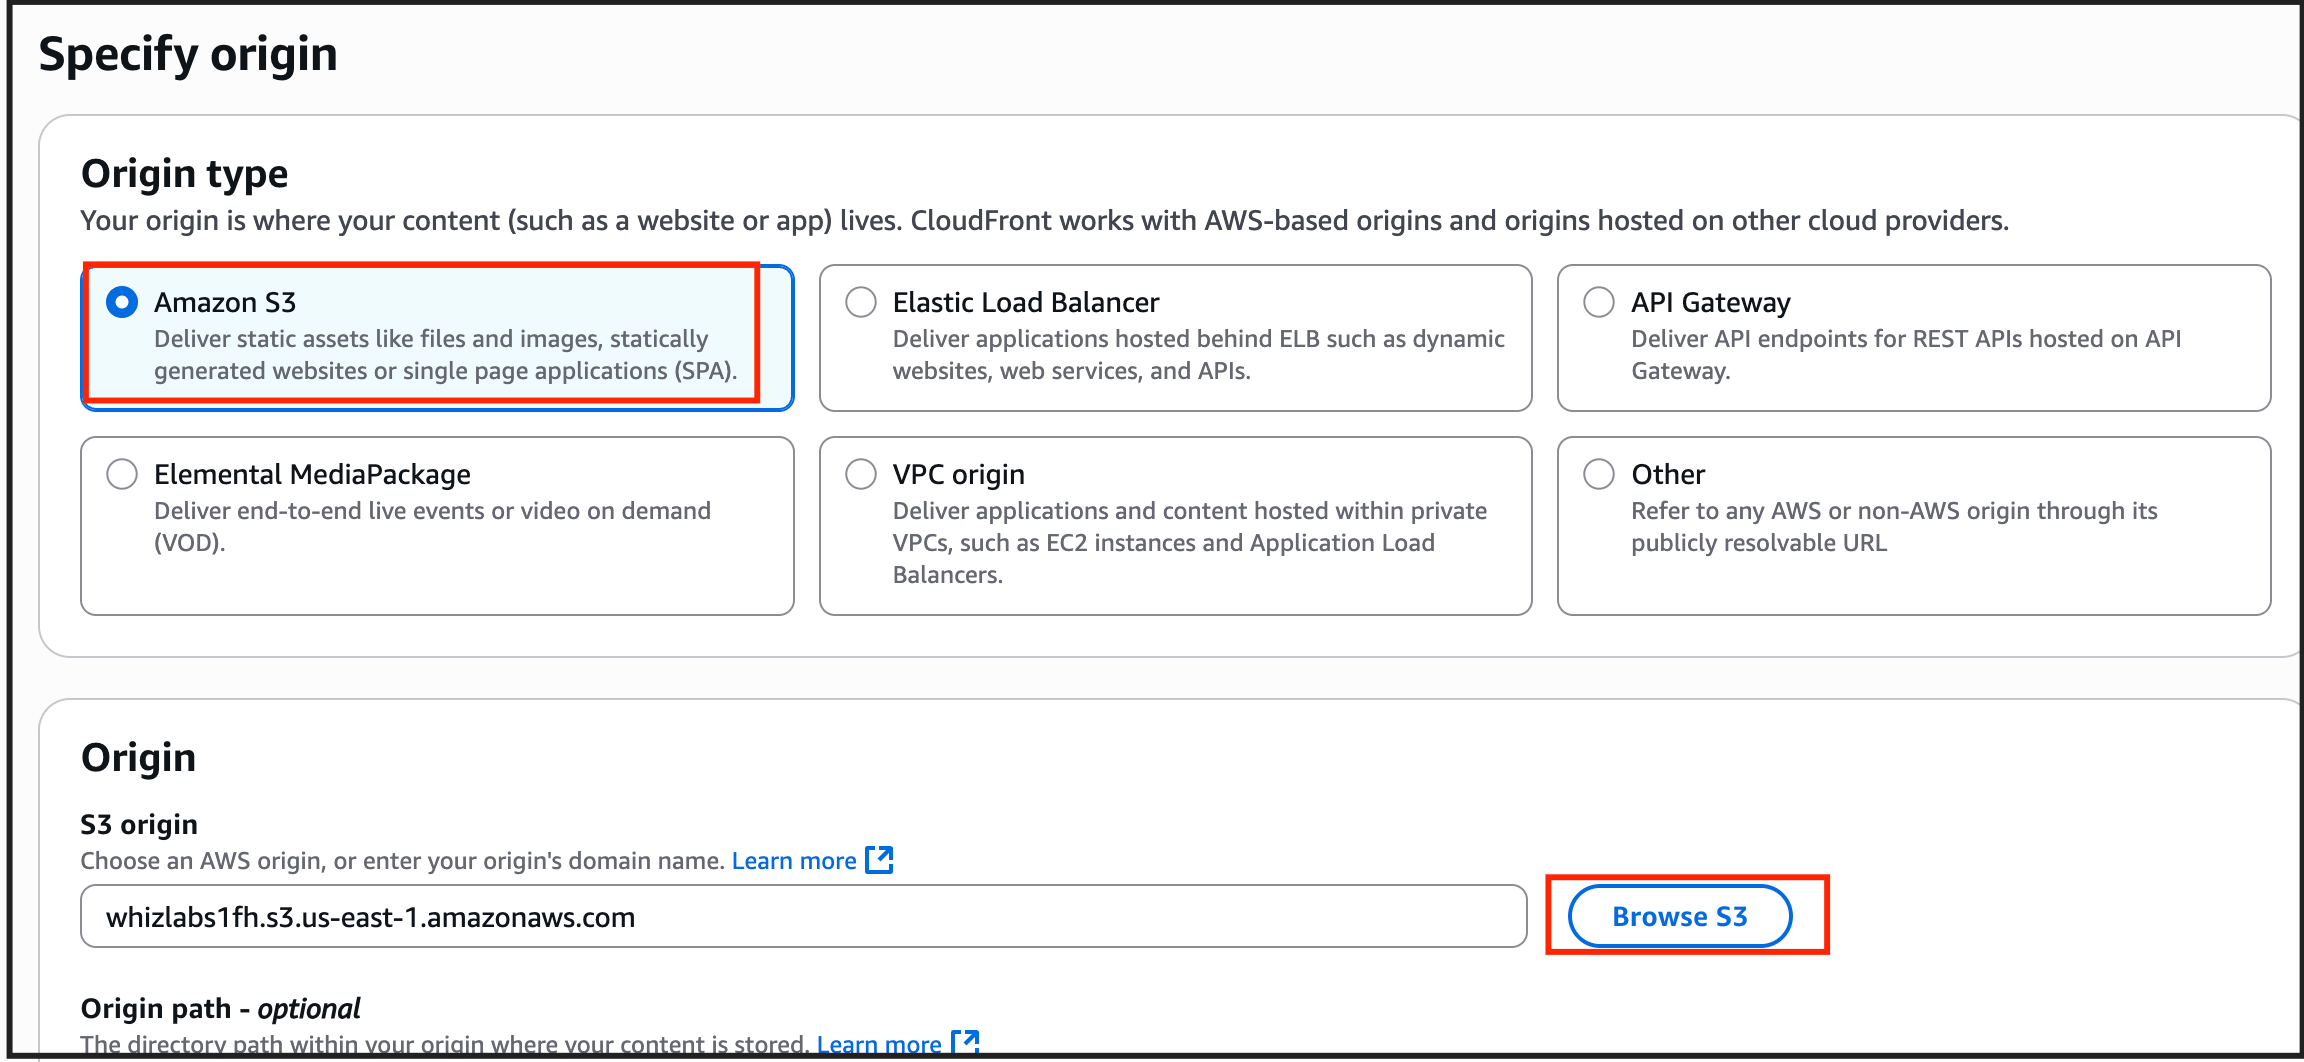
* Origin type : Select **Amazon** **S3**
* S3 origin : Click on the **Browse** **S3** button and select the previously created bucket.
 * Leave other options as it is and click on the **Next** button.
5. For Web Application Firewall (WAF) select **Do not enable security protections**
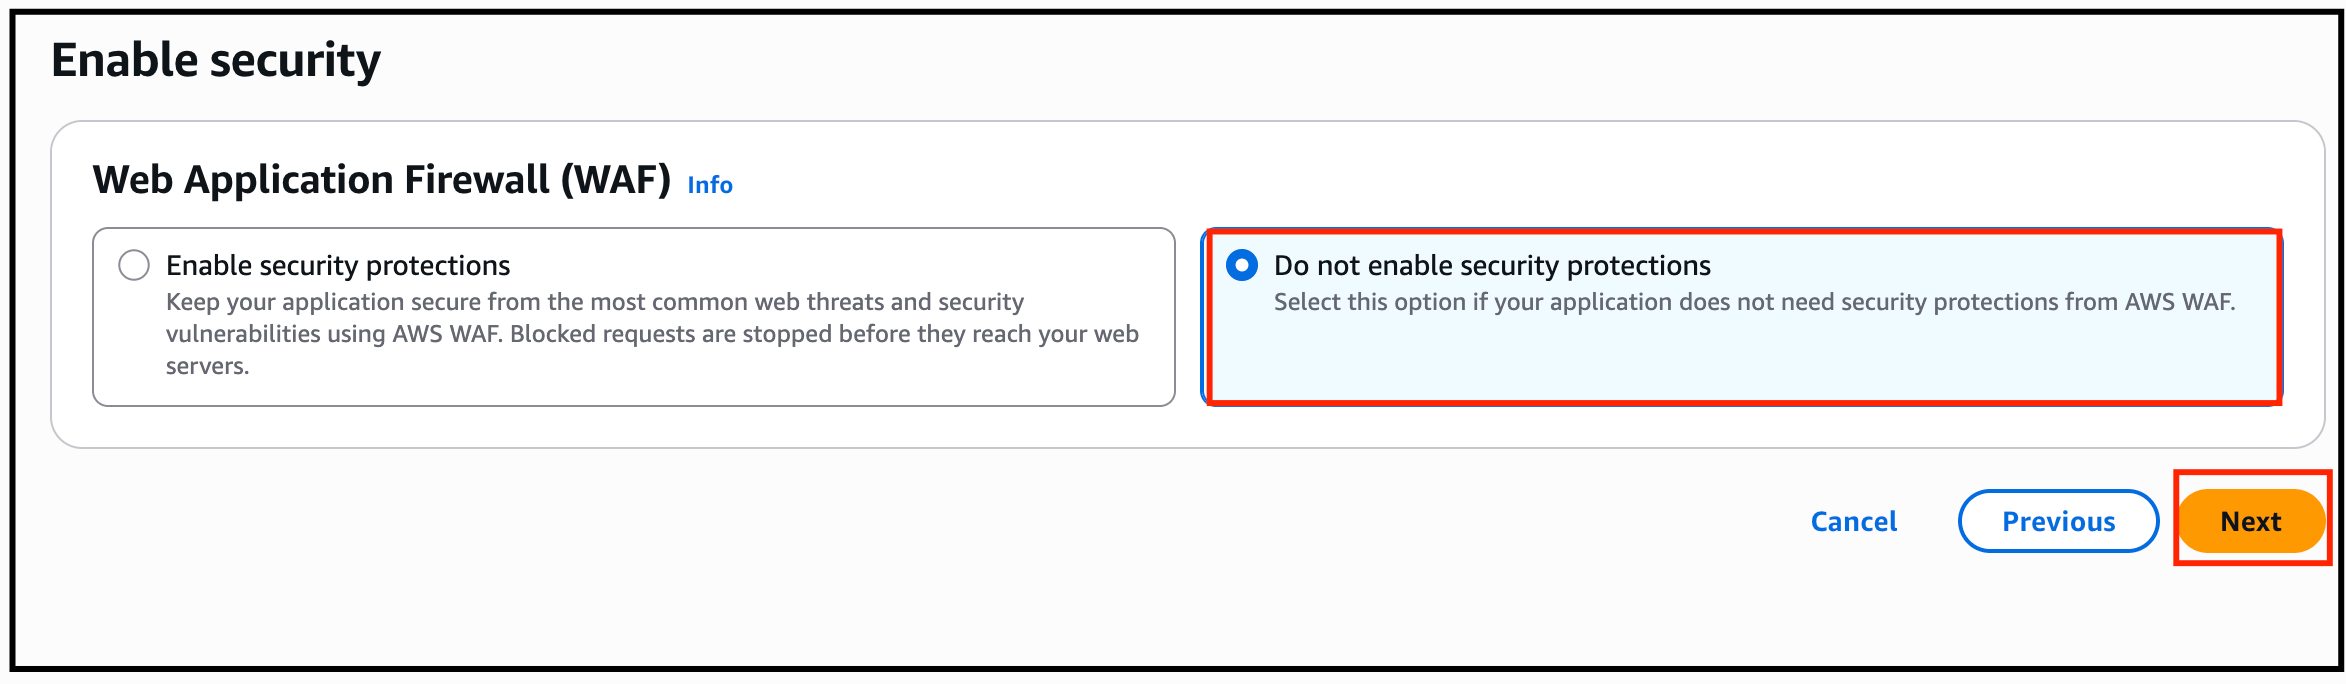 6. Click on the **Next** button, scroll down, and lastly click on the **Create Distribution** button.
7. You can see that CloudFront is **enabled** and **deployed**
* **Note:** This process will take around **10–15** minutes.
* You can see the Deploying status changed and the **last modified time** is present.
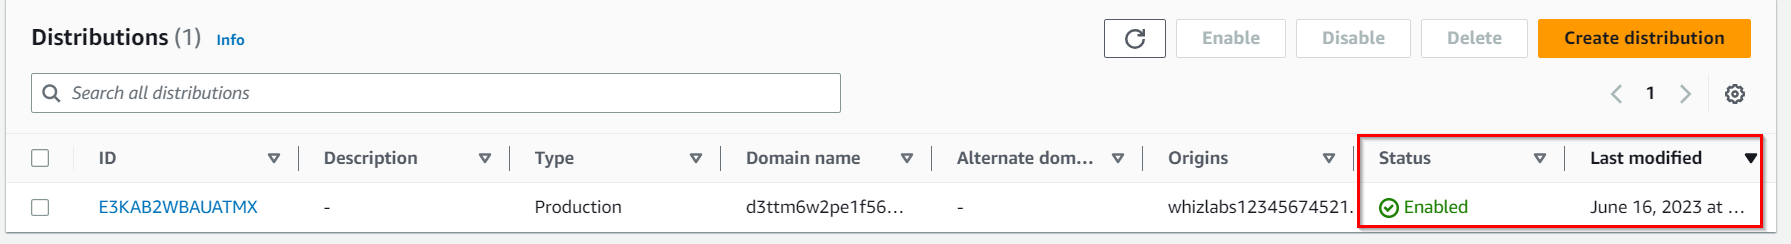 8. The domain name that Amazon CloudFront assigns to your distribution appears in the list of distributions.
9. Copy and paste the domain of the CloudFront distribution in the new tab of your browser.
10. **It will throw an error because the S3 bucket is having object index.html and to access that enter the same in the path.**
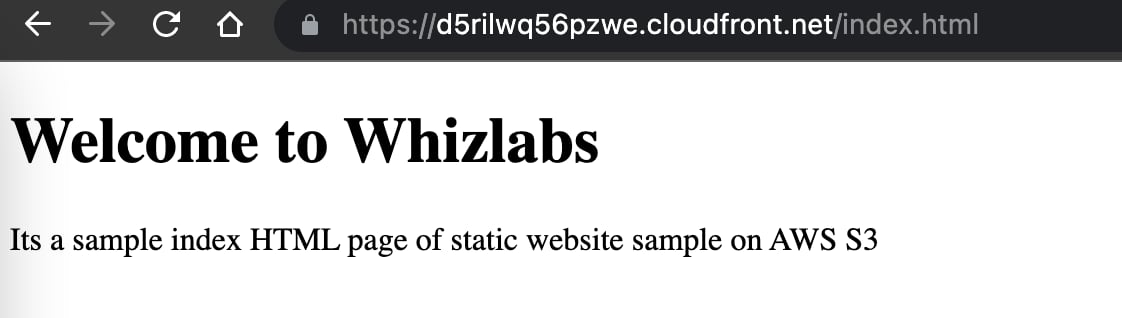
11. Copy and paste the domain of CloudFront distribution in the new tab of your browser and add **/index.html** in the URL.
12. It should display the index.html page present in the S3 bucket.
 #### Task 6: Launching an EC2 Instance
In this task, we are going to launch an Amazon EC2 instance. The EC2 instance will serve as another origin for the CloudFront distribution, alongside the S3 bucket.
1. Make sure you are in **US East (N. Virginia) us-east-1** Region.
2. Navigate to EC2 by clicking on the **Services** menu in the top, then click on **EC2** in the **Compute** section.
3. Navigate to **Instances** from the left side menu and click on **Launch instance** button.
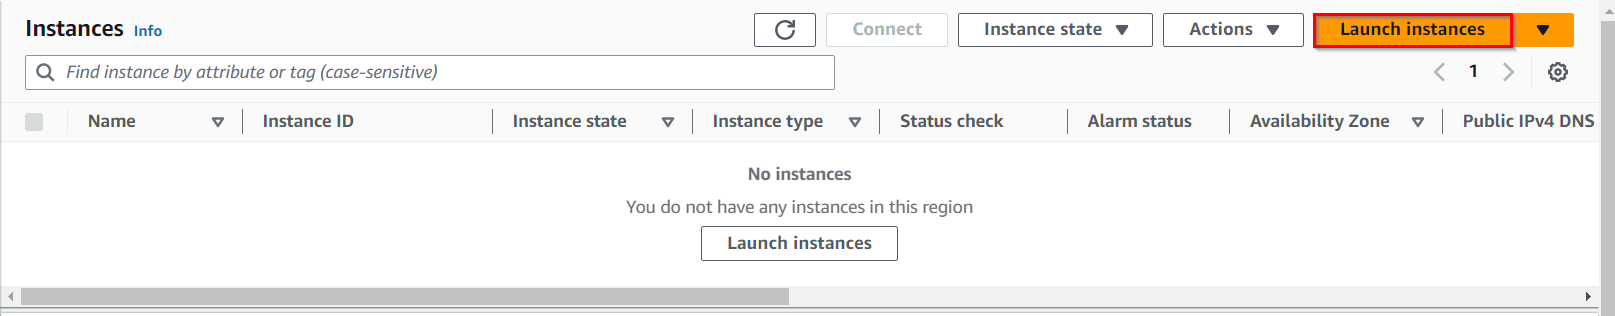 4. Under the **Name and tags** section : Name – **MyEC2server**
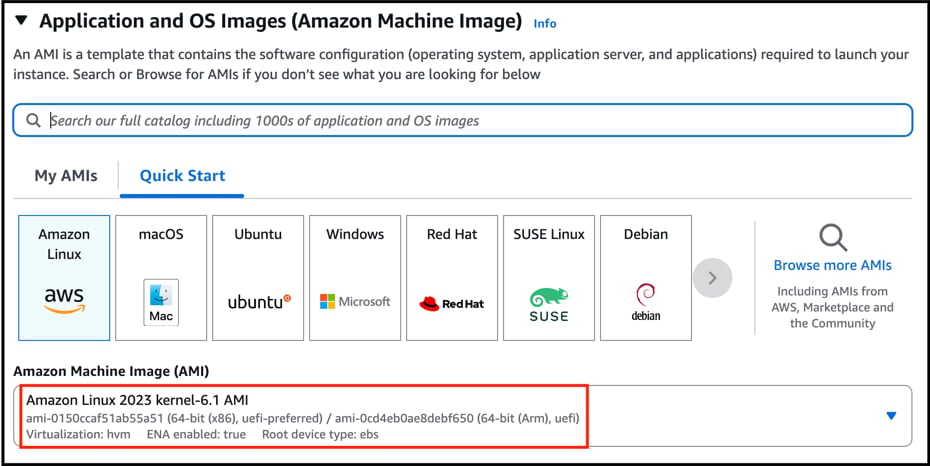
5. **Choose an Amazon Machine Image (AMI):** Search for **Amazon Linux 2023 kernel-6.1 AMI.**
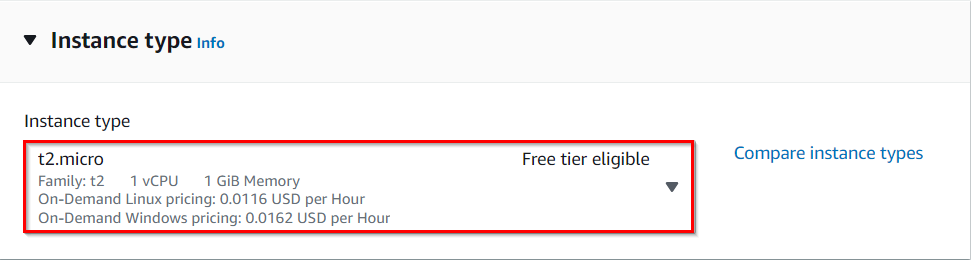
 6. **Choose an Instance Type:** select **t2.micro.**
 7. **Keypair Details:** No need to generate Keypair for this instance, you can **proceed without a keypair.**
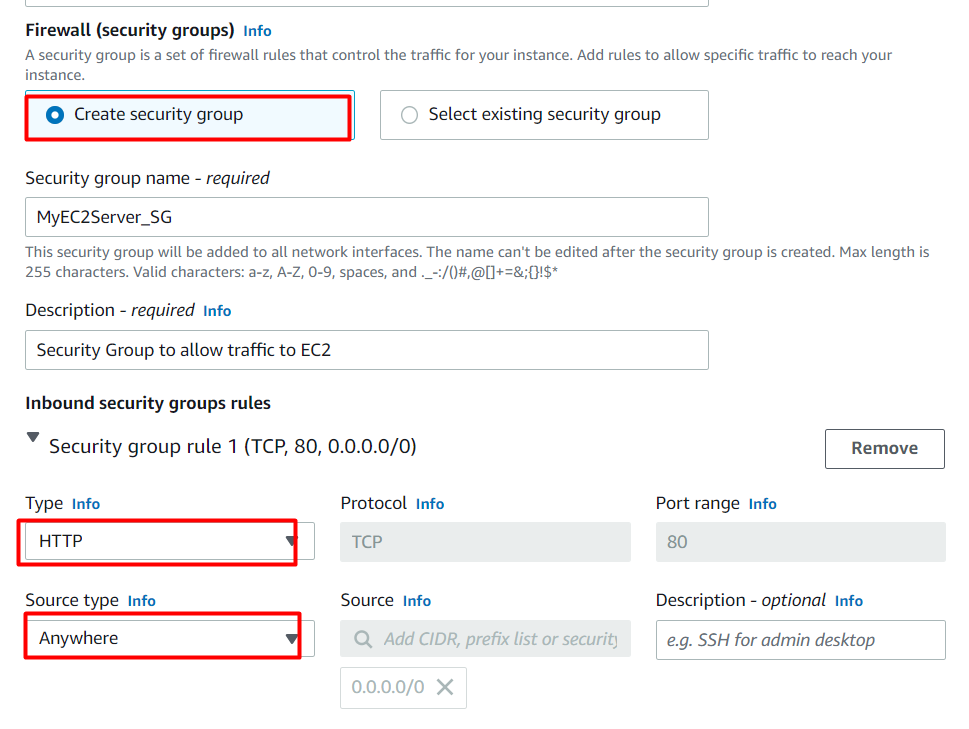
8. Under the **Network Settings** section **:**
* Click on **Edit** button.
* Leave the default VPC as it is.
* Subnet\*\*:\*\* default subnet
* Auto-assign public IP: select **Enable**
* Firewall (security groups) : Select **Create security group**
* Security group name : **MyEC2Server\_SG**
* Description : **Security Group to allow traffic to EC2**
* For HTTP:
* Choose Type: Select **HTTP**
* Source: Select **Anywhere**
 9. **Click on Advanced Details :** Scroll to the end and paste the below script in the **user data section.**
```plaintext theme={null}
#!/bin/bash
dnf update -y
dnf install -y httpd
systemctl enable httpd
systemctl start httpd
cat > /var/www/html/index.html <Hello, this index.html page from $(hostname -f)
EOF
cat > /var/www/html/index2.html <Hello, this index2.html page from $(hostname -f)
EOF
chmod 644 /var/www/html/index.html
chmod 644 /var/www/html/index2.html
systemctl restart httpd
```
10. Keep everything else as default and click on the **Launch instances** button.
11. After 1–2 minutes, the **Instance State** will change to **running**.
12. **Note down the sample Public IPv4 DNS Address of the EC2 instance.**
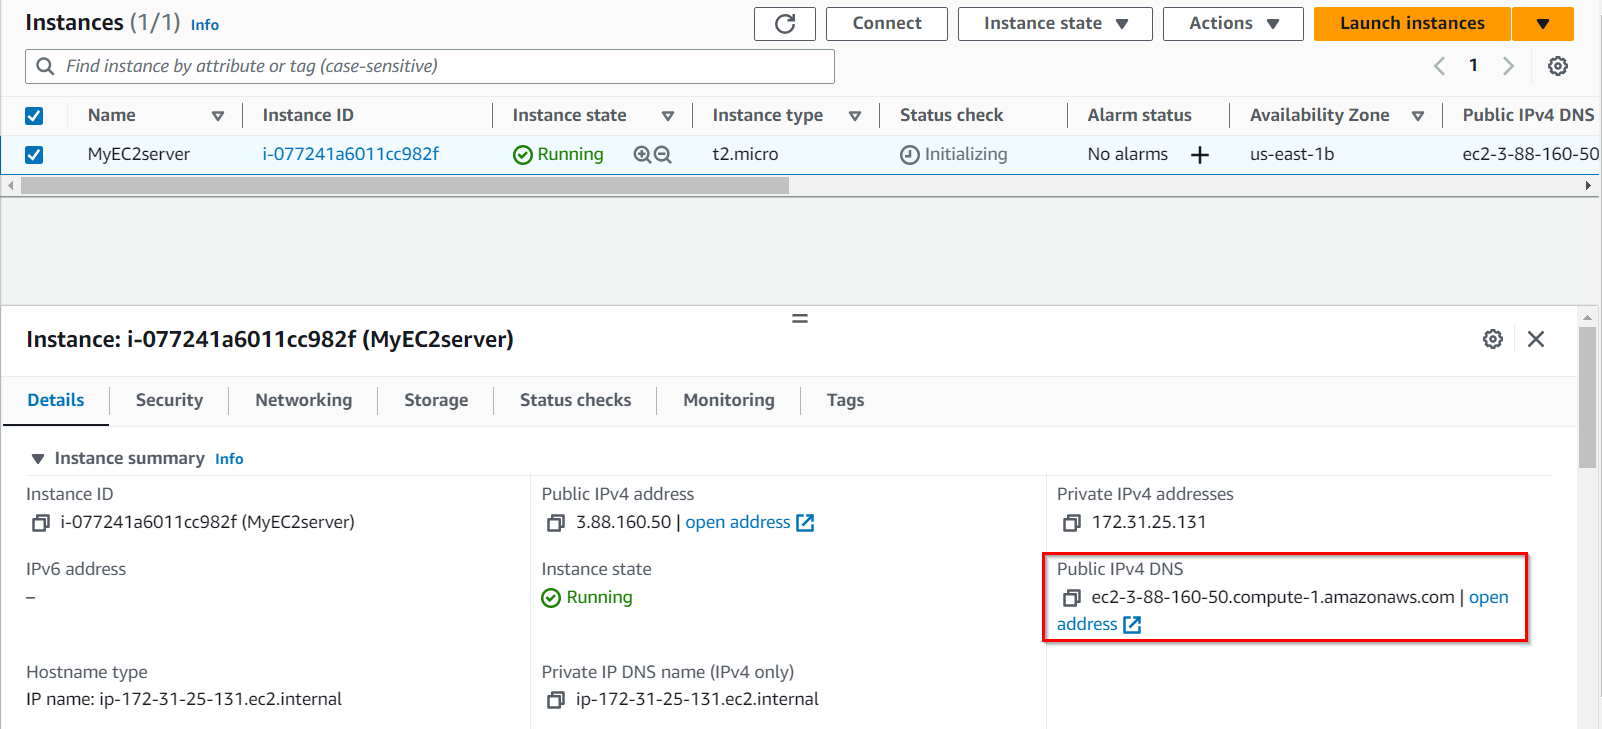 13. Try accessing the Public IPv4 DNS address by pasting in the browser and adding **/index.html** at the end, you will see the response as present below.
 14. Now update the URL by modifying /index.html to **/index2.html**
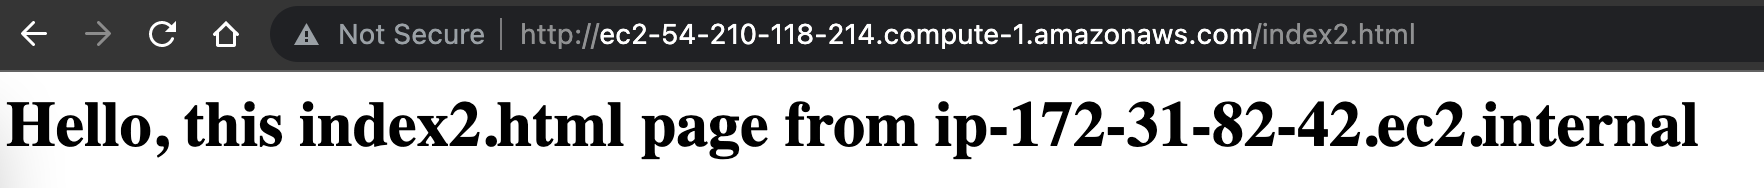 #### Task 7: Add EC2 as the Origin and create Origin Group
In this task, we are going to add the EC2 instance as an additional origin to the CloudFront distribution and create an origin group. This allows CloudFront to distribute the content from both the S3 bucket and the EC2 instance, providing redundancy and failover capabilities.
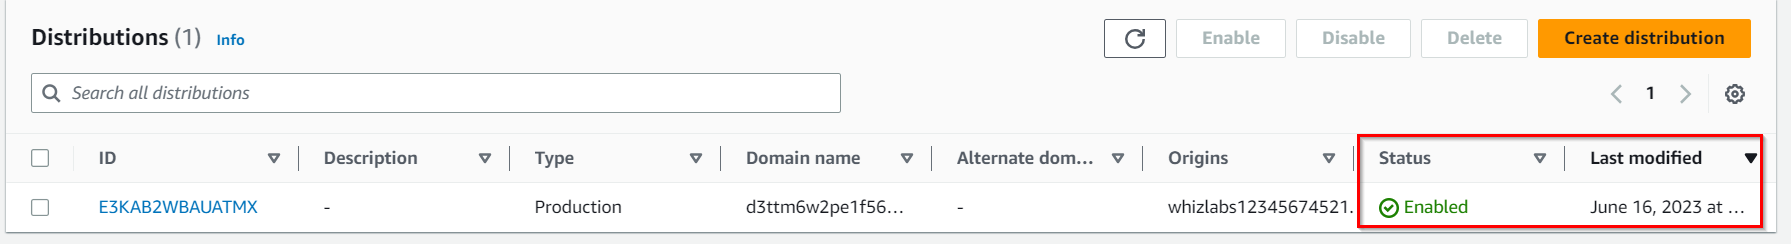
1. Before adding EC2 Instance as Origin, make sure CloudFront distribution is having Enabled status
2. Once the CloudFront distribution is having Enabled status, click on the ID to add the origin.
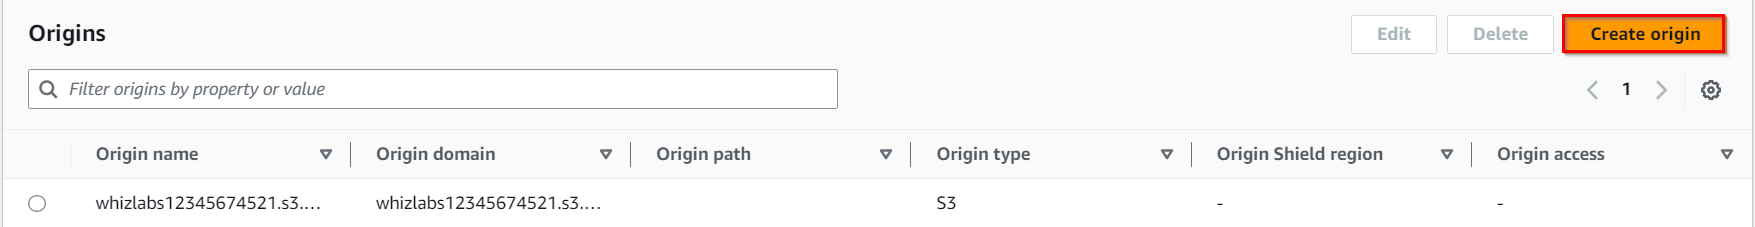
 3. Switch to the **Origins** tab and click on the **Create origin** button.
 4. In the first option **Origin domain**, paste the copied Public IPv4 DNS of EC2 Instance.
5. Once pasted, all the details of the Origin domain will be listed below.
6. Protocol : Select **HTTP Only**
7. Keep all the options as default and click on the **Create origin** button.
8. Now there are two origins present.
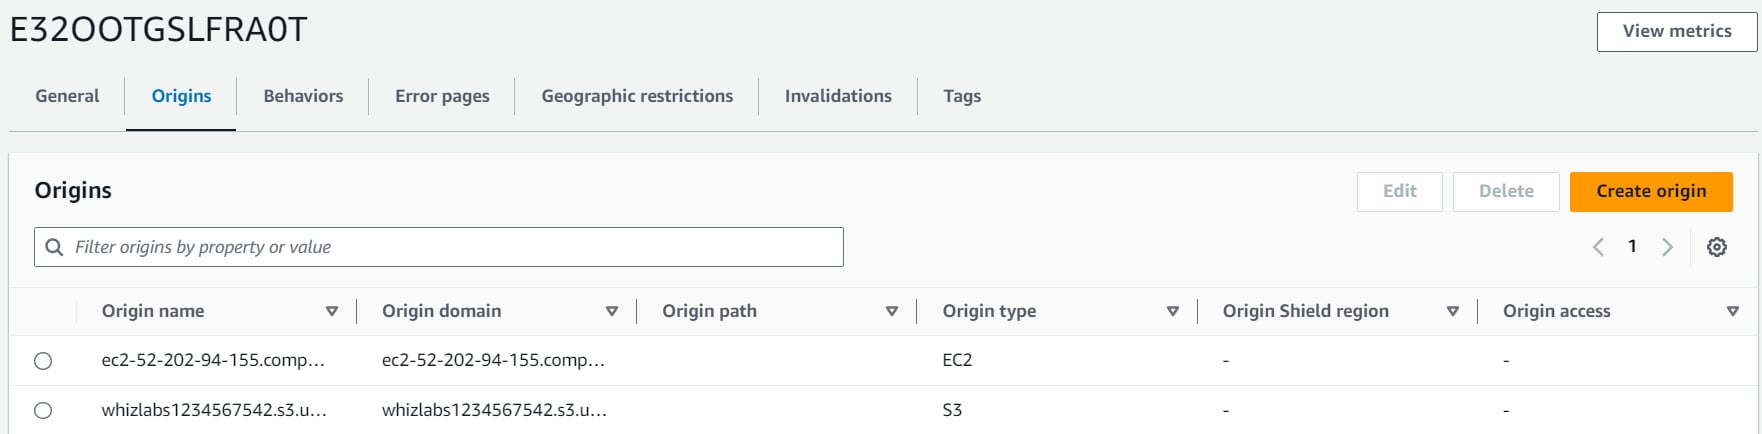 9. Go back to the General tab, you will see these changes are getting deployed.
10. Wait for 5-10 minutes until you see the Deploying status changes and the Last modified time is present.
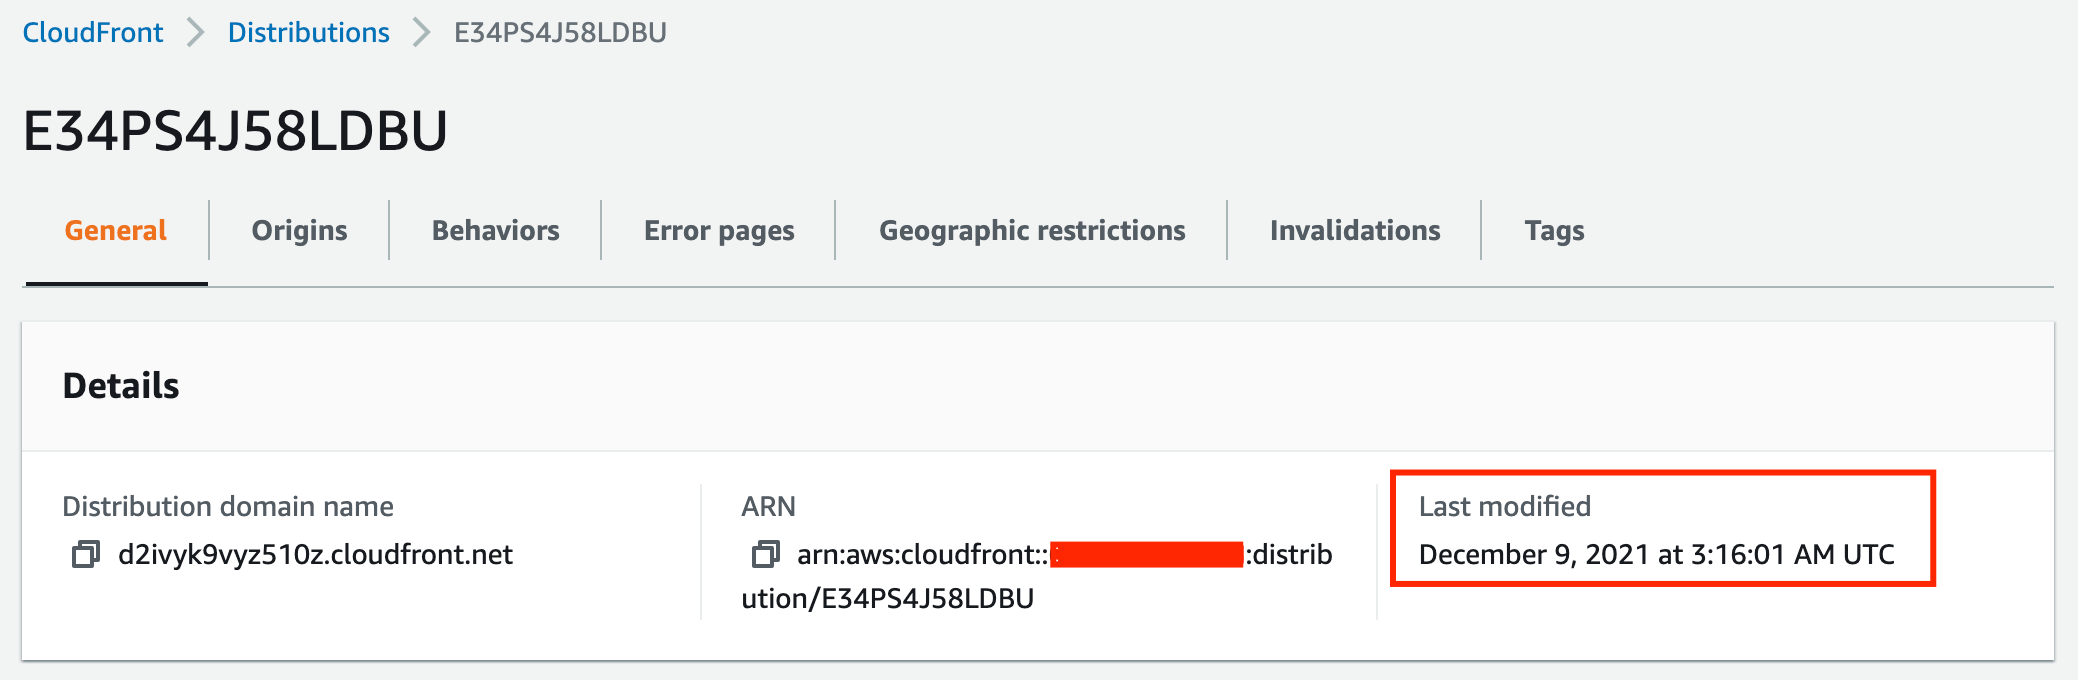 11. Switch to **Origins** tab and scroll below and click on the **Create origin group** button.
12. Select the Public IPv4 DNS of EC2 Instance and click on the **Add** button.
13. Similarly, select the S3 Bucket endpoint and click on the **Add** button.
14. Once both the Origins are added, give a name as **Whiz-Origin-Group** in the next field.
15. For the failover criteria, Select **404 Not found** error code present.
16. Once done, click on the **Create origin group** button.
17. Origin group is now created.
18. Go back to the **General** tab, you will see these changes are getting deployed.
19. Wait for 5-10 minutes until you see the Deploying status changes and the **Last modified time** is present.
20. Now Switch to the **Behaviors** tab.
21. Select the present behavior and click on the **Edit** button.
22. On the **Edit behavior** page, for the **Origin and origin groups** option, select the present Origin Group i.e. **Whiz-Origin-Group** from the dropdown.
23. In Cache key and origin requests, select **CachingOptimized**
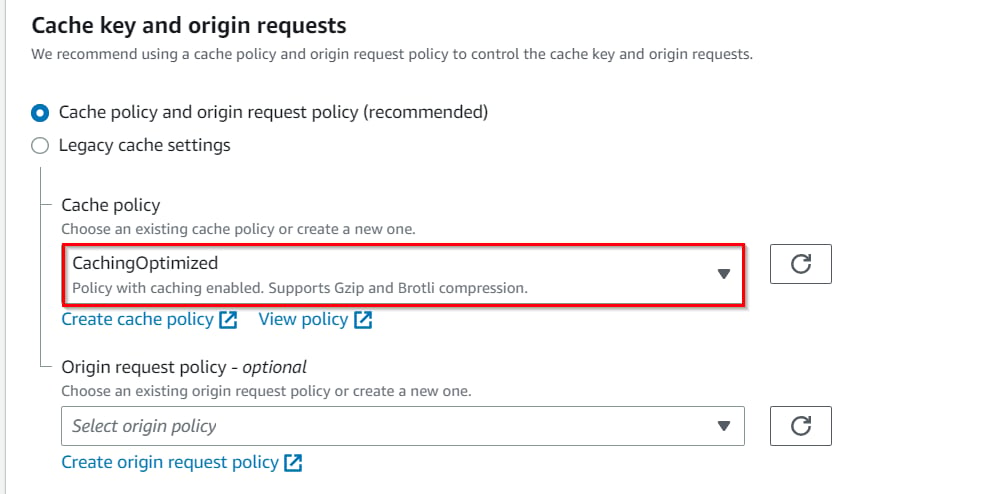 19. Scroll to the end of the page and click on the **Save changes** button.
20. The default cache behavior is now updated to the Origin group.
21. Go back to the **General** tab, you will see these changes are getting deployed.
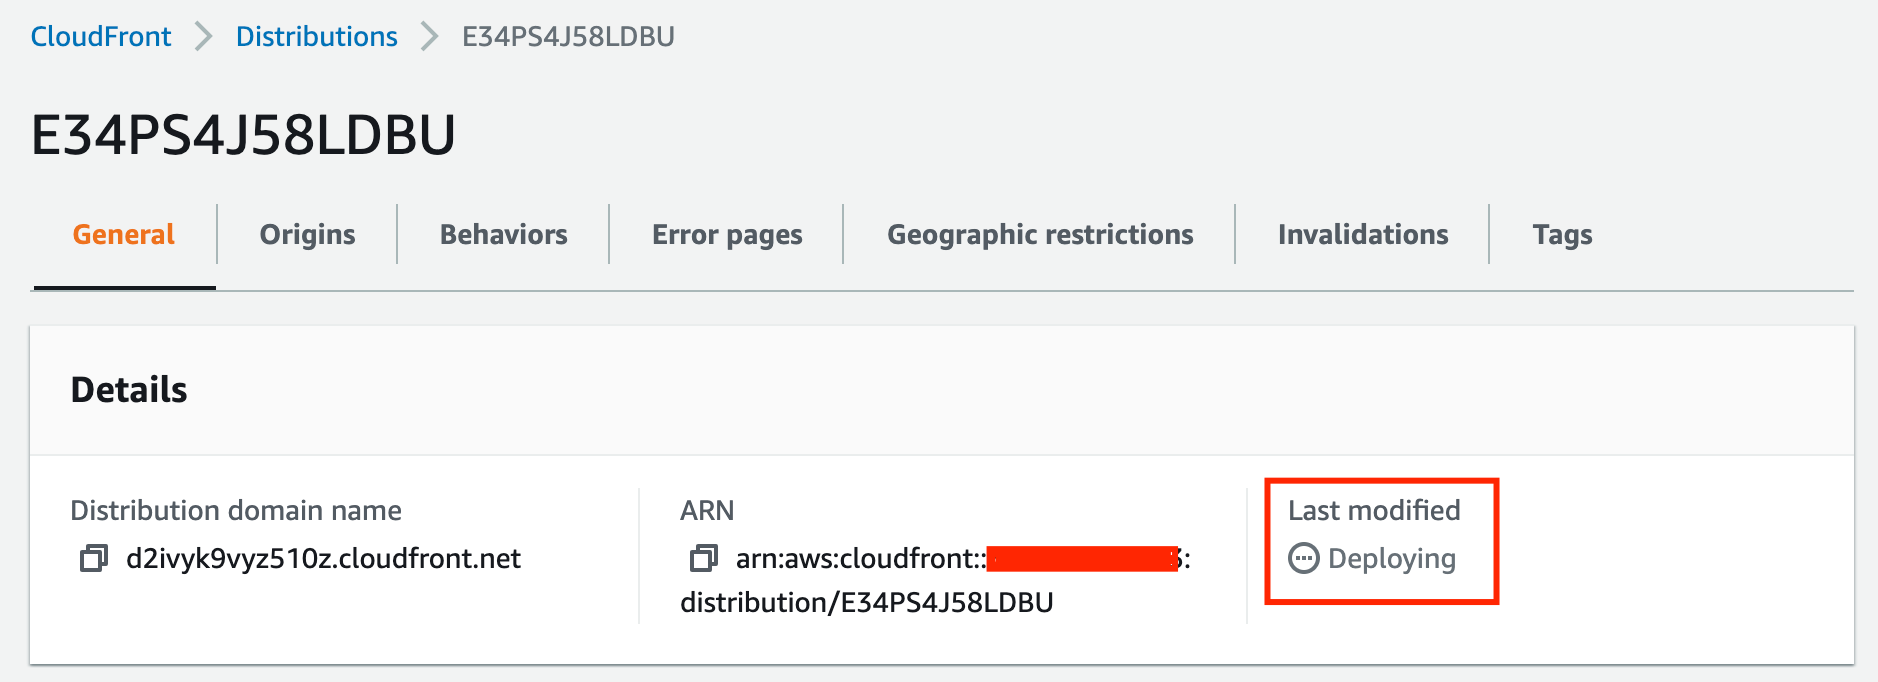 22. Wait for 5-10 minutes until you see the Deploying status changes and the **Last modified time** is present.
23. Now you can test the origin group.
#### Task 8: Test the Origin group
In this task, we are going to test the functionality of the origin group. By accessing the CloudFront distribution URL, users can verify that the content from both the S3 bucket and the EC2 instance is being served correctly.
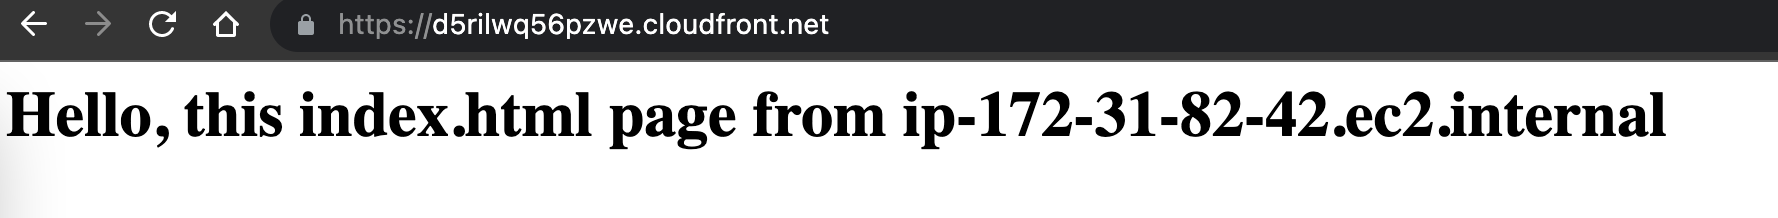
1. Copy the Distribution domain name and paste it into the new tab of your browser.
2. This should now display the index.html page from EC2 Instance as it has the Private IP DNS name.
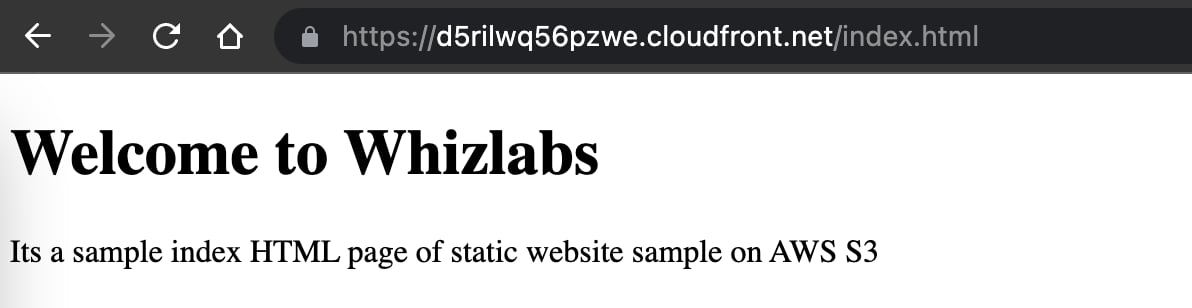
 3. Now add **/index.html** into the URL. This displays the contents of the index.html file present in the S3 Bucket.
 4. Now update the URL by changing /index.html to **/index2.html**
 > ##### Do You Know?
>
> Amazon CloudFront has a massive global presence, with edge locations located in over 200 cities across more than 90 countries. This extensive network allows CloudFront to deliver content with low latency and high data transfer speeds to users around the world, ensuring a fast and responsive experience for accessing websites, streaming videos, downloading files, and more.
1. Once the lab steps are completed, please click on the **Validation** button on the left side panel.
### Completion and Conclusion
1. You have successfully created an S3 Bucket, uploaded index.html, and made the bucket publicly accessible using bucket policy.
2. You have successfully created an Amazon CloudFront distribution and published the S3 bucket's index.html file through CloudFront.
3. You have successfully launched the EC2 Instance and tested the Public IPv4 DNS of the instance.
4. You have successfully created the origin and origin groups in CloudFront.
5. You have successfully tested the failover using the distribution domain name.
### End Lab
1. Sign out of AWS Account.
2. You have successfully completed the lab.
3. Once you completed the task, click on **End Lab** from the IP Lab Portal dashboard.
## What gets checked
When you press **Check my work**, the platform verifies each of these:
* **Launch an EC2 Instance** — Check whether an EC2 Instance is launched or not.
* **Validate EC2 Instance Type t2.micro** — Check whether the EC2 instance type is t2.micro.
* **Launch EC2 AMI type Amazon Linux** — Check whether the EC2 instance is launched using an Amazon AMI.
* **Create Public AWS S3 Bucket** — Check whether a Public S3 Bucket created or not
* **Create an AWS S3 Bucket with Policy** — Check whether S3 bucket is created and bucket policy added or not
* **check s3 object** — Check whether an object is uploaded to the S3 bucket.
* **Create CloudFront Distribution** — Check whether a CloudFront Distribution is created and status as Deployed or not.
* **Invoke CloudFront Distribution Domain** — Check whether the CloudFront Distribution domain is accessible from the internet or not.
## Related help
* [FAQs and Troubleshooting](/aws-saa/support/faqs-and-troubleshooting)
* [SSH into EC2 Instance](/aws-saa/support/ssh-into-ec2-instance)
This documentation is built and hosted on [Mintlify](https://mintlify.com), a developer documentation platform.