> ## Documentation Index
> Fetch the complete documentation index at: https://cloud-architect.ipoint-labs.com/llms.txt
> Use this file to discover all available pages before exploring further.
# Access S3 from Private EC2 instance using VPC Endpoint
> Hands-on lab · 30m
Launch this lab in the IP Lab Portal, then follow the steps below in the AWS console.
Open IP Lab Portal
## Overview
### Lab Details
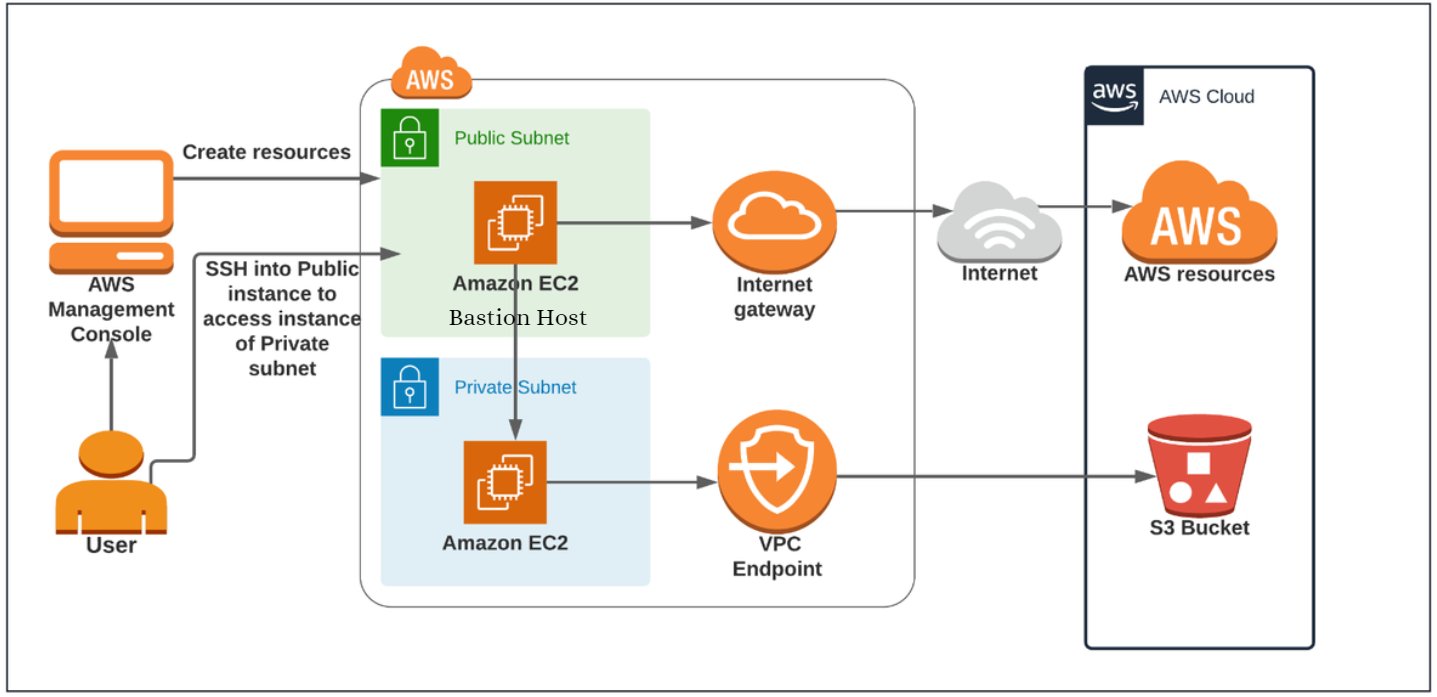
1. This lab walks you through the steps to create an endpoint for Amazon S3 and access with EC2 Instance in Private subnet.
2. EC2 instances of private subnet will be accessible from a bastion host or so-called an EC2 instance in a public subnet.
3. Duration: **90 minutes**
4. AWS Region: **US East (N. Virginia) us-east-1**
### Introduction
#### Bastion Instance
* **A bastion host is a system** that is exposed to the internet.
* In terms of security, Bastion is the only server that is exposed to the internet and should be highly protective of malicious attacks.
* **A Bastion host** is also **known as a Jump Box**. It is a computer that acts like a proxy server and that allows the client machine to connect to the remote server.
* In this lab, we are using Bastion instance as a Public instance to SSH into a Private instance.
#### VPC endpoint for S3
* VPC Endpoint allows us to securely connect your VPC and supported AWS services powered by AWS PrivateLink. AWS PrivateLink is a service that allows you to access AWS services by using private IP addresses. In this case, traffic does not leave Amazon’s network.
* VPC endpoint does not require a NAT Gateway, NAT instance, Internet Gateway, or any VPN services to access AWS Services.
* There are two types of VPC endpoints: Gateway and Interface.
* VPC endpoint for S3 comes under Gateway endpoint.
* When you create a VPC endpoint for S3, it asks for the Route table, then it adds the Prefix list to that route table. You can’t modify/delete the entry present in the route table, created by Endpoint.
### Architecture Diagram
 ### Task Details
1. Sign into AWS Management Console
2. Create a VPC
3. Create and attach an Internet Gateway with custom VPC
4. Create a Public and Private Subnet
5. Configure the Public subnet to enable auto-assign public IPv4 address
6. Create a Route Table for the Public subnet
7. Create security groups
8. Create a Bastion Host (Publicly accessible EC2 Instance)
9. Create an Endpoint instance (Privately accessible EC2 instance)
10. SSH into Endpoint instance (Privately accessible) through Bastion host
11. Create a VPC endpoint for S3, attach it to the Private subnet's Route table.
12. List all the S3 Bucket and its objects
13. Deleting AWS Resources.
### Launching Lab Environment
1. To launch the lab environment, Click on the **Start Lab** button.
2. Please wait until the cloud environment is provisioned. It will take less than a minute to provision.
3. Once the Lab is started, you will be provided with **IAM user name**, **Password**, **Access** **Key**, and **Secret** **Access** **Key**.
> **Note** : You can only start one lab at any given time
## Lab guide
### Lab Steps
#### Task 1: Sign in to AWS Management Console
1. Click on the **Open Console** button, and you will get redirected to AWS Console in a new browser tab and it will be Logged in Successfully.
2. On the AWS Console, in the search bar search for **IAM** and click on it.
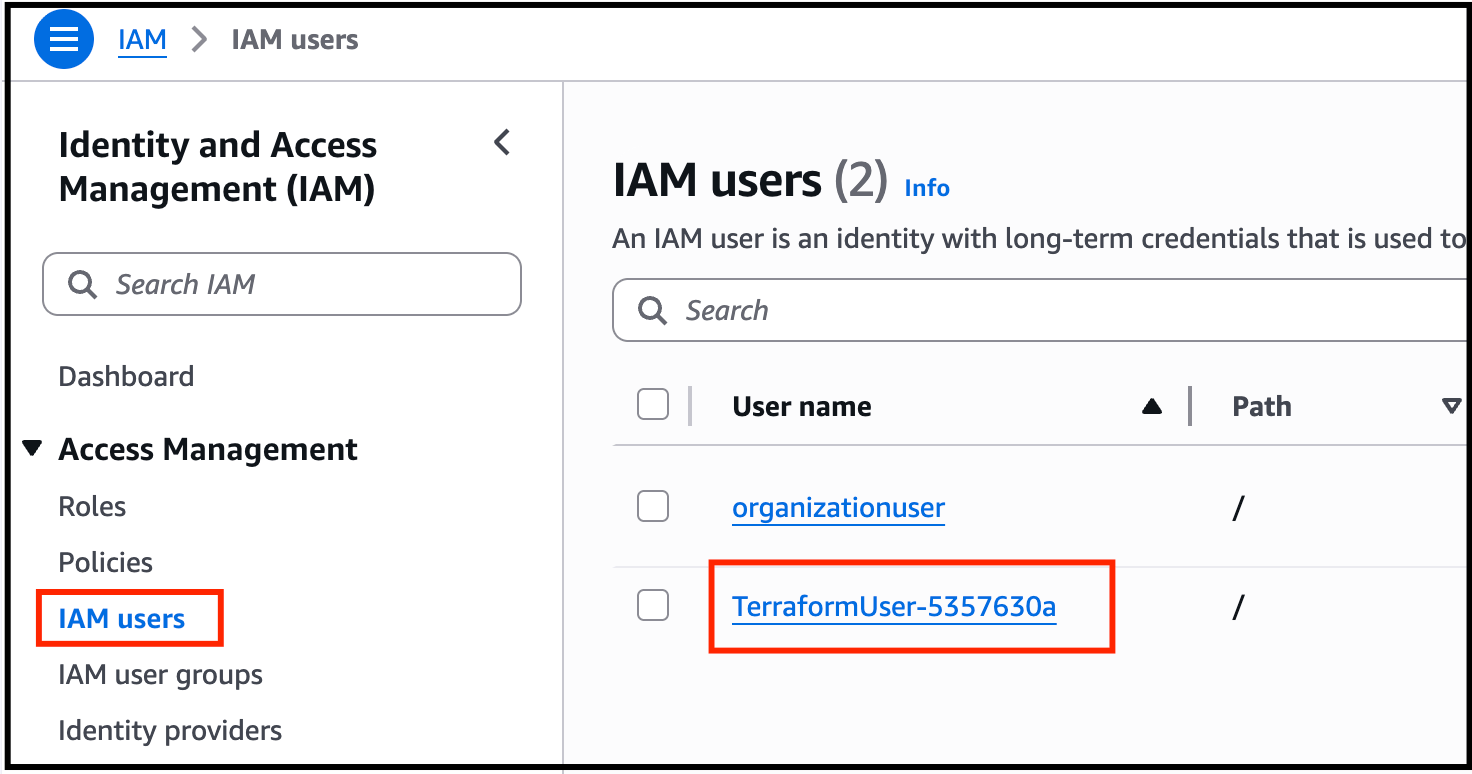
3. Then Click on **IAM Users** and select **TerraformUser-XXXXX**
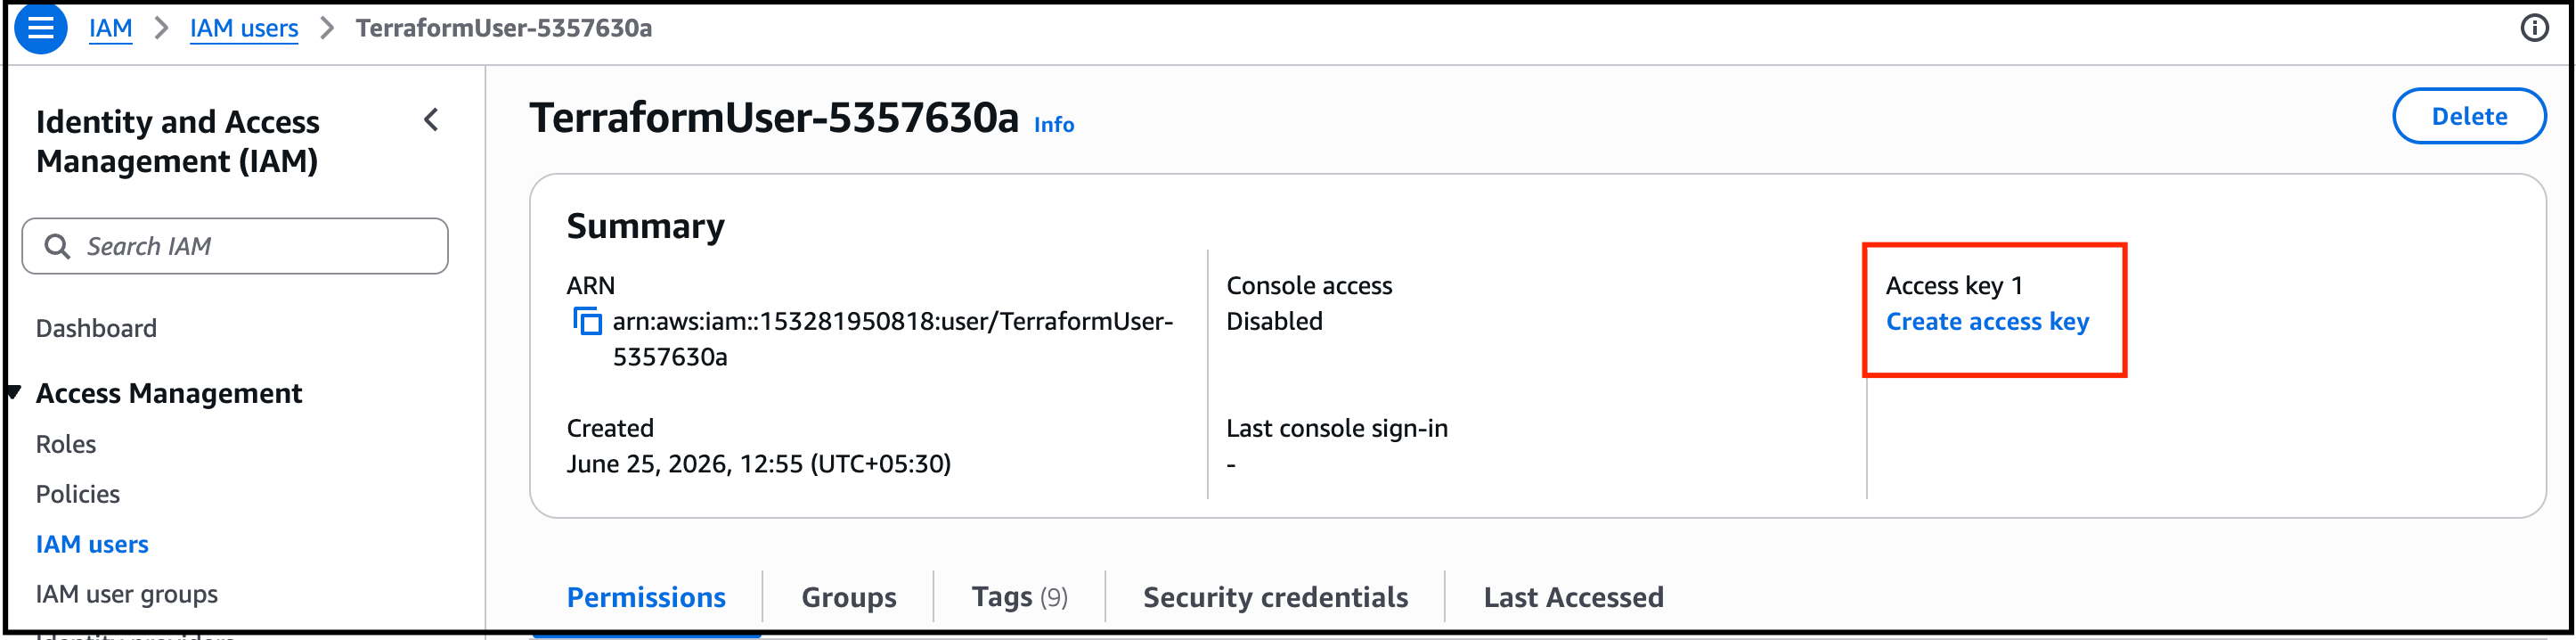
 4. Click on **Create Access Key**.
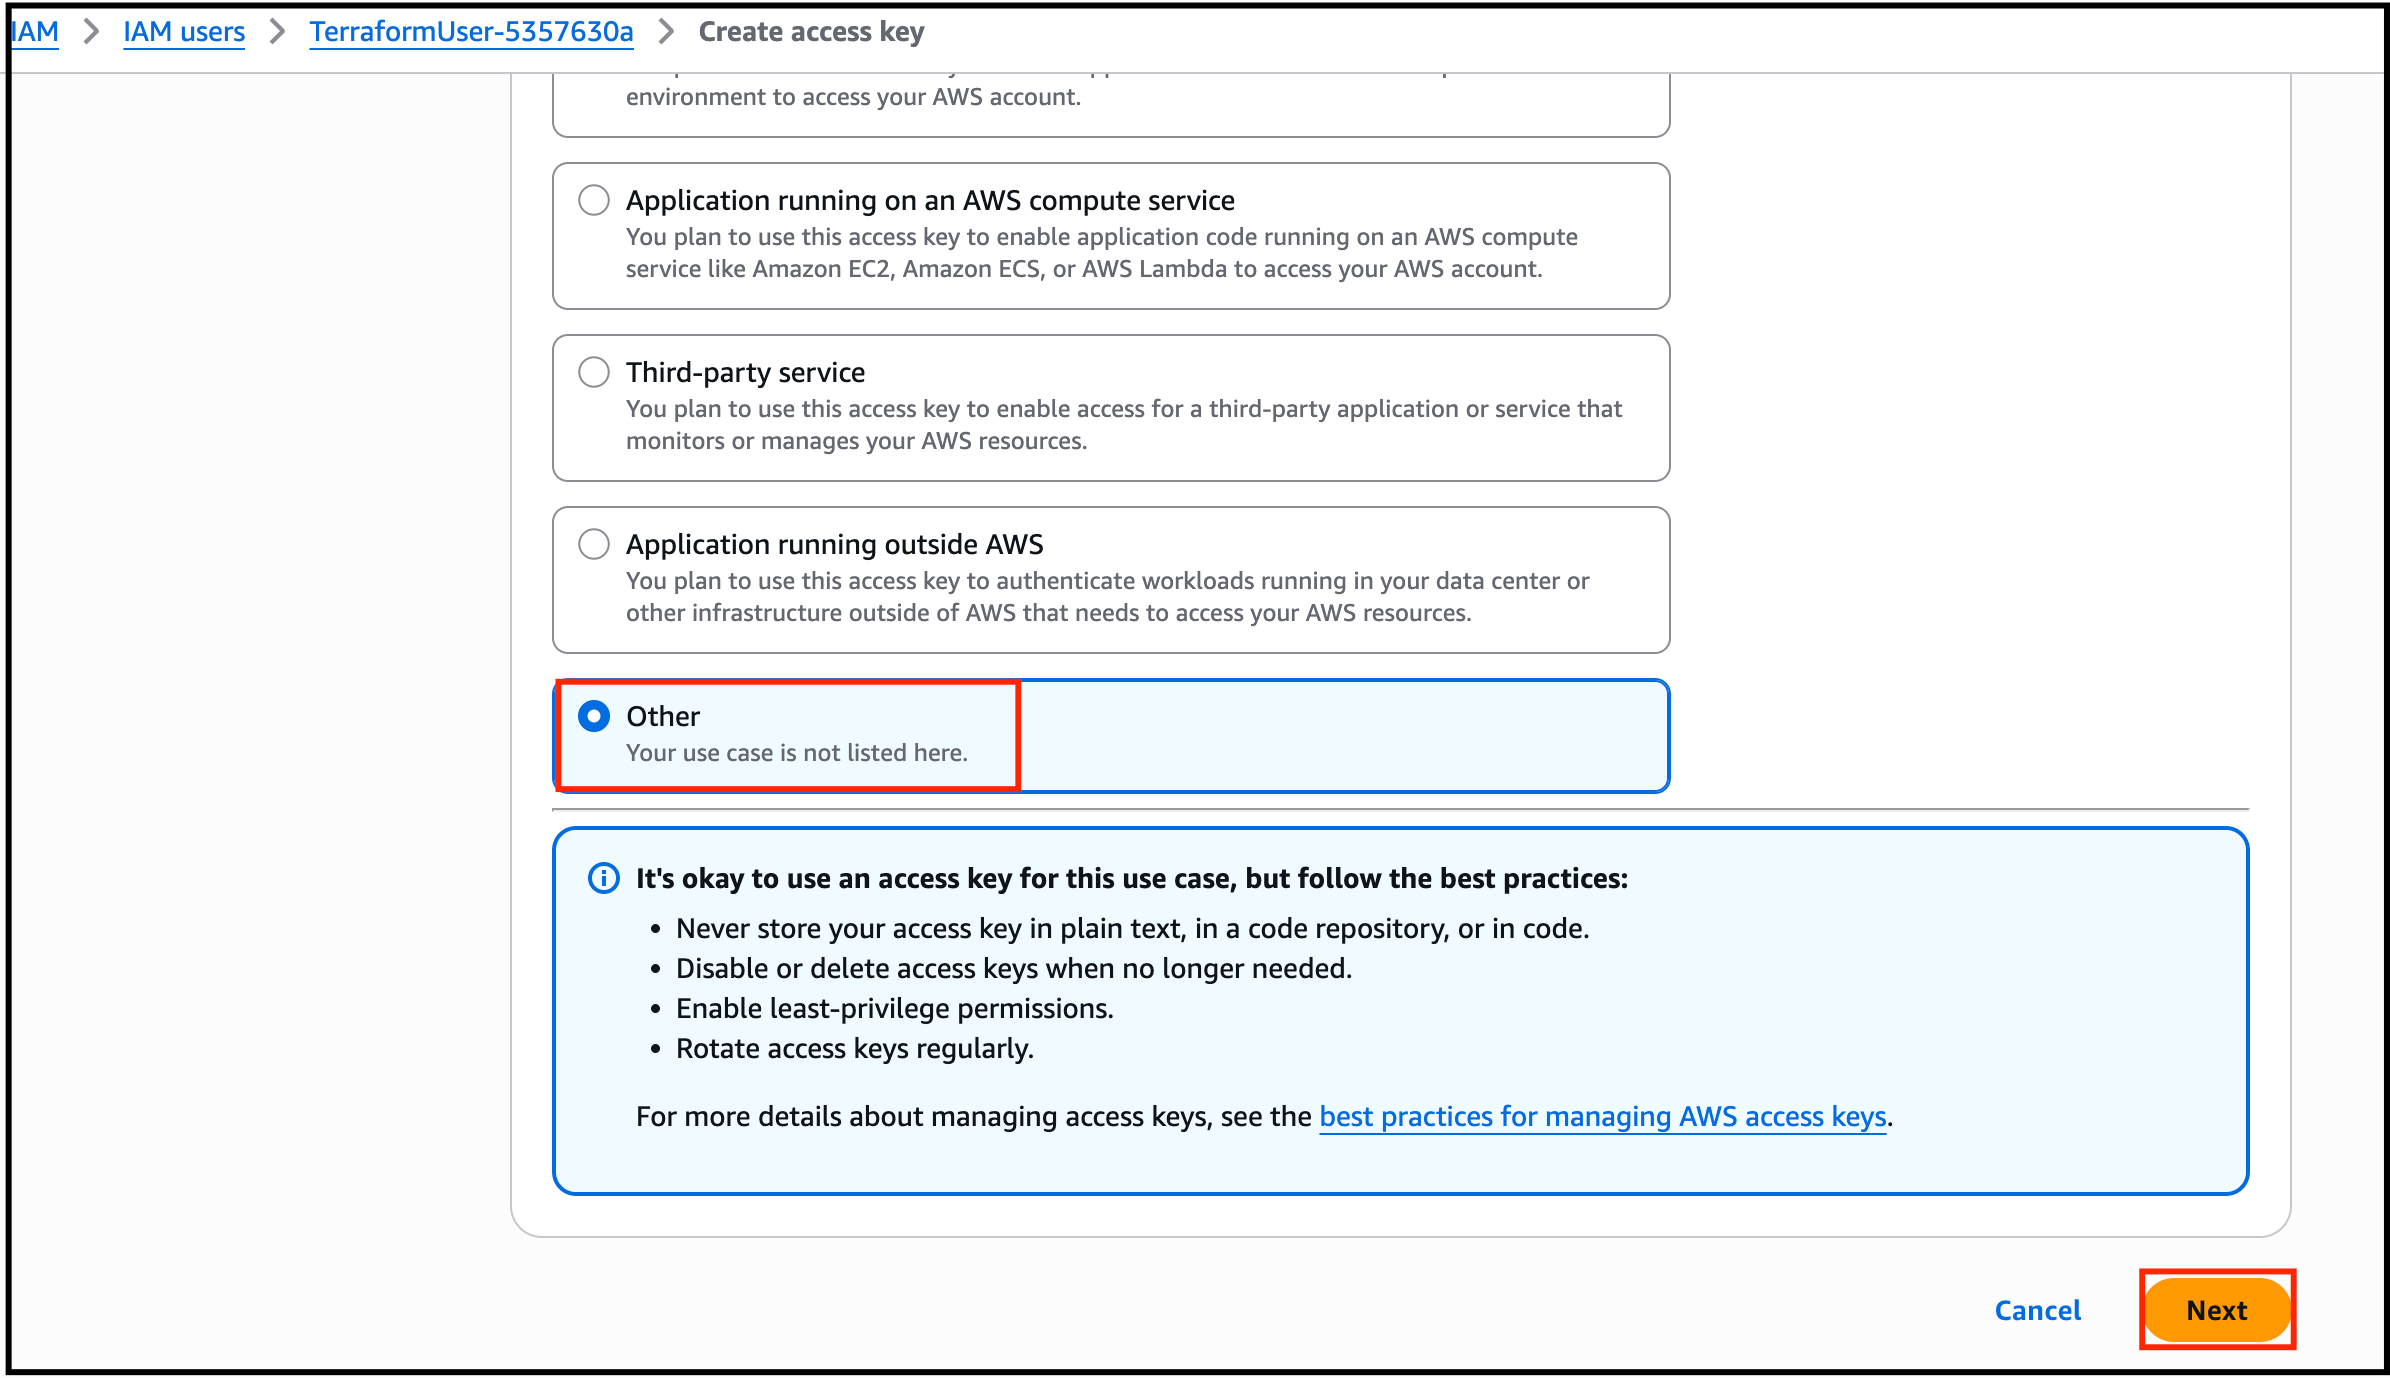
 5. Choose **Other**, Click on **Next** and click on **Create Access Key.**
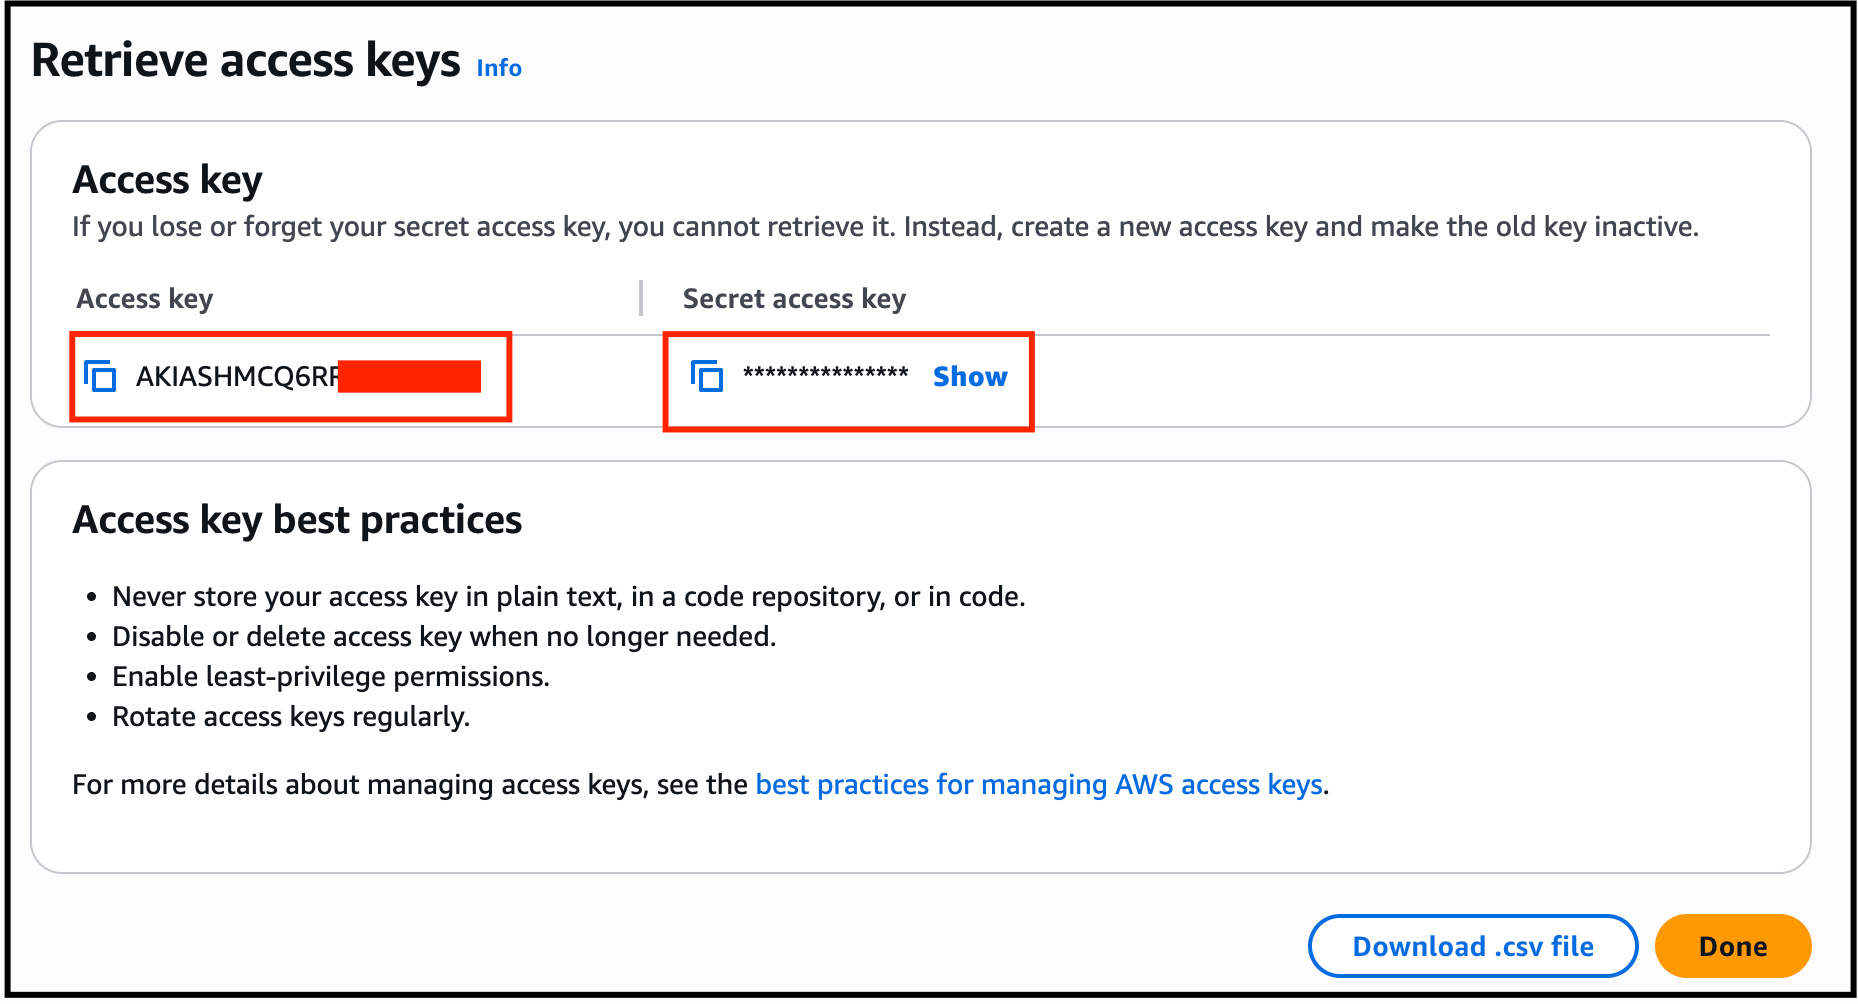
 6. Your **Access and Secret key** will get Created. Make a note of it for later use
 ####
#### Task 2: Create a VPC
1. Make sure you are in the **N.Virginia** Region.
2. Navigate to **VPC** by clicking on the **Services** menu at the top, then click on **VPC** in the **Network and Content Delivery** section.
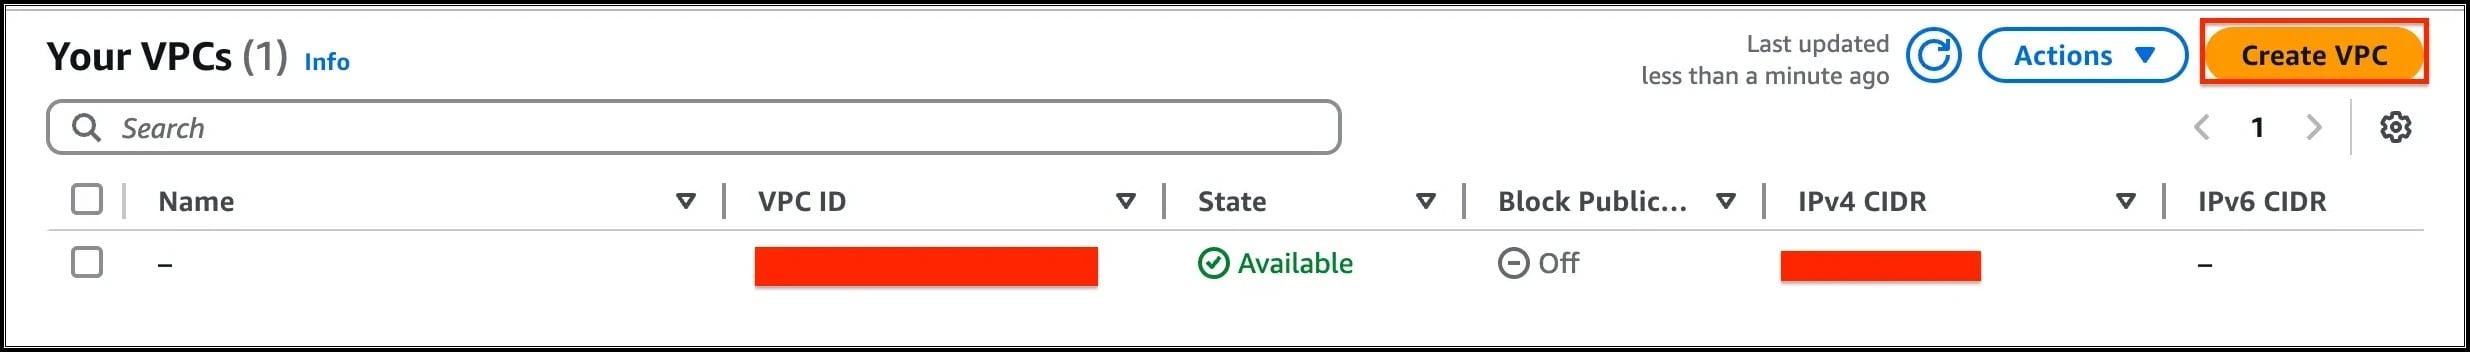
3. To create a **VPC** click on **Your VPCs** the present in the **VIRTUAL PRIVATE CLOUD** section on the left sidebar.
4. Create a new VPC by clicking on the **Create VPC** button.
 * Select **VPC only.**
* Name tag - optional:Enter ***MyVPC***
* IPv4 CIDR block: Enter ***192.168.0.0/26***
* IPv6 CIDR block: No IPv6 CIDR block
* Tenancy: **Default**
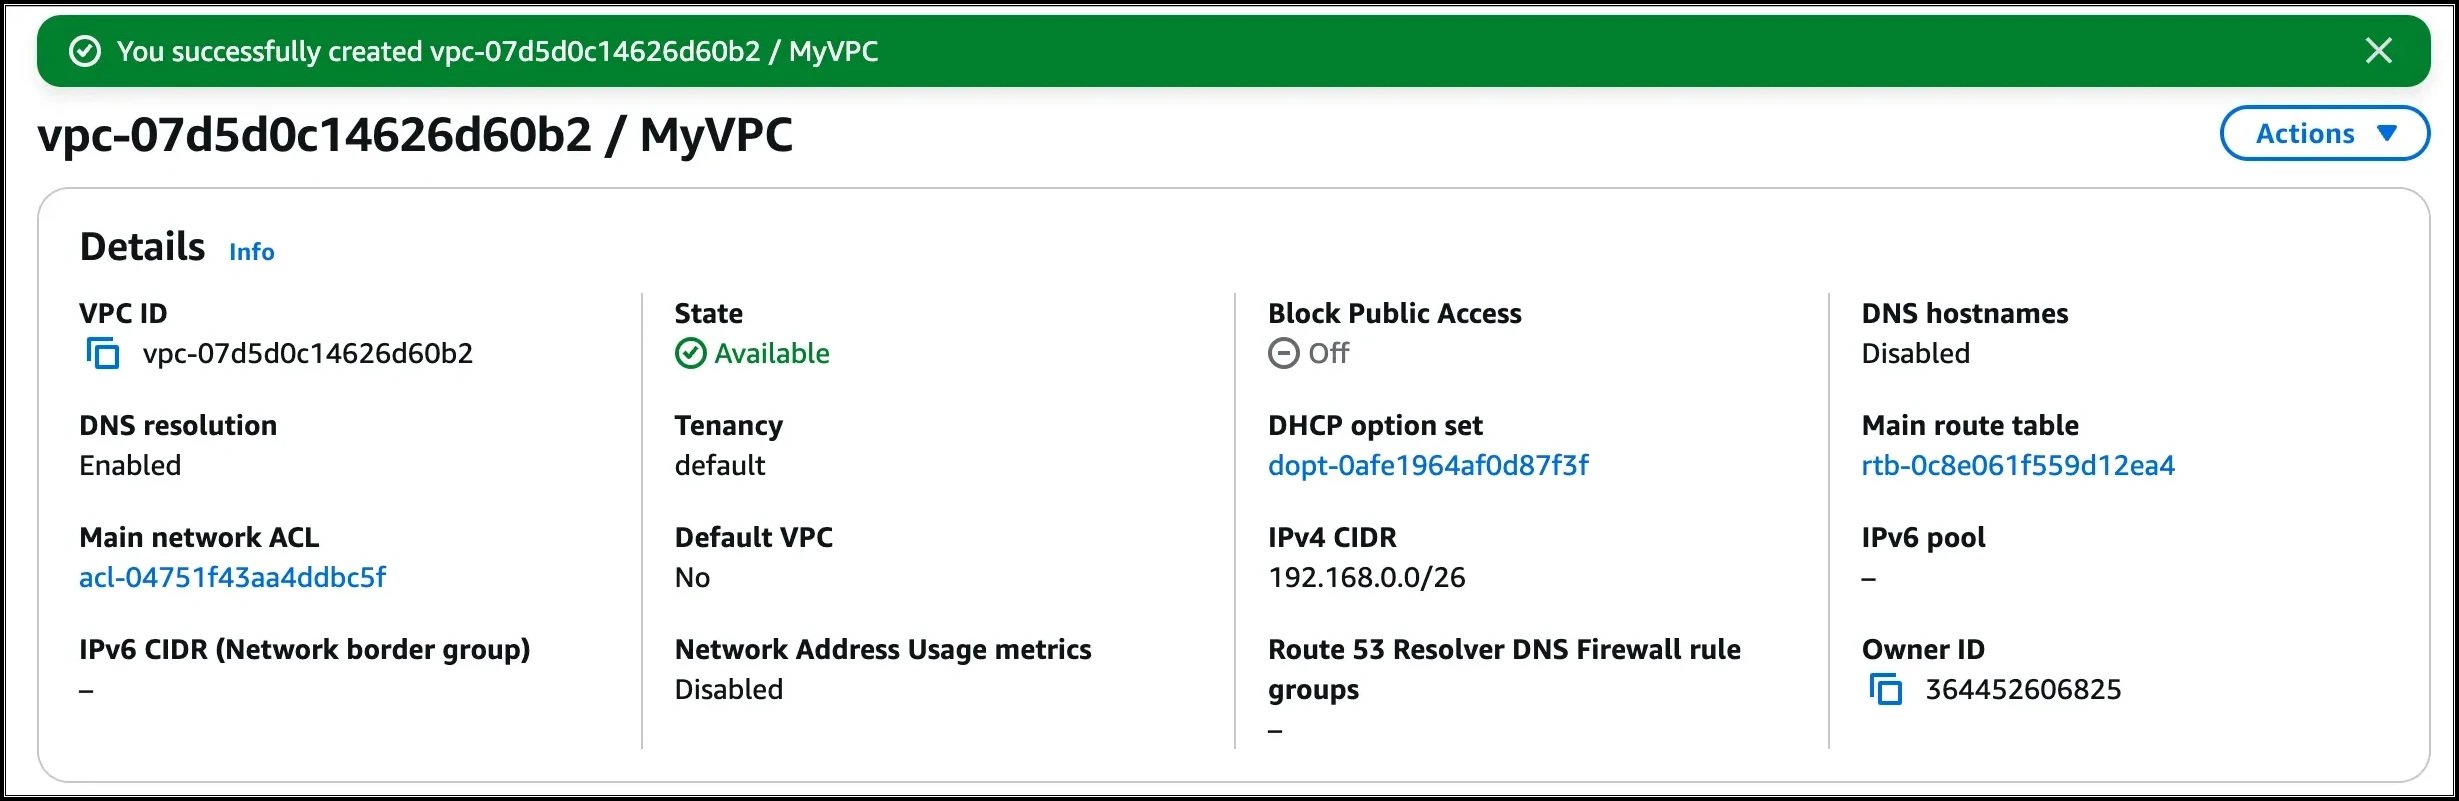
* Click on the **Create VPC** button to create the **MyVPC**.
* VPC is now created.
 #### Task 3: Create and attach an Internet Gateway with custom VPC
1. By default, instances that are launched in a VPC cannot communicate with the Internet. To enable Internet access, an Internet gateway needed to be attached to the VPC.
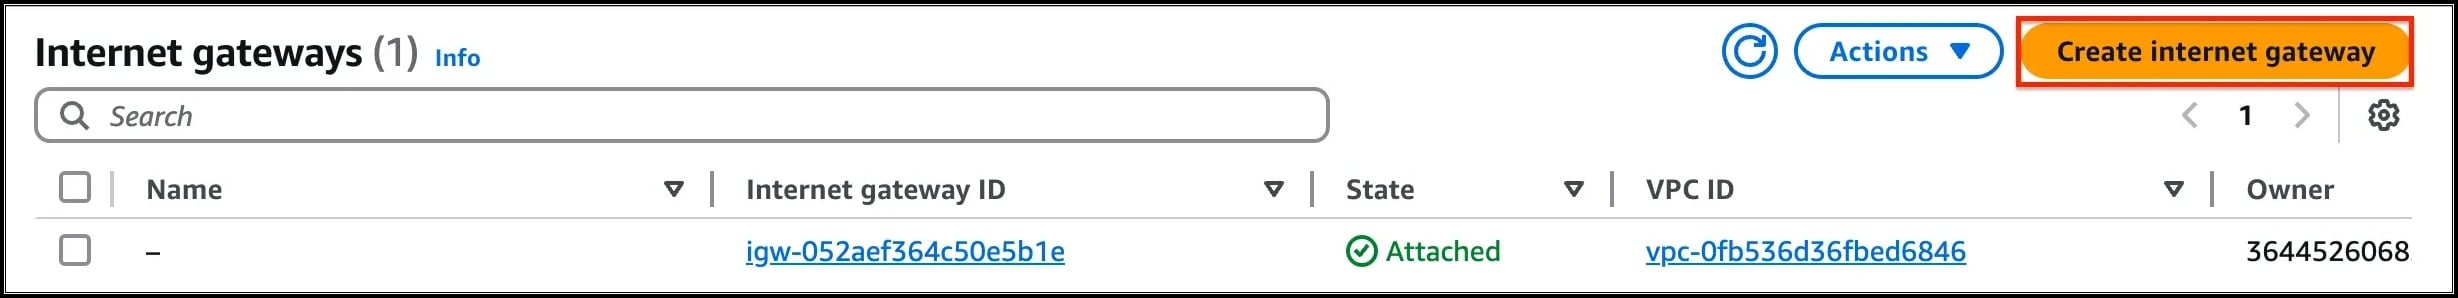
2. Click on **Internet Gateways** from the left menu and click on **Create internet gateway**.
 * **Name Tag :** Enter ***MyInternetGateway***
* Click on **Create internet gateway**.
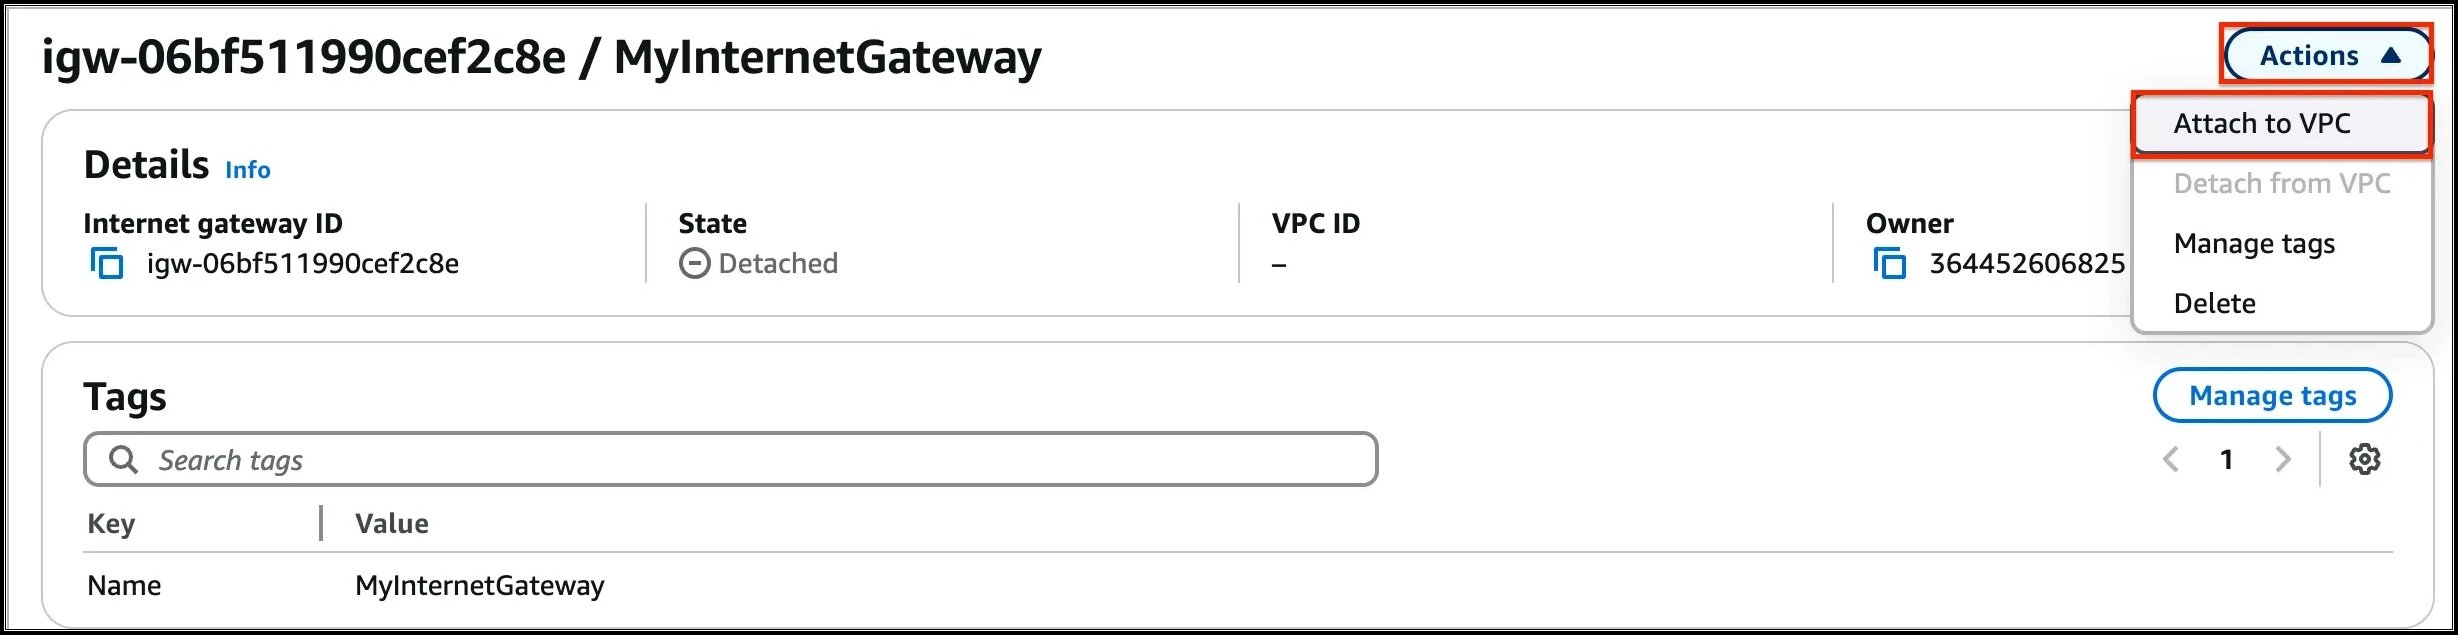
3. Select the Internet gateway you created from the list.
* Click on **Actions**.
* Select the **Attach to VPC**.
 4. Available VPCs: Select the **MyVPC**
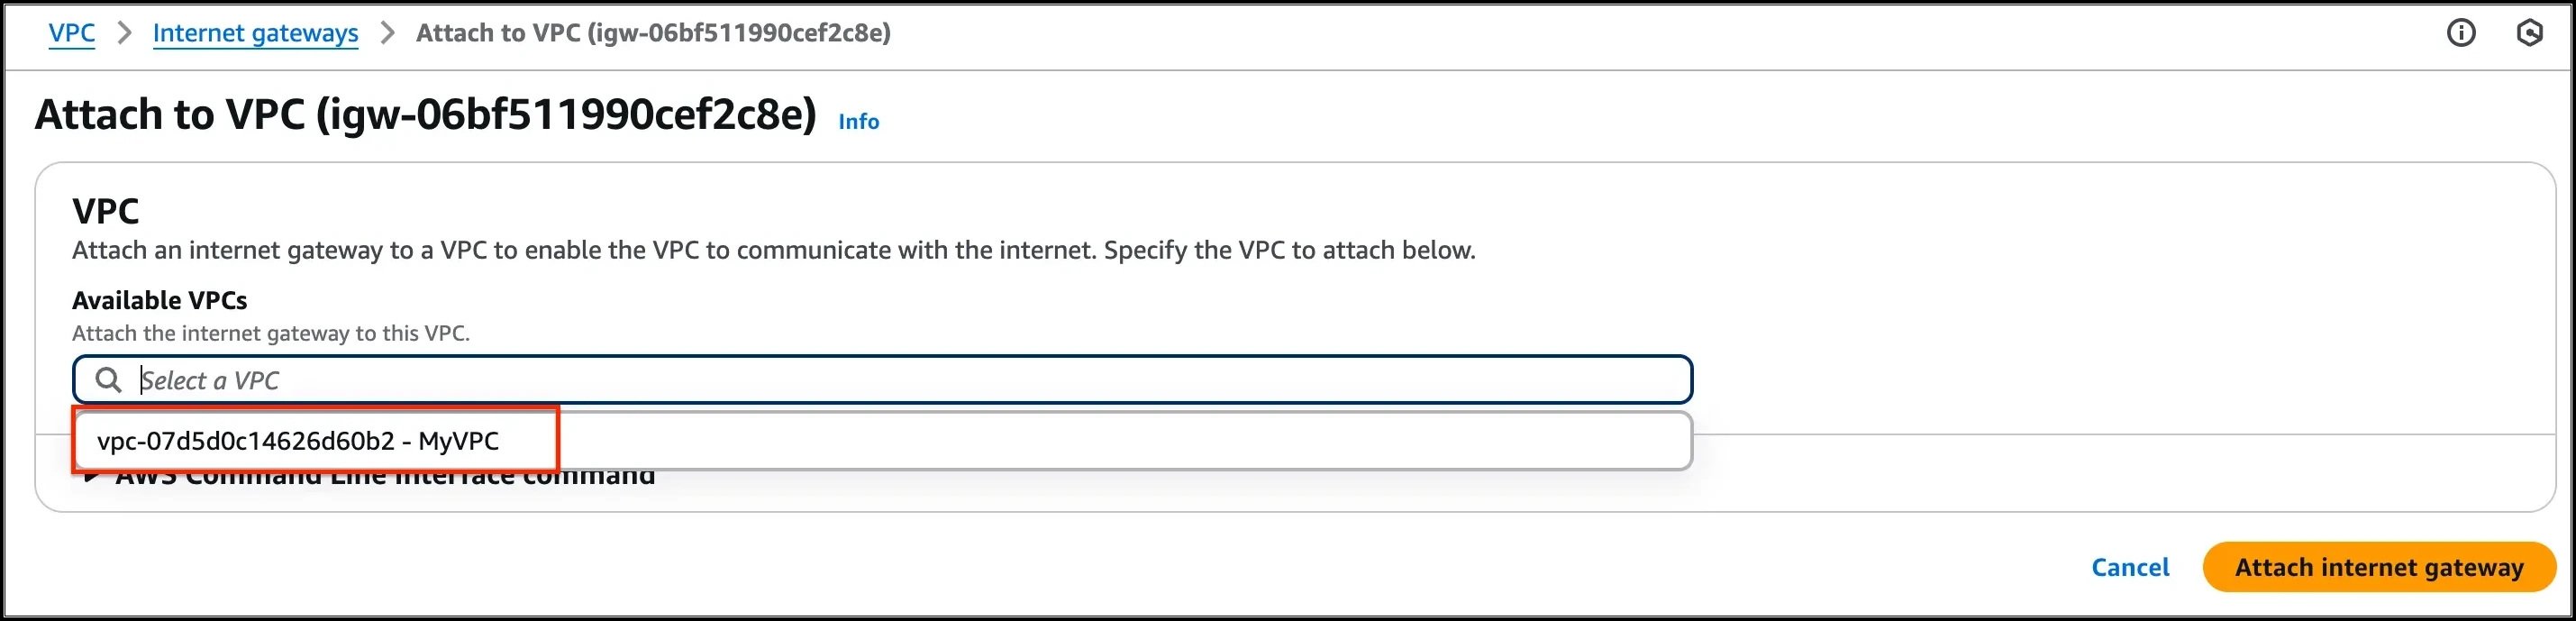 5. And click on the **Attach internet gateway** button.
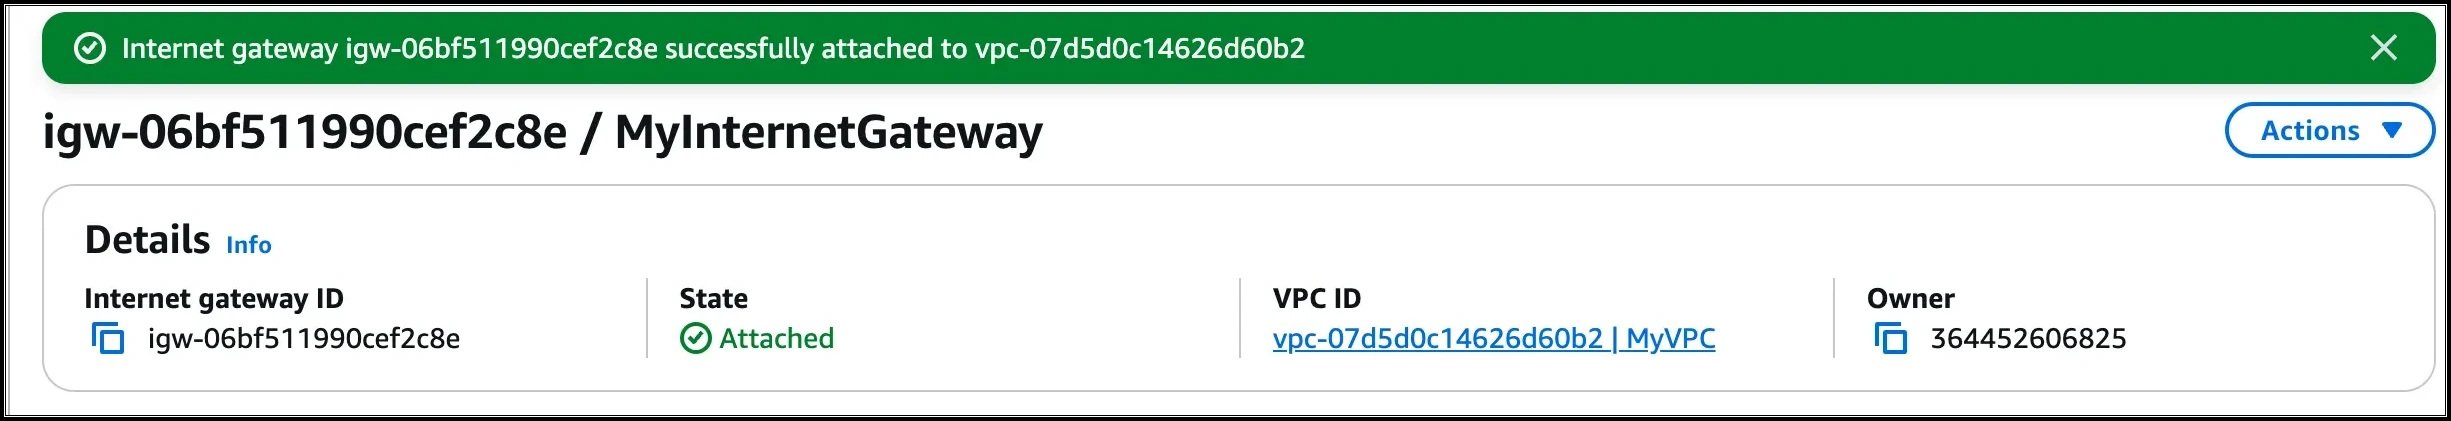
6. The Internet gateway is now attached with MyVPC.
 #### Task 4: Create a Public and Private Subnet
1. To create a **subnet** click on **Subnets** the present in the **VIRTUAL PRIVATE CLOUD** section on the left sidebar.
2. Click on the **Create Subnet** button.
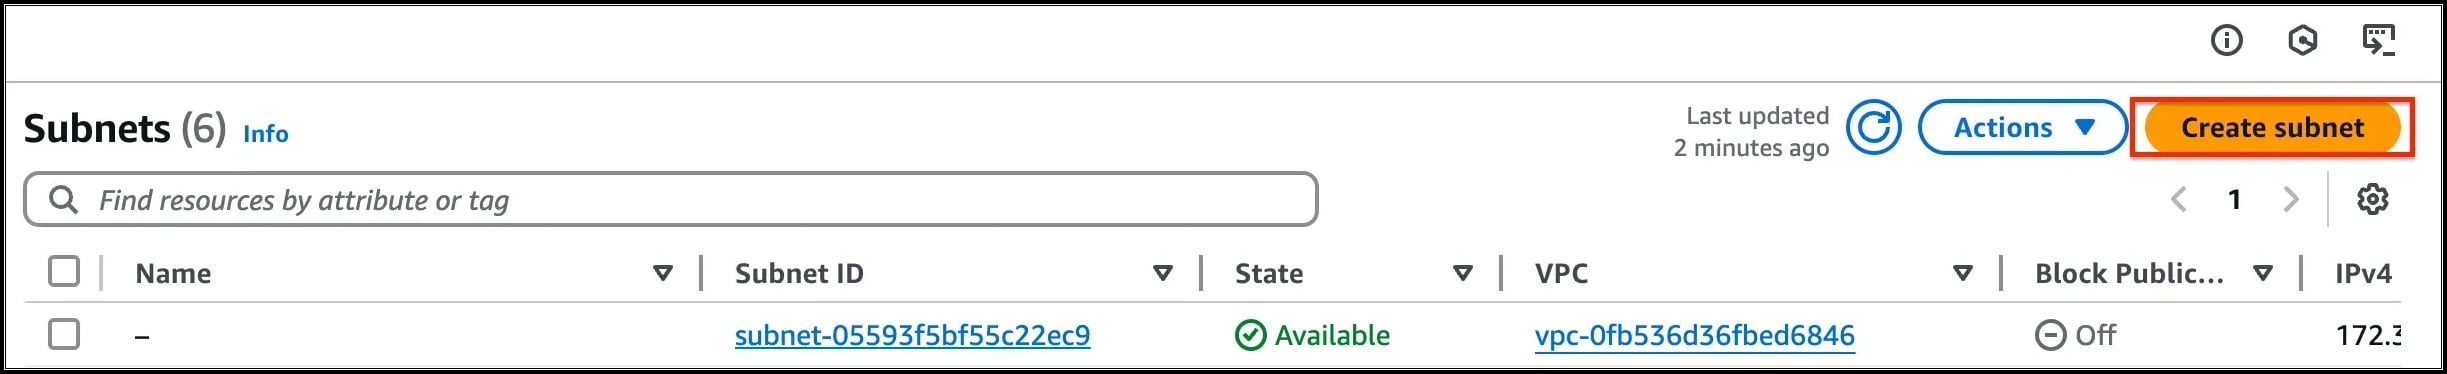 3. In the VPC ID, select **MyVPC**.
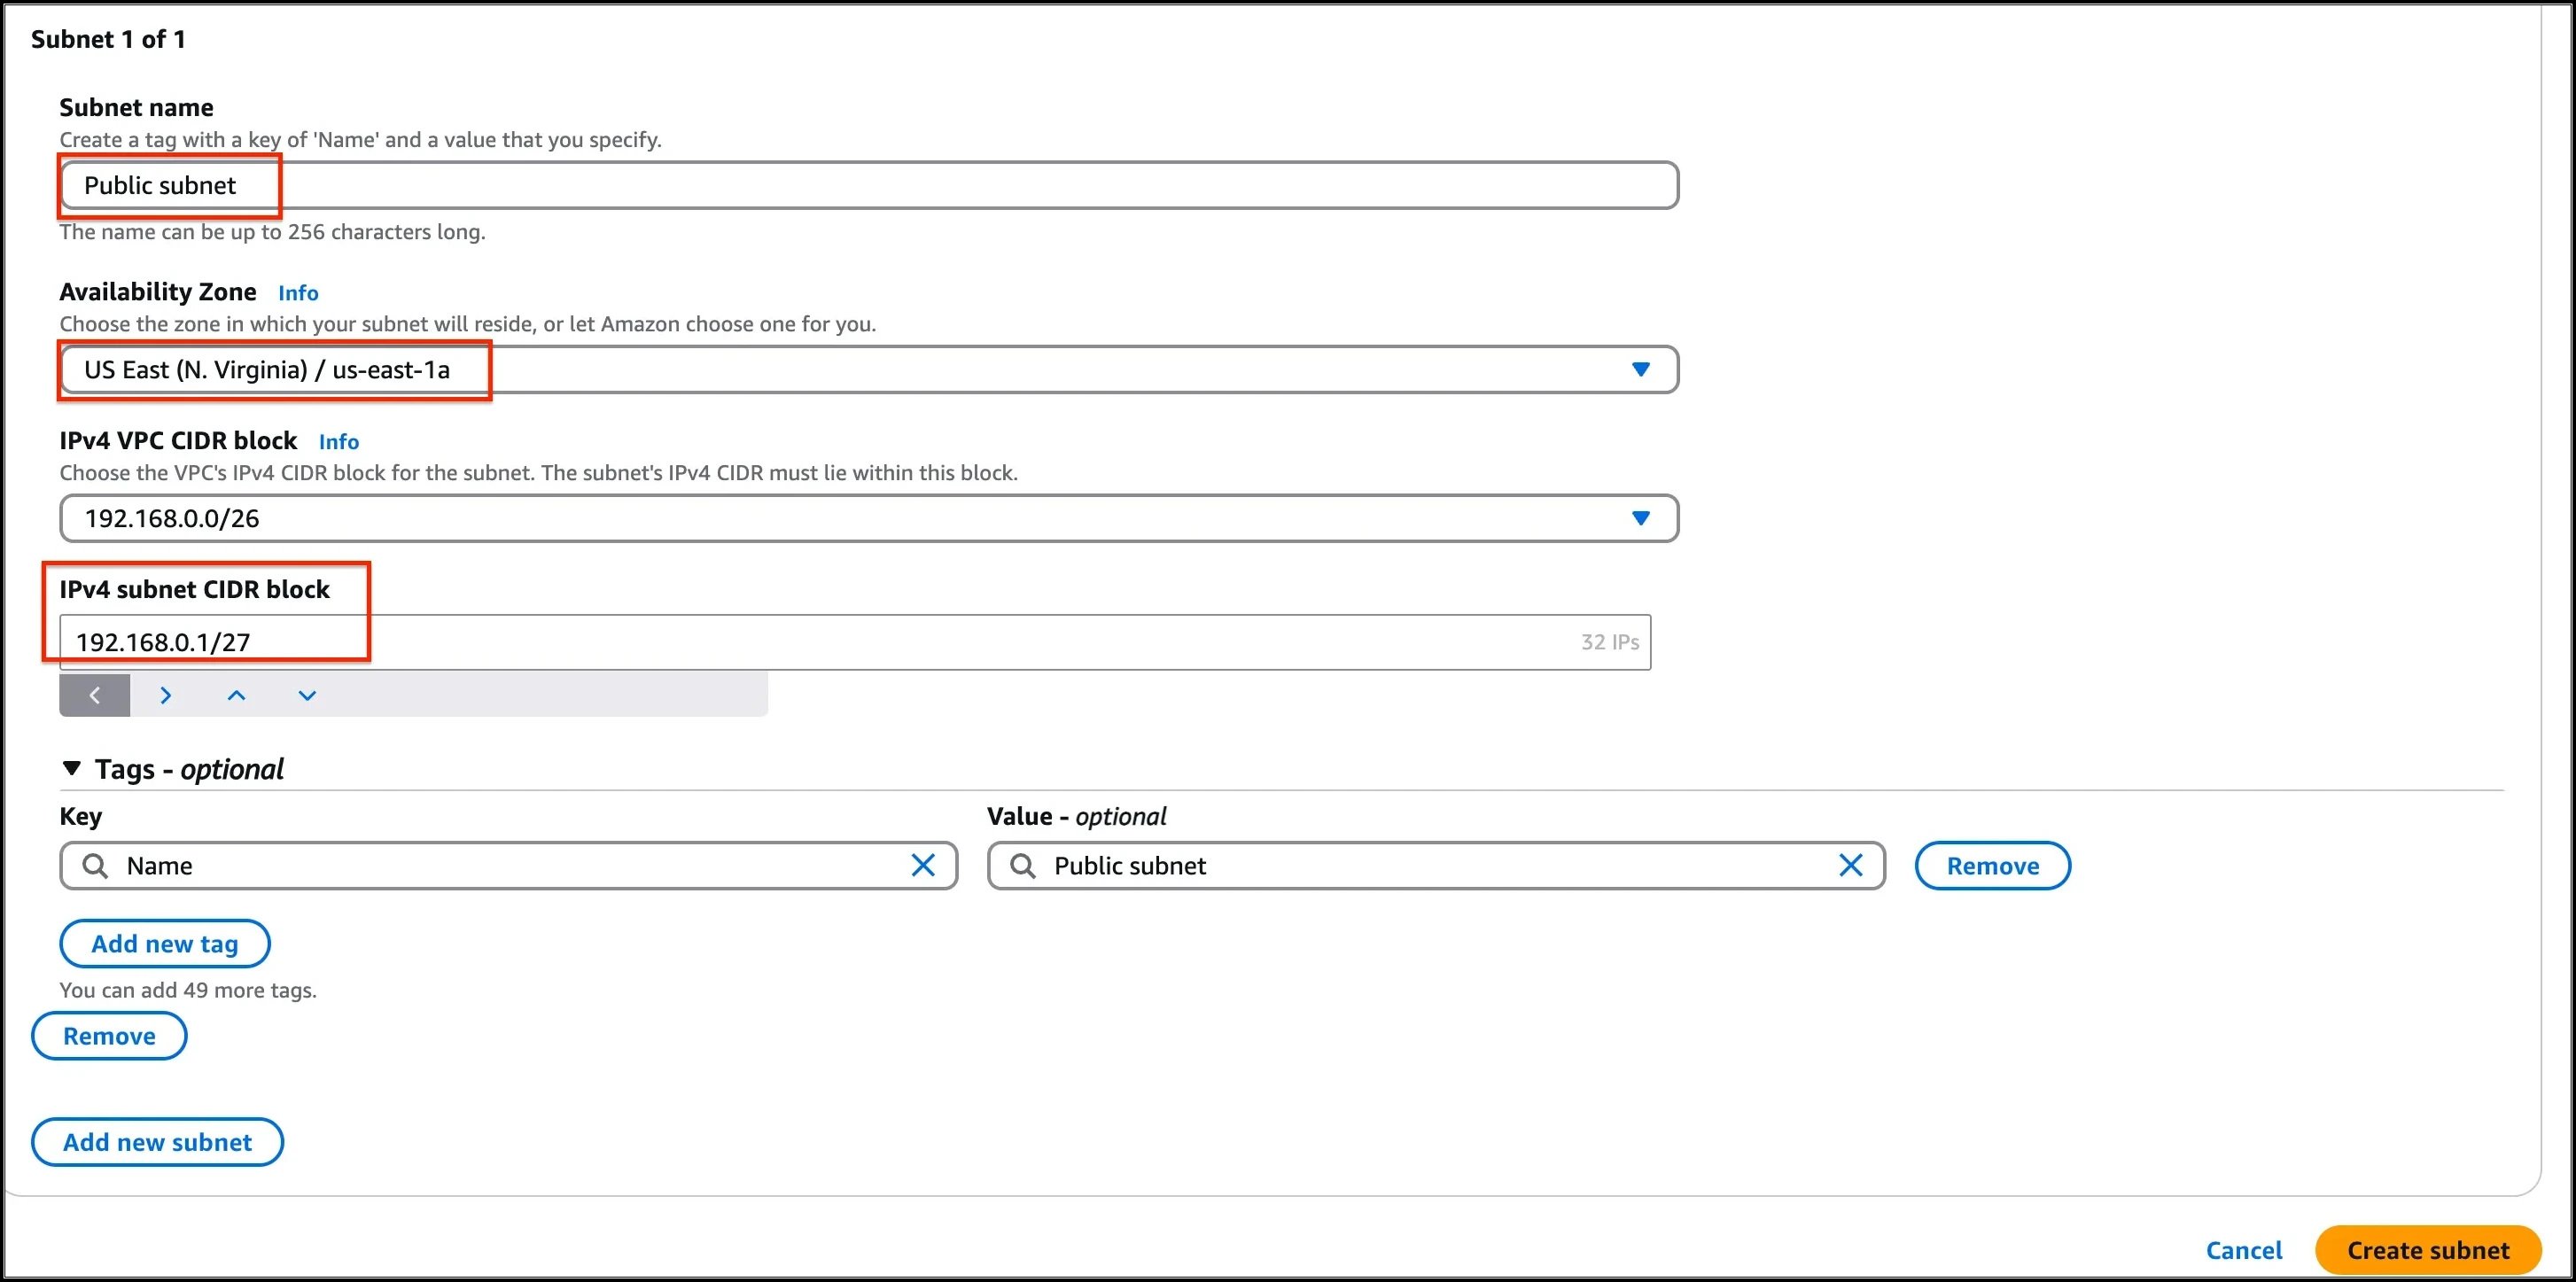
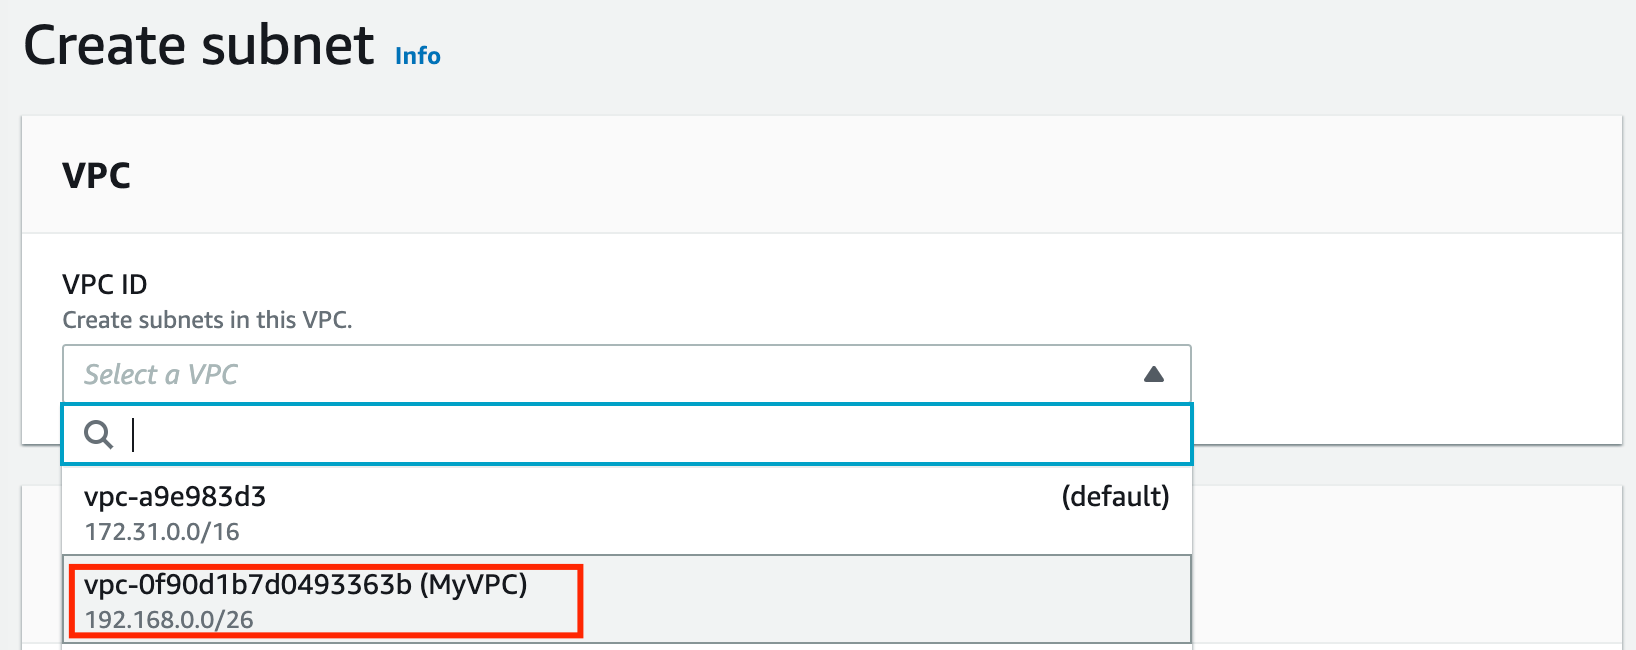 4. Create the first subnet, you will use this subnet to launch public instances, this subnet will be associated with the main route table of the VPC:
* Select the **MyVPC** from the drop-down.
* Subnet name: Enter ***Public subnet***
* Availability Zone: Select **US East (N. Virginia) / us-east-1a**
* IPV4 CIDR block: Enter ***192.168.0.1/27***
* Click on the **Create subnet** button to create the subnet.
 5. Create another subnet, click on the **Create subnet** button.
6. The second will be called Private subnet, you will use this subnet to launch private instances, this subnet will be associated with a custom route table of the same VPC:
* Select the **MyVPC** from the drop-down.
* Subnet name: Enter ***Private subnet***
* Availability Zone: Select **US East (N. Virginia) / us-east-1b**
* IPV4 CIDR block: Enter ***192.168.0.32/27***
7. Finally, click on the **Create Subnet** button.
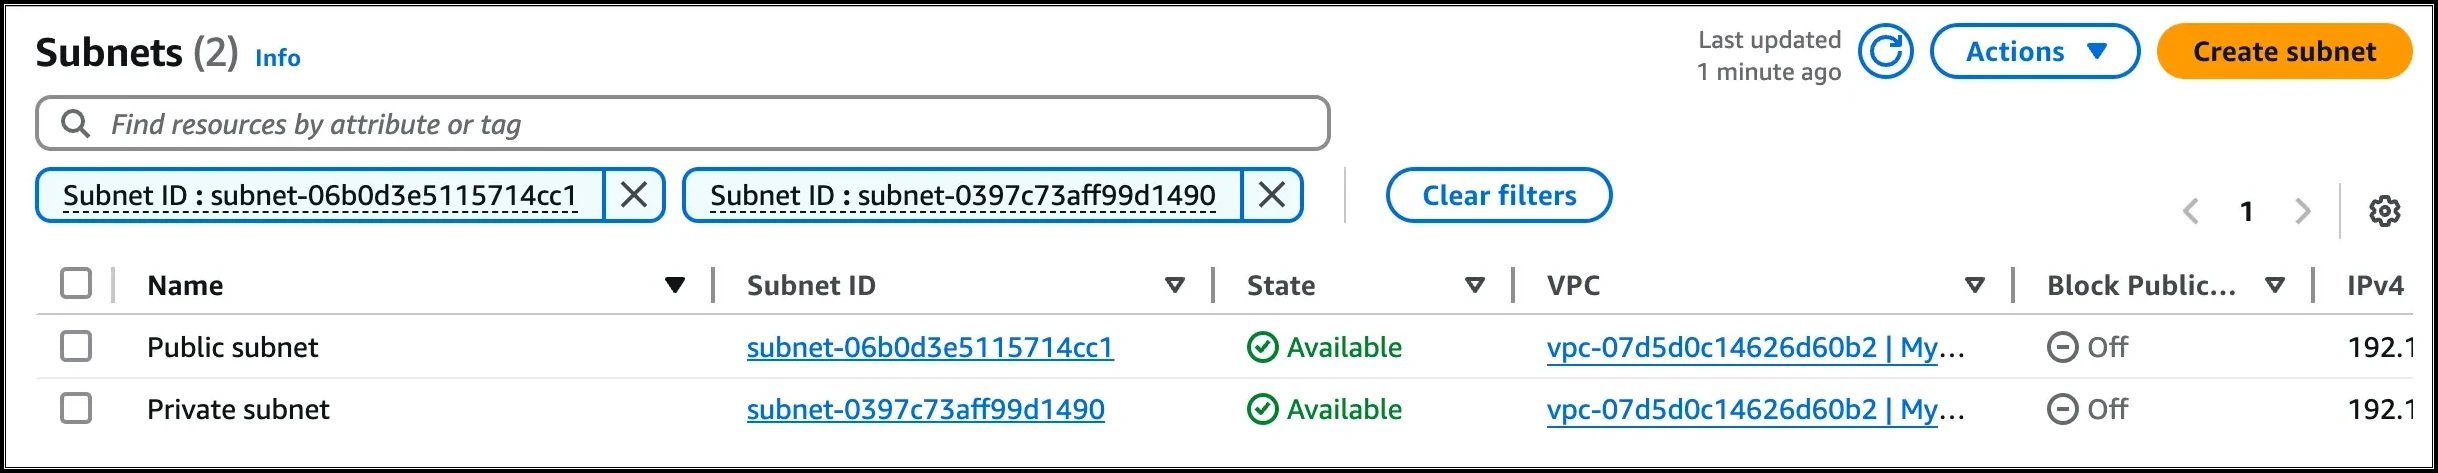
8. Both the subnets are now created.
 #### Task 5: Configure the Public subnet to enable auto-assign public IPv4 address
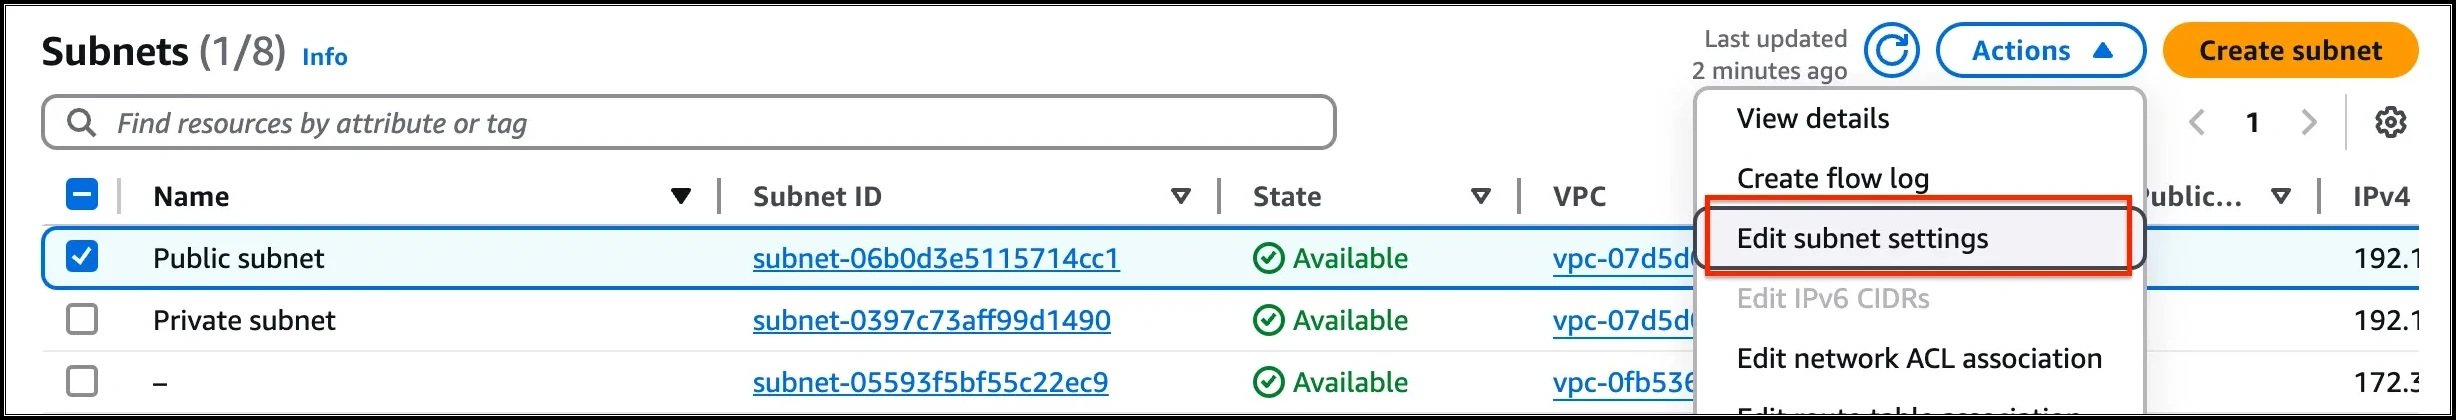
1. To modify the auto-assign IP settings for the Public subnet, do the following:
* Select the **Public subnet**
* Click on the **Actions** button
* Choose **Edit subnet settings** from the options.
 2. Check the option **Enable auto-assign public IPv4 address** under **Auto-assign IP settings.**
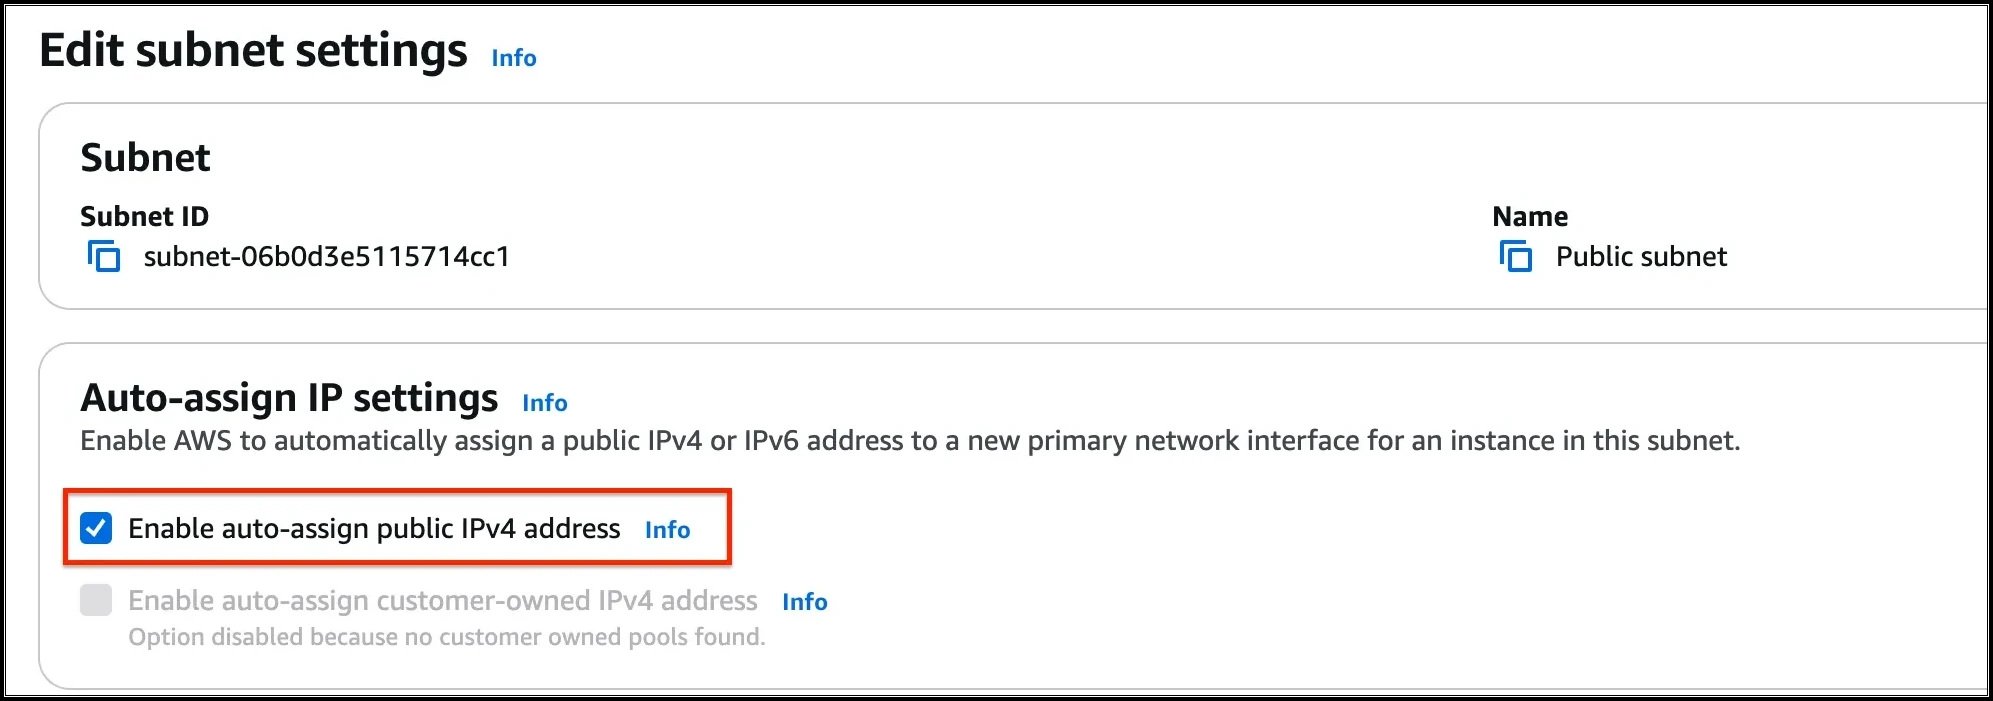 3. Click on **Save** button and modification is done now.
 #### Task 6: Create a Route Table for the Public subnet
In this task, we are going to create public route tables and associate it with the subnet.
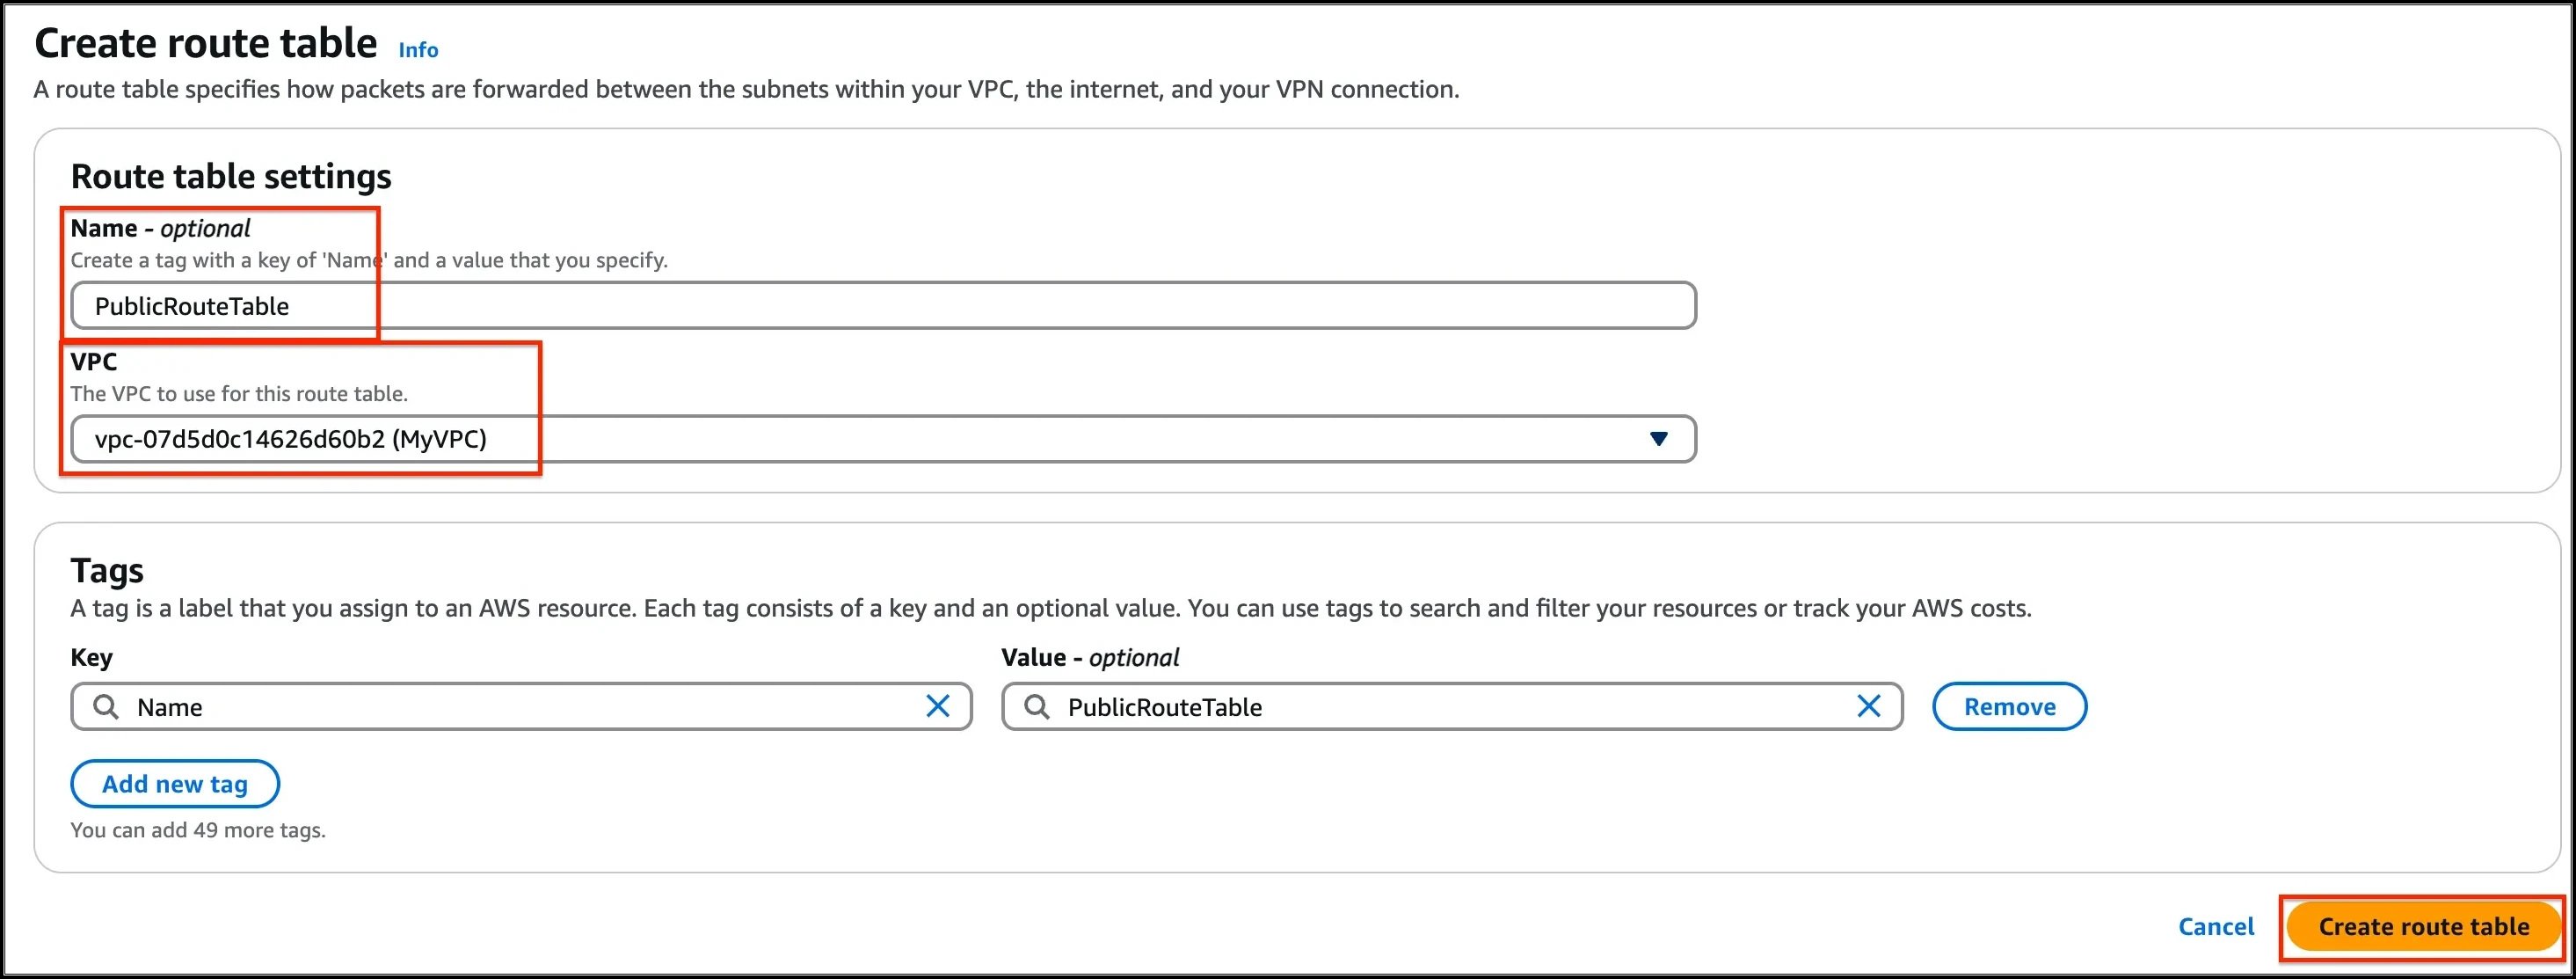
1. Go to **Route Tables** from the left menu and click on **Create route table** button.
* **Name:** Enter ***PublicRouteTable***
* **VPC:** Select **MyVPC** from the list.
* Click on **Create route table** button.
 2. Repeat the same steps to create a route table for the Private subnet.
* **Name:** Enter ***PrivateRouteTable***
* **VPC:** Select **MyVPC** from the list.
* Click on **Create route table** button.
3. Now we will **associate the subnets** to the route tables.
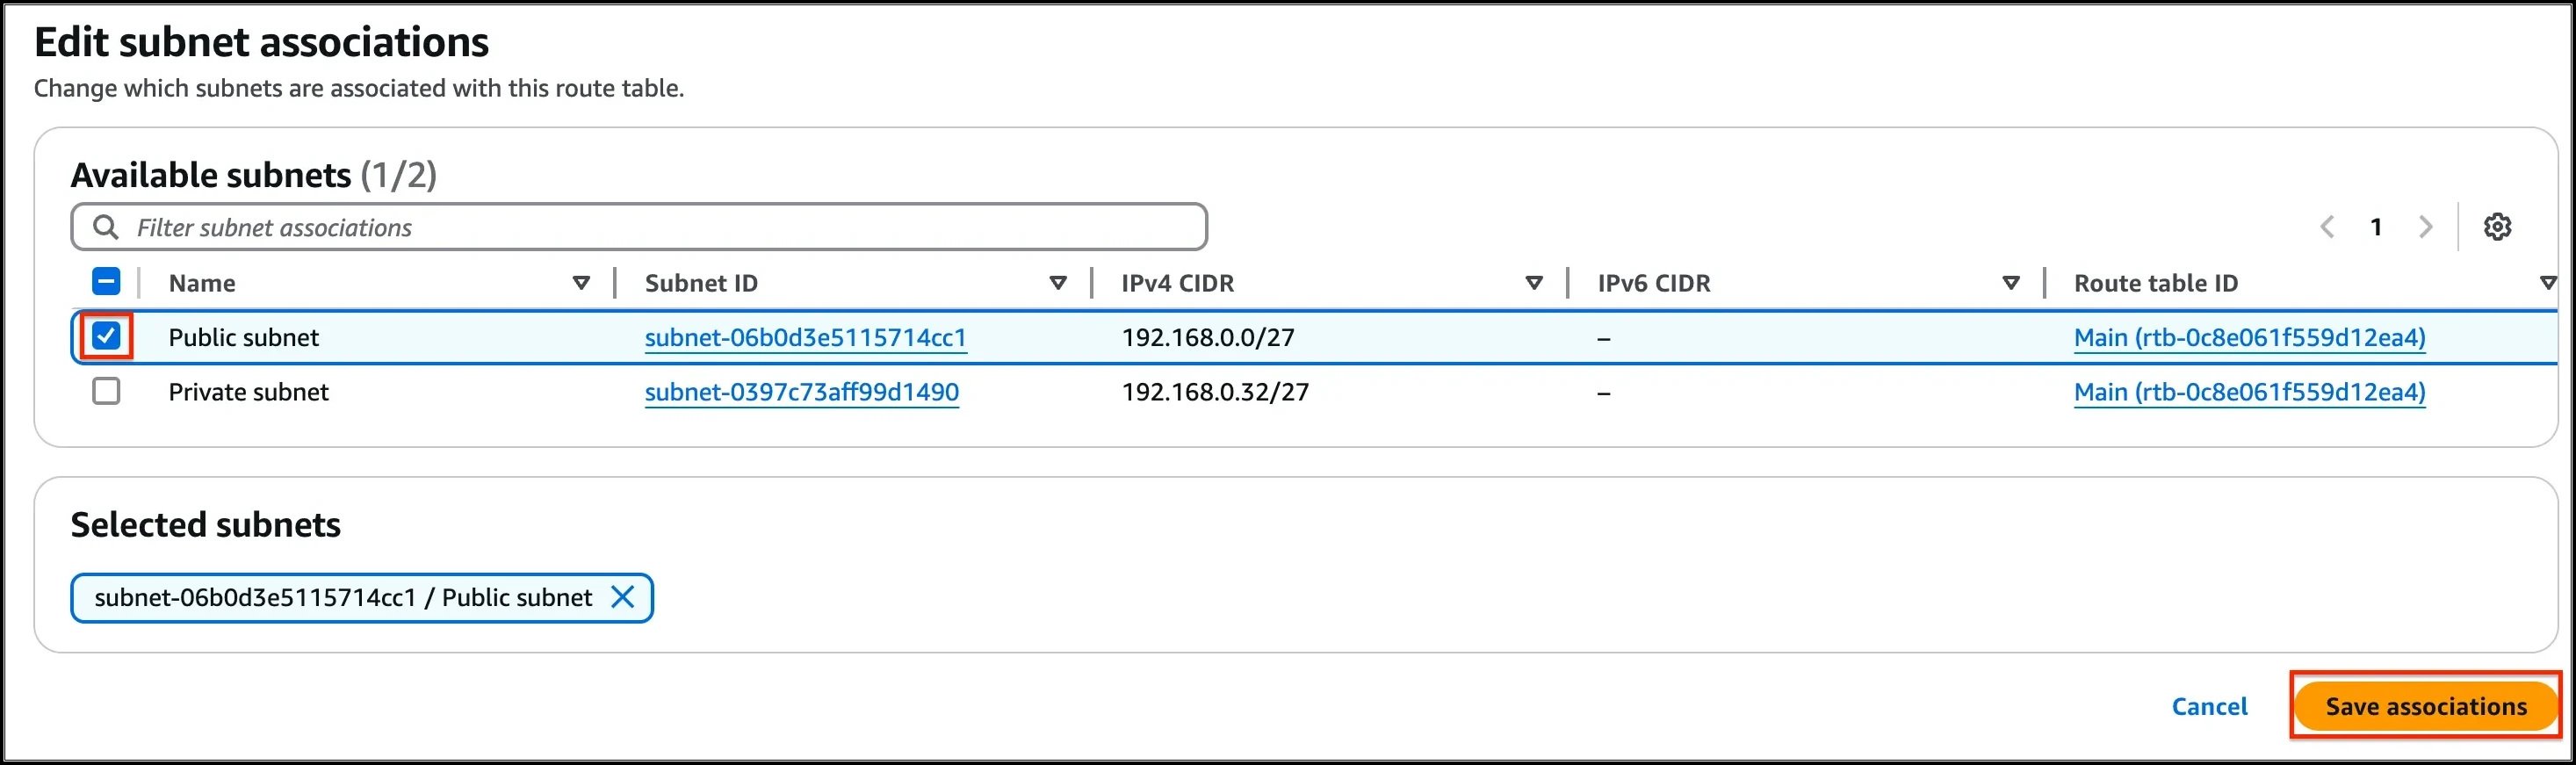
4. Select the **PublicRouteTable** and go to the **Subnet Associations** tab.
* Click on **Edit subnet associations.**
* Select **MyPublicSubnet** from the list.
* Click on **Save associations** button.
 5. Select the **PrivateRouteTable** and go to the **Subnet Associations** tab.
* Click on **Edit subnet associations**.
* Select **MyPrivateSubnet** from the list.
* Click on **Save associations** button.
6. Make sure not to associate any subnets with the **Main Route Table**.
7. **PublicRouteTable**: Add a route to allow Internet traffic to the VPC.
* Select **PublicRouteTable.**
* Go to **Routes** tab, click on **Edit routes** and on the next page, click on **Add route** button.
* Specify the following values:
* **Destination:** Enter ***0.0.0.0/0***
* **Target:** Select **Internet Gateway** from the dropdown menu to select **MyInternetGateway**.
* Click on **Save changes** button.
#### Task 7: Create Security groups
1. In this lab, we will create two security groups, the **first one will be used for Bastion host** and the **second one for private instance having access to VPC Endpoint for S3.**
2. To get started with creating security groups, click on the **Security groups** , present in the **SECURITY** section in the left sidebar.
3. Click on the **Create Security group** button
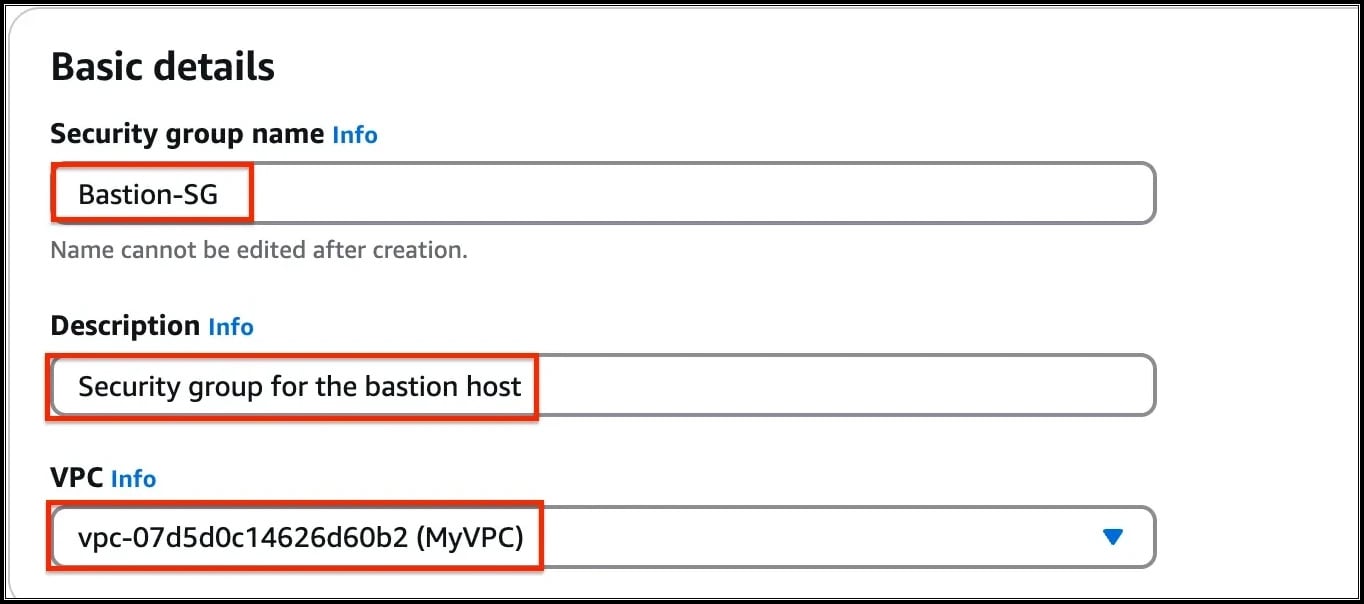
4. Fill in the below details under **Basic details**:
* Enter **Security group** name as ***Bastion-SG***
* Enter **Description** as ***Security group for the bastion host***
* Select the **MyVPC** under the **VPC** field.
 5. By default, no inbound rule will be allowed, and when you check in the outbound rules, there is only one rule present that has a Type with **All traffic** because **Security groups are Stateful** in nature, **when inbound is allowed outbound is also allowed.**
6. To add the Inbound rules for the same, click on the **Add rule** button.
7. We will add **3 rules** for the Bastion host security group i.e. **SSH, HTTP, and HTTPS.**
* For the first rule, Select the **Type** as ***SSH***, **Source** as **Anywhere-IPv4** and **enter** ***0.0.0.0/0***
* For the second rule, click on the **Add rule** button. Select the **Type** as ***HTTP***, **Source** as **Anywhere-IPv4** and **enter** ***0.0.0.0/0***
* For the third rule, click on the **Add rule** button. Select the **Type** as ***HTTPS***, **Source** as **Anywhere-IPv4** and **enter** ***0.0.0.0/0***
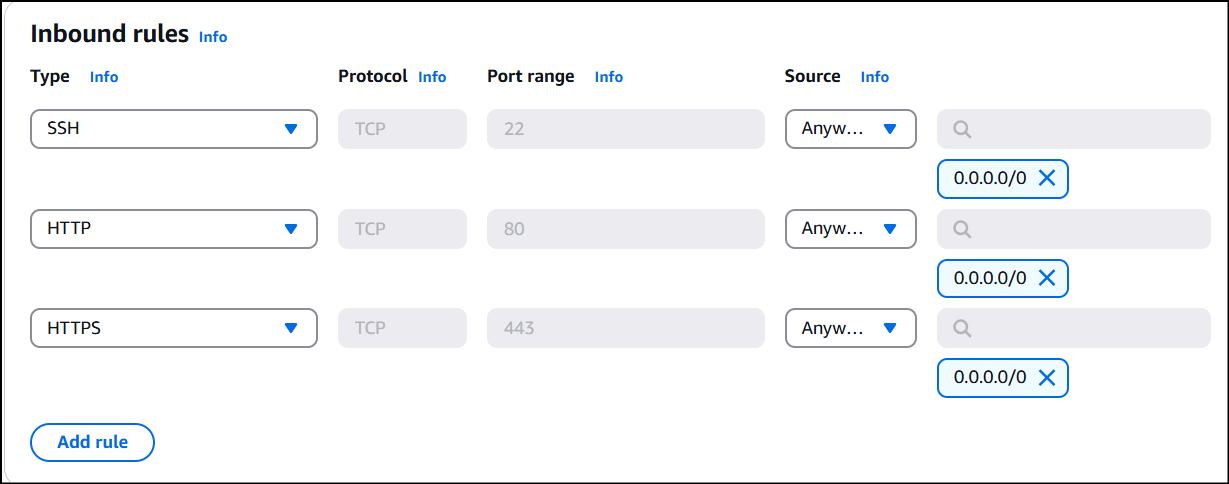 8. Finally, click on the **Create Security group** button.
9. The security group for the Bastion host is now created.
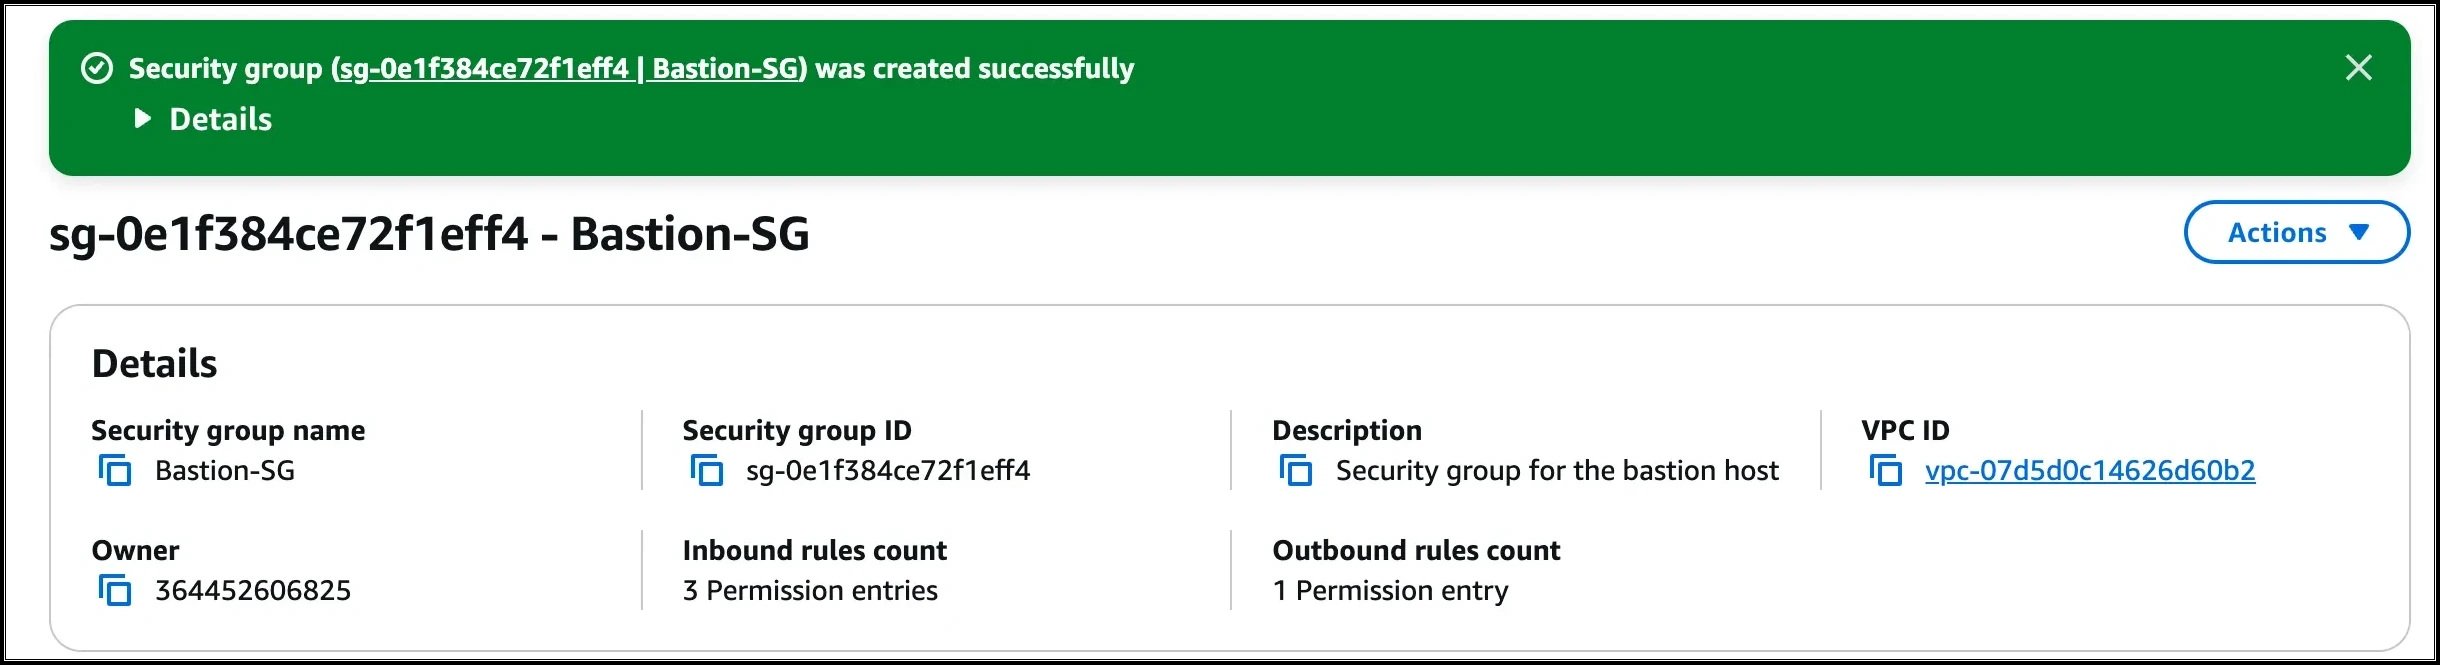 10. Click on the **Security groups** button, present in the **SECURITY** section in the left sidebar.
11. To create the second security group, click on the **Create Security Group** button.
12. Fill in the below details under **Basic details**:
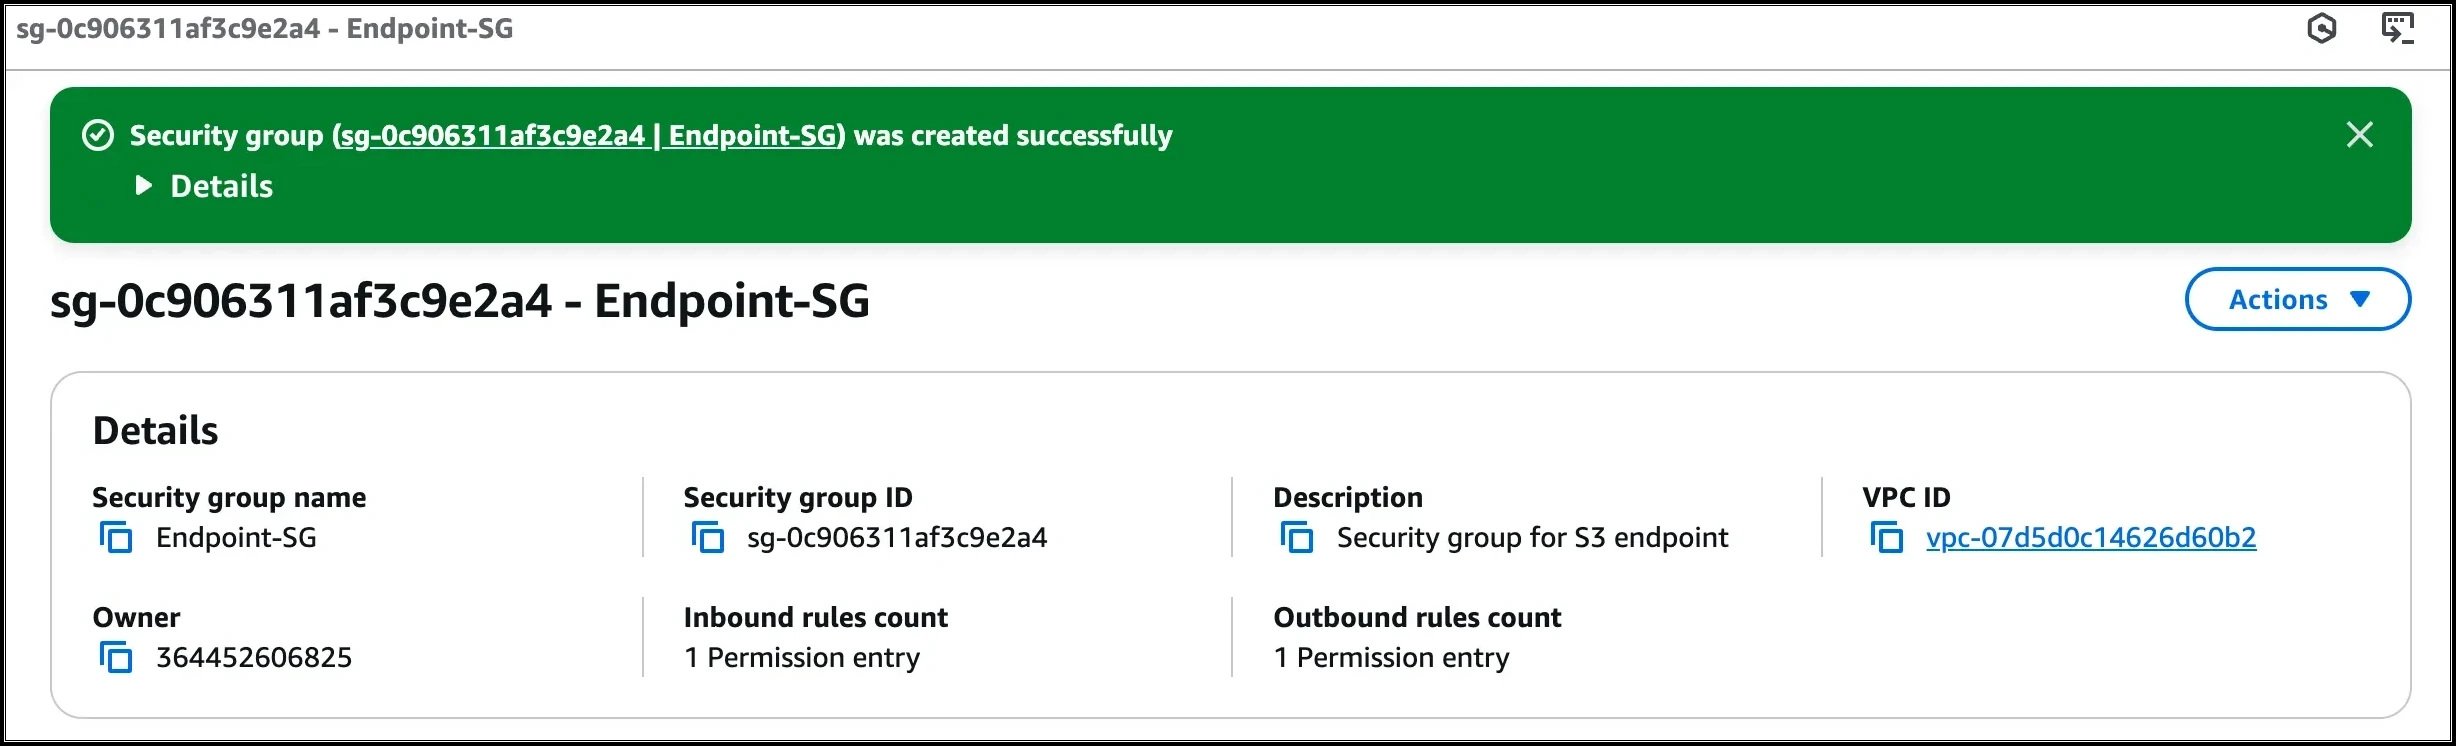
* Enter **Security group** name as ***Endpoint-SG***
* Enter **Description** as ***Security group for S3 endpoint***
* Select the **MyVPC** under the **VPC** field.
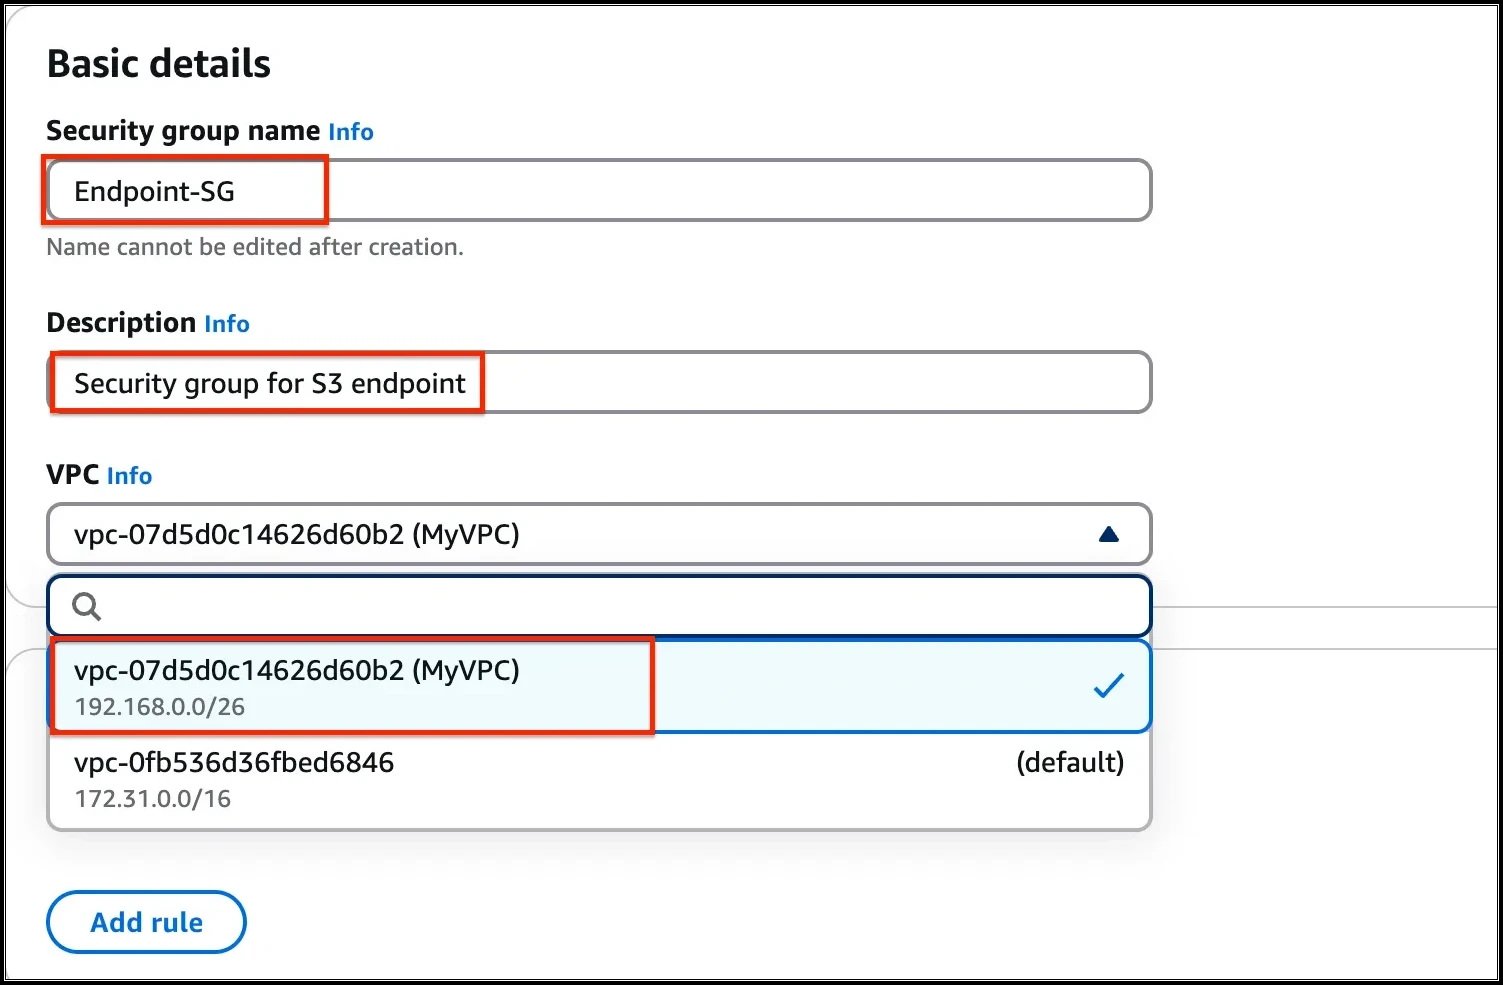 13. To add the Inbound rules for the same, click on the **Add rule** button.
14. We will add **1 rule** for the S3 endpoint security group i.e. **SSH** ***only***\*\*.\*\* But here our source will be **Bastion host security group**,
you will select the **ID of Bastion-SG** security group.
* For the rule, select the **Type** as ***SSH***, **Source** as **Custom,** and **type** ***Bastion***\*\*,\*\* Bastion hosts security group will be shown, select that Security group.
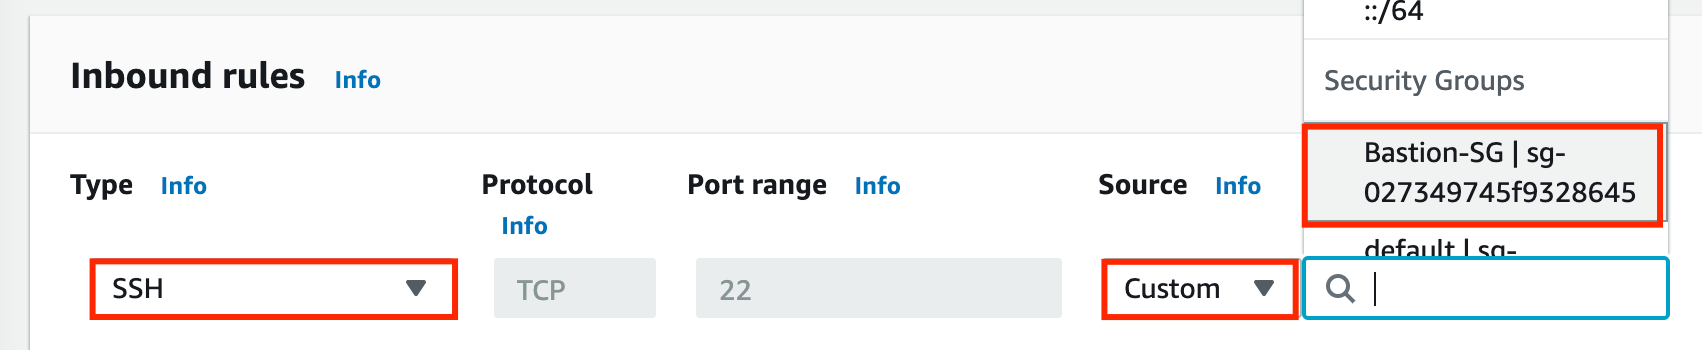 15. Finally, click on the **Create Security group** button.
16. The security group for the Bastion host is now created. And, it will be listed there.
 #### Task 8: Create a Bastion host (Publicly accessible EC2 Instance)
1. Navigate to **EC2** by clicking on the **Services** menu at the top, then click on **EC2** in the **Compute** section.
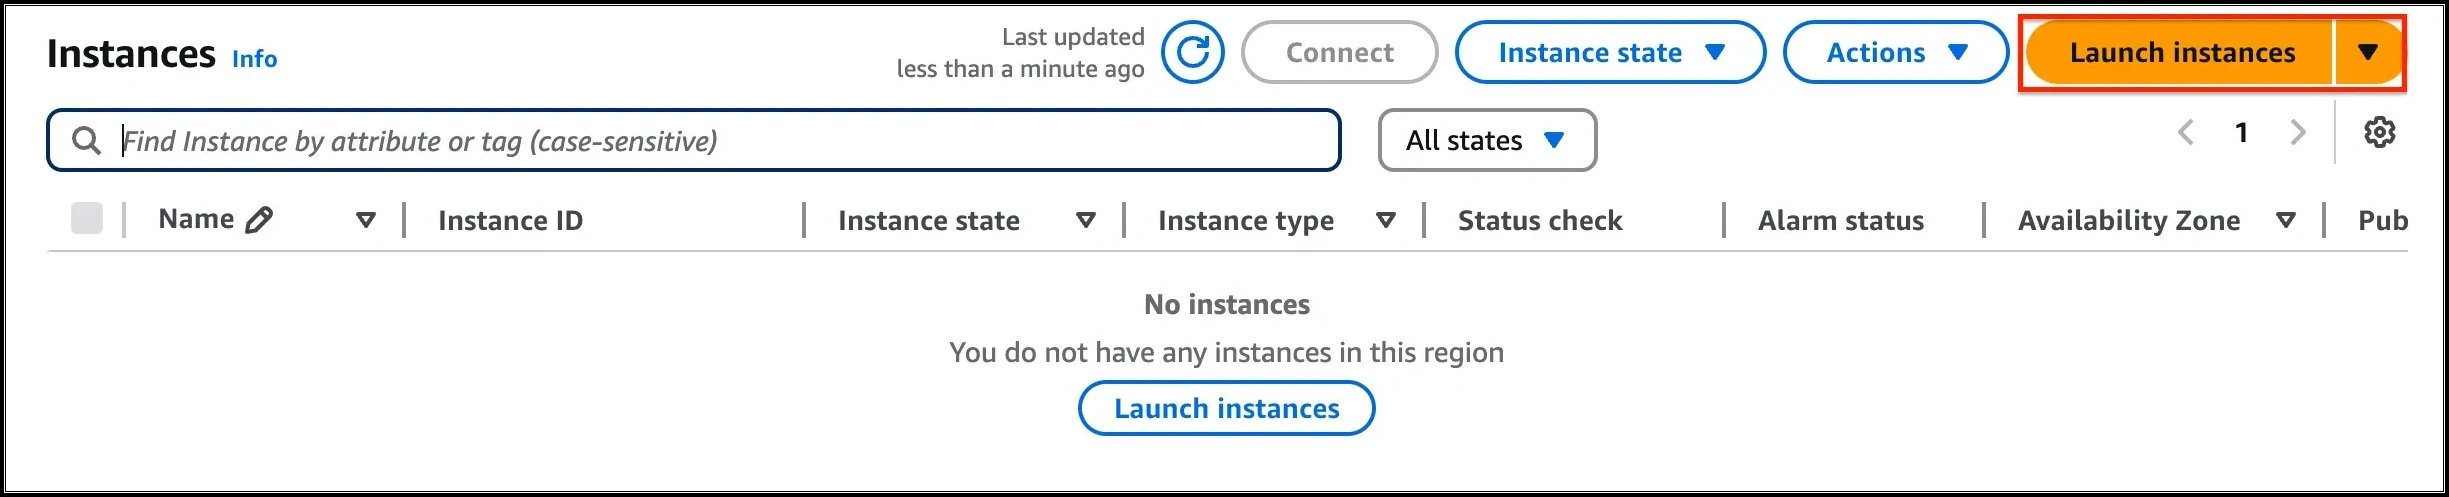
2. Navigate to **Instances** on the left panel and click on **Launch instances.**
 3. Name : Enter ***Bastion-host.***
4. For Amazon Machine Image (AMI)**:** Search for **Amazon Linux 2023 AMI** in the search box and click on the **Select** button
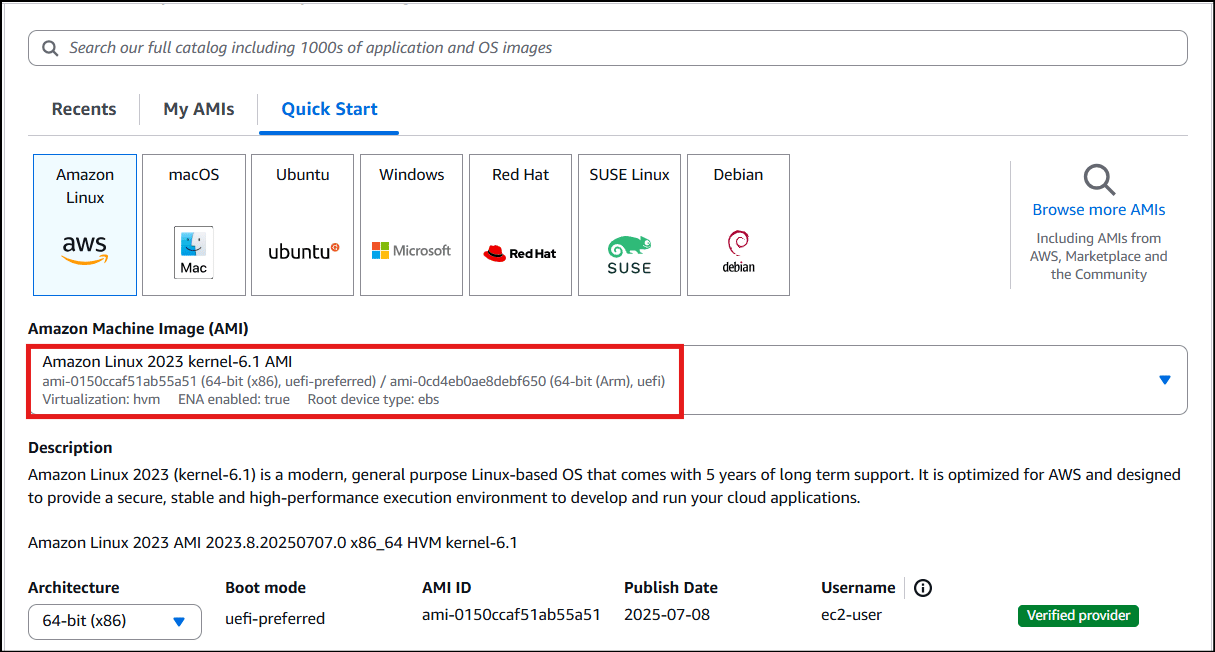 5 . **Note: if there are two AMI's present for Amazon Linux 2023 AMI, choose kernel-6.1 AMI.**
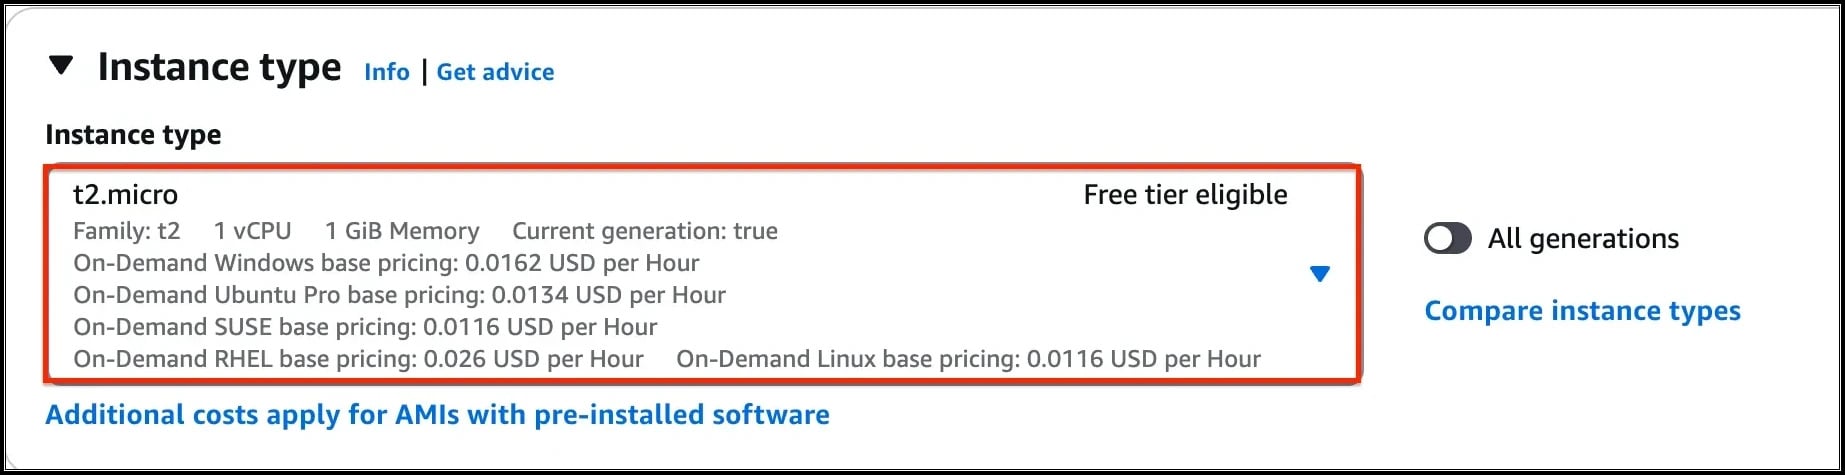
6. For Instance Type: select ***t2.micro***
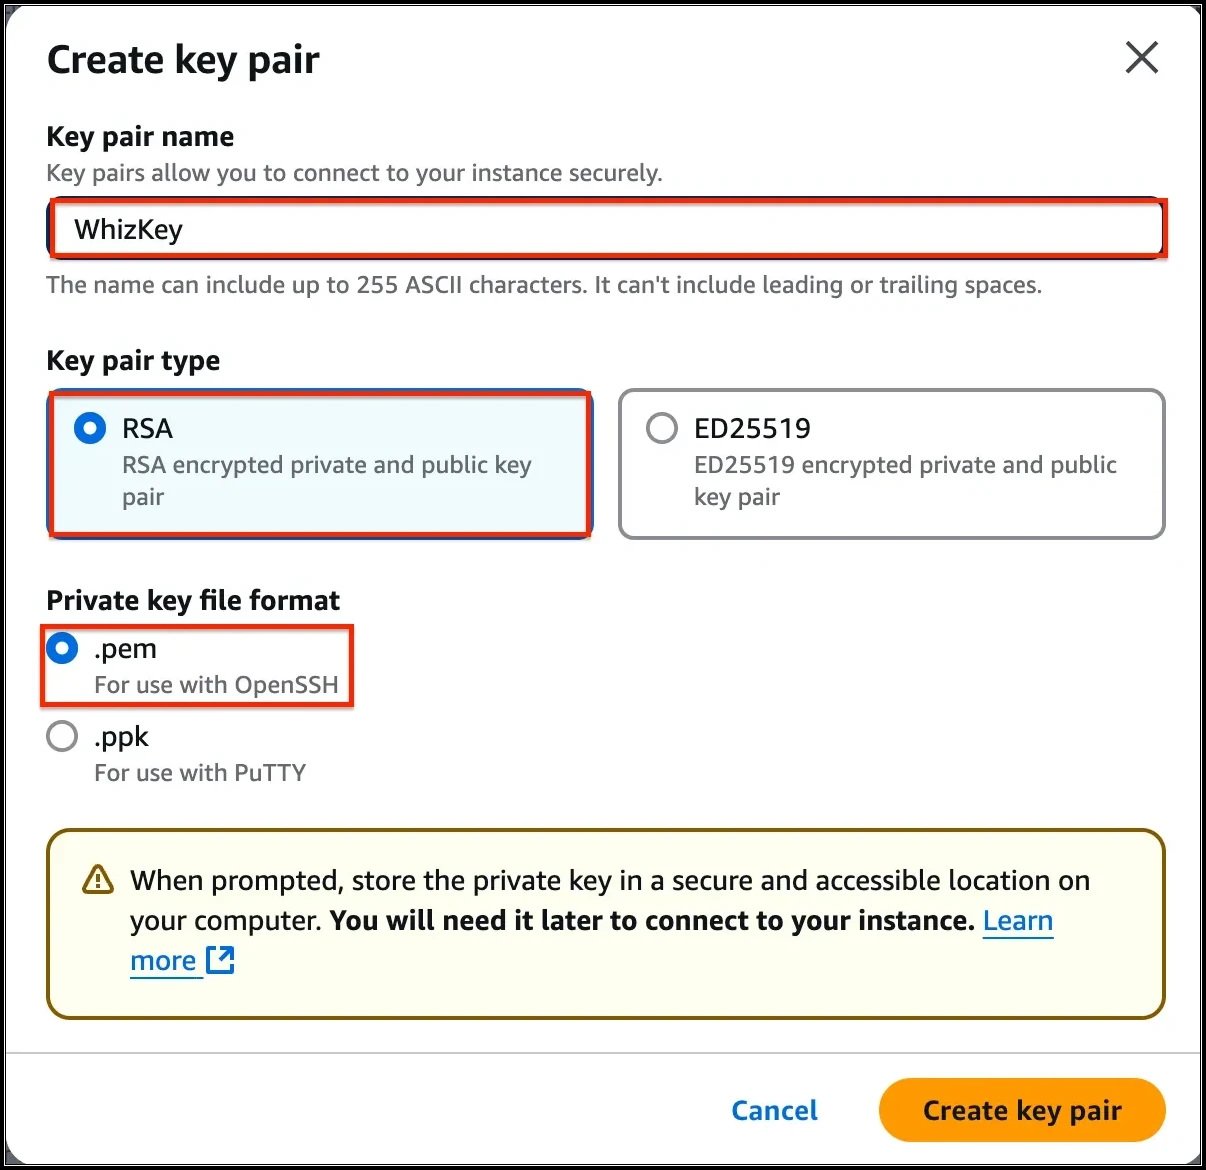
 7. For Key pair: Select **Create a new key pair** Button
* Key pair name: **WhizKey**
* Key pair type: **RSA**
* Private key file format: **.pem**
8. Select **Create key pair** Button.
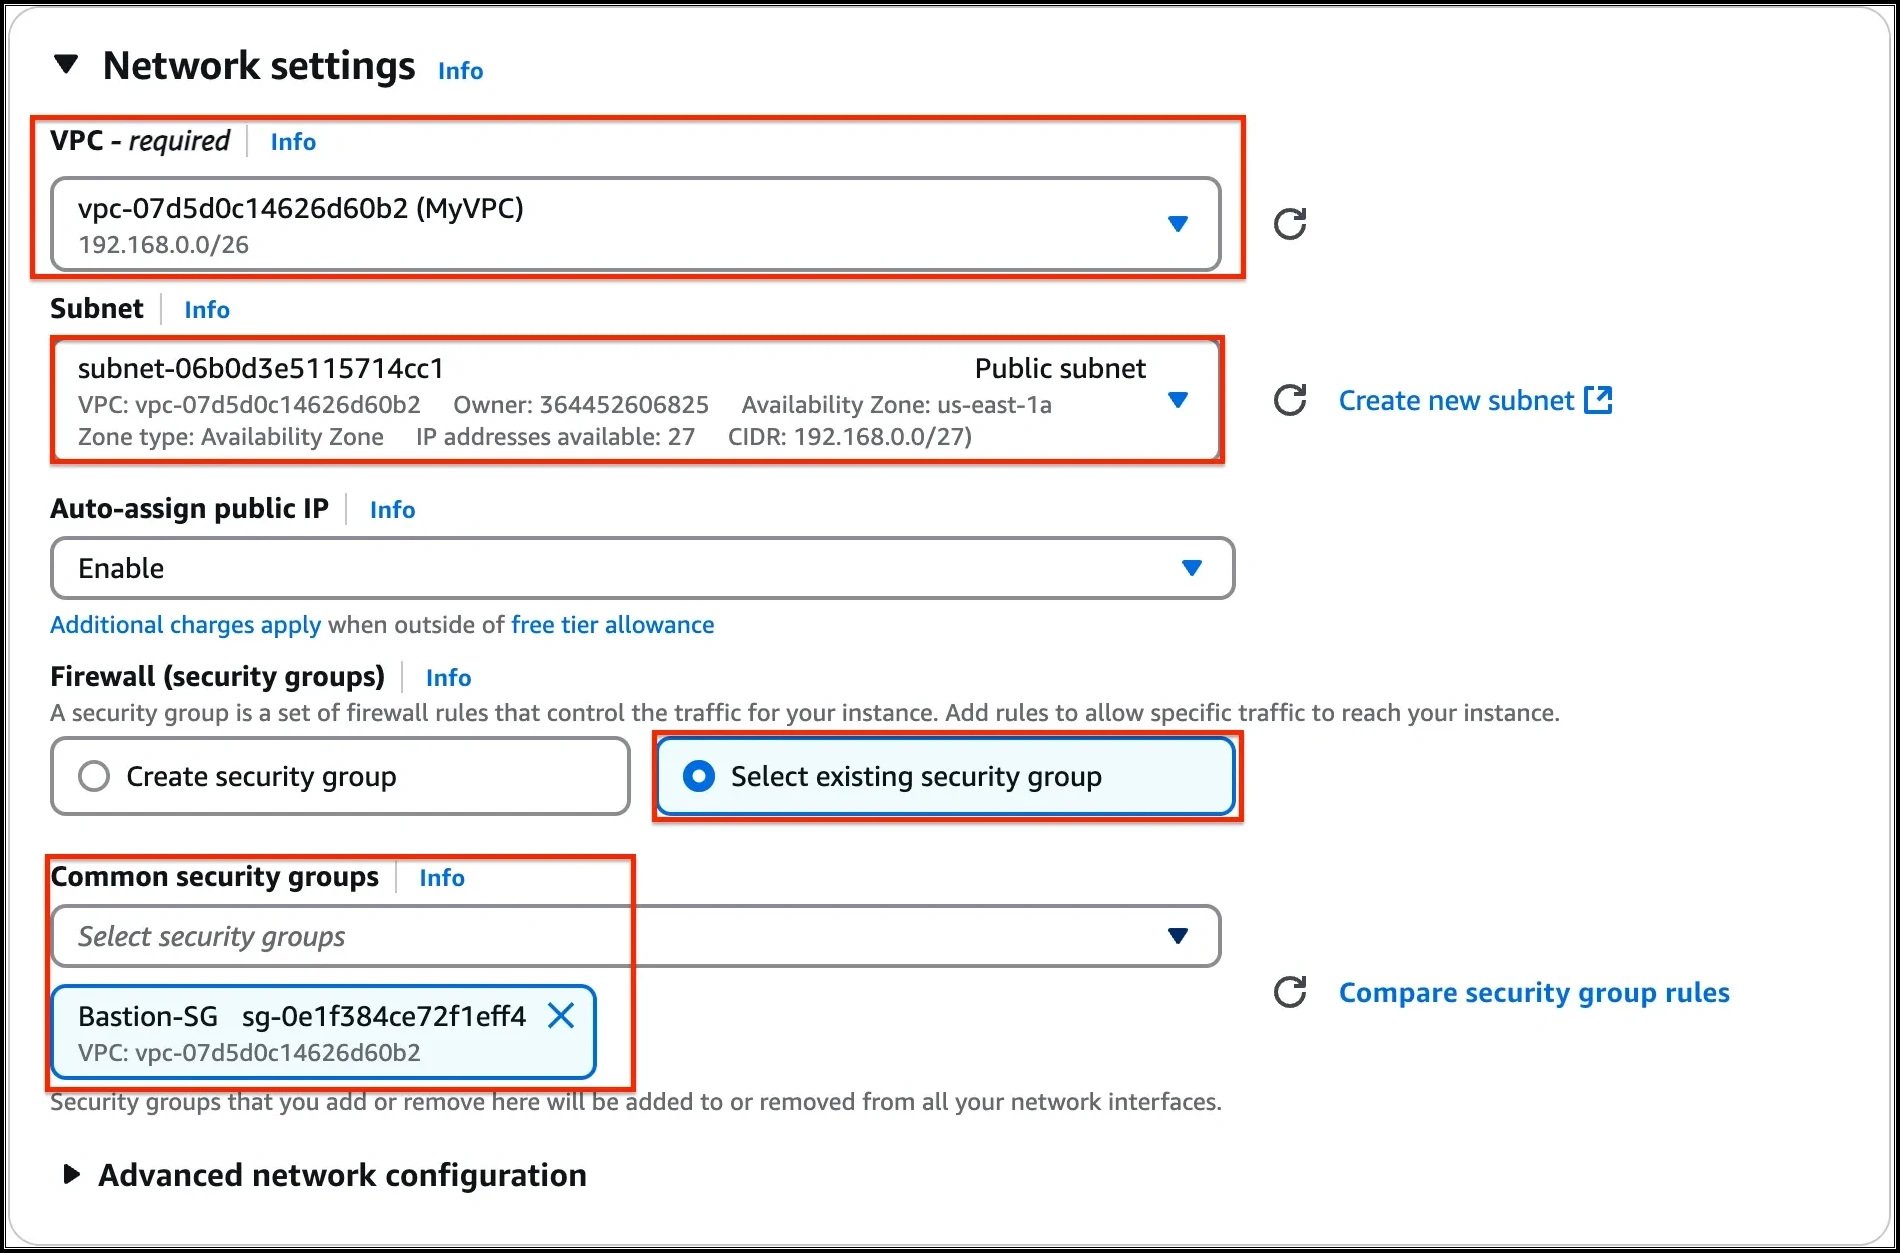
 9. In Network Settings Click on **Edit** Button:
* VPC: Choose **MyVPC**
* Subnet : Choose **Public Subnet**
* Auto-assign public IP: **Enable**
* Select **existing security group**
* Security group name : Choose **Bastion-SG**
 10. Keep rest thing default and Click on **Launch Instance b**utton.
11. Select **View all Instances** to view Instance you created
12. **Launch Status:** Your instance is now launching, Click on the instance ID and wait for complete initialization of the instance till status changes to **Running**.
#### Task 9: Create an Endpoint instance (Privately accessible EC2 instance)
1. Navigate to **EC2** by clicking on the **Services** menu at the top, then click on **EC2** in the **Compute** section.
2. Navigate to **Instances** on the left panel and click on **Launch instances.**
3. Name : Enter ***Endpoint-instance.***
4. **For Amazon Machine Image (AMI):** Search for **Amazon Linux 2023 AMI** in the search box and click on the **Select** button.
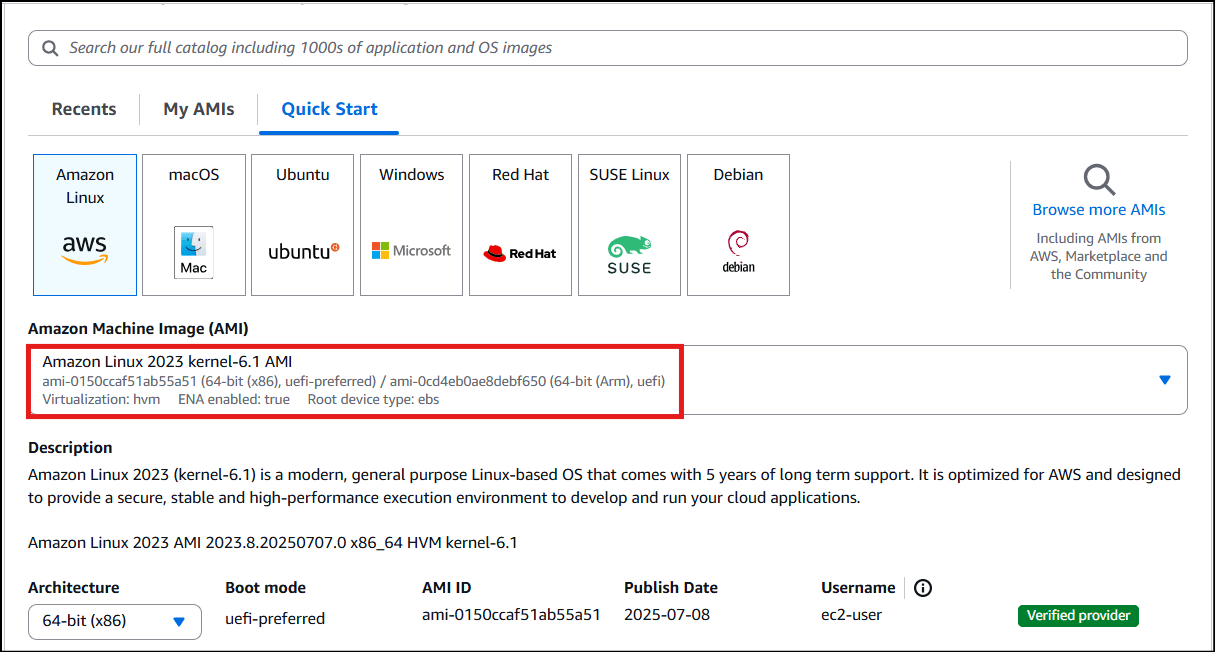 5 . **Note: if there are two AMI's present for Amazon Linux 2023 AMI, choose kernel-6.1 AMI.**
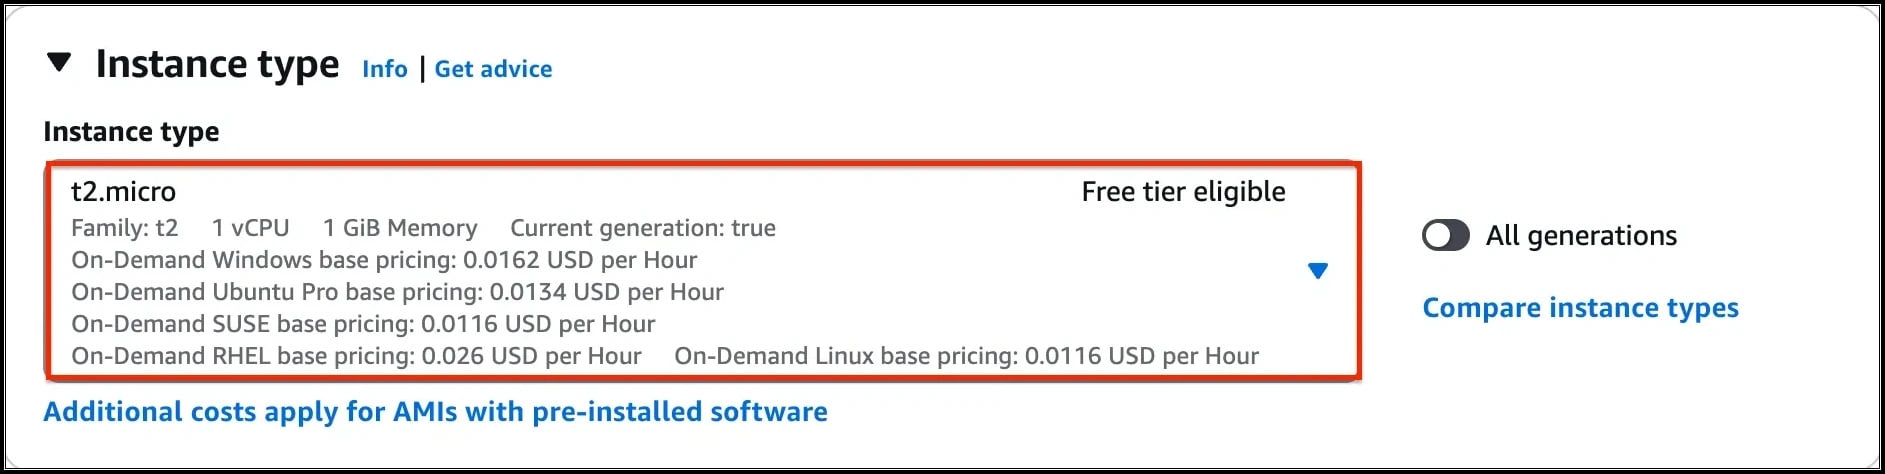
6. For Instance Type: select ***t2.micro***
 7. For Key pair: Select the key pair made during the previous task.
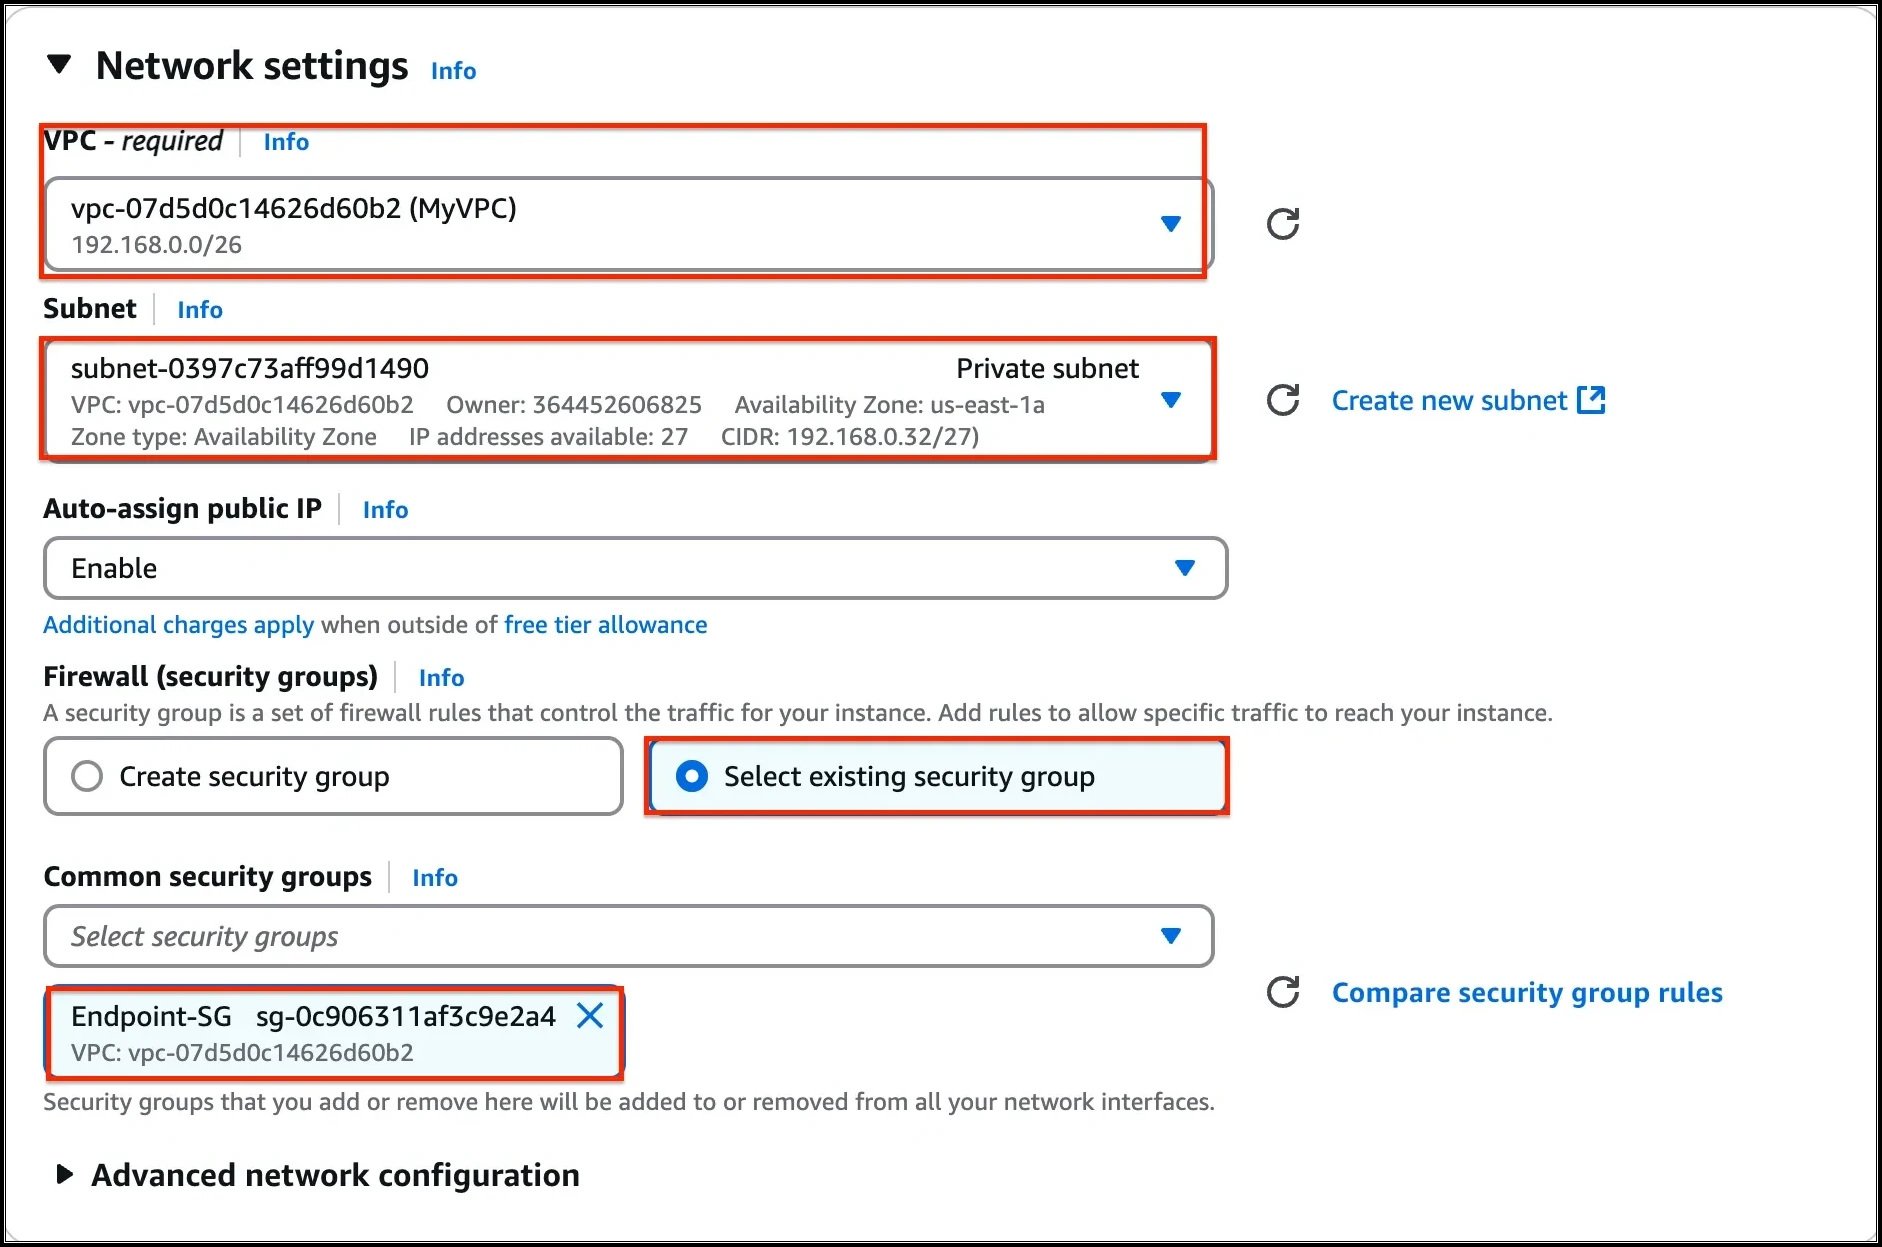
8. In Network Settings Click on **Edit** Button:
* VPC: Choose **MyVPC**
* Subnet : **Private Subnet**
* Select **existing security group**
* Security group name : Choose **Endpoint-SG**
 9. Keep rest thing Default and Click on **Launch Instance b**utton.
10. Select **View all Instances** to view Instance you created
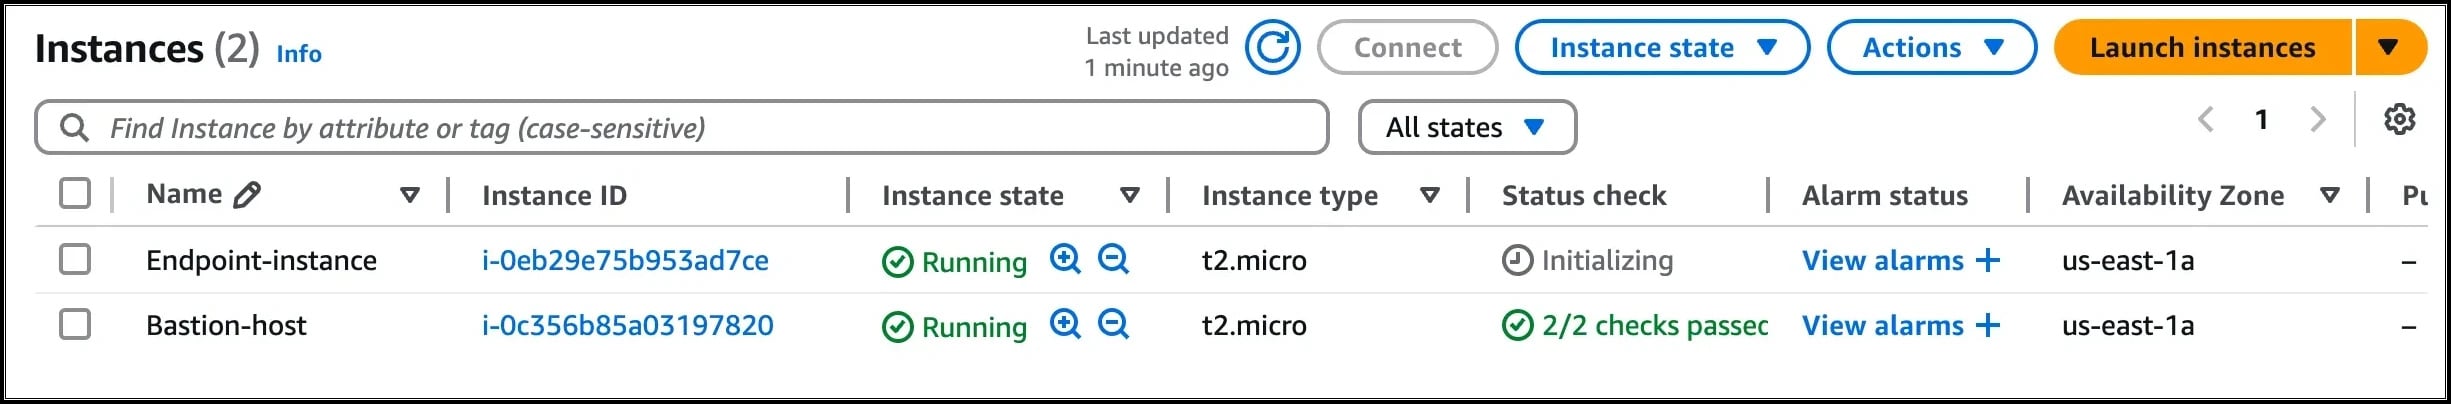
11. **Launch Status:** Your instance is now launching, Click on the instance ID and wait for complete initialization of the instance till status changes to **Running**.
12. Navigate to **Instances** and wait for 1-2 minutes (until the **Endpoint-instance's** status changes from **pending** to **running** state)
 #### Task 10: SSH into Endpoint instance (Privately accessible) through Bastion host
1. [SSH into the Bastion instance](https://play.whizlabs.com/site/task_support/ssh-into-ec-instance) using the Bastion PEM key: **WhizKey.pem**
2. To SSH into **Endpoint instance via the Bastion instance**, we need the **WhizKey.pem** to be present on the **Bastion instance.**
3. Open the **WhizKey.pem** file on your local system and then **copy the text content**.
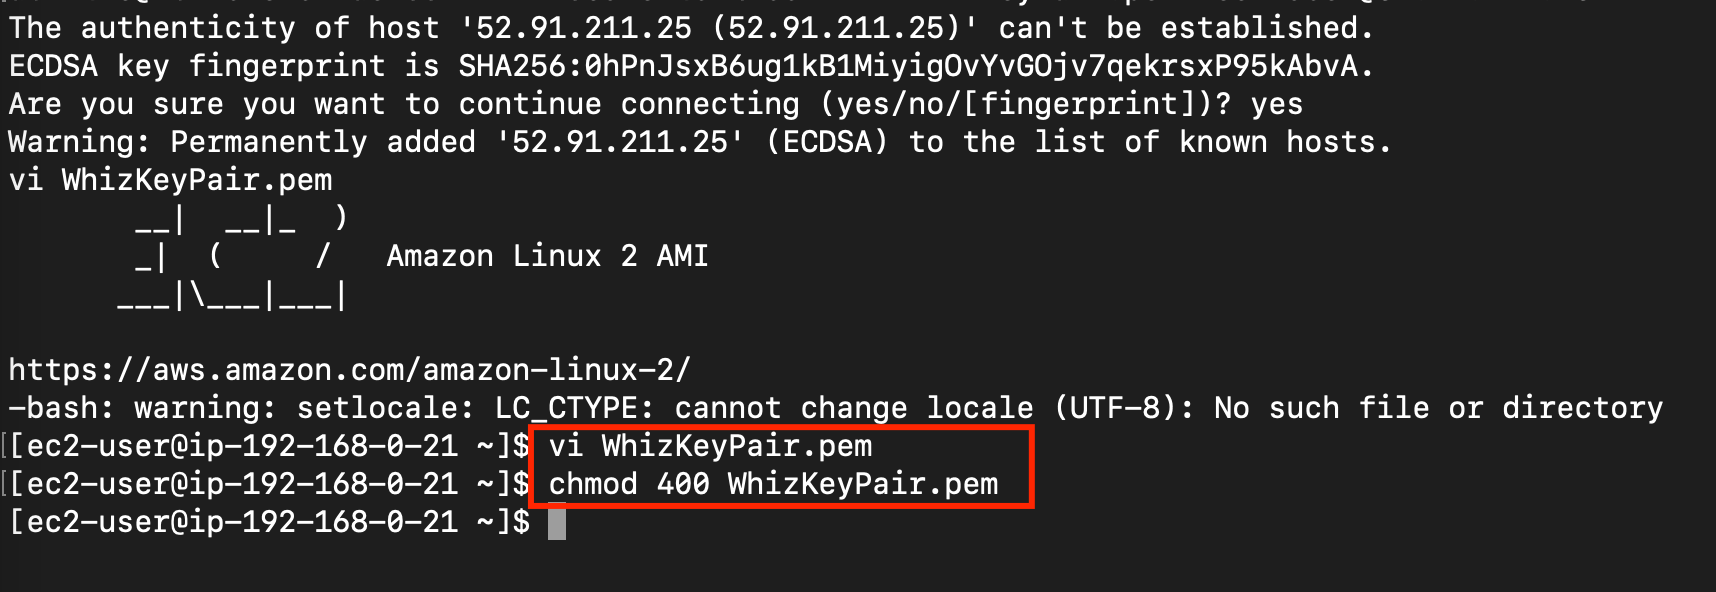
4. Navigate to the Bastion Instance and create a file named **WhizKey.pem** using the below command:
vi WhizKey.pem
5. Press **i** and paste the content of **WhizKey.pem.** Save it by pressing **Esc key** and type **:wq** and hit **Enter.**
6. Make sure you have changed the **permission of the key file to 400**. You can change the permission using the below command:
chmod 400 WhizKey.pem
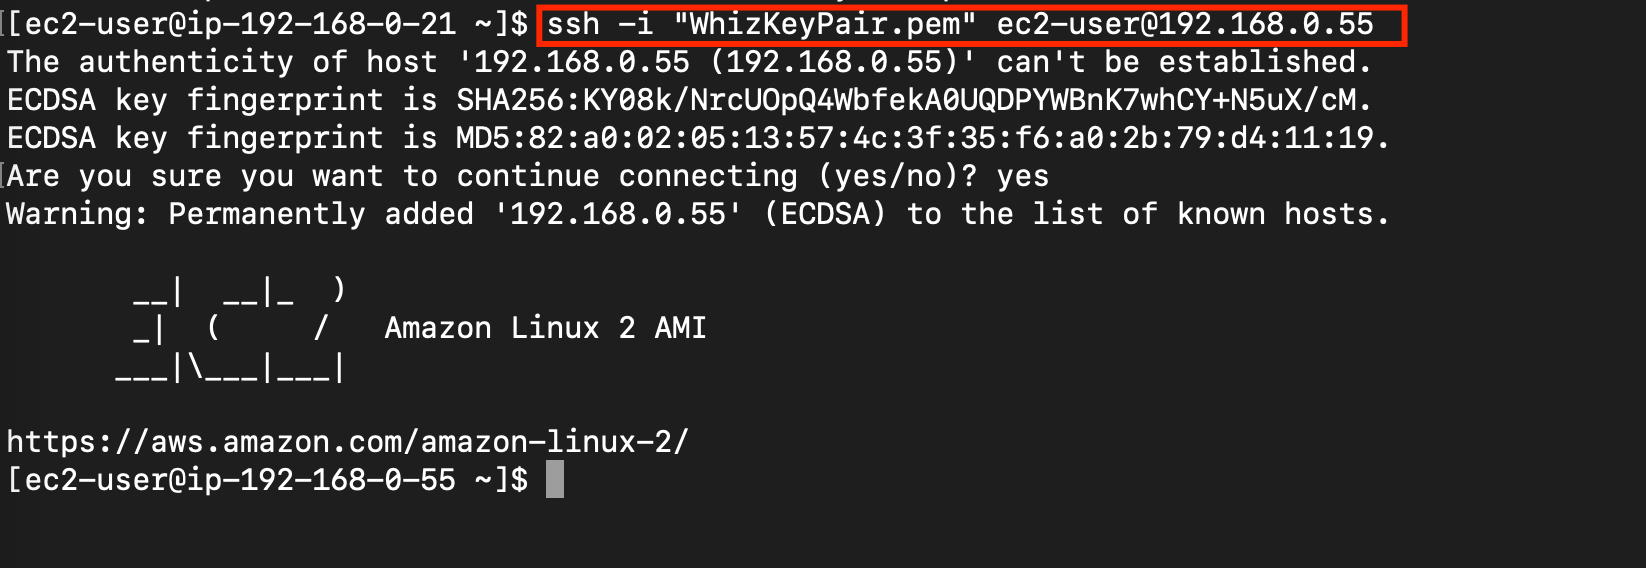
 7. Now **you can log into the web servers** using the private key copied to the bastion server with the help of the below commands.
* **Note:** You **don't have public IP's** for the Endpoint instance since we created them in a private **subnet.**
* Syntax **: ssh -i WhizKey.pem ec2-user@\<**Endpoint instance's Private IP**>**
* Example: **ssh -i WhizKey.pem ec2-user\@192.168.0.55.**
* When asked for confirmation type: **yes**
 * Enter the following command **aws configure**
* Access Key: Paste the access key provided to you
* Secret Key: Paste the secret key provided to you
* Default region name: us-east-1
* Default output-format: Enter \[**ENTER**]
> - **Note**: Though the assigned IAM role is having access for S3 Read, listing the bucket through AWS CLI command got failed, saying, connection timeout on S3's endpoint.
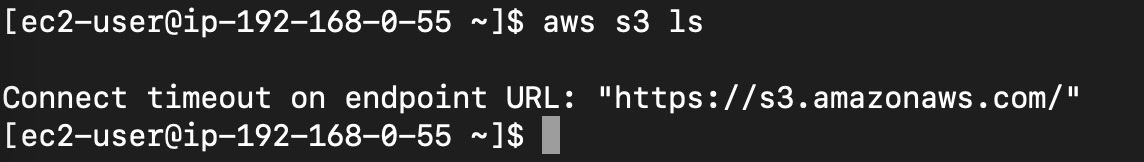 8. As, this instance's security group is only allowed to do SSH, running any other command, will fail.
9. Let's add the permission to access the S3 endpoints using the VPC Endpoint for S3.
#### Task 11: Create a VPC Endpoint for S3, attach it to the Private subnet's Route table
1. Navigate to **VPC** by clicking on the **Services** menu at the top, then click on **VPC** in the **Networking and Content Delivery** section.
2. Click on **Endpoints** present under **PrivateLink and Lattice.**
3. Click on the **Create endpoints** button.
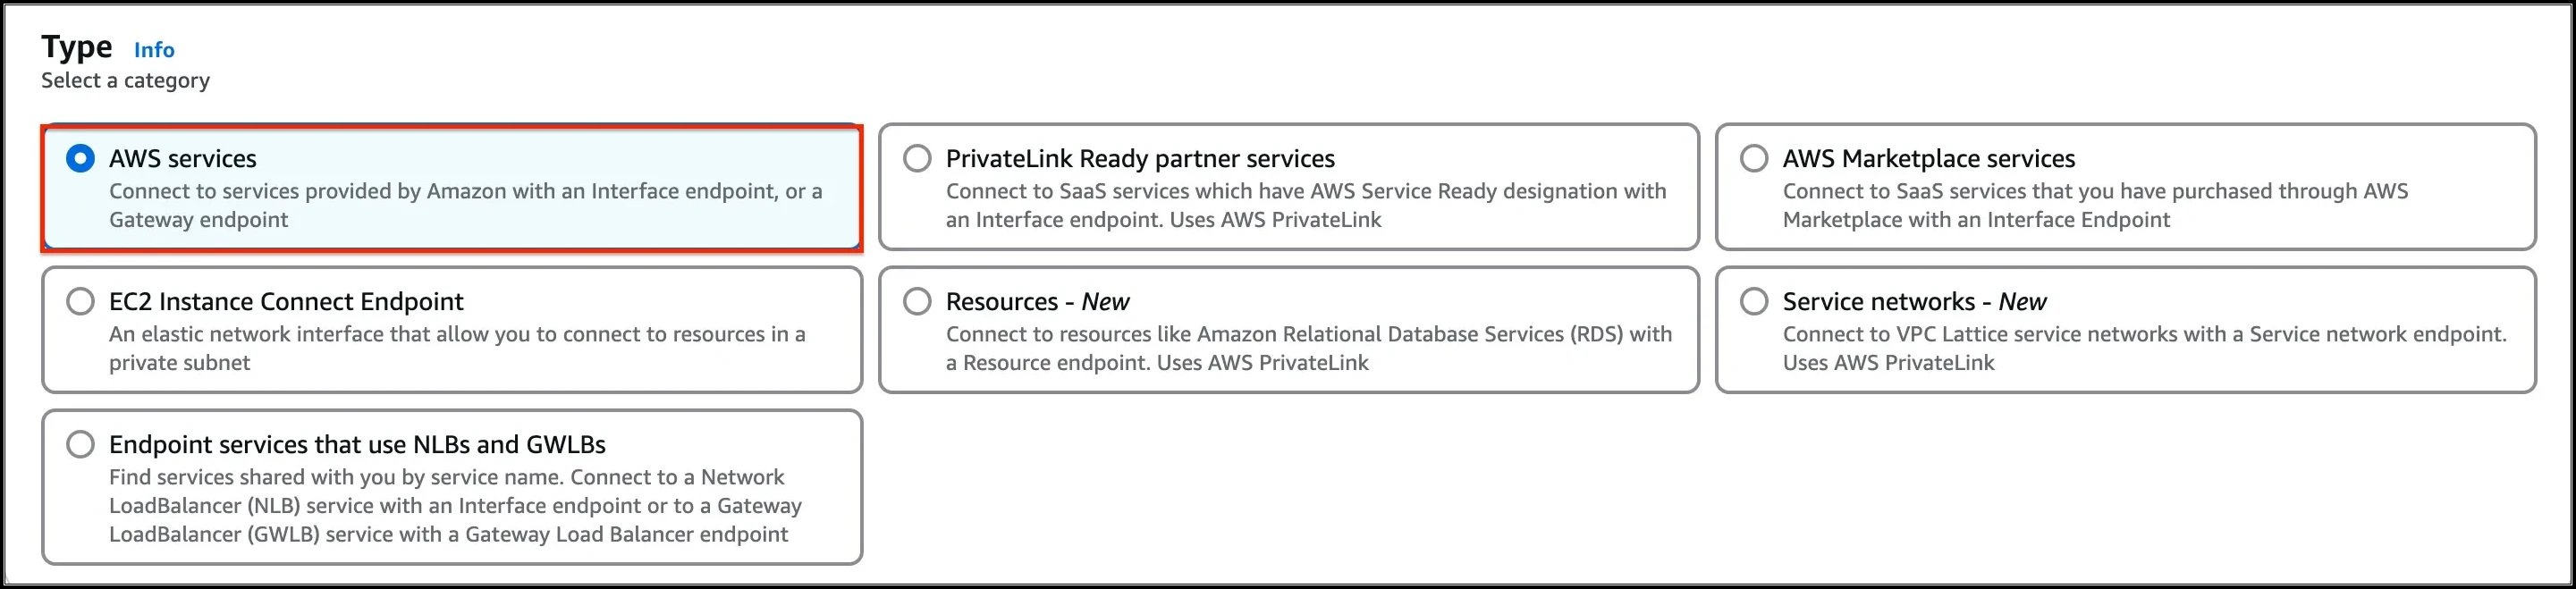
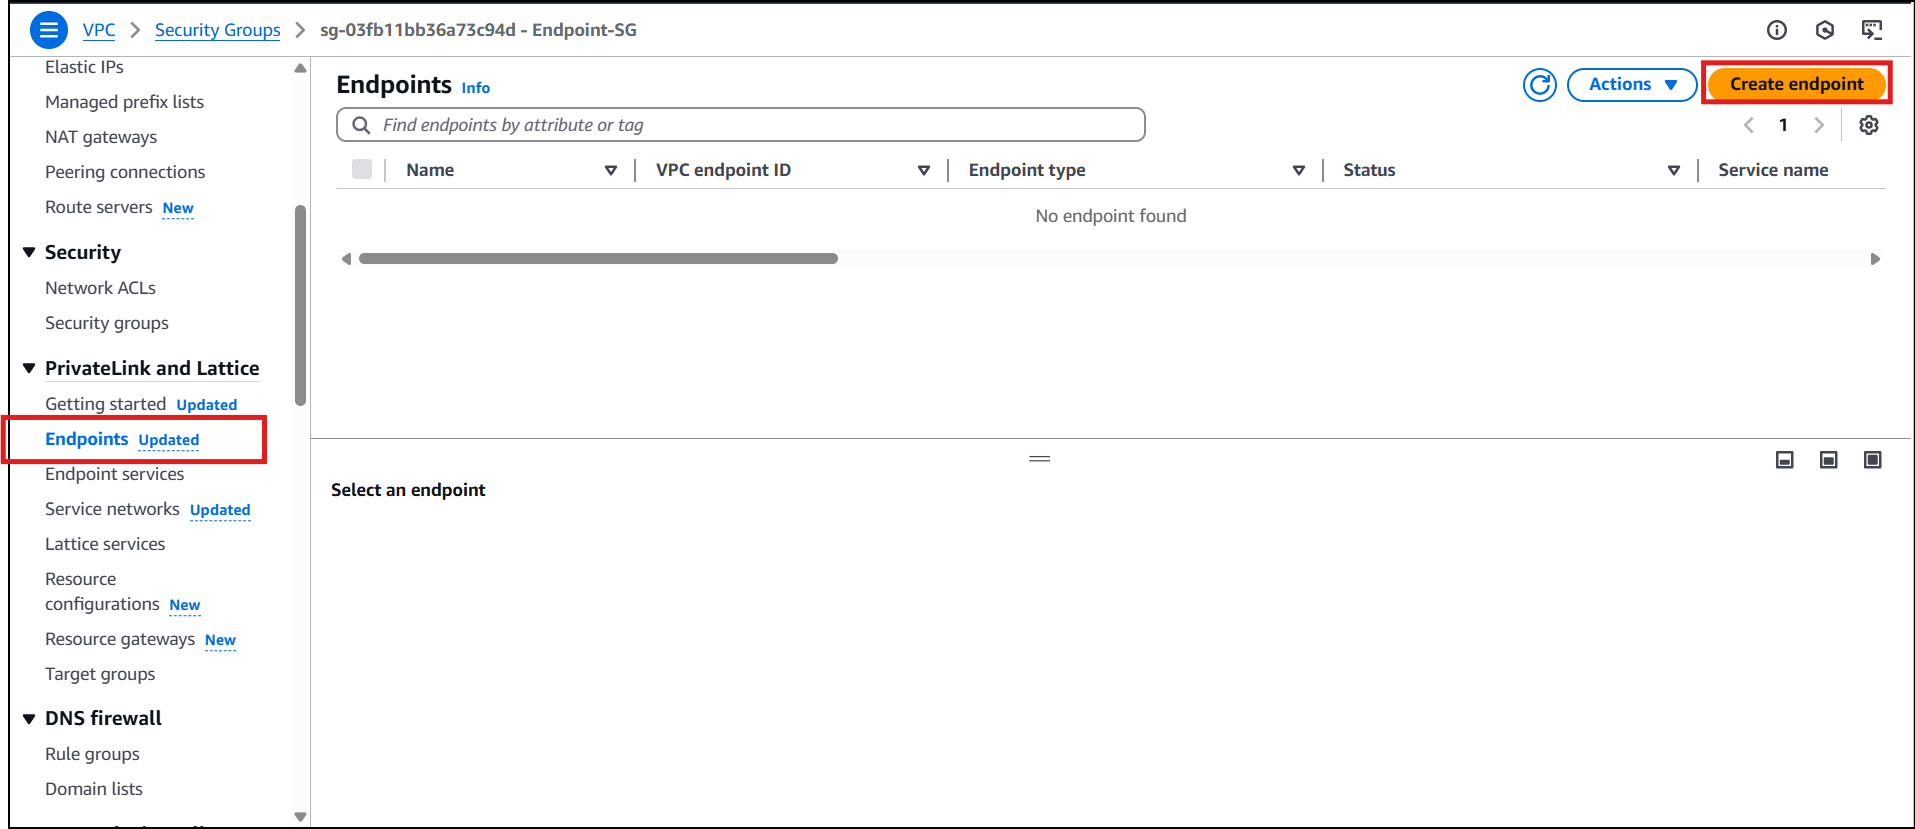 4. Make sure the **Service category** is selected for **AWS services.** In the **Service name** search bar, **type** ***s3***\*\*,\*\* and **press enter**
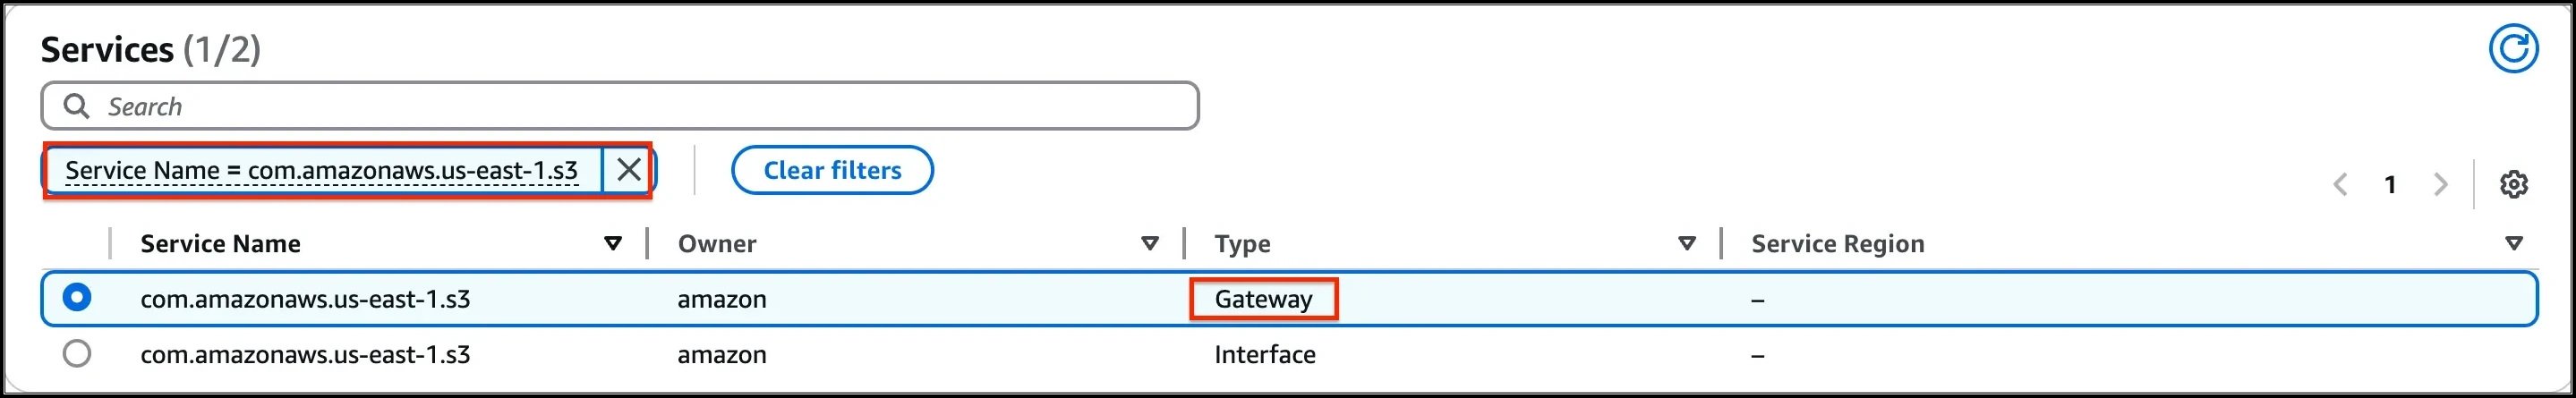 5. The endpoint of **Type**, **Gateway** with Service name as **com.amazonaws.us-east-1.s3** will be listed.
6. Change the VPC, and select **MyVPC**.
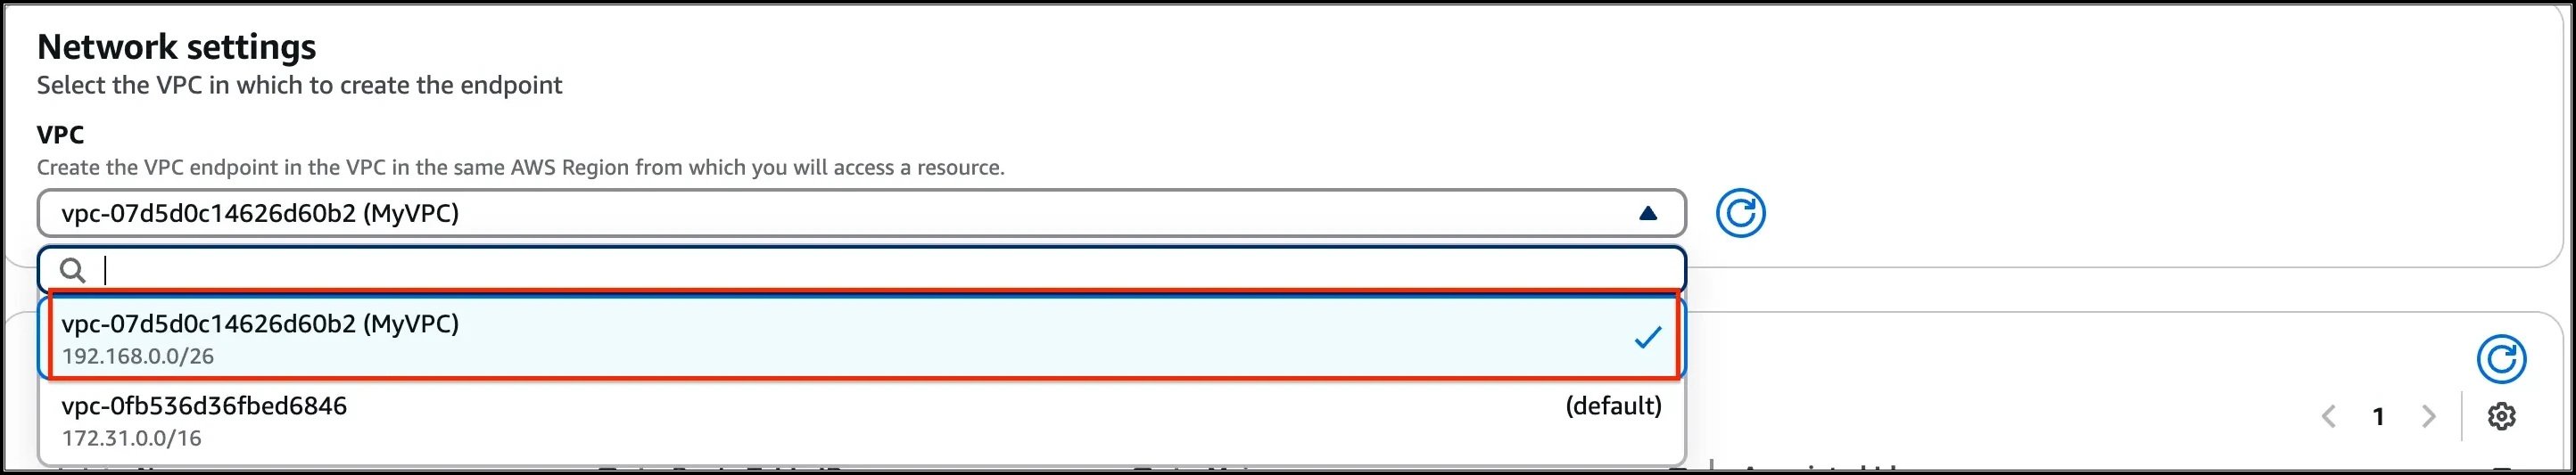 7. Check the option for Route Table having name as **PrivateRouteTable.**
8. Finally, click on the **Create endpoint** button.
9. An **endpoint** will be created.
10. Click on the **Close** button, and within a few moments, you will see the **endpoint** will be listed.
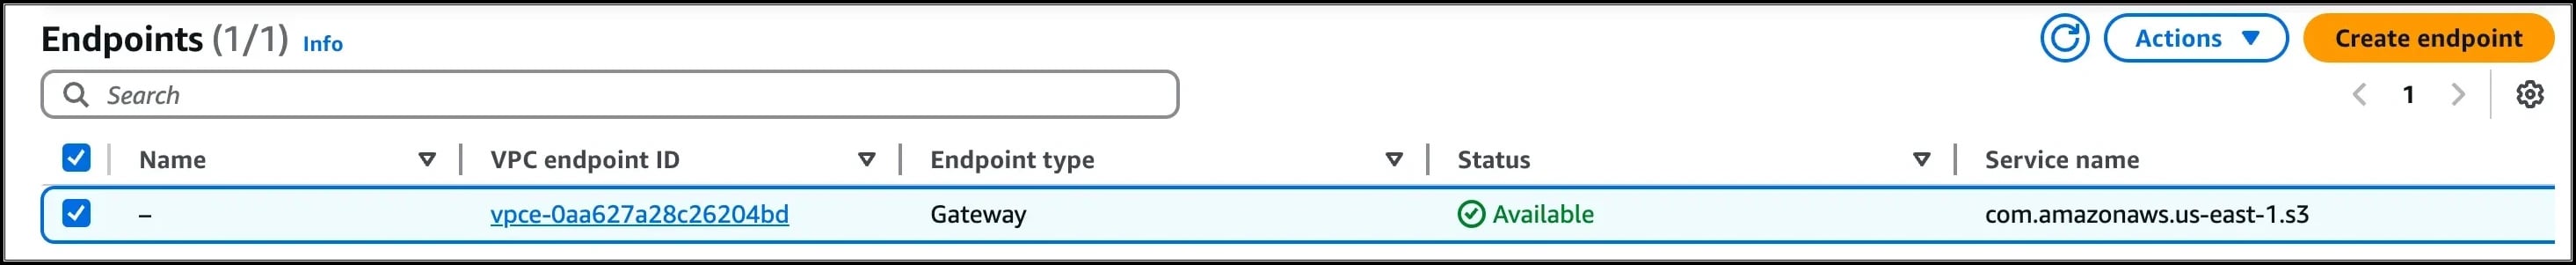 11. (Optional) To check whether the endpoint is associated with the custom route table (RT for Private subnet) or not.
12. Go to the Route tables, Select the custom route table and click on the **Routes** options below, you will see an entry of S3.
#### Task 12: List all the S3 bucket and it's objects
1. Now SSH into the **Endpoint instance** from your bastion instance as mentioned in **task 10**.
Enter **aws configure.**
* Access Key: Paste the access key created earlier.
* Secret Key: Paste the secret key created earlier.
* Default region name: us-east-1
* Default output-format: Enter **\[ENTER]**
2. List all the bucket's using the following AWS CLI command:
aws s3 ls
 3. List the objects of the S3 bucket starting with name whizlabs..
4. Replace the S3 bucket name for the below command
aws s3 ls s3://whizlabs
> #### Do you know?
>
> VPC Endpoint Service enables private connectivity, you can avoid data transfer charges associated with public internet traffic. By utilizing VPC endpoints, you can significantly reduce data transfer costs, especially if you have large volumes of data flowing between your VPC and AWS services.
1. Once the lab steps are completed, please click on the **Validation** button on the Right side panel.
#### Task 13: Delete AWS Resources
#### Delete VPC Endpoint
1. Navigate to **VPC** by clicking on the **Services** menu at the top, then click on **VPC** in the **Networking and Content Delivery** section.
2. Click on **Endpoints** present in the **VIRTUAL PRIVATE CLOUD** section on the left sidebar.
3. To delete the VPC endpoint, perform the following tasks:
* Select the Endpoint,
* Click on the **Actions** button,
* Choose the option of **Delete VPC endpoints**
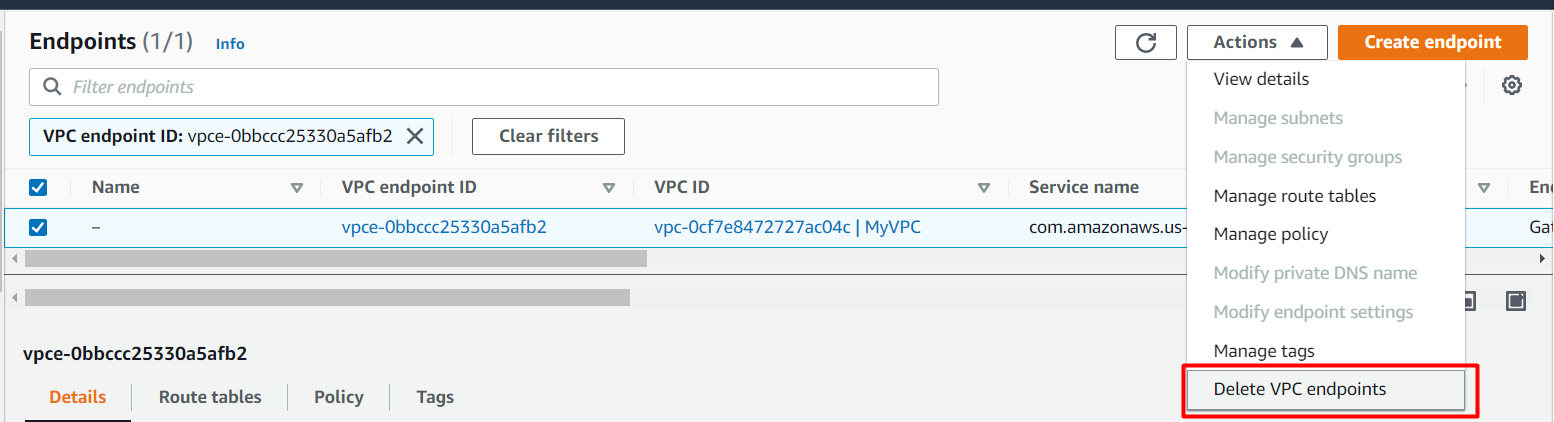 4. Confirm the deletion by typing **delete.**
5. The endpoint will be deleted immediately.
#### EC2 Instance termination
1. Navigate to **EC2** by clicking on the **Services** menu at the top, then click on **EC2** in the **Compute** section.
2. Click on **Instances** on the left panel.
3. EC2 Instances will be listed here.
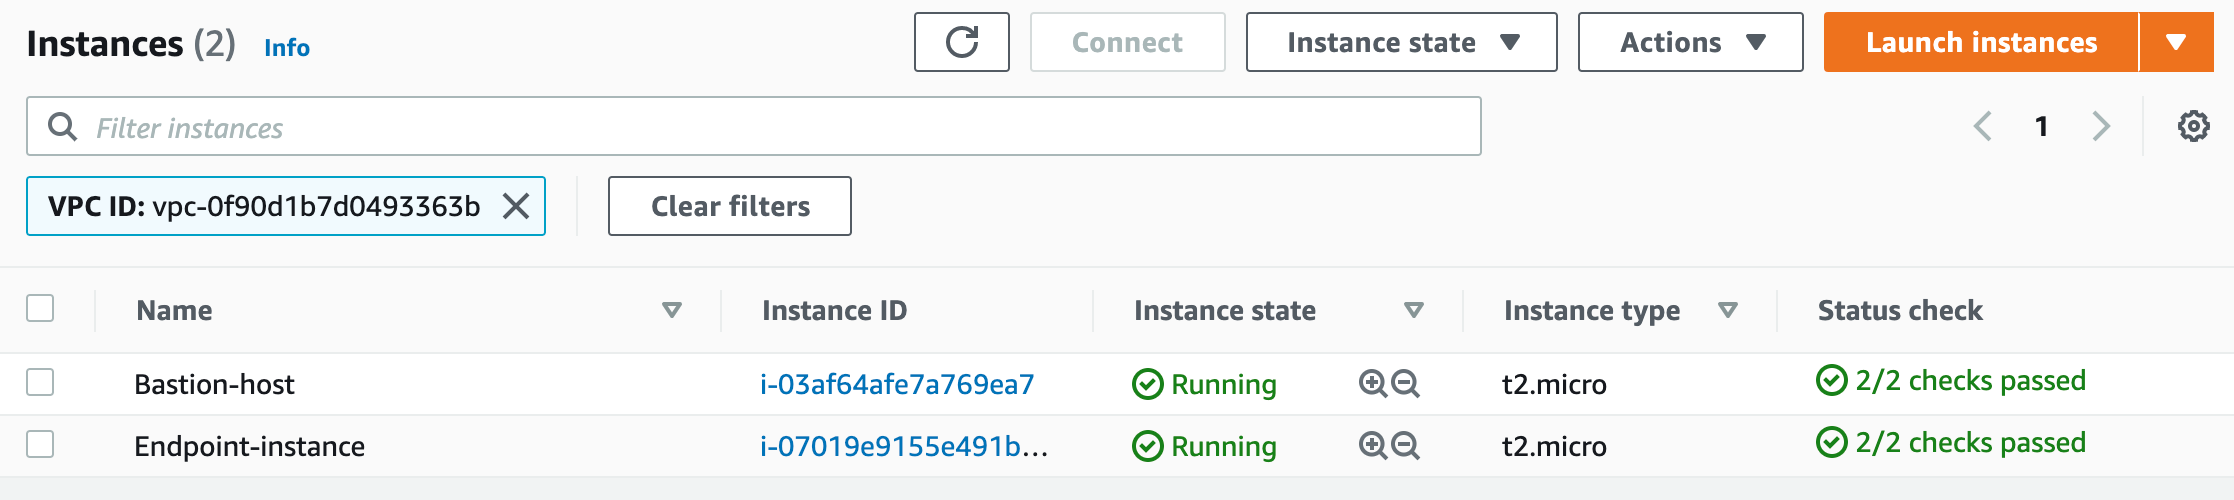 4. To terminate both the present instances, perform the following tasks:
* Select both the **EC2 instances**
* Click on the **Instance state**
* Choose to **Terminate instance**
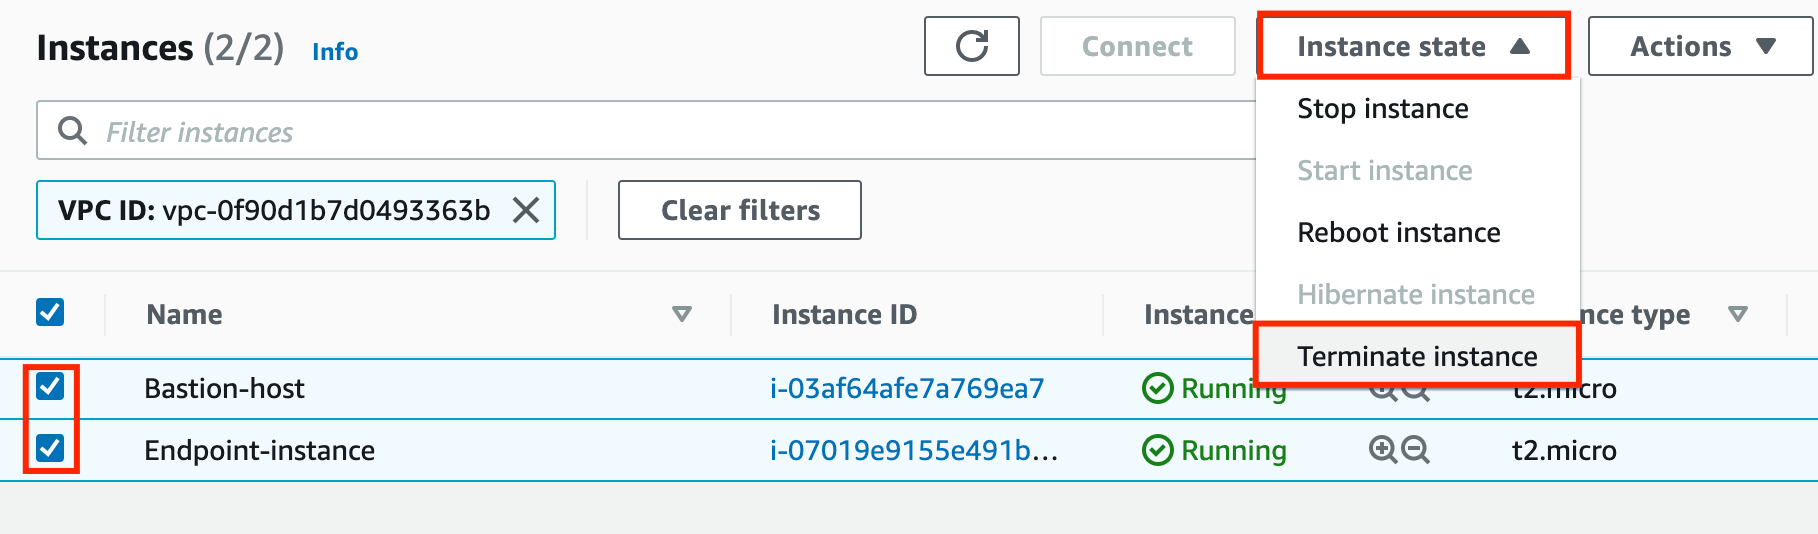 5. To confirm the termination of both the selected EC2 instance, click on the **Terminate** button.
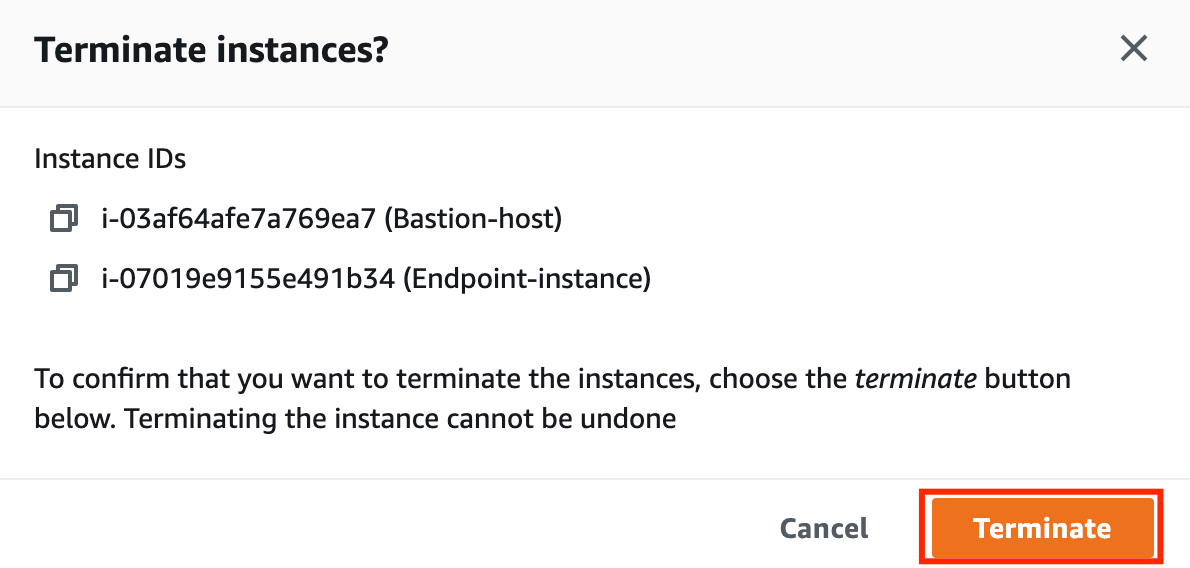 6. The instance will be terminated in a minute or so.
 ### Completion and Conclusion
1. We have launched two EC2 instances i.e. Bastion instance and Endpoint instance. We were able to SSH into the Endpoint instance via Bastion Instance successfully.
2. We have created a VPC endpoint for S3 to securely access S3 Buckets and their objects without going to the internet i.e. within Amazon's network through the Endpoint instance.
3. We tested the VPC endpoint for S3 from the private instance.
### End Lab
1. Sign out of the AWS Account.
2. You have successfully completed the lab.
3. Once you have completed the steps, click on **End Lab** from the IP Lab Portal dashboard.
## What gets checked
When you press **Check my work**, the platform verifies each of these:
* **Create Amazon Custom VPC** — Check whether a Custom VPC is created or not.
* **Create Amazon Custom VPC Private Route Table** — Check whether a Custom VPC Private Route Table is created or not.
* **Create Amazon Custom VPC Subnet** — Check whether a Subnet is created for the Custom VPC or not.
* **Create Internet Gateway** — Check whether an Internet Gateway is created and attached to the Custom VPC or not.
* **Create Amazon Custom VPC Public Route Table** — Check whether a Custom VPC Public Route Table is created and an Internet Gateway route is added or not.
* **Create VPC Endpoint** — Check whether a VPC Endpoint is created for the Custom VPC or not.
* **Launch an EC2 Instance** — Check whether an EC2 Instance is launched or not.
## Related help
* [FAQs and Troubleshooting](/aws-saa/support/faqs-and-troubleshooting)
This documentation is built and hosted on [Mintlify](https://mintlify.com), a developer documentation platform.