> ## Documentation Index
> Fetch the complete documentation index at: https://cloud-architect.ipoint-labs.com/llms.txt
> Use this file to discover all available pages before exploring further.
# Introduction to Creating AWS VPC Flow Logs
> Hands-on lab · 45m
Launch this lab in the IP Lab Portal, then follow the steps below in the AWS console.
Open IP Lab Portal
## Overview
### Lab Details
1. This lab walks you through the steps to creating VPC Flow Logs. VPC Flow Logs allow you to capture information about the IP traffic going to and from your VPC, including details such as source and destination IP addresses, ports, protocols, and packet counts.
2. You will practice using VPC flow logs with AWS VPCs.
3. Duration: **45 minutes**.
4. AWS Region: **US East (N. Virginia) us-east-1**
### Introduction
#### Amazon Virtual Private Cloud
* Amazon Virtual Private Cloud (Amazon VPC) lets you provision a logically isolated section of the AWS Cloud where you can launch AWS resources in a virtual network that you define. You have complete control over your virtual networking environment, including a selection of your own IP address range, creation of subnets, and configuration of route tables and network gateways.
* You can use both IPv4 and IPv6 in your VPC for secure and easy access to resources and applications.
* You can easily customize the network configuration of your Amazon VPC. For example, you can create a public-facing subnet for your web servers that have access to the internet.
* You can also place your backend systems, such as databases or application servers, in a private-facing subnet with no internet access. You can use multiple layers of security, including security groups and network access control lists, to help control access to Amazon EC2 instances in each subnet.
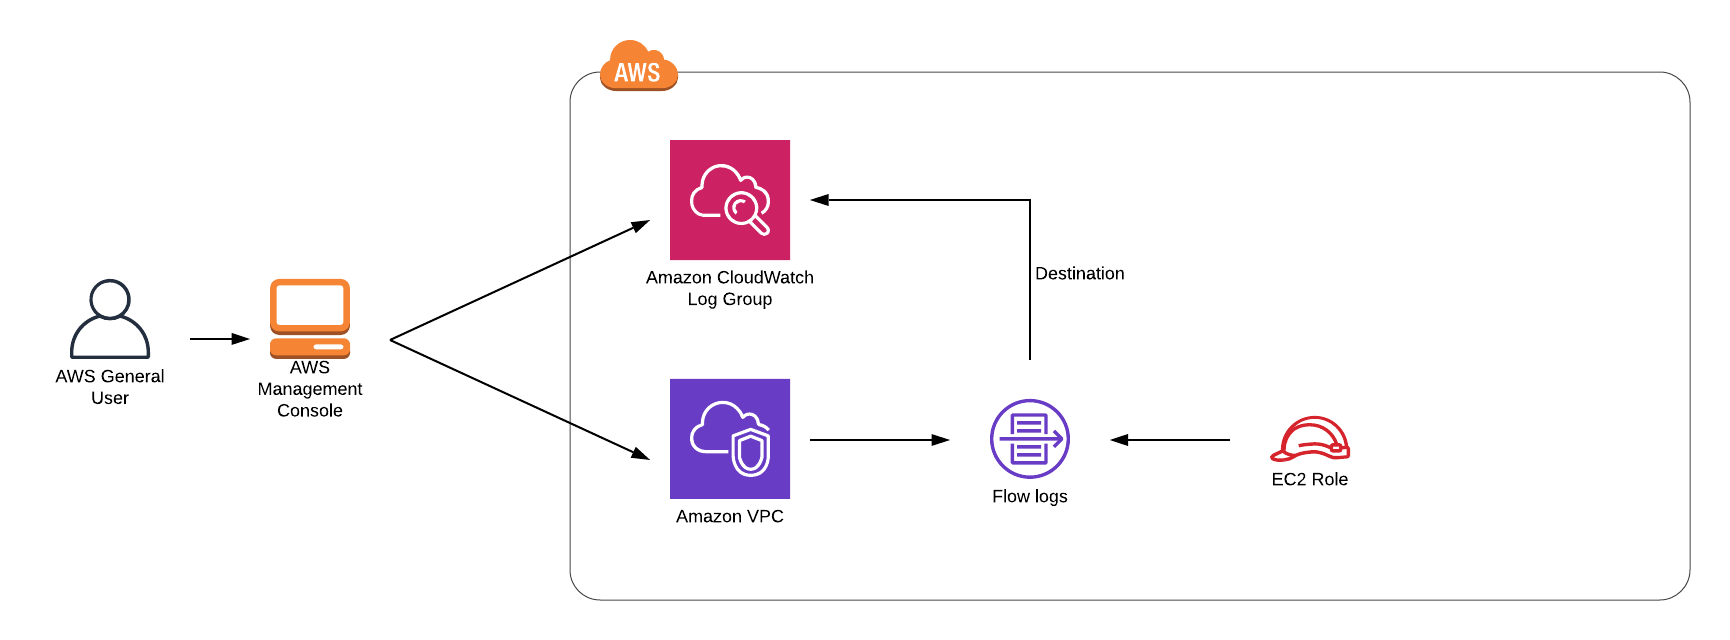
### Architecture Diagram
 ### Task Details
1. Sign in to the AWS Management Console.
2. Create CloudWatch Logs.
3. Create a VPC.
4. Create VPC Flow Logs
### Launching Lab Environment
1. To launch the lab environment, Click on the **Start Lab** button.
2. Please wait until the cloud environment is provisioned. It will take less than a minute to provision.
3. Once the Lab is started, you will be provided with **IAM user name**, **Password**, **Access** **Key**, and **Secret** **Access** **Key**.
> **Note** : You can only start one lab at any given time
## Lab guide
### Lab Steps
#### Task 1: Sign in to AWS Management Console
1. Click on the **Open Console** button, and you will get redirected to AWS Console in a new browser tab.
2. On the AWS sign-in page,
* Leave the Account ID as default. Never edit/remove the 12 digit Account ID present in the AWS Console. otherwise, you cannot proceed with the lab.
* Now copy your **User Name** and **Password** in the Lab Console to the **IAM Username and Password** in AWS Console and click on the **Sign in** button
3. Once Signed In to the AWS Management Console, Make the default AWS Region as **US East (N. Virginia) us-east-1.**
#### Task 2: Create a CloudWatch Log
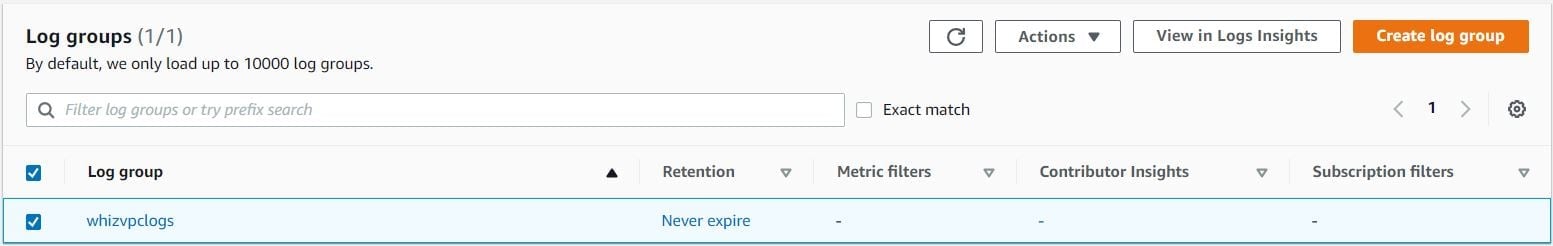
In this task, you will create a CloudWatch Log Group called "whizvpclogs" using the CloudWatch service. Follow the steps below:
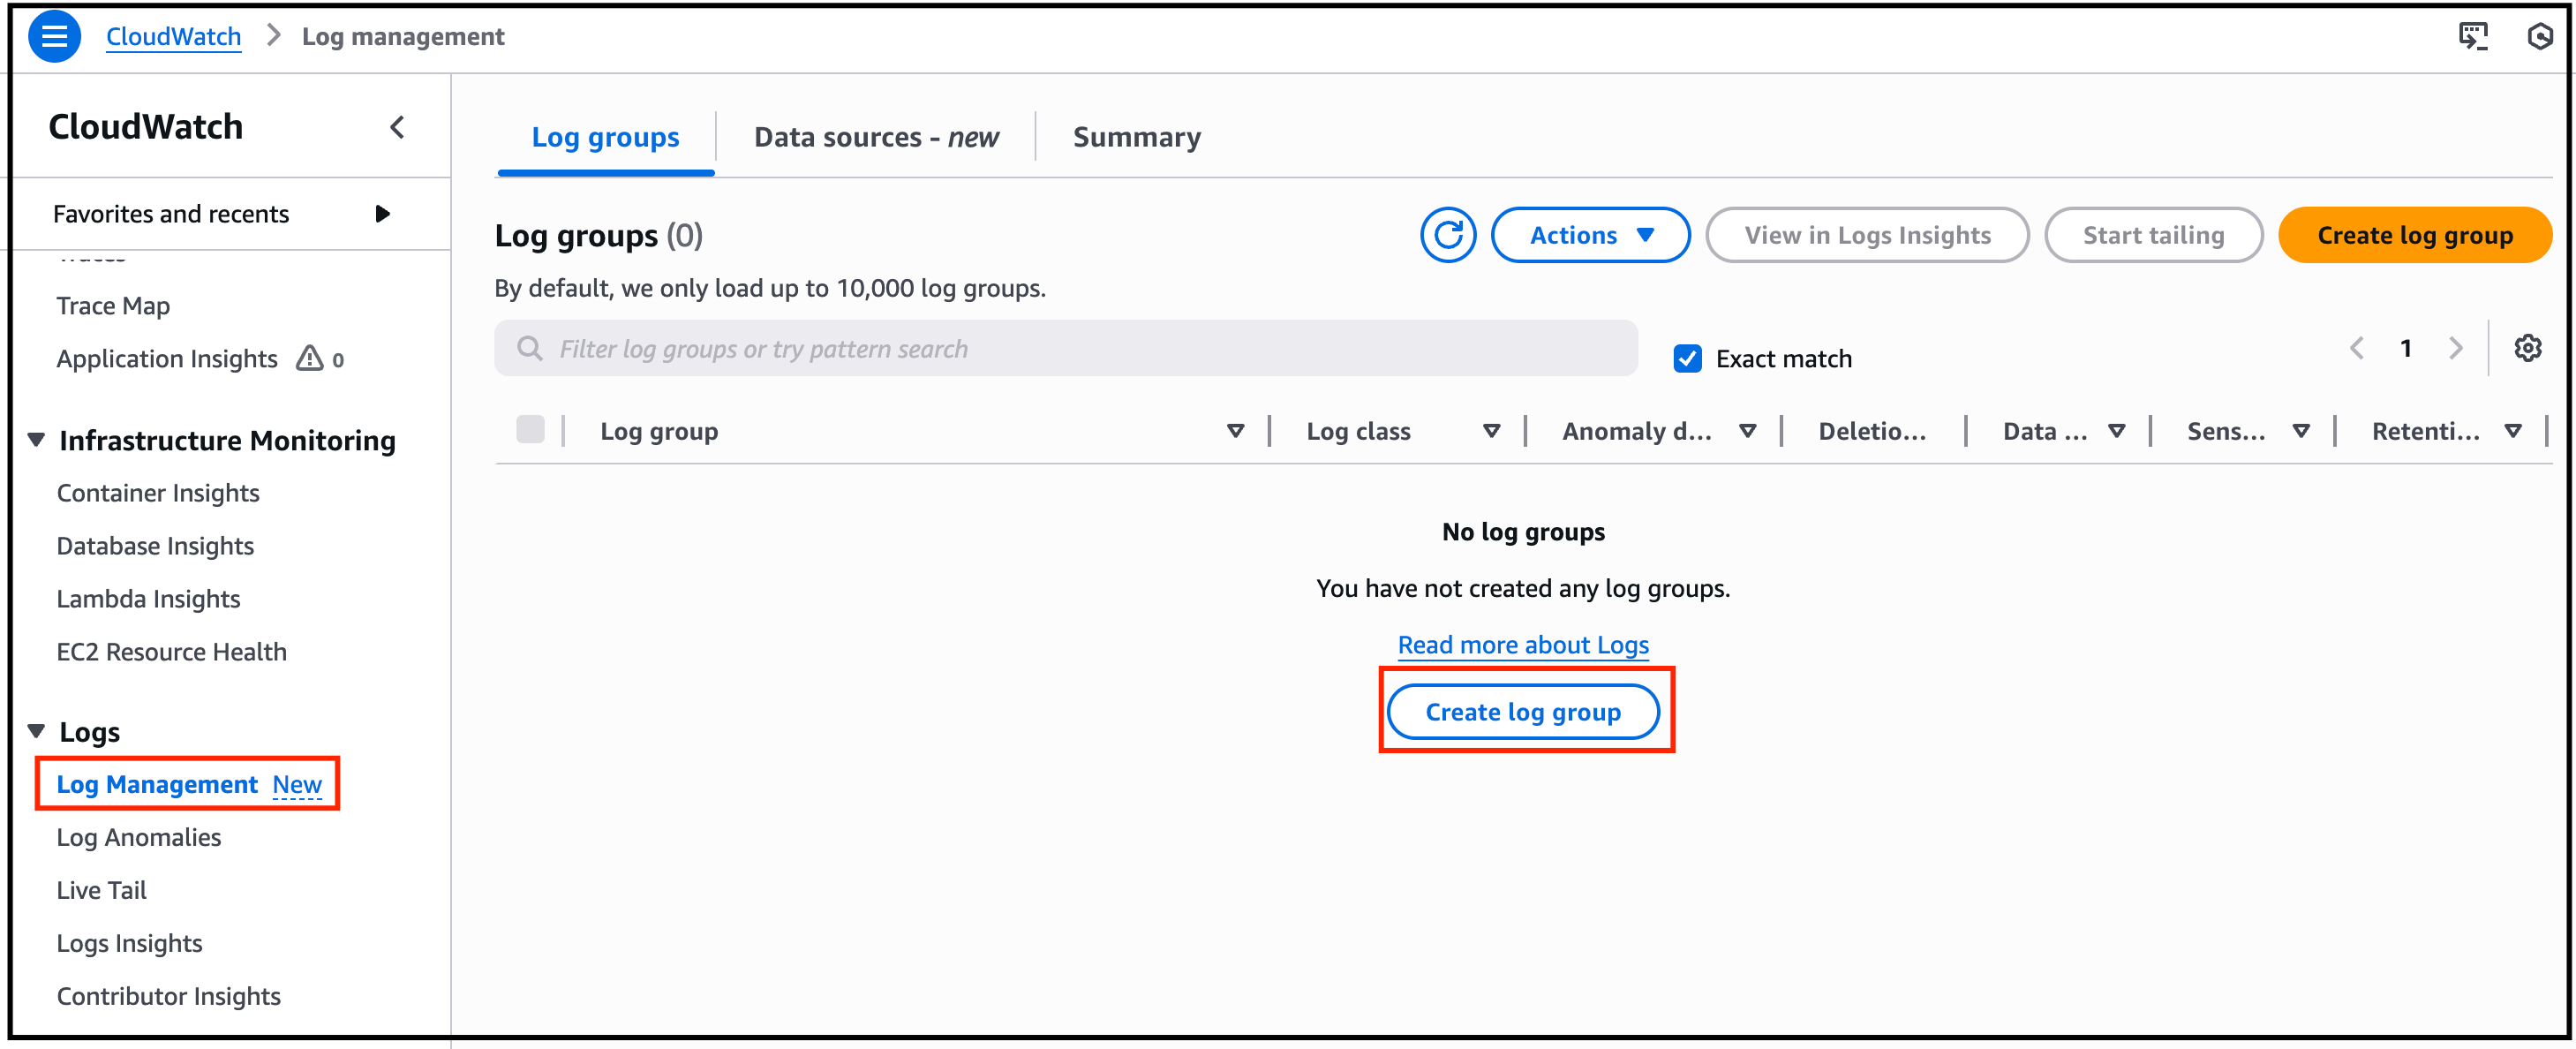
1. Navigate to the **Services** menu at the top and choose **CloudWatch** under **Management and Governance**.
2. Click on **Log Management** under **Logs** in the left-side panel, click on **Create Log Group.**
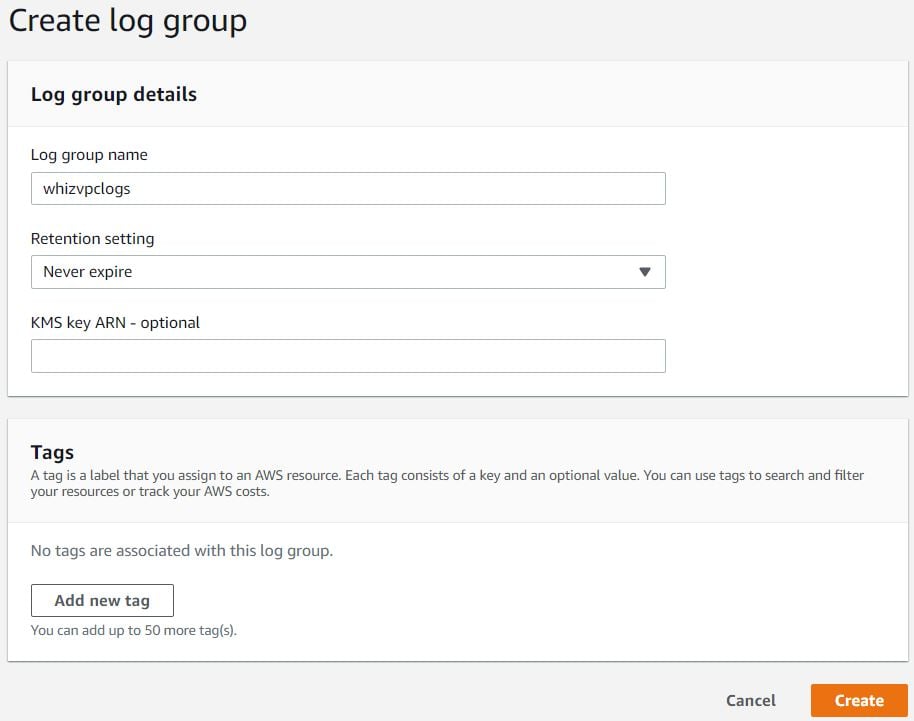
 3. Enter the Log Group Name : ***whizvpclogs*** and click on **Create** button.
**Note: You can ignore the error related to fetching CloudWatch metrices**
 #### Task 3: Create a VPC
1. Navigate to the **Services** menu on the top and choose **VPC** under **Networking and Content Delivery**.
2. Click on **Your VPC’s** in the left side panel then click on **Create VPC.**
3. Select **VPC only.**
4. Enter the Name tag: ***whizvpc*** and enter IPv4 CIDR block: ***10.1.0.0/16***. Leave other options as default and click on **Create** button.
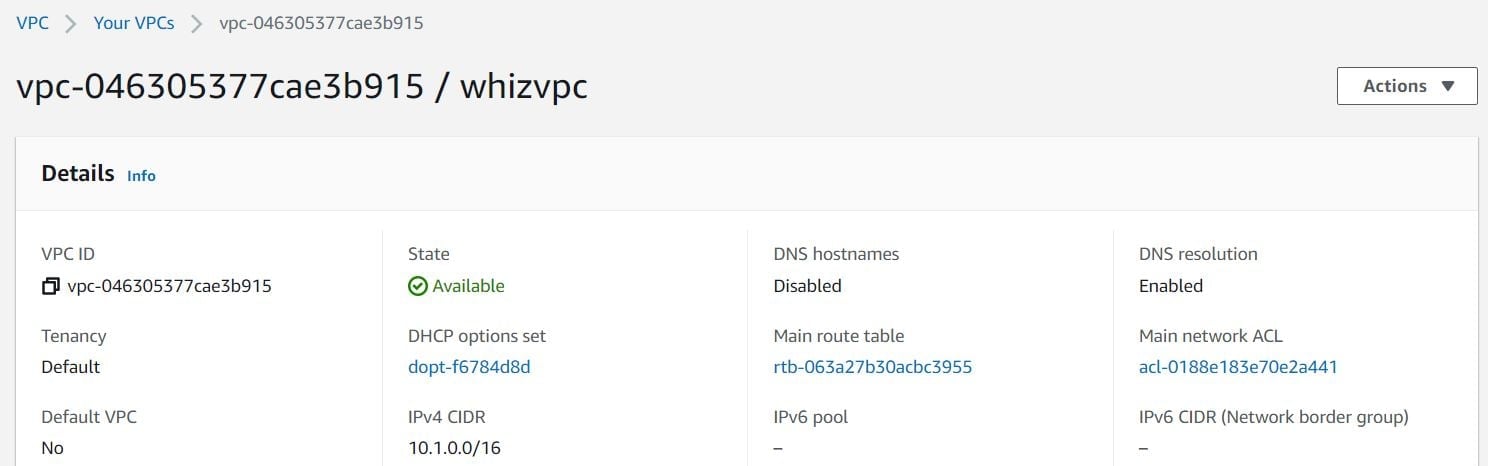 #### Task 4: Create VPC Flow Logs
In this task, you will create VPC Flow Logs for your VPC using the AWS Management Console. Follow the steps below:
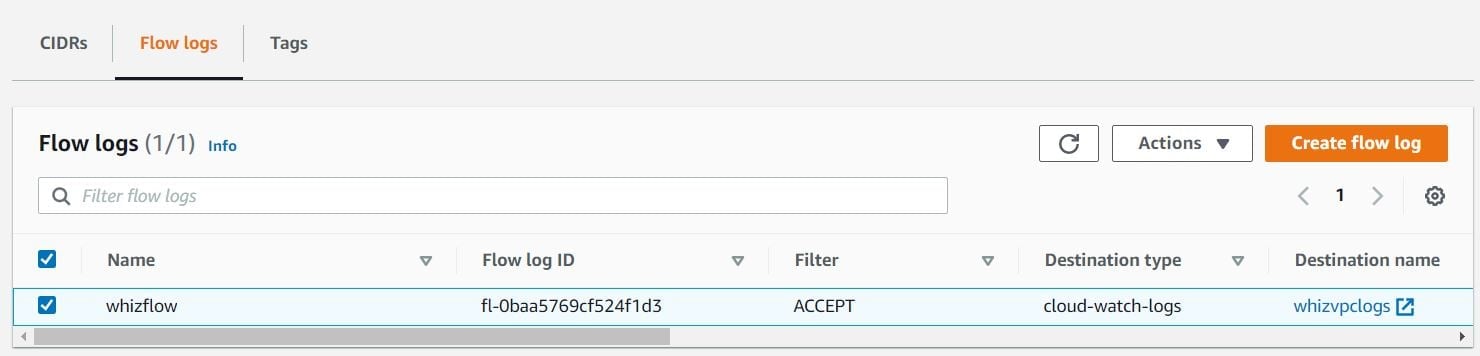
1. Inside **whizvpc,** scroll down and click on **Flow logs** tab and click on **Create Flow Log** button\*\*.\*\*
2. Under Flow log settings: Name: ***whizflow***
3. Select “Filter” as **Accept** and select “Destination” as **Send to CloudWatch Logs.** Choose the above created CloudWatch Logs “**whizvpclogs**”.
4. Under **Service access,** choose **Use an existing service role** and select the IAM role “**EC2VPCNetworkingProvisionerUSE1Role-xxxx**” under **Service role** and leave the others as default. Click on **Create flow log.**
* Once the flow logs are created, scroll down click on **Flow Logs.**
 5. Now you have successfully learned how to create VPC Flow Logs.
> ##### Do You Know?
>
> **AWS VPC Flow Logs can be used not only for network monitoring and security analysis but also for troubleshooting and performance analysis of your Amazon Virtual Private Cloud (VPC) environment.**
6. Once the lab steps are completed, please click on the Validate button on the left side panel.
### Completion and Conclusion
1. You have successfully created the CloudWatch Logs.
2. You have successfully created the VPC.
3. You have successfully created the VPC Flow Logs.
### End Lab
1. Sign out of AWS Account.
2. You have successfully completed the lab.
3. Once you have completed the steps click on **End Lab** from the IP Lab Portal dashboard.
## What gets checked
When you press **Check my work**, the platform verifies each of these:
* **Check Log Group** — Check whether a CloudWatch log group exists.
* **Create Amazon Custom VPC** — Check whether a Custom VPC is created or not.
* **Create VPC Flow Logs** — Check whether VPC Flow Logs are created for the Custom VPC or not.
This documentation is built and hosted on [Mintlify](https://mintlify.com), a developer documentation platform.