

Overview
Prerequisites
-
Good knowledge of AWS Service
- Amazon Macie
- S3 Bucket
- Laptop/Desktop
- Internet Browser
- Internet connection
Challenge Instructions
- Region: Make sure to use us-east-1 region to create all the resources.
- You will be provided with the requirements of the challenge. If you are new to AWS Cloud, we recommend you go through our hands-on labs before taking this challenge.
- Challenge Duration: 60 minutes
How to submit the challenge
- After building the infrastructure, click on the Validation button, to validate if you have built the required infrastructure and completed the challenge successfully.
-
Validation status:
- Success - you have completed the challenge successfully.
- Failed - you have failed to complete the challenge.
- Once you have successfully validated the challenge, click on End Lab button to end the challenge.
Launching Challenge Environment
- To launch the challenge environment, click on the Start Challenge button.
- Please wait until the cloud environment is provisioned. It will take less than a minute to provision.
- Once the challenge is started, you will be provided with IAM Username, Password, Access Key, and Secret Access Key.
Lab guide
Sign in to AWS Management Console
- Click on the Open Console button, and you will get redirected to AWS console in a new browser tab.
- On the AWS sign-in page, leave the account id as default. Never edit/remove the 12-digit account id present in the AWS console. Otherwise, you cannot proceed with the challenge.
- Now copy your Username and Password in the lab console to the IAM username and password in AWS console and click on the sign in button.
- Once signed in to the AWS management console, make the default AWS region as US East (N. Virginia) us-east-1.
Cloud Challenge Details
In this challenge lab, your AWS management and governance skills are put to the test as you embark on creating and configuring an Amazon Macie job to uncover sensitive data.Architecture Diagram
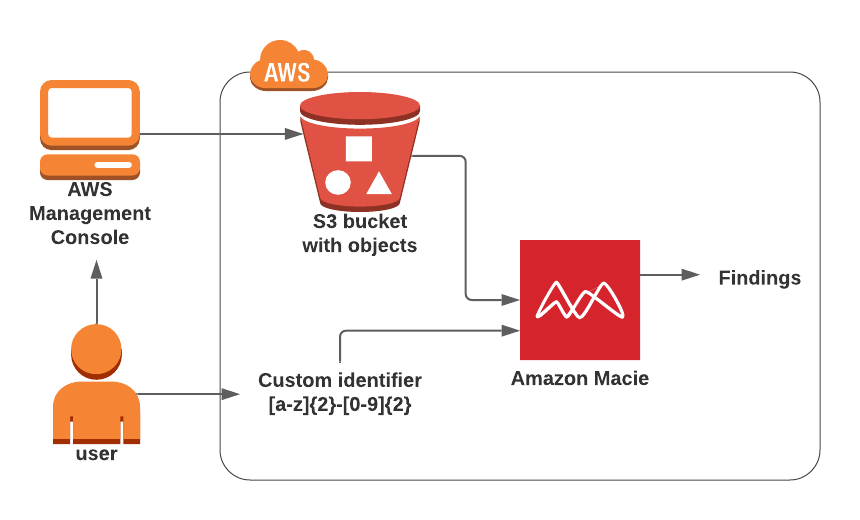
- Enable AWS Macie for the account.
-
Create a Macie job according to the provided instructions:
- Start by selecting the S3 bucket whose name starts with “whizlabs”.
-
Refine the scope for sensitive data discovery:
- Sensitive data discovery: One-time job
- Object criteria: File name extensions.
- Include: File name extensions: csv
- Select managed data identifiers: Recommended
-
For Custom data identifiers, create a Managed custom identifier:
- Name: Whiz
- Regular expression: [a-z]{2}-[0-9]{2}
- Select allow lists.
-
For general settings, provide:
- Job name: WhizJob
- Wait for Macie job completion, then view findings, and export them as a JSON report.
End Challenge
- Sign Out of the AWS account.
- You have successfully completed the challenge.
- Click on End Challenge button from IP Lab Portal Labs console and wait till the process gets completed.
What gets checked
When you press Check my work, the platform verifies each of these:- Check Macie job findings — Check whether Macie job findings are present or not
- Create a Macie Classification job — Check whether a Macie classification job is created or not