

Overview
Lab Details
- This lab focuses on the essential steps to set up auto-scaling of EC2 instances using the SQS
- Duration : 1 Hour
- AWS Region: US East (N. Virginia) us-east-1.
Introduction:
What is Amazon EC2 Auto Scaling
- Amazon EC2 autoscaling is designed as a fully managed service that controls the number of running instances, in case your workload is higher, it will match by launching more instances instantaneously.
- Unlike load balancer, you don’t provision EC2 Instances in advance and register as a target but you define the whole configuration in the Launch template which will scale out or scale in based on the traffic.
- In auto-scaling, you also define what will be minimum capacity, desired capacity, and maximum capacity. Autoscaling makes sure that the number of instances specified in desired capacity is always running when traffic is normal, it will scale in when traffic is lowest and scale-out when running there is a spike.
- While creating auto-scaling, it requires a Launch template where you specify which AMI to choose, what will be instance type, security group associated, and all other options required to launch an EC2 Instance including key pair.
SQS (Simple Queue Service)
- Amazon SQS is a reliable, easy to manage, scalable queuing service. SQS is a simple and cost-effective cloud application.
- AWS SQS can be used to transmit any amount of data, at any level of throughput, without losing messages. It doesn’t interrupt other services when run continuously.
- SQS helps to reduce administrative tasks by scaling high-available messaging clusters. While we pay only for what we use. AWS SQS helps us to save important data which could be lost if an entire application goes down or if any component becomes unavailable.
- SQS queue acts as a buffer between the application components that receive the data and the other parts that process the data in the system.
- SQS is used for message-oriented architecture. If the processing server cannot process the work fast enough (for whatever reason) the work is queued so that the processing servers can work on it when they have available resources to process the request. This means that work is not lost due to insufficient resources.
- The default Amazon SQS ensures that each message is delivered at least once.
Architecture Diagram
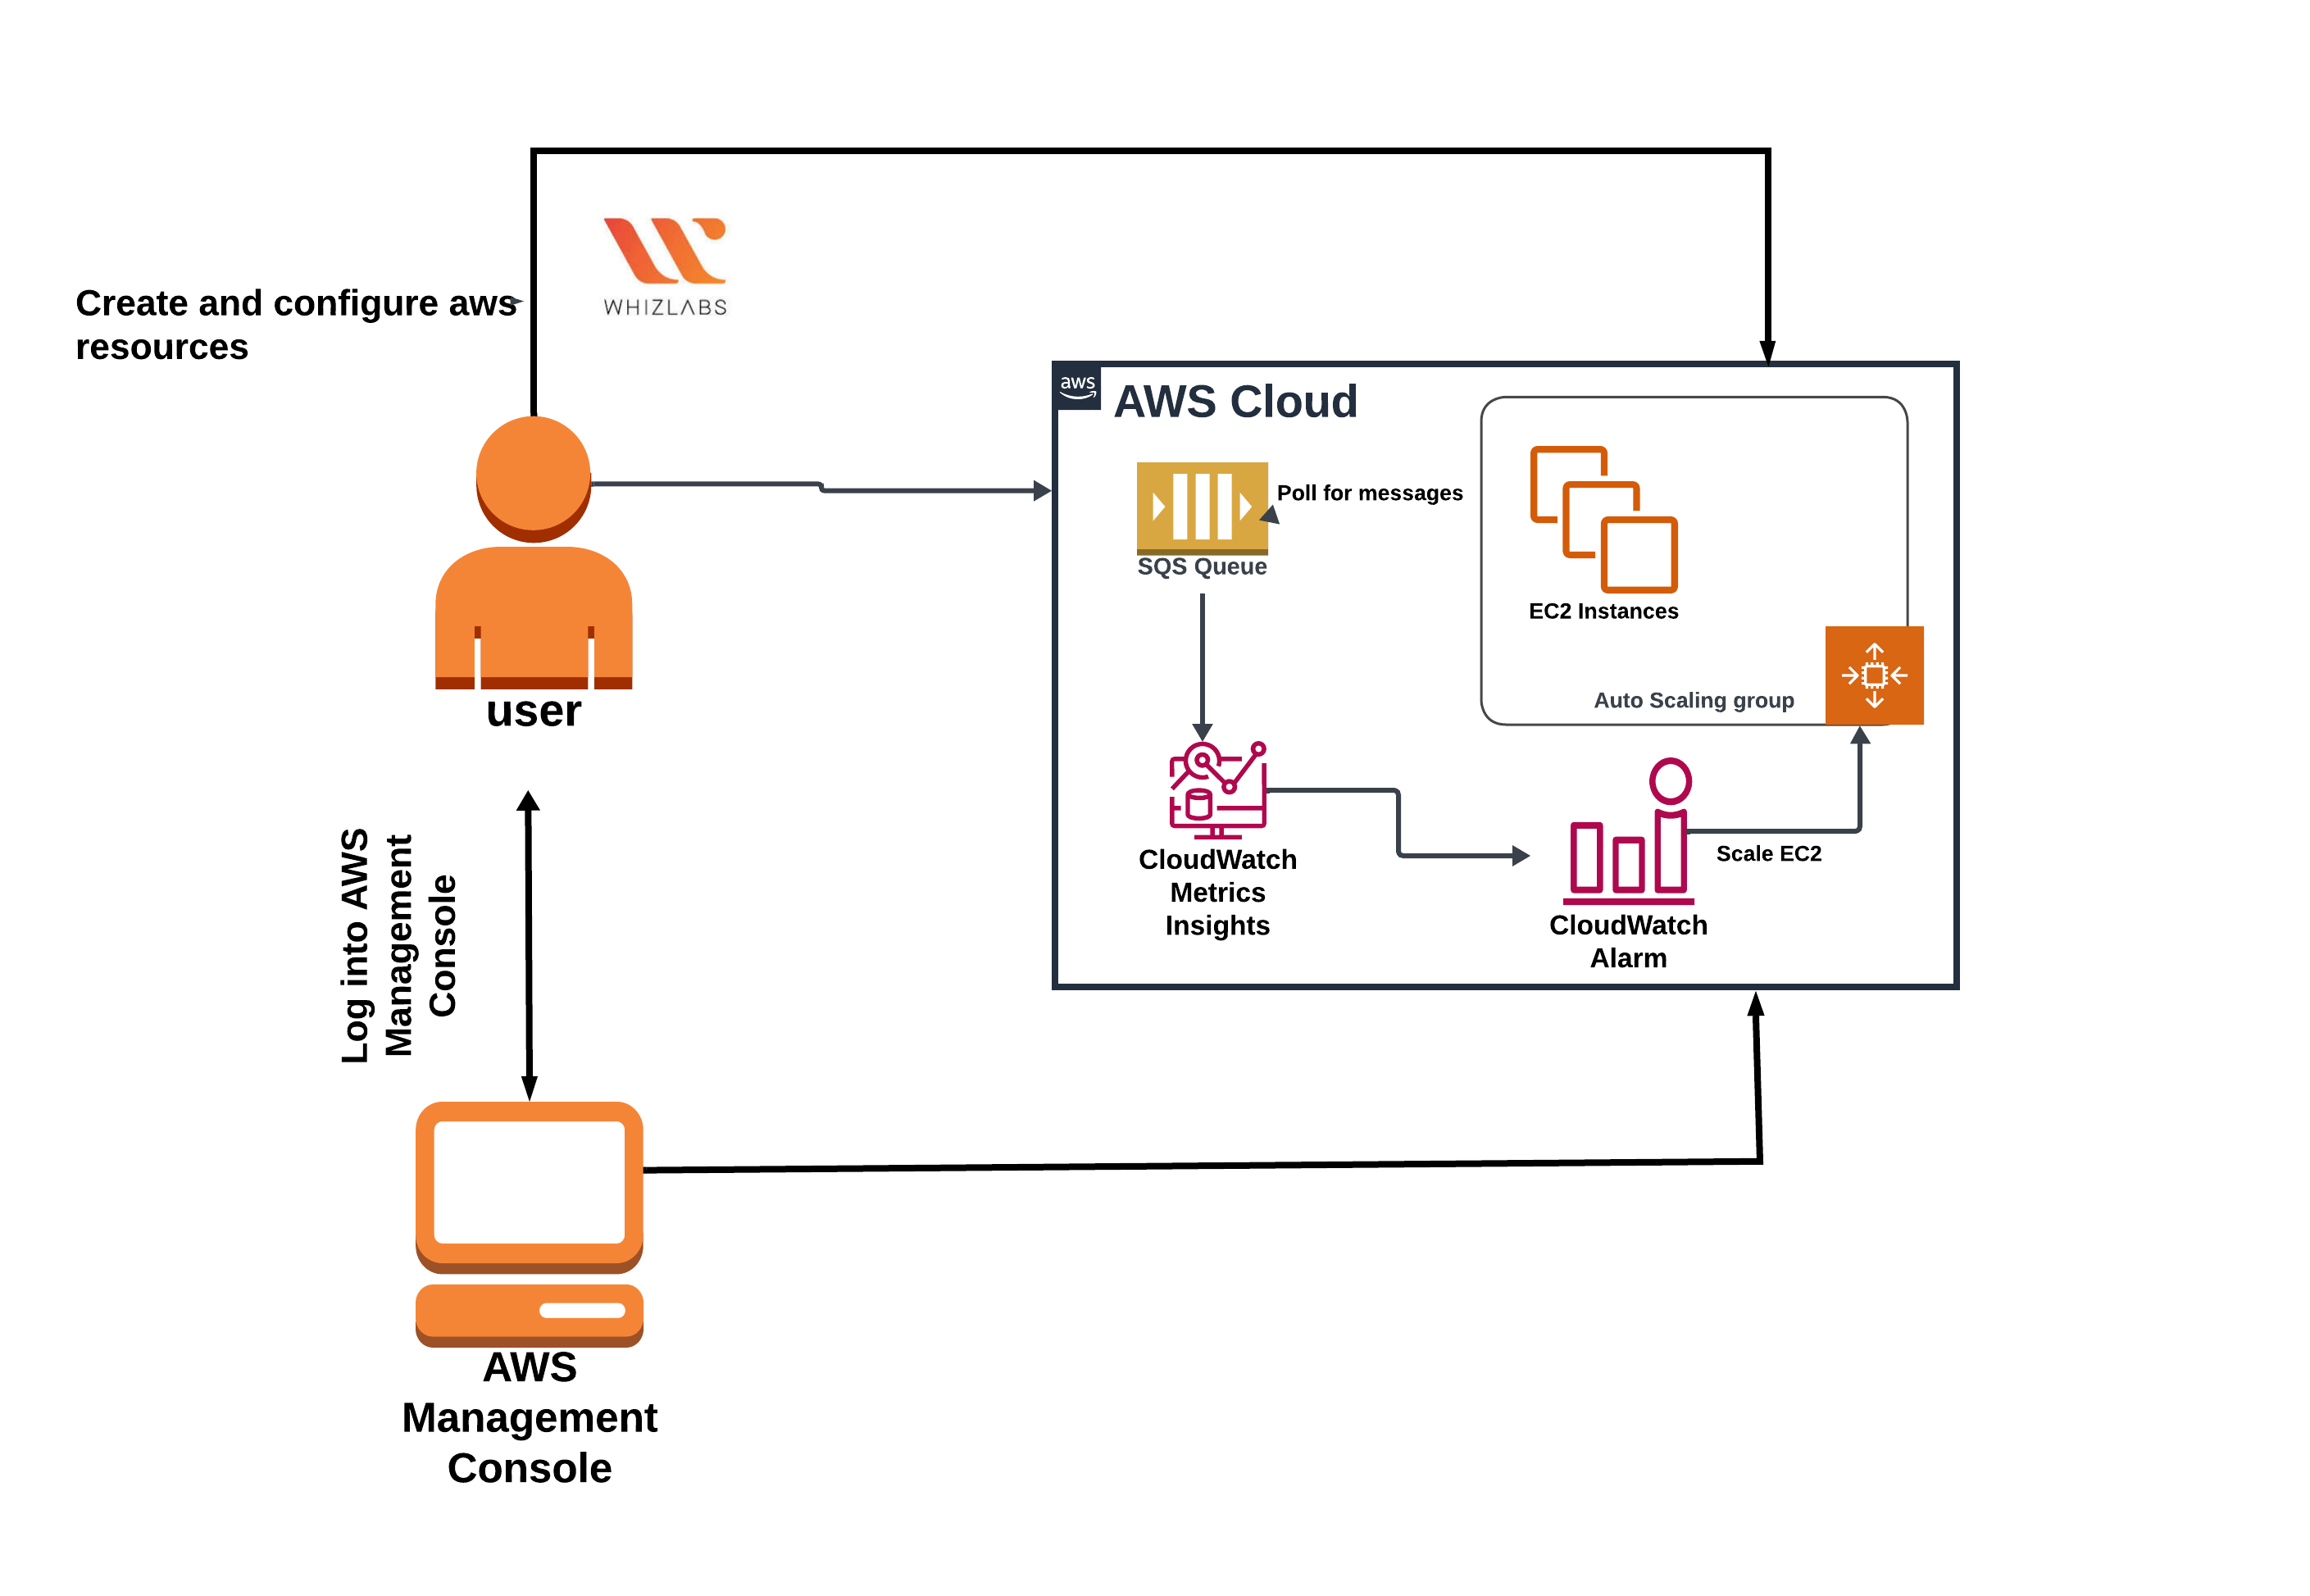
Task Details
- Sign into the AWS Management Console.
- Create an S3 Bucket.
- Create an SQS Queue
- SSH into EC2 instance
- Create CloudWatch Alarms
- Create a Launch Template
- Create an Auto Scaling Group
- Verifications and Monitoring
Launching Lab Environment
- To launch the lab environment, Click on the Start Lab button.
- Please wait until the cloud environment is provisioned. It will take less than a minute to provision.
- Once the Lab is started, you will be provided with IAM user name, Password, Access Key, and Secret Access Key.
Lab guide
Lab Steps
Task 1: Sign in to AWS Management Console
- Click on the Open Console button, and you will get redirected to AWS Console in a new browser tab.
- On the AWS sign-in page,
- Leave the Account ID as default. Never edit/remove the 12-digit Account ID present in the AWS Console. Otherwise, you cannot proceed with the lab.
- Now copy your User Name and Password in the Lab Console to the IAM Username and Password in the AWS Console and click on the Sign-in button.
- Once Signed In to the AWS Management Console, make the default AWS Region as US East (N. Virginia) us-east-1.
Task 2: Create an S3 bucket
- Navigate to S3 in the Services menu under the Storage section.
- In the left menu, choose Buckets, click Create Bucket, and fill in the bucket details.
- AWS Region: Select US East (N. Virginia) us-east-1.
- Bucket Name: Enter whizlabs<RANDOM_NUMBER>
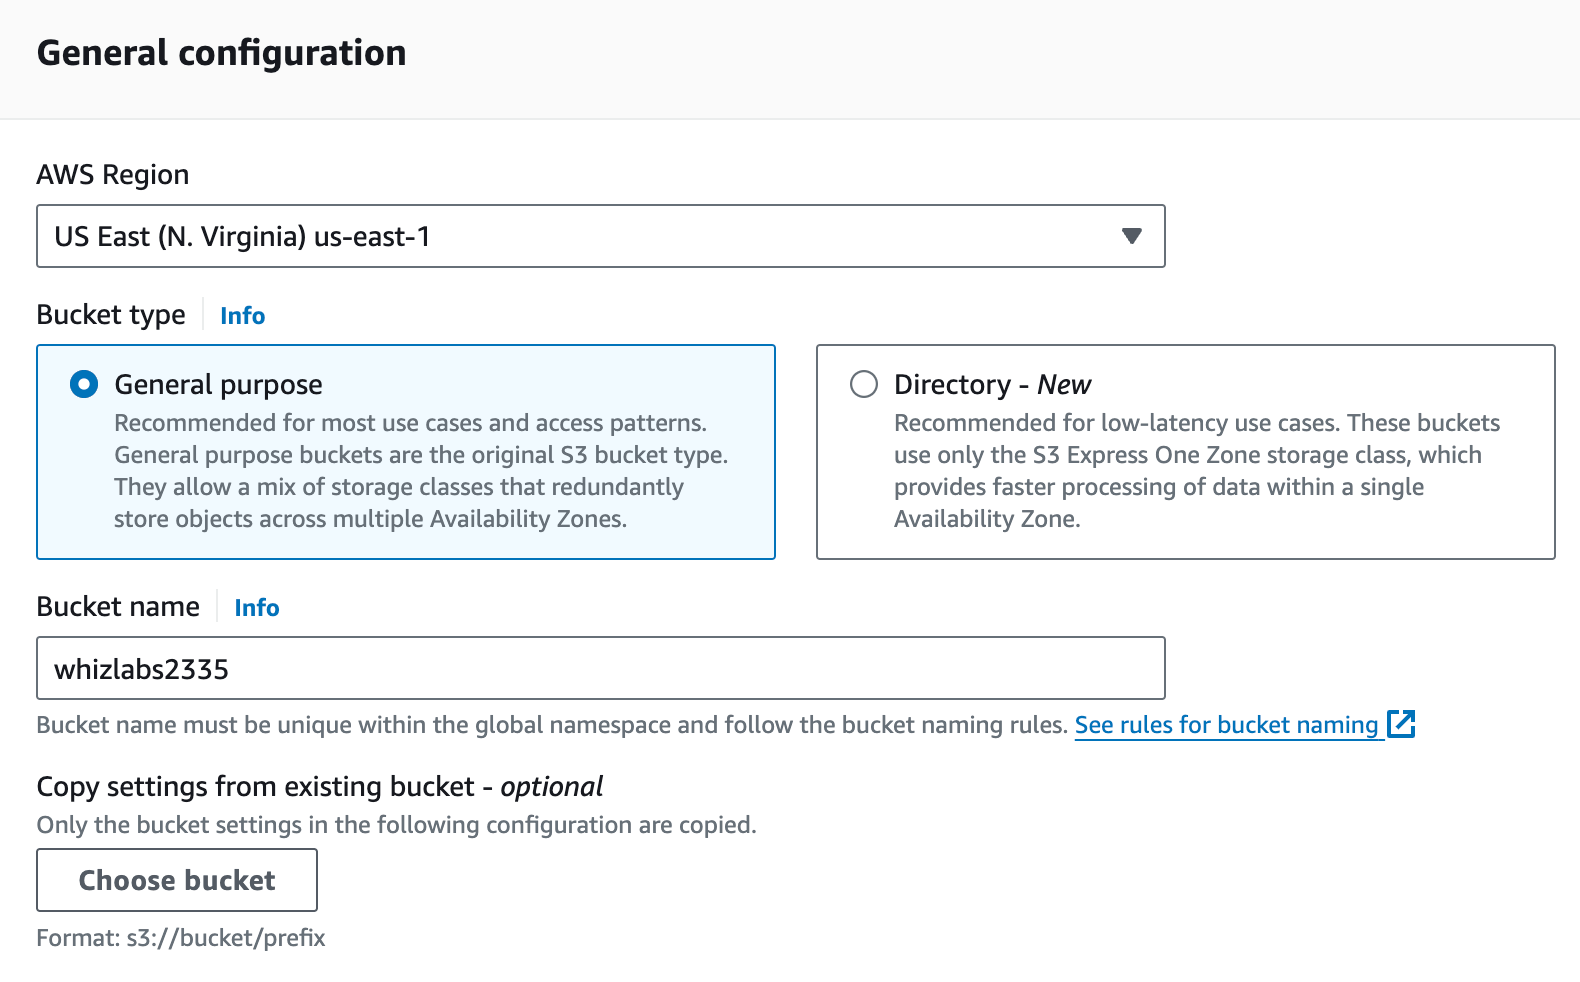
- Leave other settings as default.
- Click on Create bucket button.
- Your S3 Bucket is now created. Once it is created Click on your bucket name.
- In the Objects, You can see the following message
- You don’t have any objects in this bucket.
- Click on the Add files.
- Download the Zip file from here.
- Unzip the file and upload sendmessages and receivemessages files into the bucket
- Click on Upload button. Once your file has been uploaded, it will be displayed in the bucket.
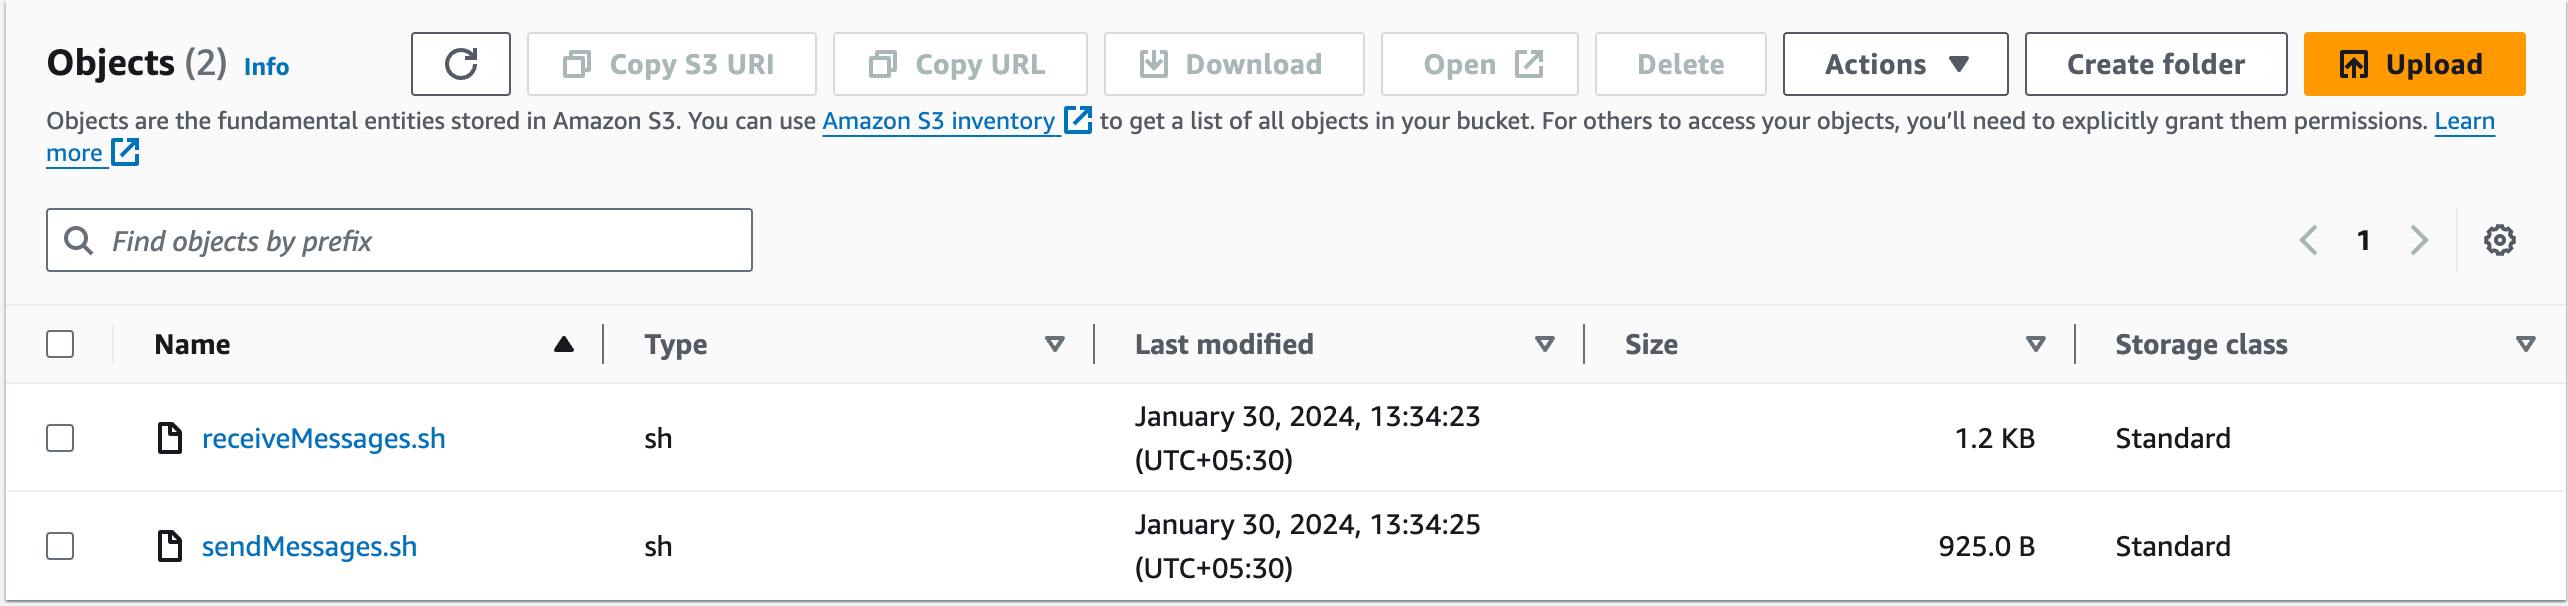
Task 3: Create an SQS Queue
In this task, we are going to create an sqs queue that will send and receive messages- Make sure you are in the N. Virginia region.
- Navigate to the Services menu on the top, search for SQS and select it.
- Now, We’ll create a Queue, with all the default options. Click on Create queue button.
- Details :
- Type : Select Standard
- Name : Enter MyMessages {IMPORTANT : use same name}
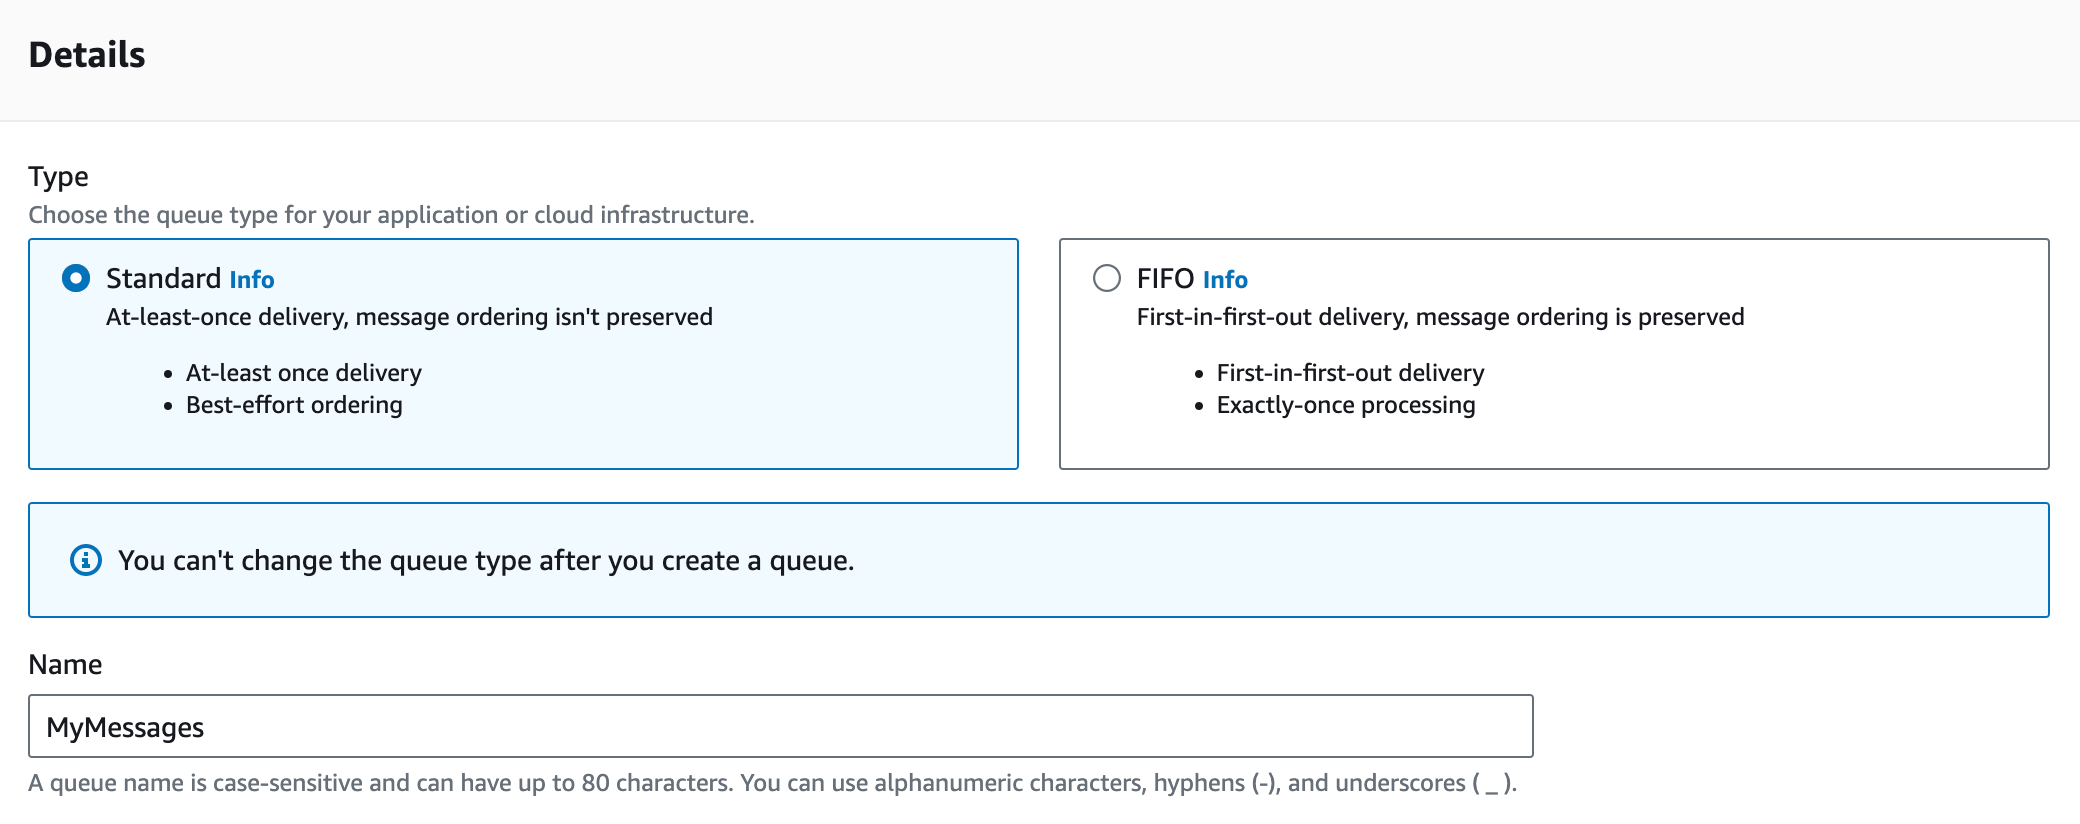
- Once you click on Create Queue you will get a success message.
Task 4: SSH into EC2 instance
- Make sure you are in the US East (N. Virginia) us-east-1 Region before proceeding with the Lab.?
- Navigate to EC2 by clicking on the Services menu in the top, then click on EC2 in the Compute section.
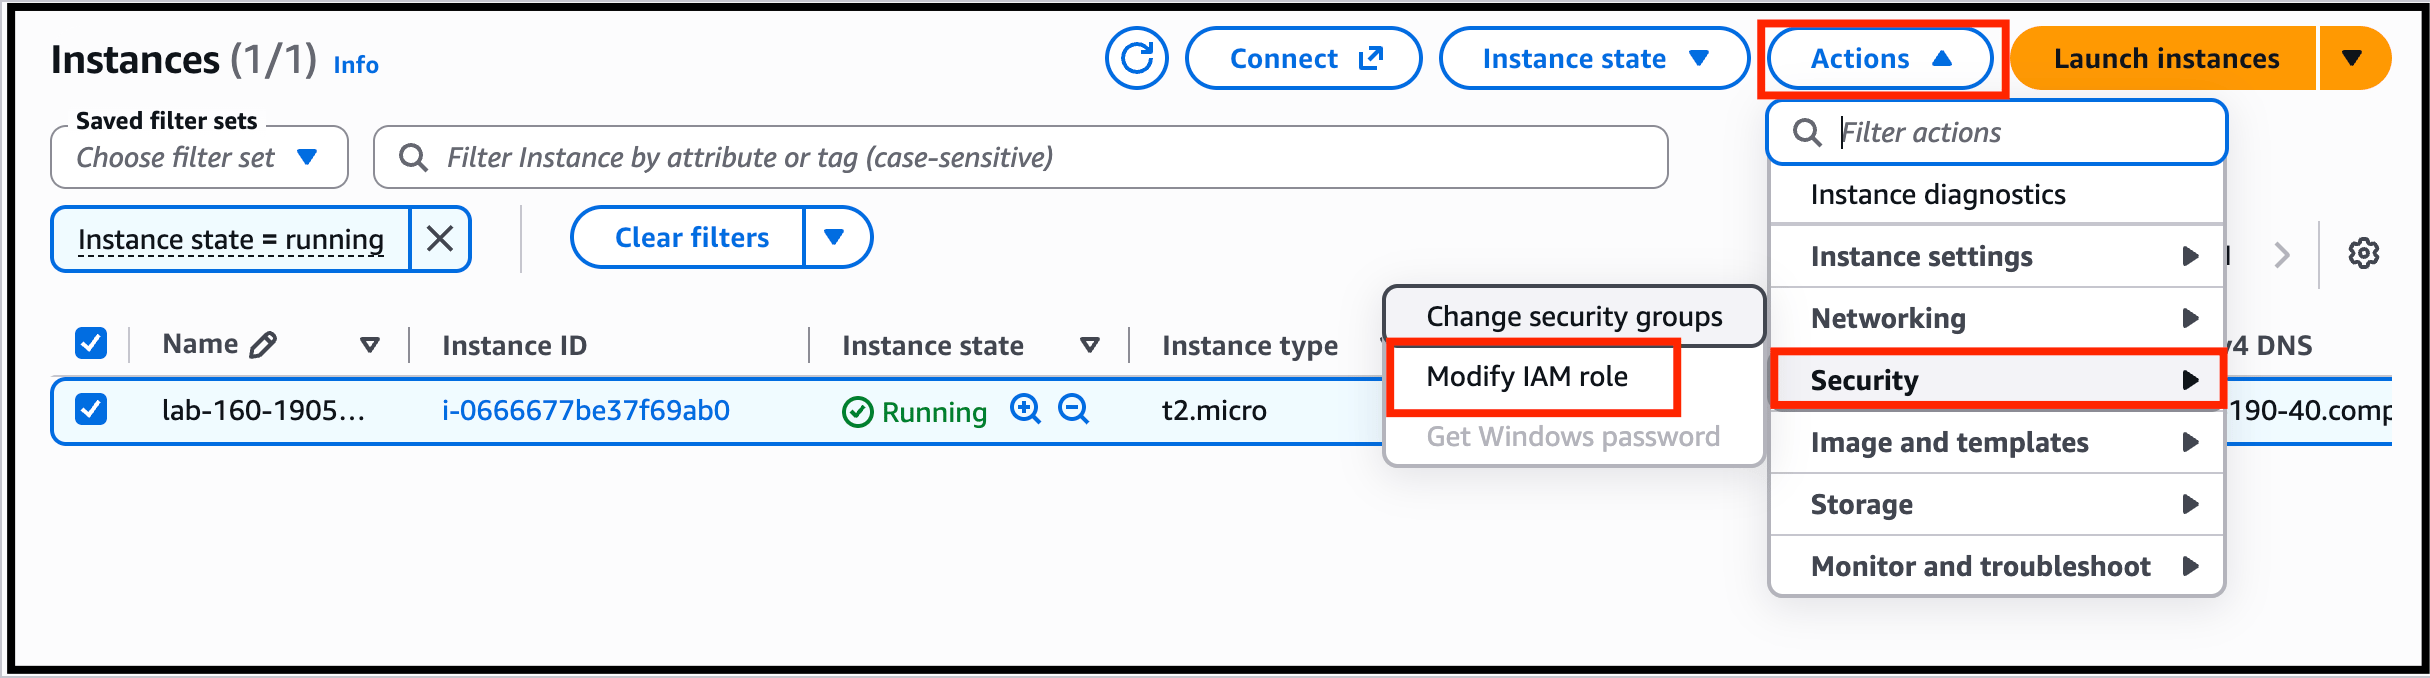
- You will see a running instance named lab-xxx-xxxxx. Select the Instance and click on Actions Button.
-
From the dropdown select Security and Choose Modify IAM Role option.
-
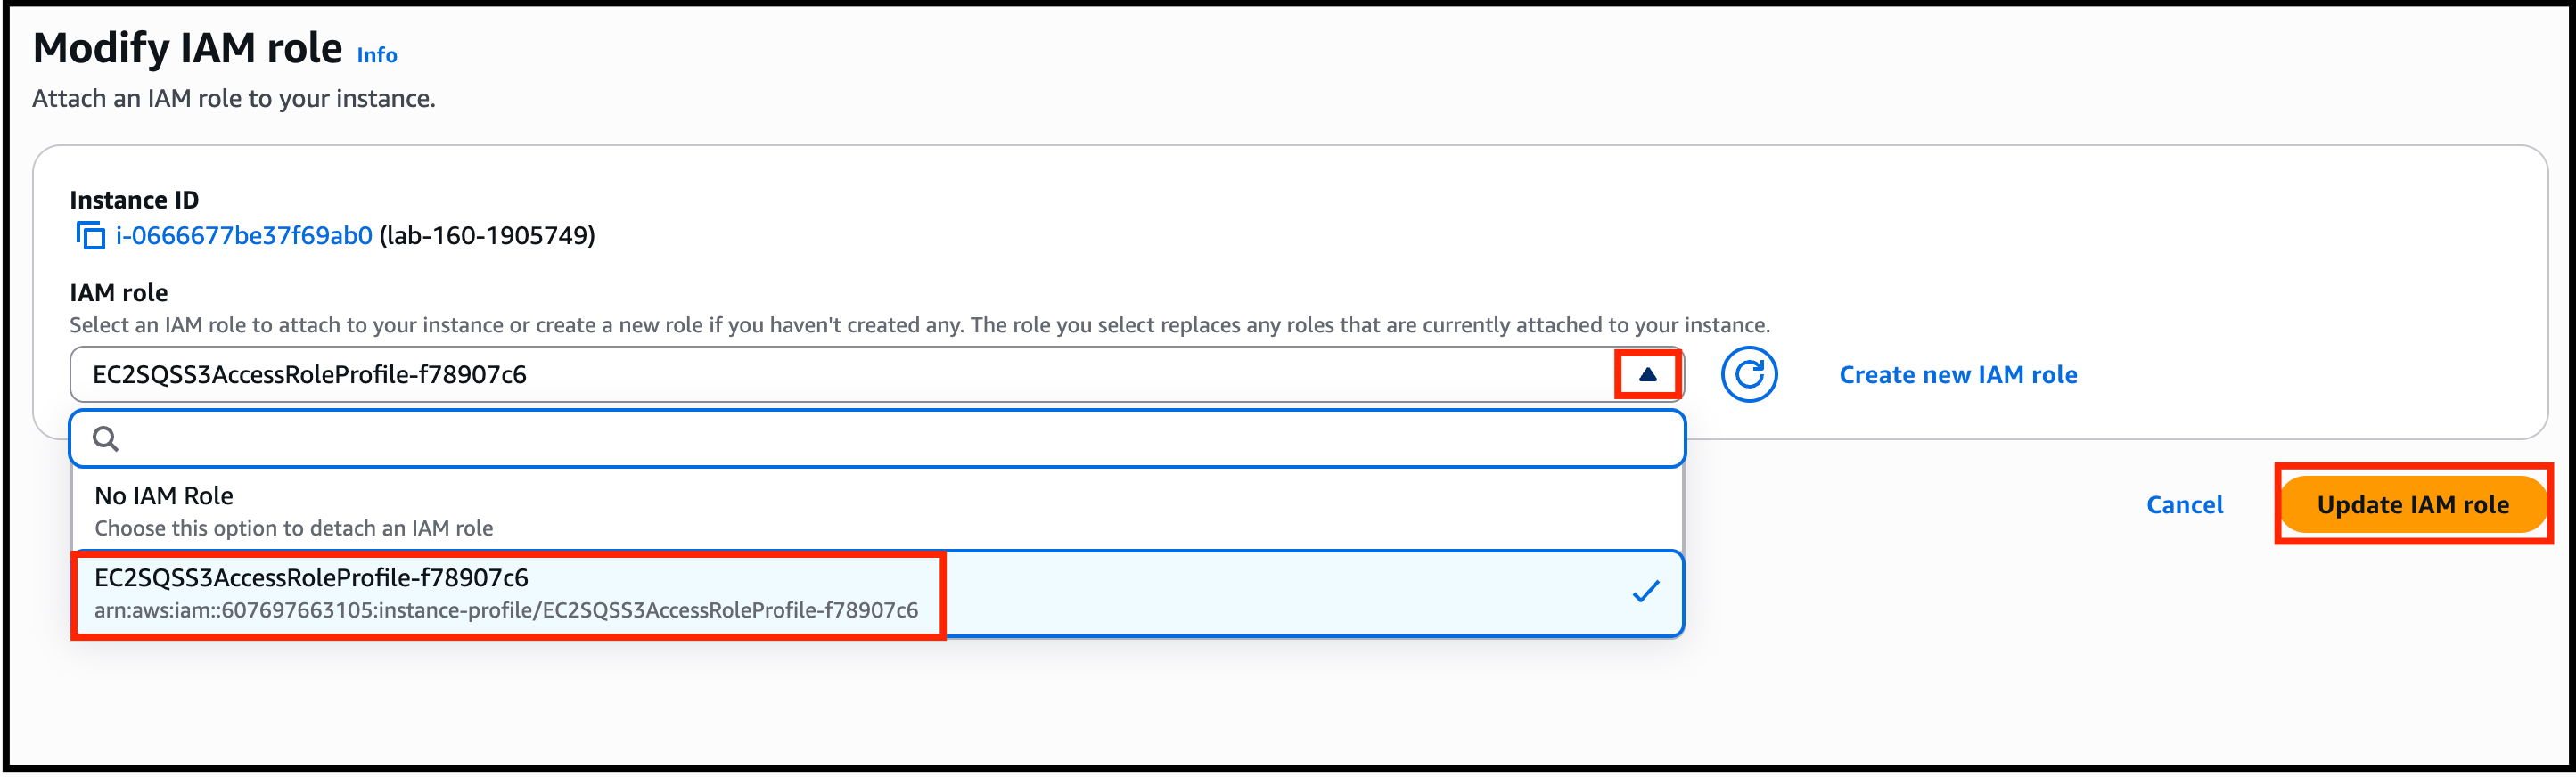
Under IAM role, choose EC2SQSS3AccessRoleProfile-xxxxxxxx. Then click on Update IAM role option.
-
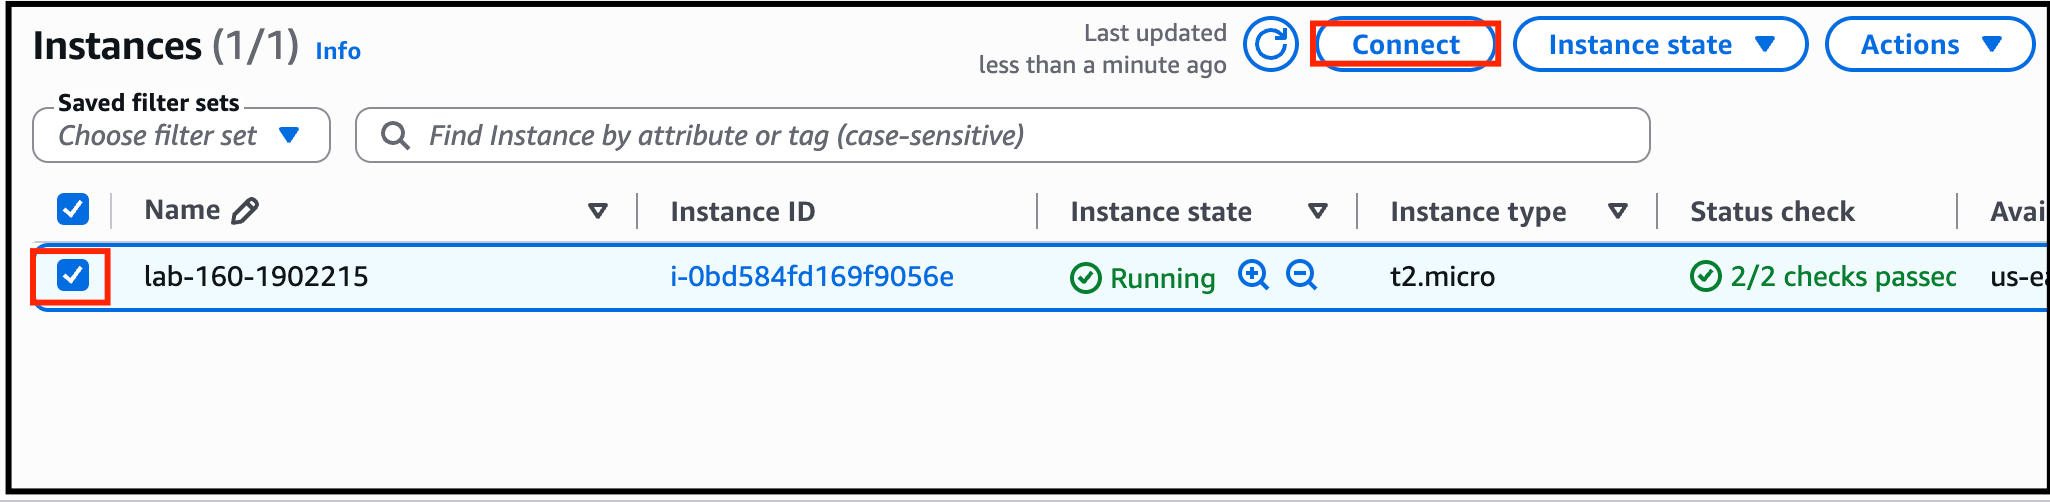
Click on the instance and then click on the Connect button.
-
Click on the Connect button again.
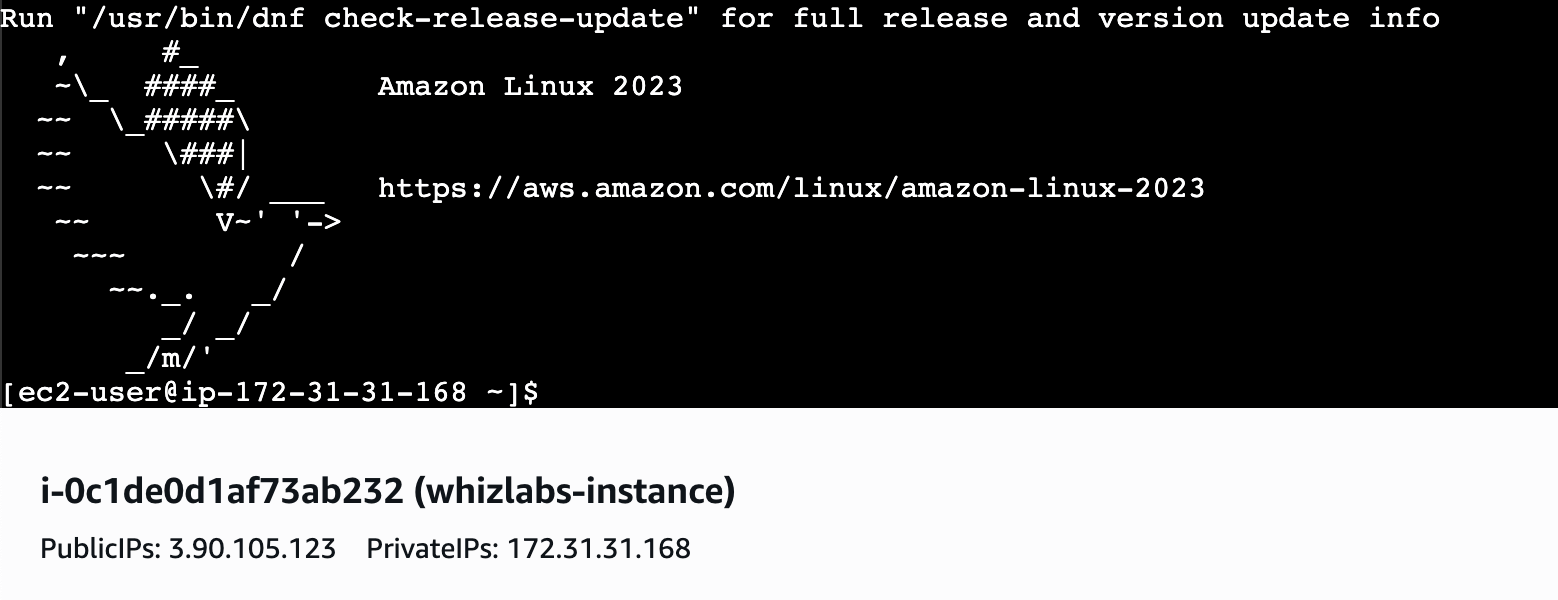
- Run the below commands.
- Lets create sendmessage file in the nano editor.
- Paste the given code in the editor, and press CTRL+X to save the file and then enter Y and click Enter button.
- Run the below command to download the dependencies
- Execute below command to provide the execute permissions.
- It will run the script to send 2000 messages to MyMessages queue.
Task 5: Create CloudWatch Alarms
In this task we are going to create 2 alarms for scalein and scaleout ec2 instances.- Navigate to CloudWatch by clicking on the Services menu available under the Management & Governance section.
- Click on All alarms under Alarms in the left panel of the CloudWatch dashboard.
- Click on Create alarm button available on the top right corner.
- In the Specify metric and conditions page:
- Click on Select metric. It will open the Select Metrics page.
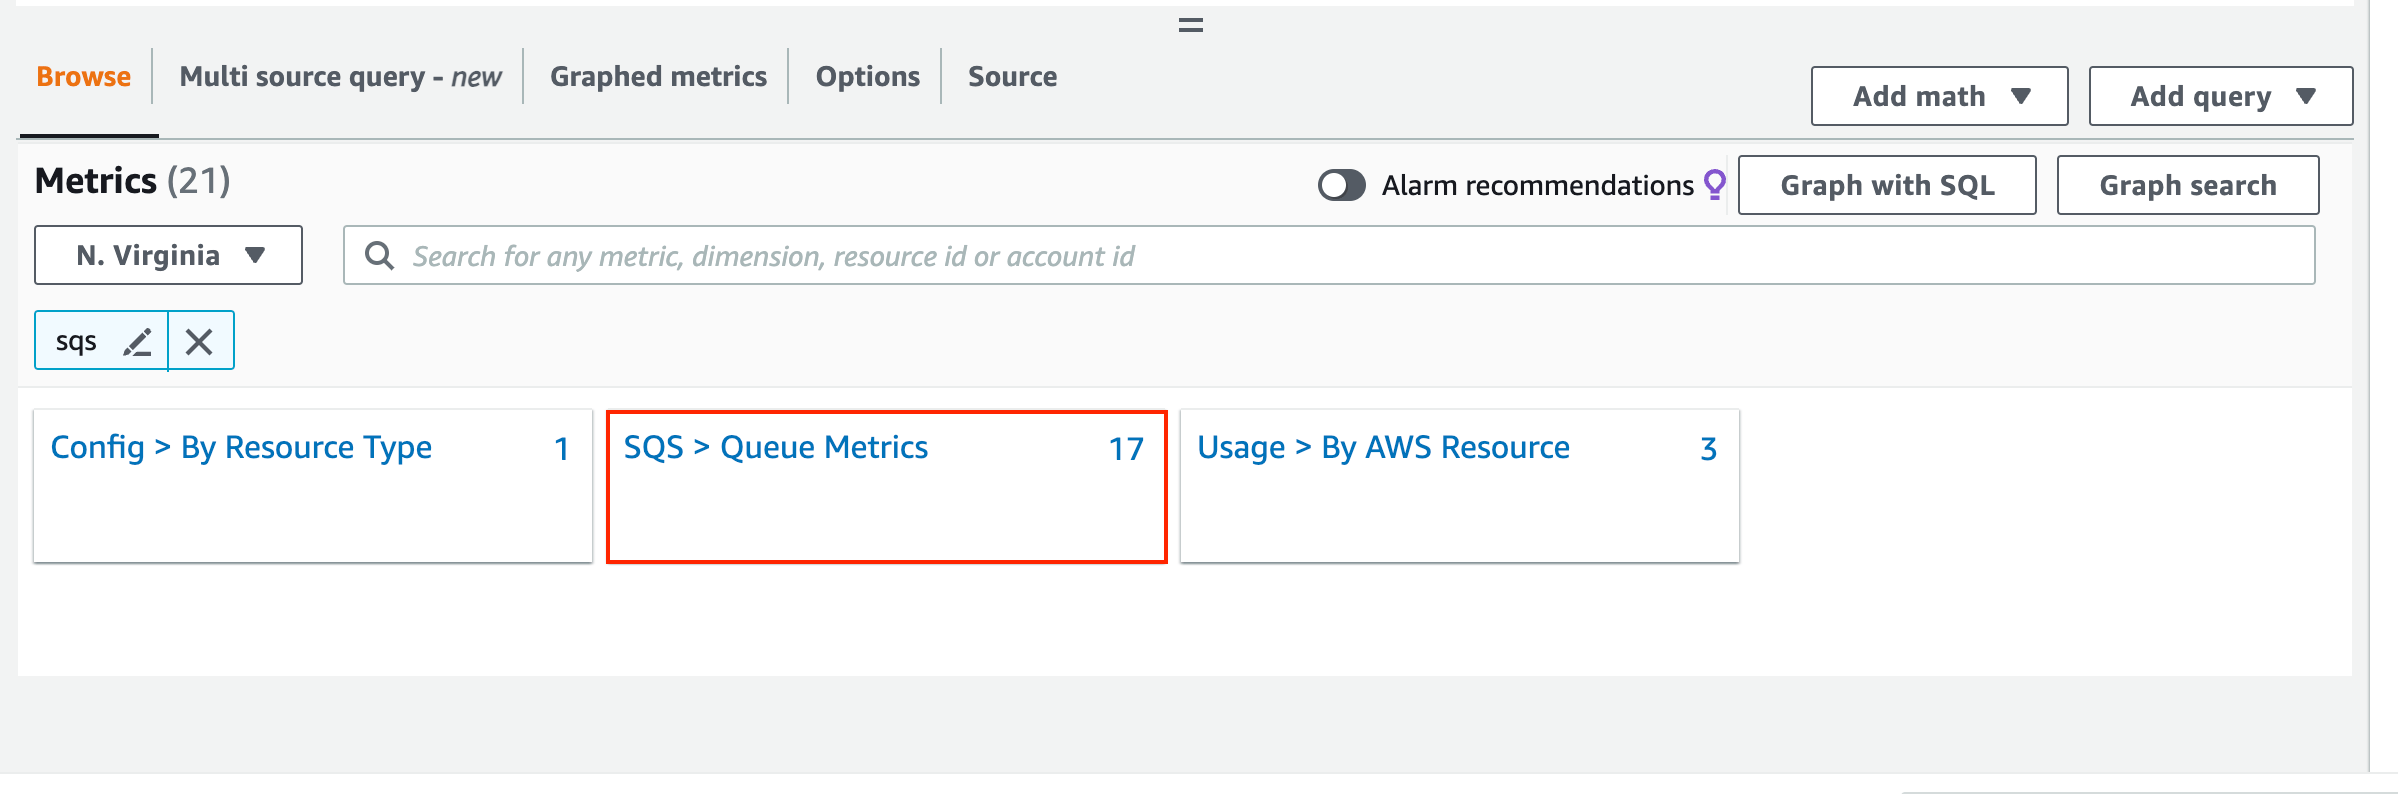
- search for SQS and select SQS > Queue Metrics.
- Now, Select MyMessages > ApproximateNumberOfMessagesVisible and Click Select Metric. {Wait for few minutes and refresh if matric not visible}
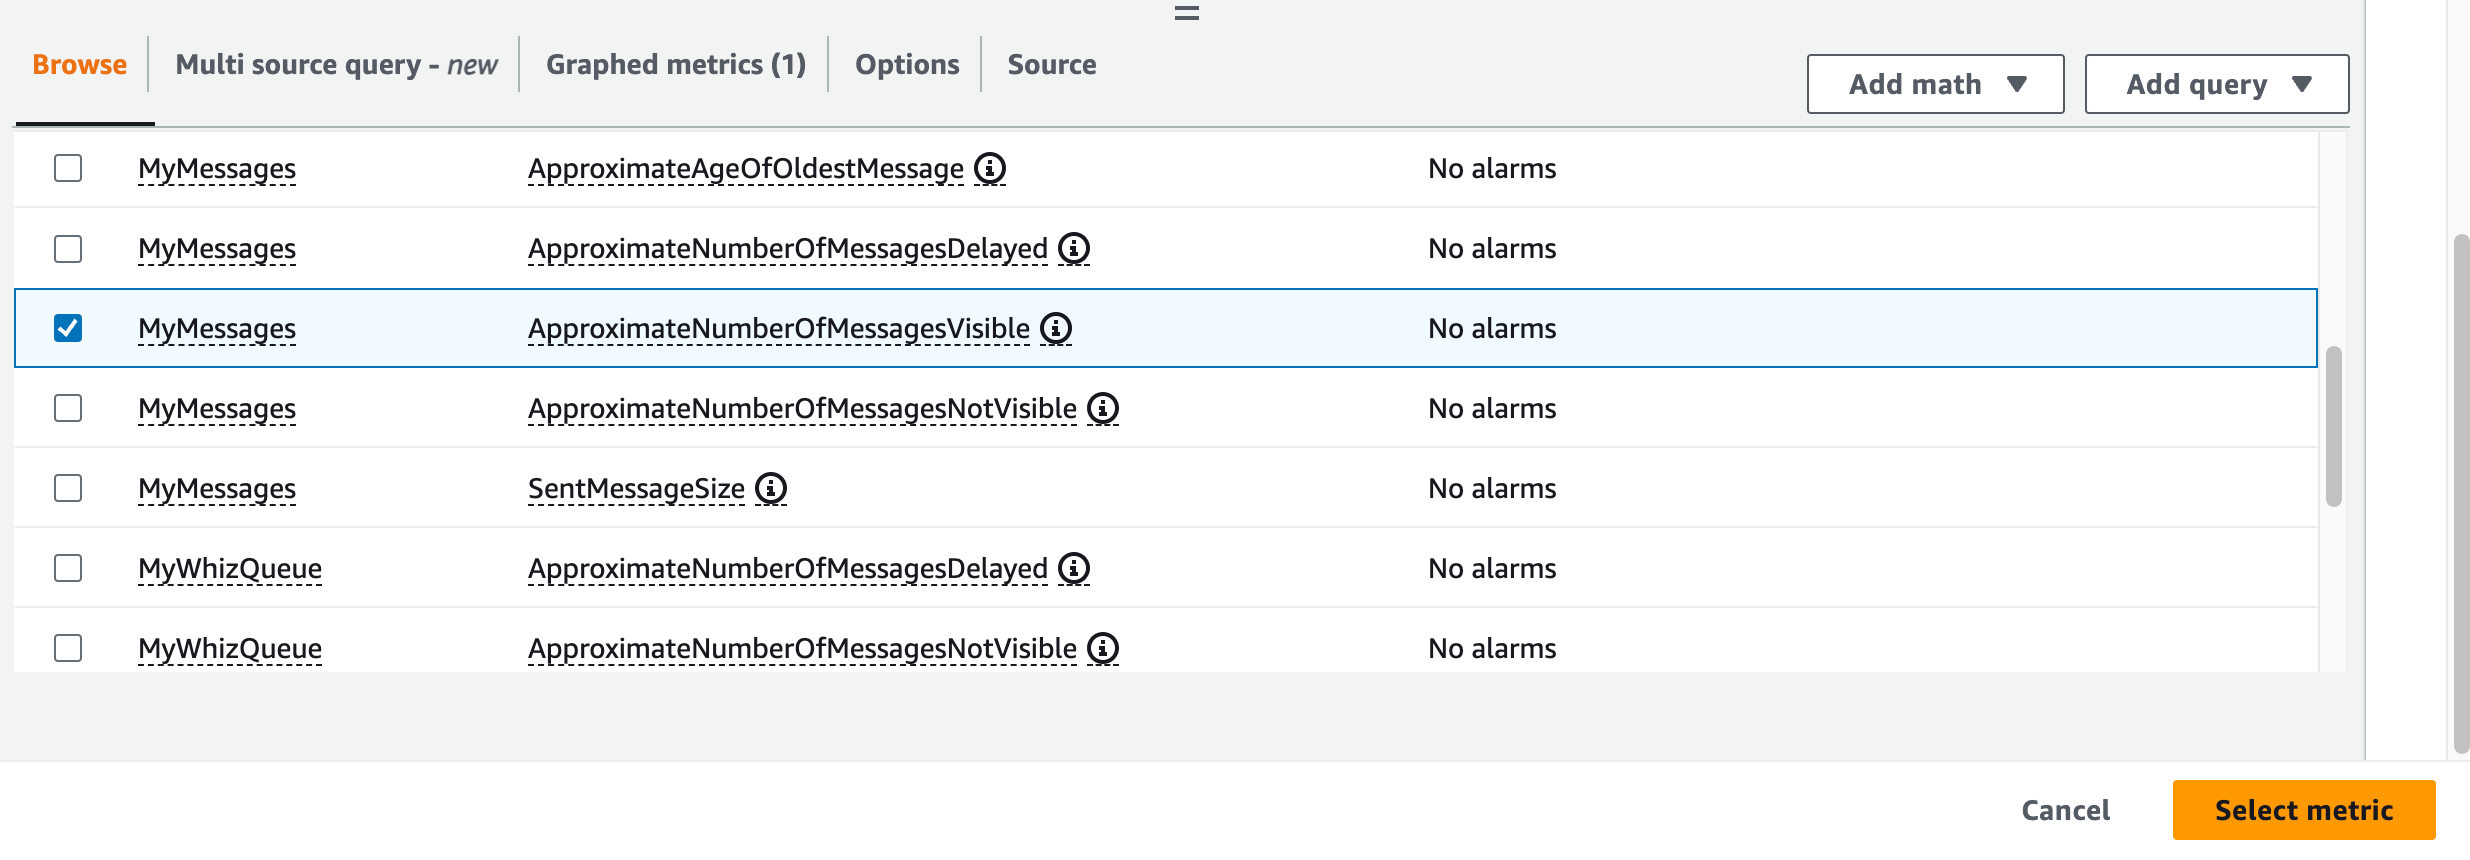
- Click on Select metric button.
- Now, configure the alarm with the following details:
- Under Metrics
- Statistic : Select Sum
- Period: Select 1 Minute
- Under Conditions
- Threshold type: Choose Static
- Whenever CPU Utilization is…: Choose Greater
- than: Enter 500
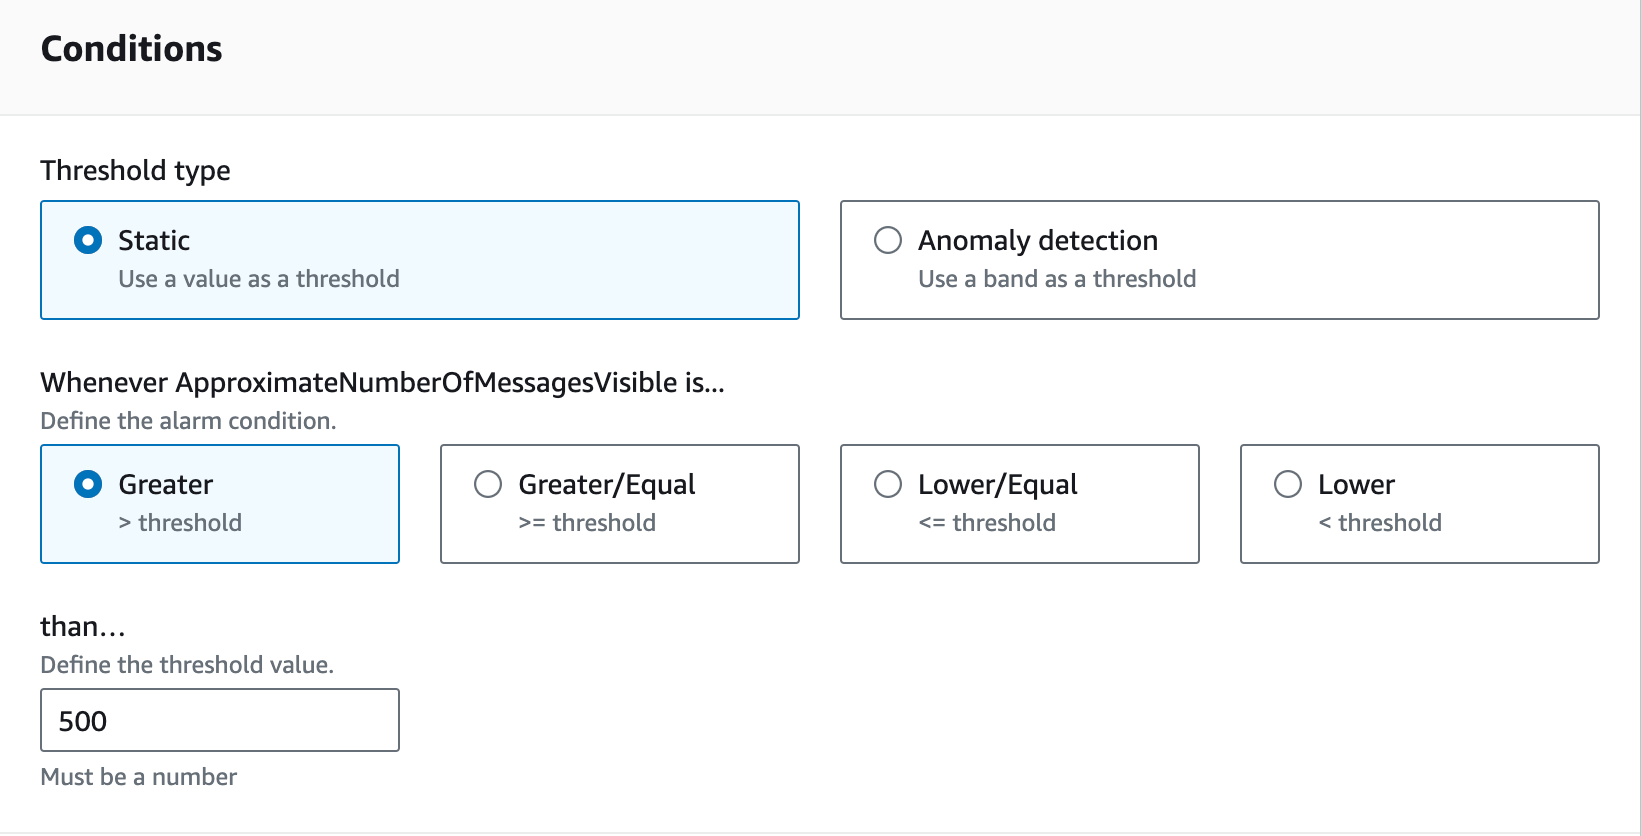
- Leave other values as default and click on Next button.
- In Configure actions page:
- Under Notification : Click on Remove button and click on Next button. Click on Proceed without actions in pop-up appeared
- In the Add a description page, (under Name and Description):
- Name: Enter the Name ScaleOut
- Click on Next button.
- A preview of the Alarm will be shown. Scroll down and click on Create alarm button.
- A new CloudWatch Alarm is now created.
- Now, Similar to ScaleOut, we also need to create a ScaleIn Alarm to launch new instances when the ApproximateNumberOfMessagesVisible is lower than 300.
- Click on ScaleOut alarm and in Actions dropdown click on Copy
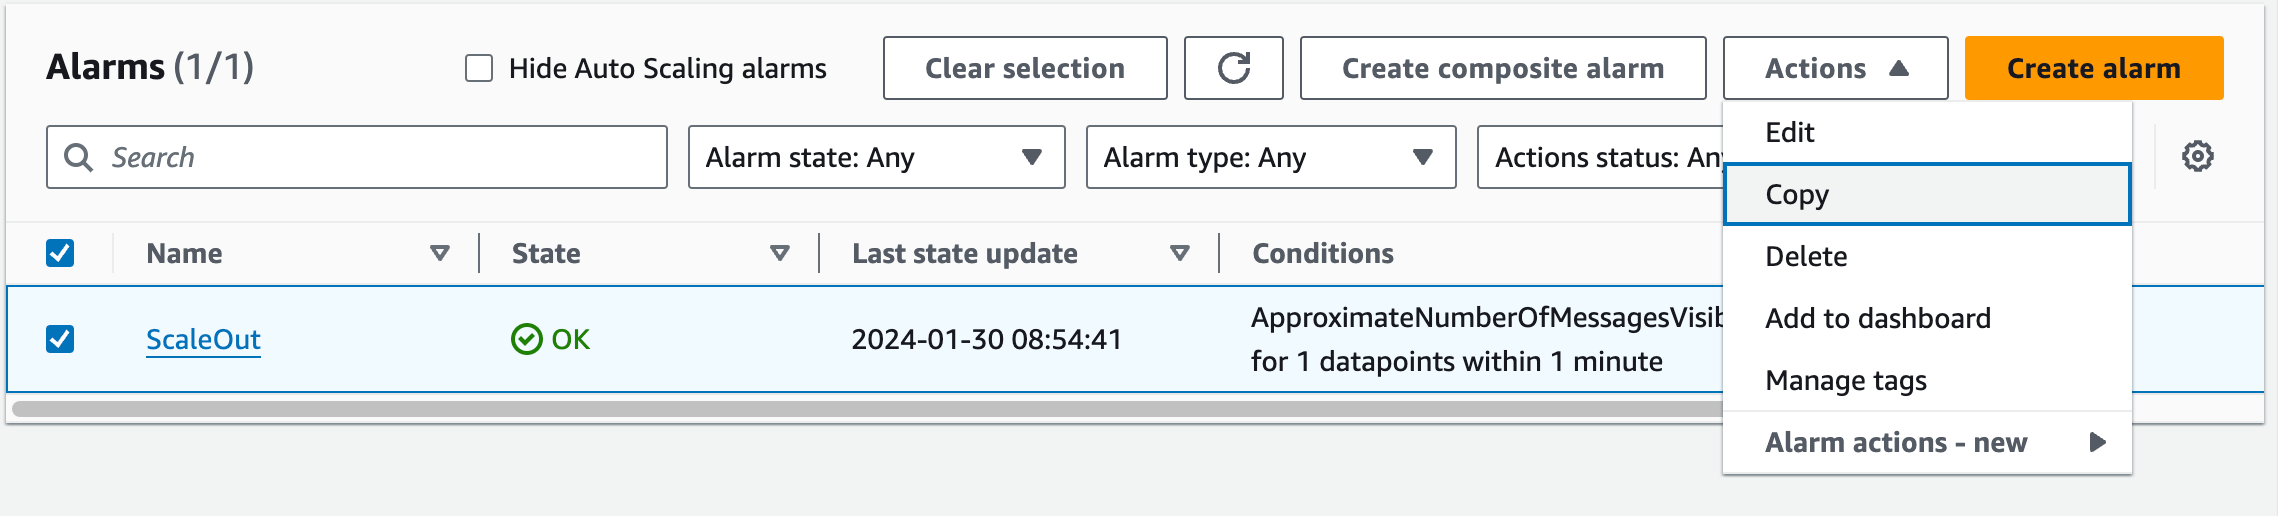
- In conditions change the following :
- Threshold type: Choose Static
- Whenever CPU Utilization is…: Choose Lower
- than: Enter 300
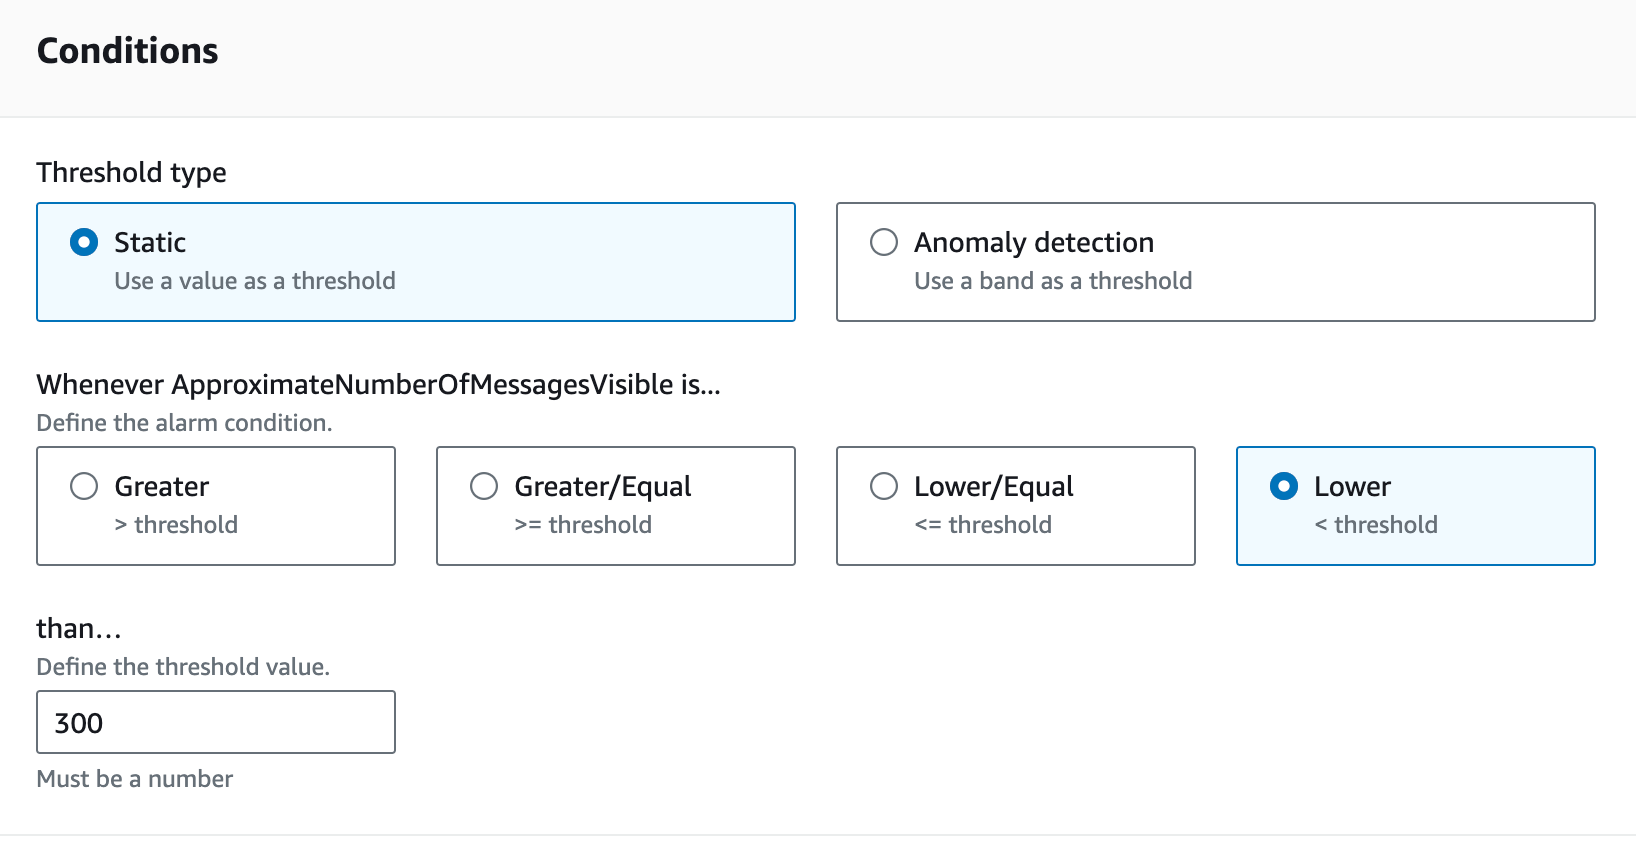
- Leave everything as default and click on Next buttons
- No changes needed, click on Next button.
- Name: Enter the Name ScaleIn
- Click on Next button.
- A preview of the Alarm will be shown. Scroll down and click on Create alarm button.
Task 6: Create a Launch Template
In this task, we are going to create a Launch Template.- Make sure you are in the US East (N. Virginia) us-east-1 Region before proceeding with the Lab.
- Navigate to EC2 by clicking on the Services menu in the top, then click on EC2 in the Compute section.
- In the left navigation menu, scroll down to Launch Templates and click on Create launch template button.
- Launch template name: Enter whizlabsLT
- Template version description: Enter Launch template version 1
- Launch template contents:
- Amazon machine image (AMI): Select Amazon Linux kernel-6.1 AMI
-
Instance type: Select t2.micro
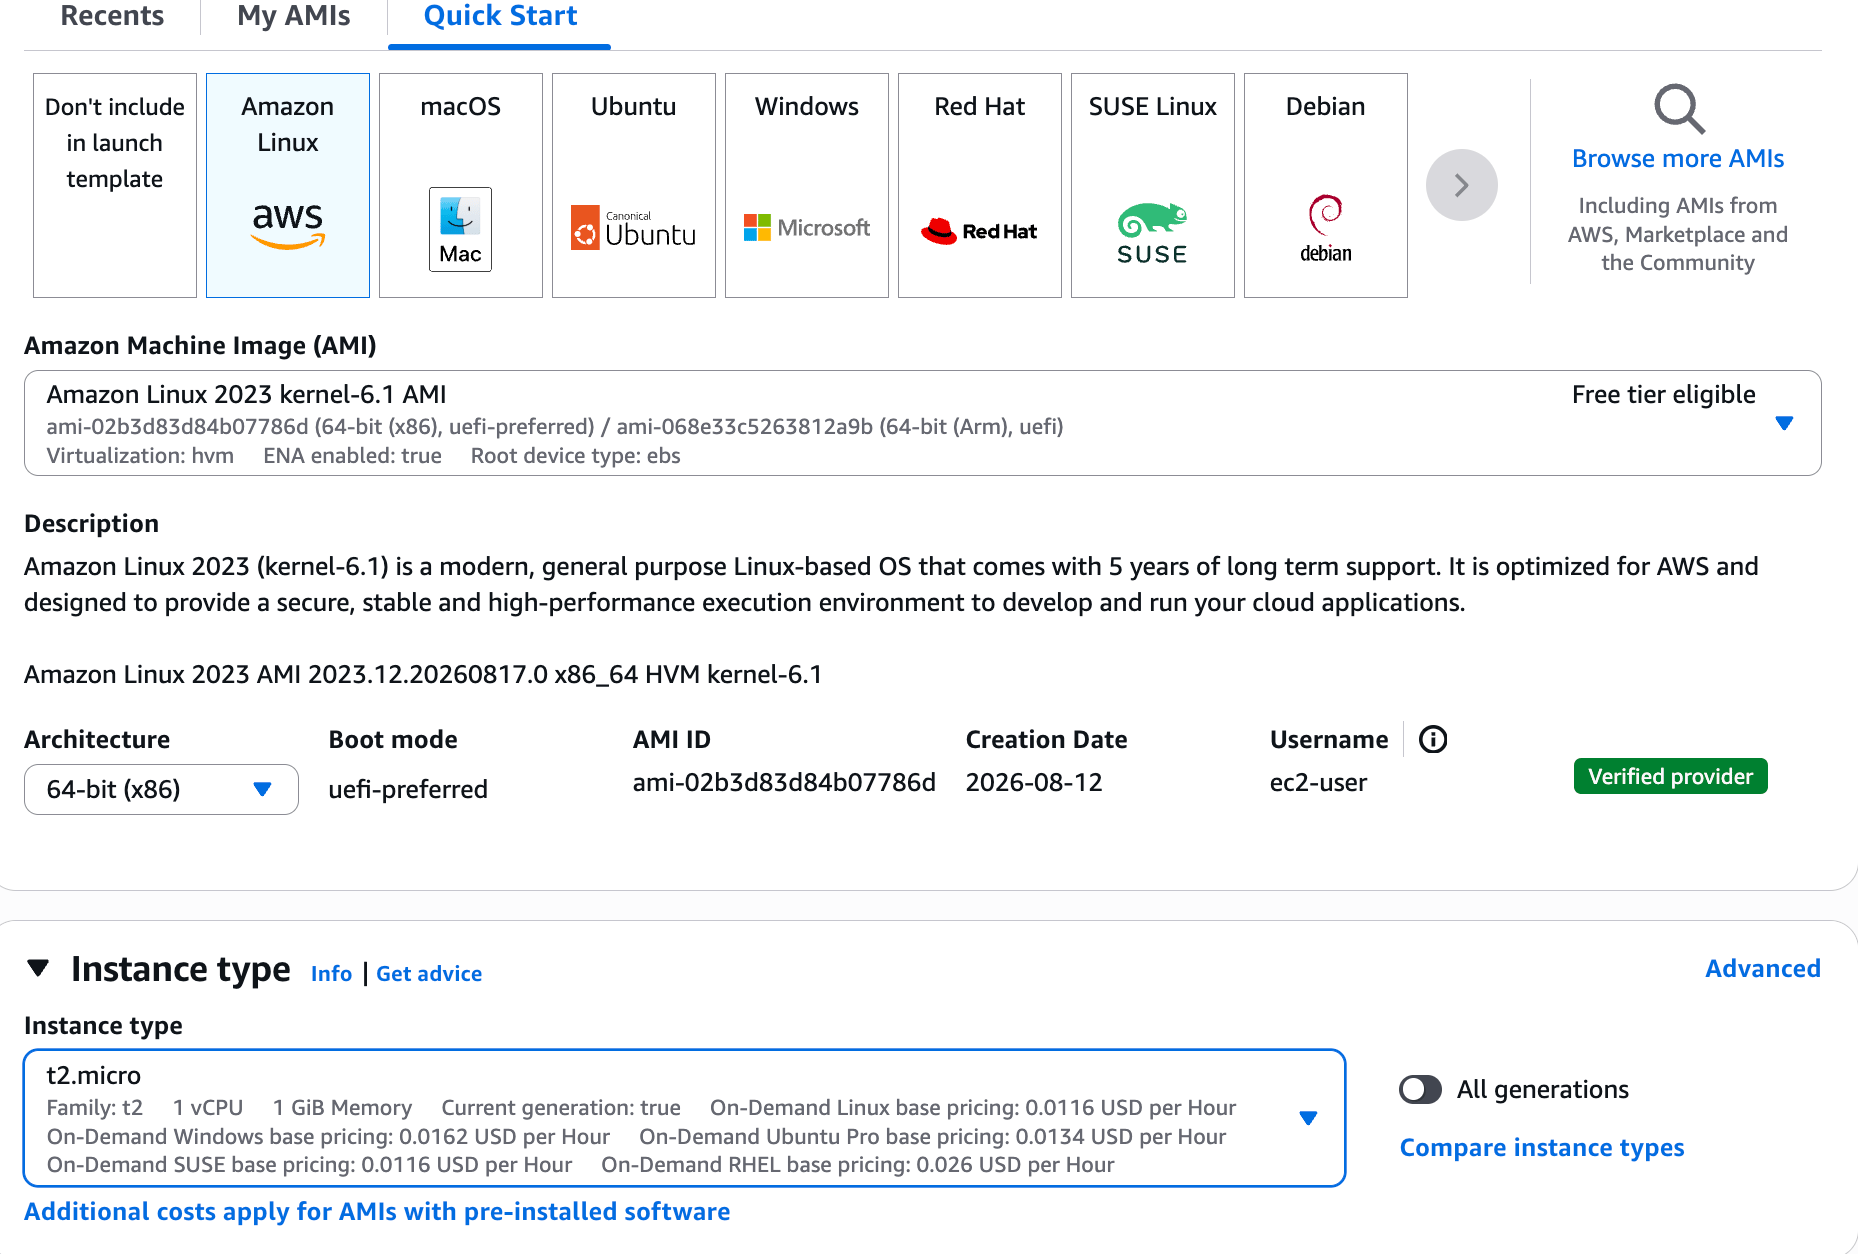
- Key pair (login):
- Key pair name: Don’t include in launch template
- Network settings:
- Security groups: Select the Default security group of Default VPC
- Expand Advance details section;
- For IAM Instance profile : Select EC2SQSS3AccessProfile<random number> Role which is pre-created for use.
- Scroll down to user-data section and copy paste the script.
- Note : Update the bucket name in 14th line with your bucket name
- Now, click on Create launch template button
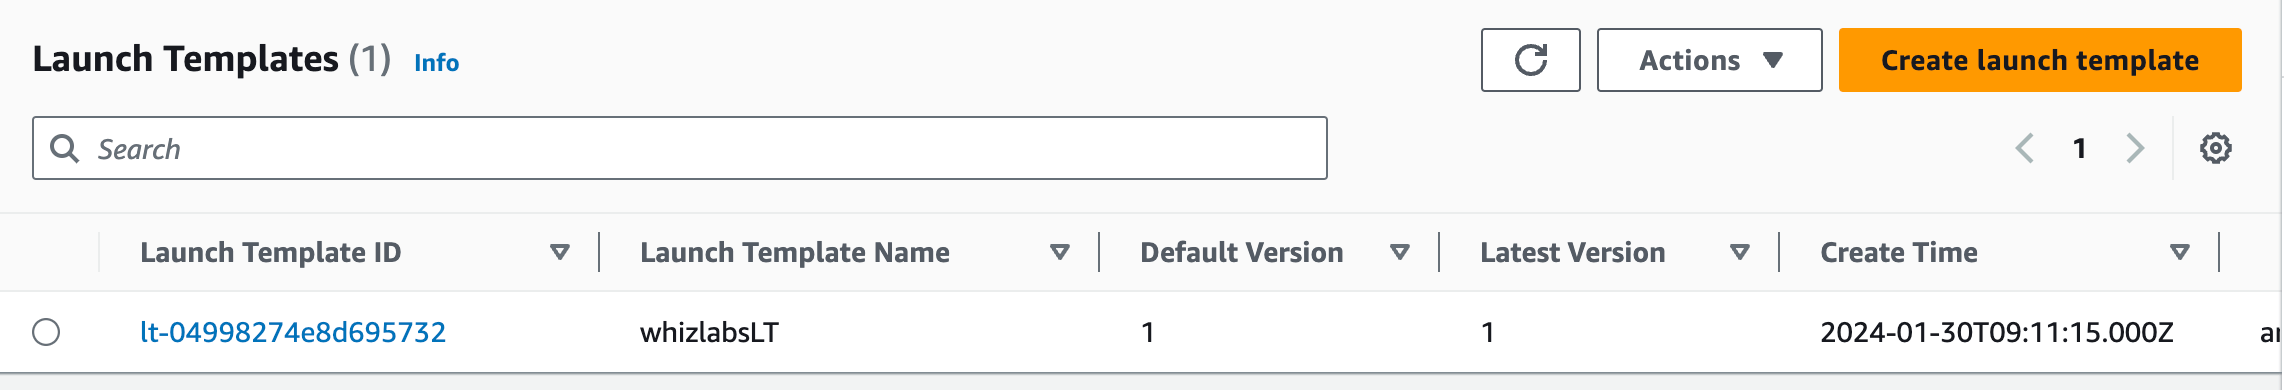
- Launch template is now created.
- Click on the View launch template button.
- Launch template is now listed.
Task 7: Create an Auto Scaling Group
In this task, we are going to create an Auto Scaling group.- Go to the left menu under EC2 and choose Auto Scaling Group under Auto Scaling
- Click on the Create Auto Scaling group button.
- Step 1: Choose launch template or configuration
- Auto Scaling group name: Enter whiz-ASG
- Launch template: Select whizlabsLT
- Click on the Next button.
- Step 2: Configure settings
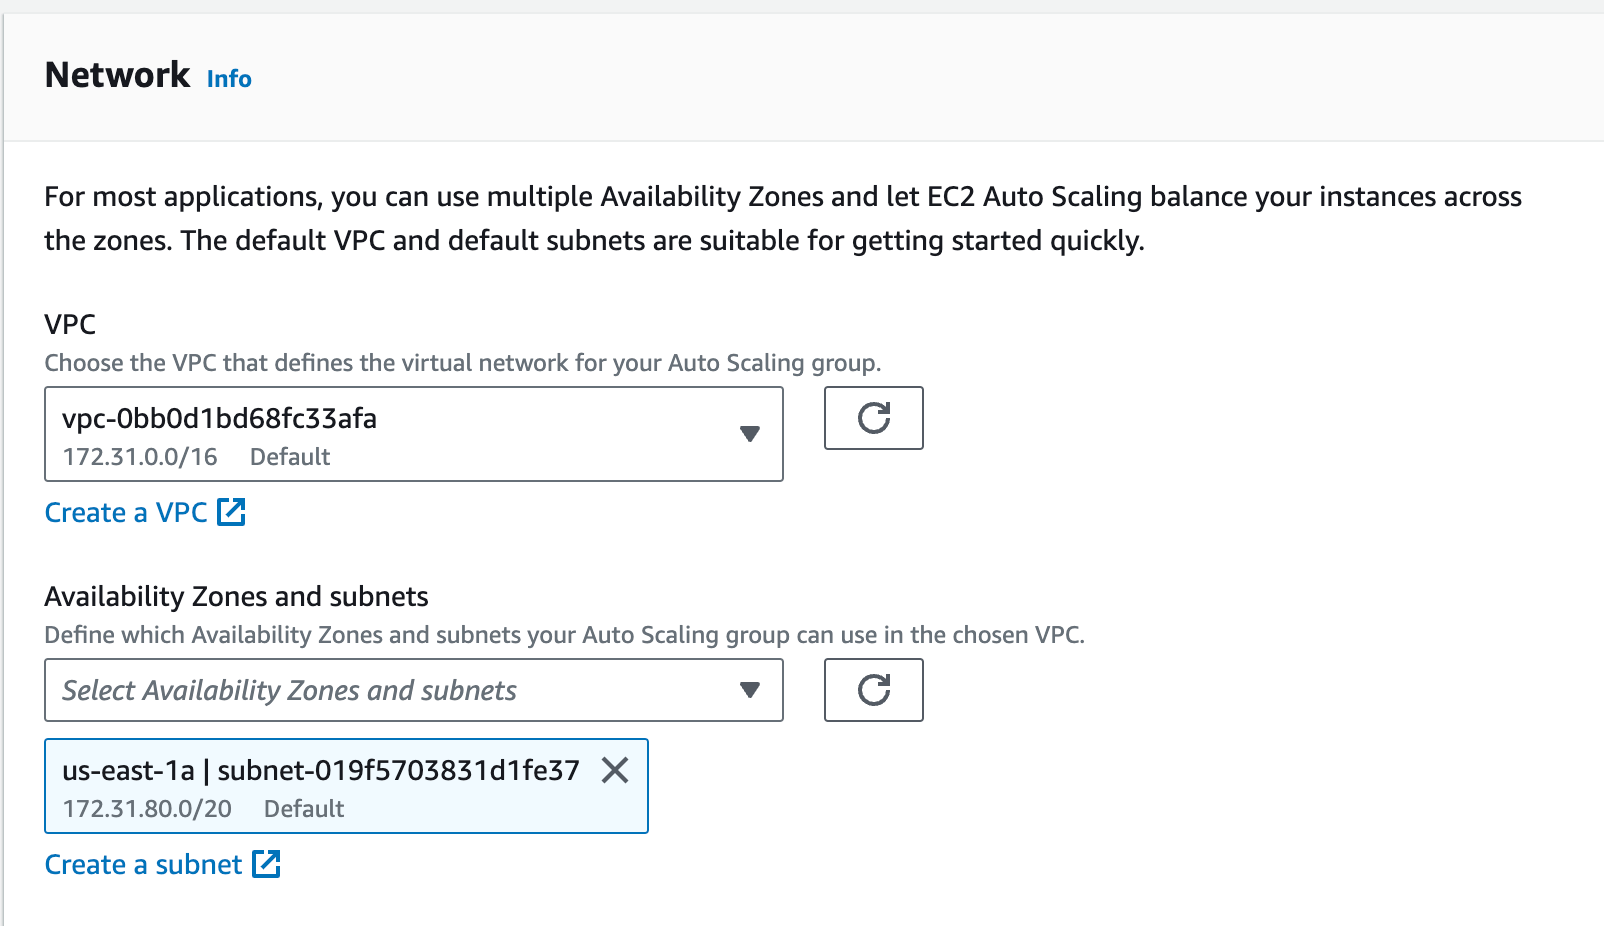
- VPC: Select the Default VPC from the list.
- Subnet: Select subnet available in us-east-1a region.
- Click on the Next button.
- Step 3: Configure advanced options
- No changes are needed on this page, click on the Next button.
- Step 4: Configure group size and scaling policies
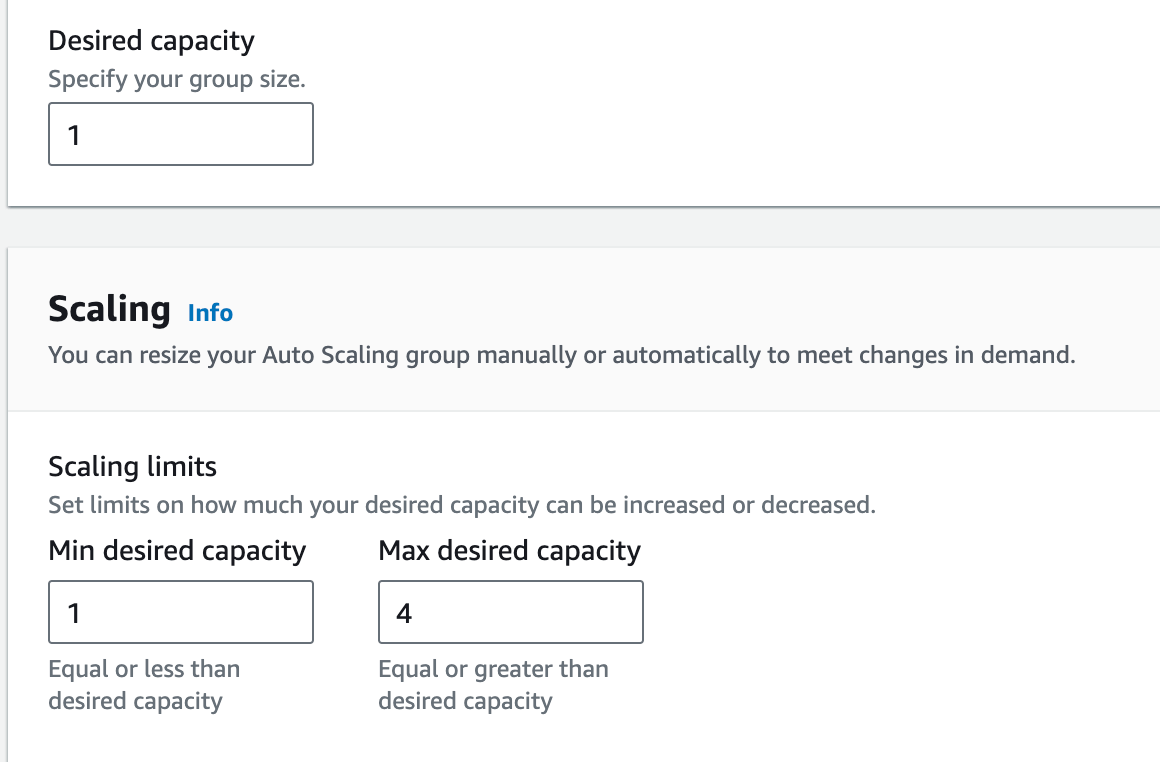
- Under Group size – optional
- Desired capacity: Enter 1
- Minimum capacity: Enter 1
- Maximum capacity: Enter 4
- No changes are needed, click on the Next button
- Step 5: Add notifications
- No changes are needed on this page, click on the Next button.
- Step 6: Add tags
- No changes are needed on this page, click on the Next button.
- Click on the Next button
- Now scroll down and click on the Create Auto Scaling group button.
- Whiz-ASG Auto scaling is created successfully.
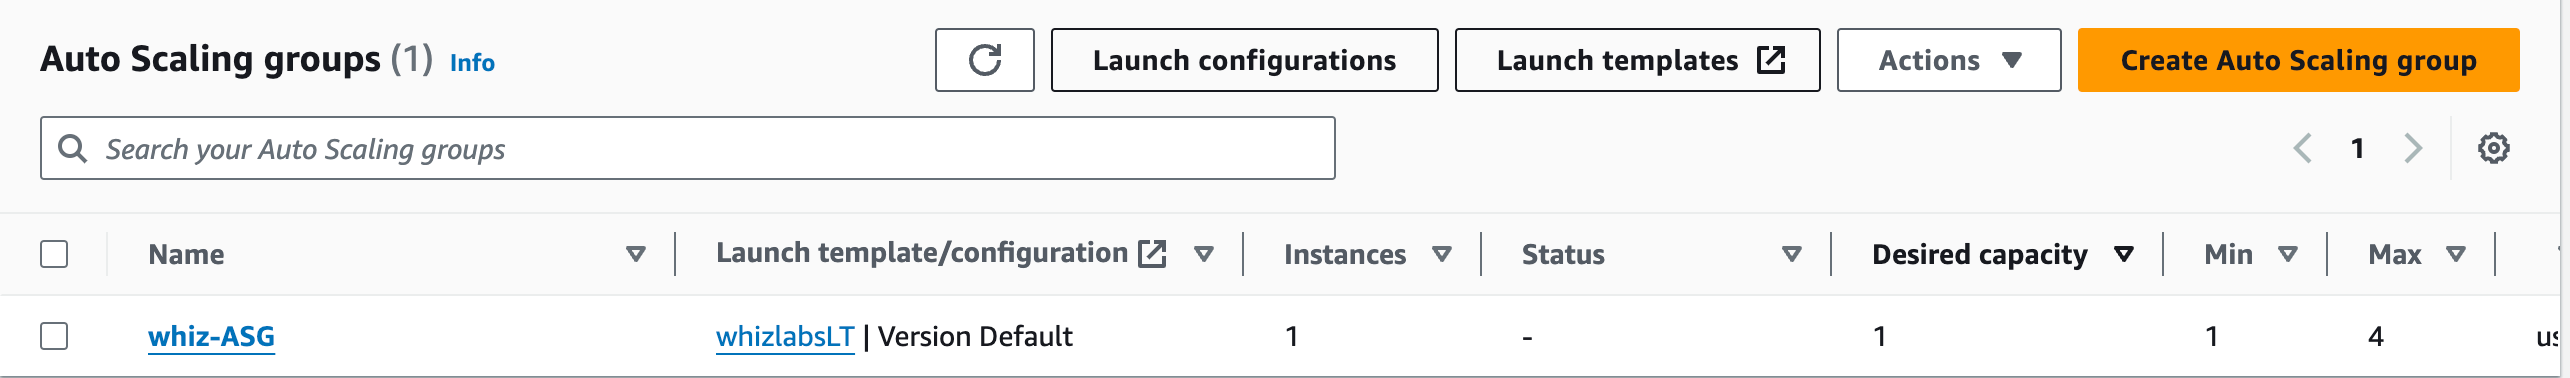
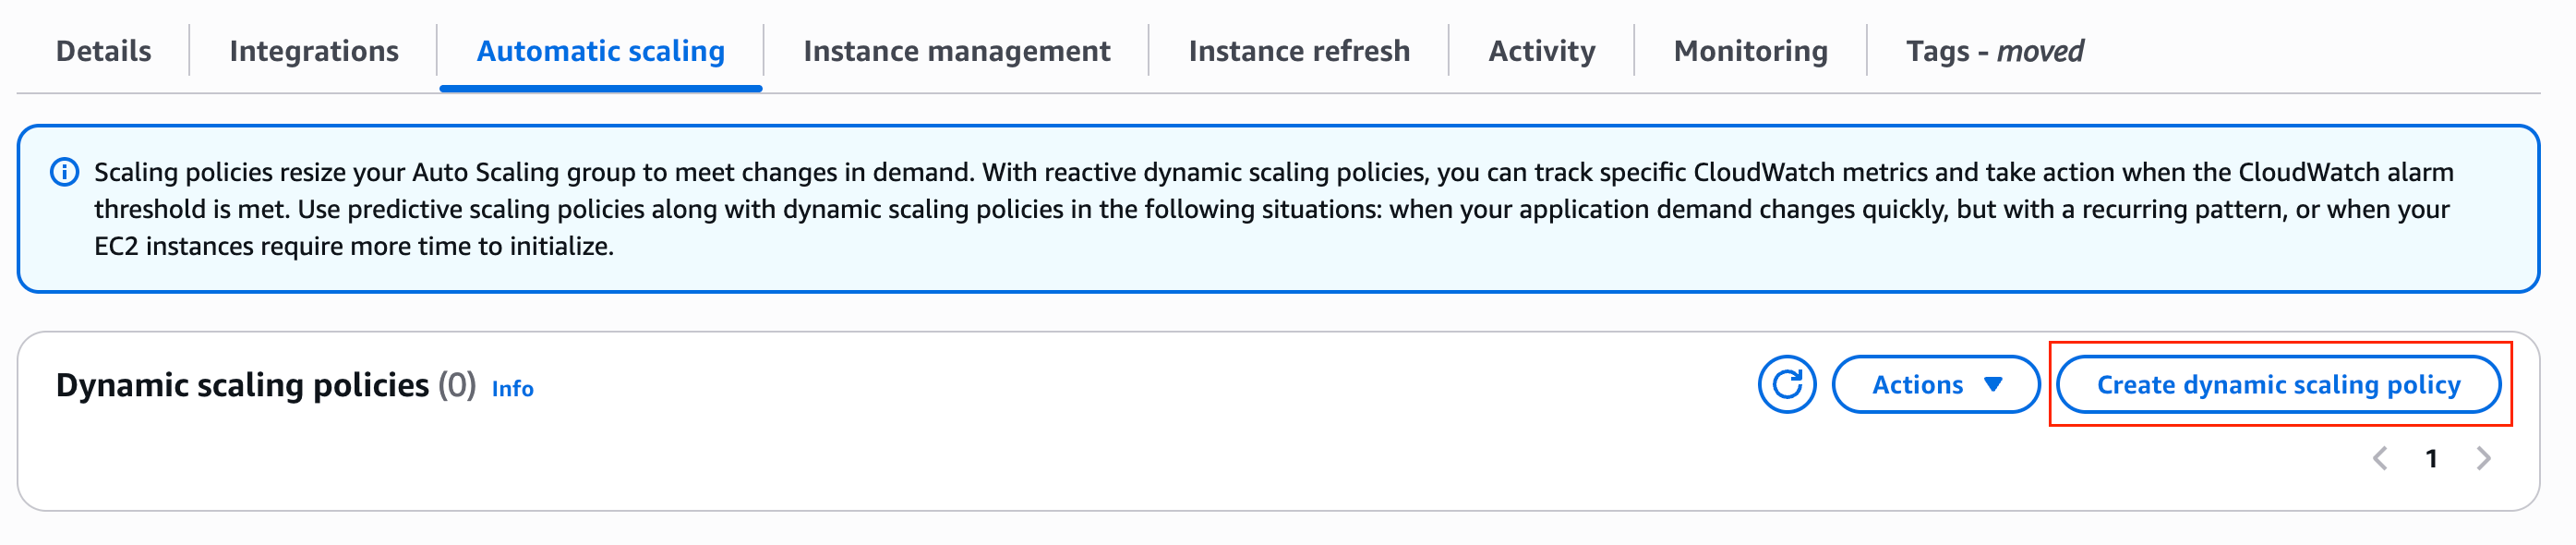
- Now, to add scaling policies in auto scaling group
- Click on autoscaling group and navigate to Automatic scaling tab and click on Create dynamic scaling policy button.
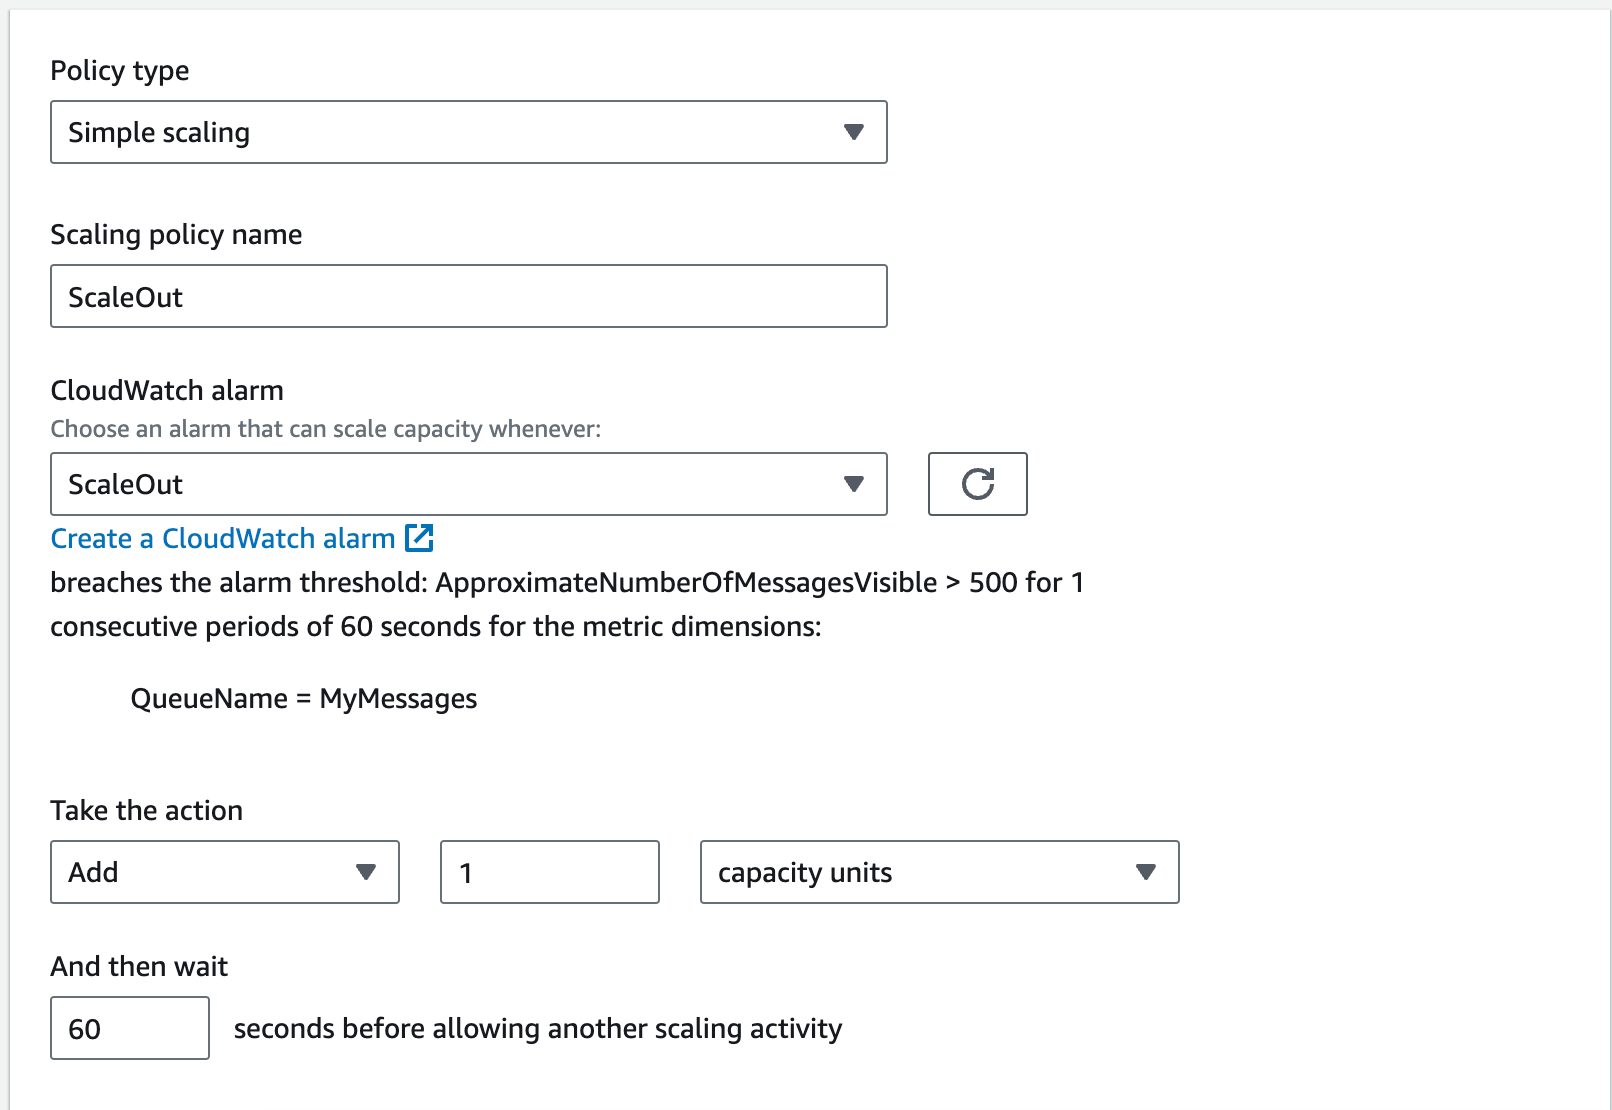
- Update the following details :
- Policy type : Select Simple scaling
- Scaling policy name: Enter ScaleOut
- CloudWatch alarm: Select ScaleOut
- Take the action: Add with 1 capacity units
- And then wait 60 seconds before allowing another scaling activity
- Click on Create button.
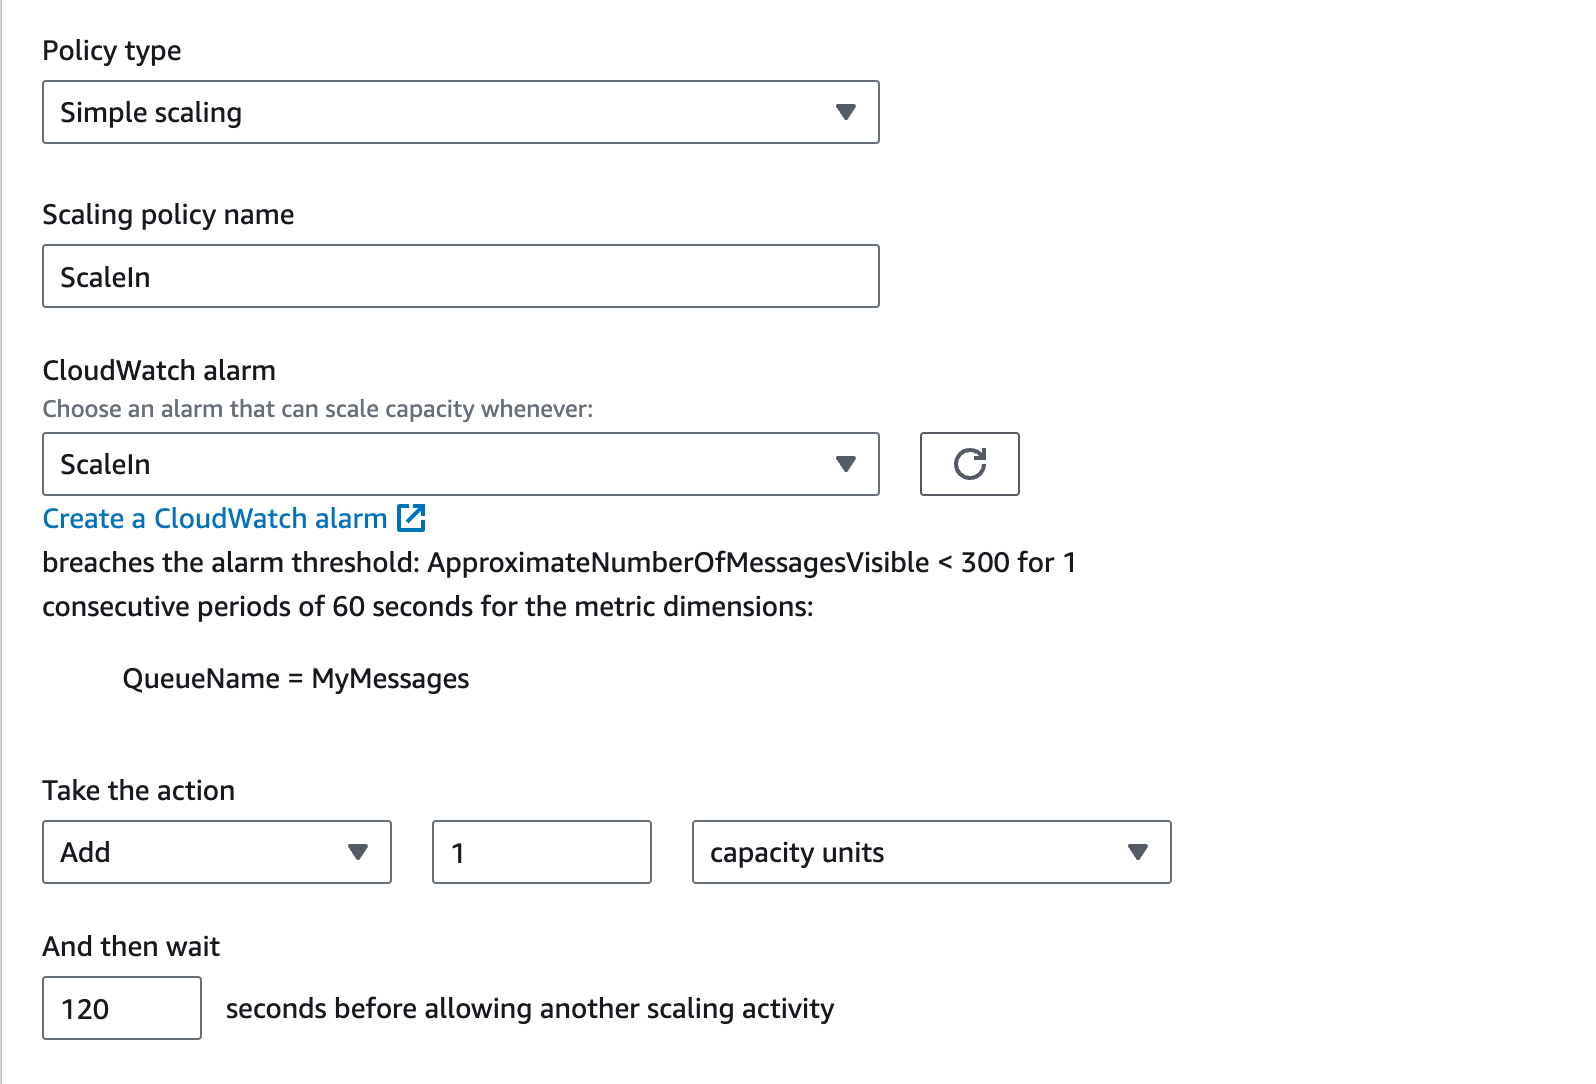
- Similarly, create another scaling policy to for ScaleIn with following details:
- Policy type : Select Simple scaling
- Scaling policy name: Enter ScaleIn
- CloudWatch alarm: Select ScaleIn
- Take the action: Add with 1 capacity units
- And then wait 120 seconds before allowing another scaling activity
- Click on Create button.
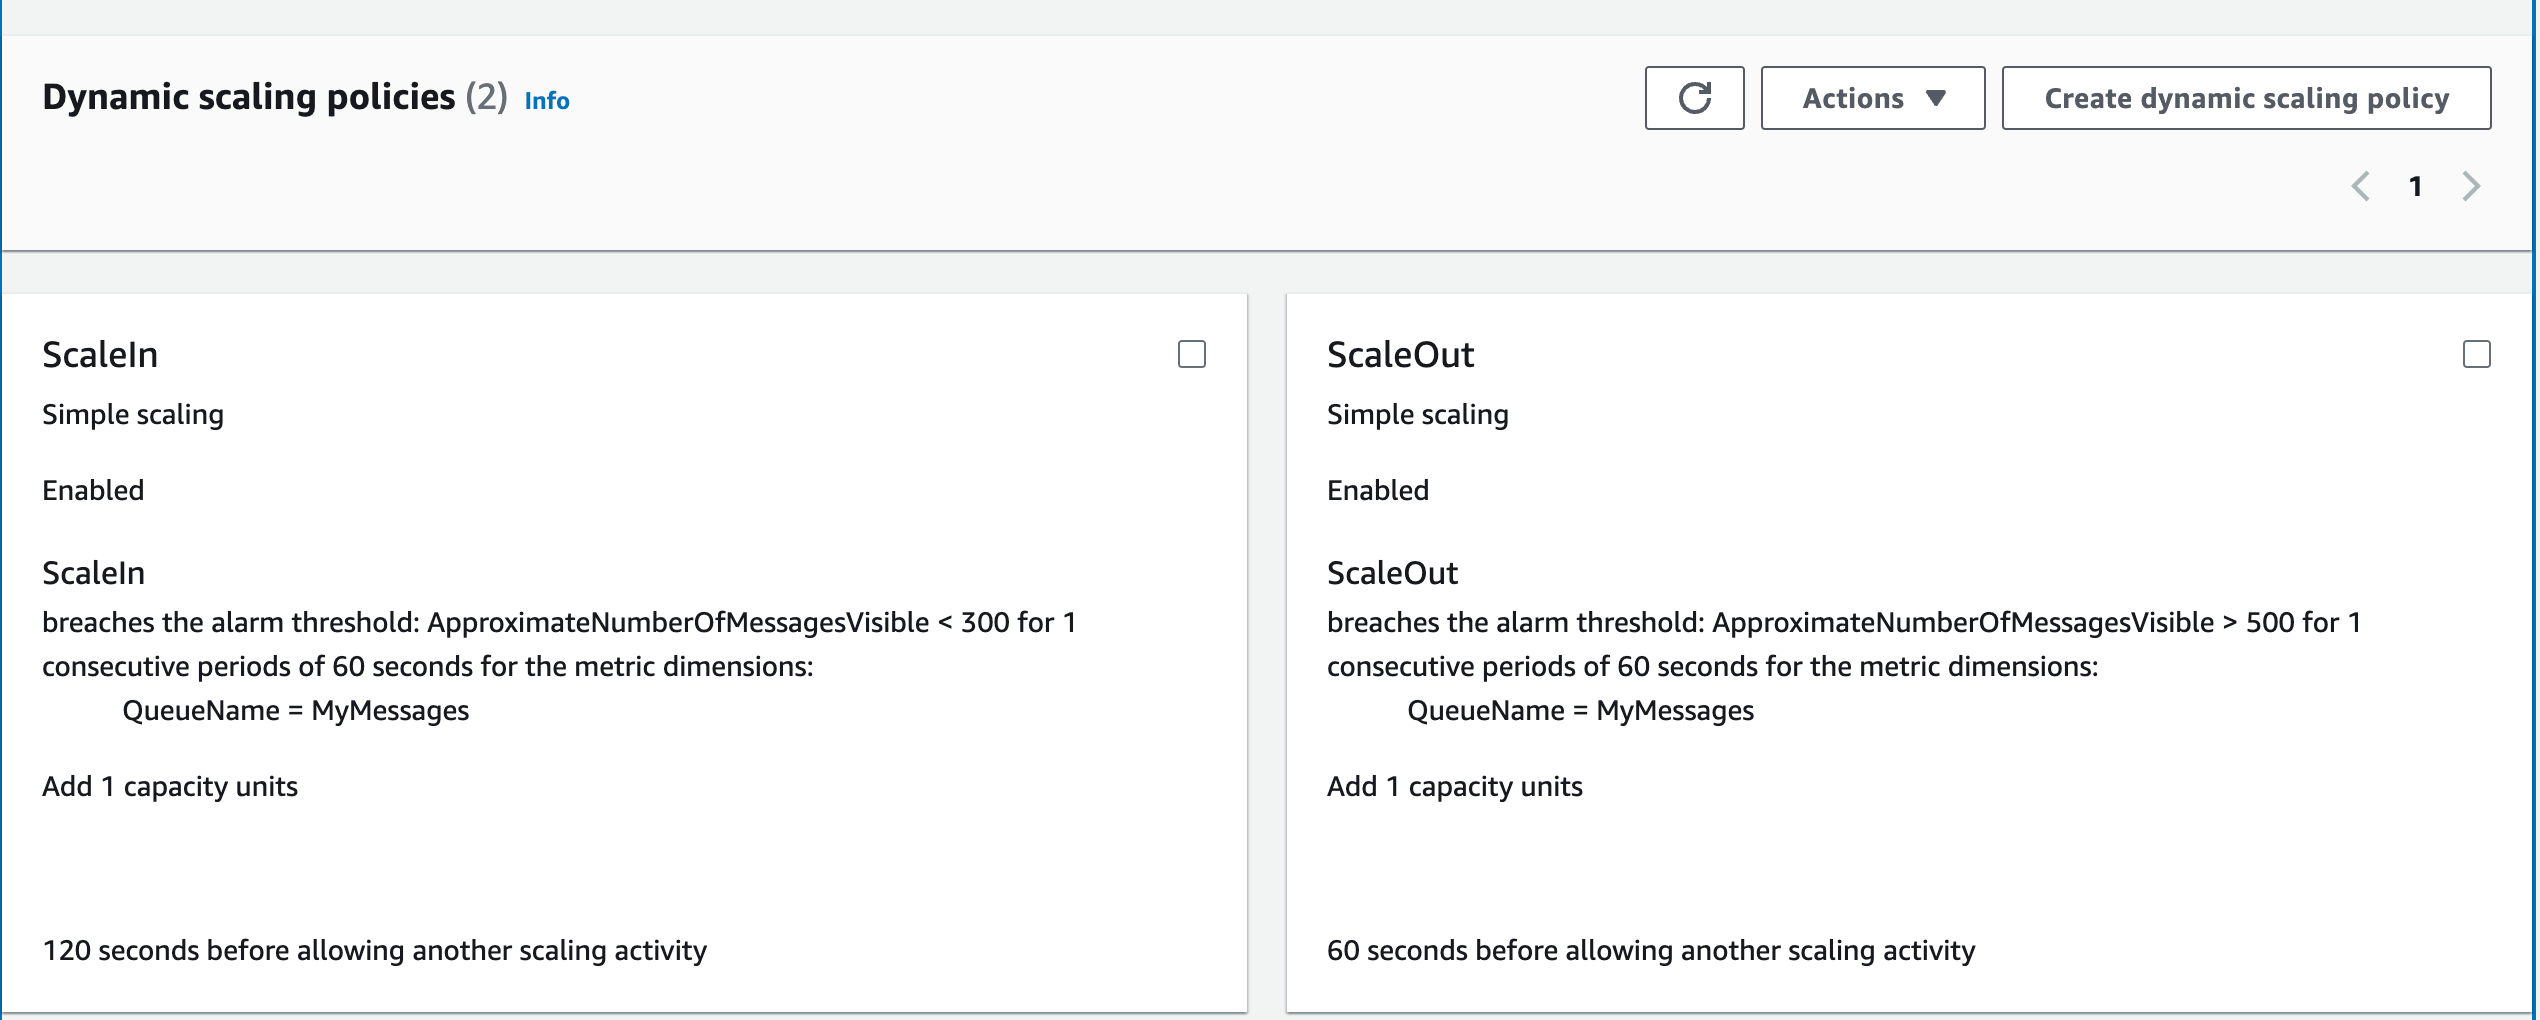
- Now, you can see two policies added.
Task 8: Verifications and Monitoring
We have populated the sqs queue with 2000 messages and have an auto scaling group launch with a maximum of 4 instances. We will now be verifying messages using Cloud Watch Alarms and Auto Scaling group’s Activity.- Navigate to CloudWatch > Alarms , and check the state of Alarm status.
- If ScaleIn alarm is in InAlarm state -> New instance will get created.
- If ScaleOut alarm is in InAlarm state -> Launched instances will be terminated
Do you know?
SQS acts as a buffer between the message producers and the EC2 instances. As messages are sent to the SQS queue, EC2 instances can retrieve messages from the queue at their own pace, allowing for smooth and balanced workload distribution.
Completion and Conclusion
- You have successfully created and uploaded object to an s3 bucket
- You have successfully created an SQS Queue
- You have successfully created CloudWatch alarms
- You have successfully created Autoscaling Groups
- You have successfully Verified and Monitored EC2 Instances
End Lab
- Sign out of AWS Account.
- You have successfully completed the lab.
- Once you have completed the steps, click on End Lab from the IP Lab Portal dashboard.
What gets checked
When you press Check my work, the platform verifies each of these:- Create Amazon EC2 Auto Scaling Group — Check whether an Auto Scaling Group is created or not.
- Launch an EC2 Instance — Check whether an EC2 Instance is launched or not.
- Create Amazon EC2 Launch Template — Check whether an EC2 Launch Template is created or not.
- check s3 object — Check whether an object is uploaded to the S3 bucket.
- Create Private S3 bucket — Check whether a private S3 bucket is created or not
- Create Standard SQS Queue — Check whether a Standard SQS Queue is created or not.
- Check CloudWatch Alarm Creation — Check whether at least one CloudWatch alarm exists or not.