

Overview
Prerequisites
1. Good knowledge of AWS service- Virtual Private Cloud (VPC)
- Elastic Compute (EC2)
Challenge Instructions
1. Region : Make sure to use us-east-1 region to create all the resources. 2. You will be provided with the requirements of the challenge. If you are new to AWS Cloud, we recommend you go through our hands-on Labs before taking this challenge. 3. Challenge Duration: 45 minHow to submit the challenge
1. After building the infrastructure, click on the Validation button, to validate if you have built the required infrastructure and completed the challenge successfully. 2. Validation status: o Success - You have completed the challenge successfully. o Failed - You have failed to complete the challenge. 3. Once you have successfully validated the challenge, click on End Lab button to end the challenge.Launching Challenge Environment
1. To launch the challenge environment, Click on the Start Challenge button. 2. Please wait until the cloud environment is provisioned. It will take less than a minute to provision. 3. Once the Challenge is started, you will be provided with IAM user name, Password, Access Key, and Secret Access Key. Note : You can only start one challenge at any given timeLab guide
Sign in to AWS Management Console
Click on the Open Console button, and you will get redirected to AWS Console in a new browser tab.
- On the AWS sign-in page, leave the Account ID as default. Never edit/remove the 12 digit Account ID present in the AWS Console. otherwise, you cannot proceed with the challenge.
- Now copy your User Name and Password in the Lab Console to the IAM Username and Password in AWS Console and click on the Sign in button.
- Once Signed In to the AWS Management Console, Make the default AWS Region as US East (N. Virginia) us-east-1.
Cloud Challenge Details
In this challenge, your Virtual Private Cloud (VPC) skills are put to the test. You’ll be given a requirement and you have to reach it using your knowledge of Elastic Compute (EC2), Internet Gateway, Route Tables, Subnets and Transit gateway which will be used in this challenge. This Challenge will help you understand the real-time scenarios.Architecture Diagram
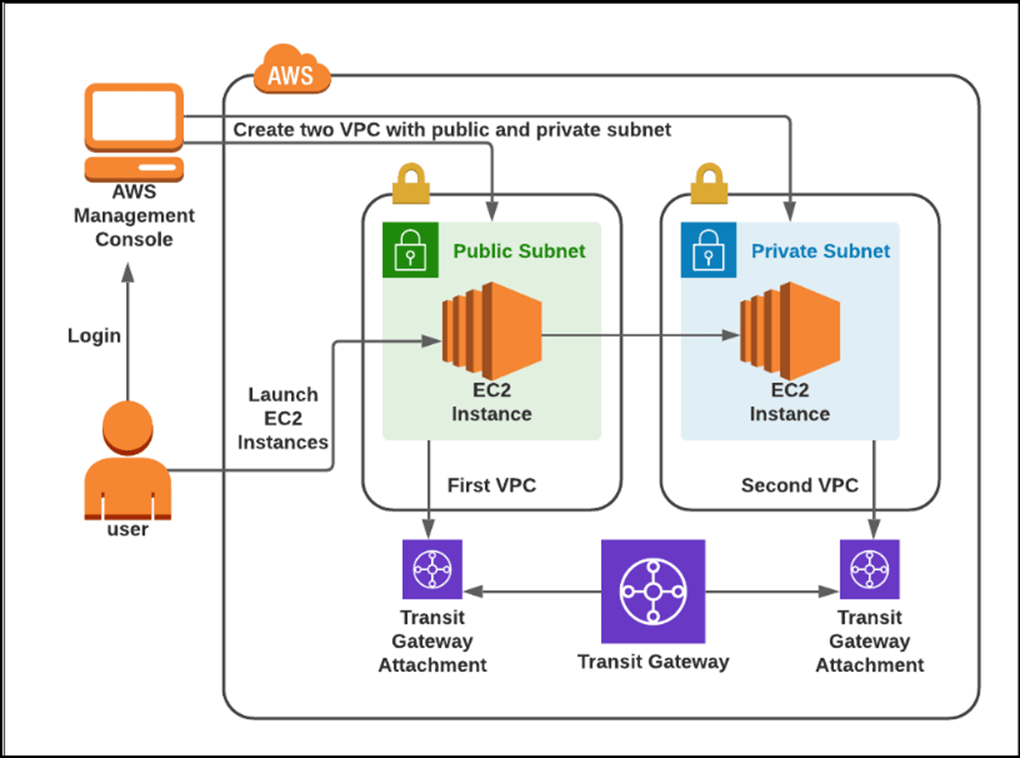
- Create VPC with 10.0.0.0/24 IPv4 block and give access to DNS.
- Create Public Subnet in VPC with 10.0.0.0/25 IPv4 block.
- Create Internet gateway and attach VPC.
- Create Public Route Table and associate it with Subnet.
- Add public route in the Route Table:
- Default Route with Internet Gateway.
- Create EC2 Instance in the VPC:
- AMI: Amazon Linux 2023 kernel-6.1 Instance type: t2.micro
- Create key pair
- Create Security Group with 3 ports like SSH, HTTP and HTTPS.
- Create an script HTML page served by Apache httpd web server.
- Create another VPC with 20.0.0.0/24 IPv4 block with DNS access.
- Create Private Subnet with 20.0.0.0/25 IPv4 block.
- Create same for another EC2 Instance in the VPC with SSH port.
- Create 2 Transit Gateway attachments for the VPCs created.
- Add the routes in the first VPC’s route table:
- Destination as 20.0.0.0/24
- Target: Transit Gateway
- Add the routes in the second VPC’s route table:
- Destination as 20.0.0.0/24
- Test the connectivity between two VPCs.
- Click on the Validate to complete the challenge.
- Delete the resources after Validation.
End Challenge
- Sign out of the AWS Account.
- You have successfully completed the challenge.
- Click on End Challenge button from IP Lab Portal Labs console and wait till the process gets completed.
What gets checked
When you press Check my work, the platform verifies each of these:- Launch an EC2 Instance — Check whether an EC2 Instance is launched or not.
- Validate EC2 Instance Type t2.micro — Check whether the EC2 instance type is t2.micro.
- Create VPC Transit Gateway — Check whether a Transit Gateway is created with status Available or not.
- Create VPC Transit Gateway Attachment — Check whether a Transit Gateway Attachment is created with Resource Type VPC and status Available or not.
- Create Amazon Custom VPC — Check whether a Custom VPC is created or not.
- Create Amazon Custom VPC Subnet — Check whether a Subnet is created for the Custom VPC or not.
- Create Amazon Custom VPC Public Route Table — Check whether a Custom VPC Public Route Table is created and an Internet Gateway route is added or not.
- Create Internet Gateway — Check whether an Internet Gateway is created and attached to the Custom VPC or not.