

Overview
Lab Details
- This lab walks you through the steps to create and configure an Amazon EC2 Auto Scaling with Launch templates using the AWS Management Console.
- You will practice using Amazon Machine Image (AMI) to launch Amazon EC2 Instances using Launch templates and will use key pairs for SSH authentication to log into your instance.
- You will create a web page and publish it.
- Duration: 55 minutes
- AWS Region: US East (N. Virginia) us-east-1
Architecture Diagram
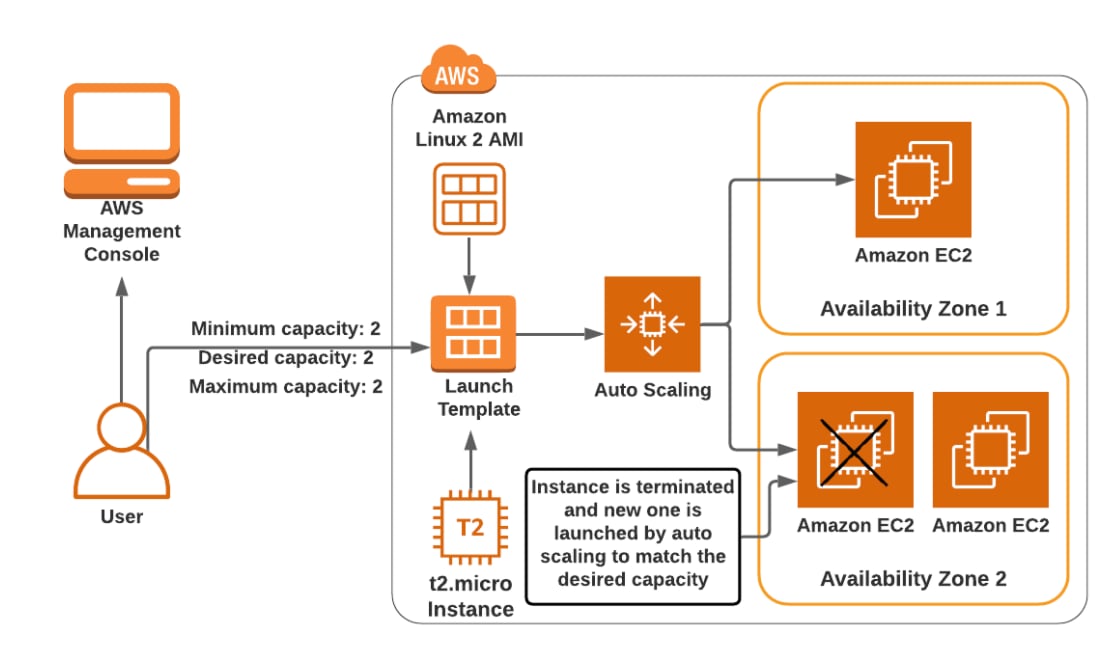
Task Details
- Sign into AWS Management Console.
- Create a security group for Launch template
- Create a key pair for the Launch template.
- Create a launch template
- Create an EC2 Auto Scaling group
- Test Auto scaling group
Launching Lab Environment
- To launch the lab environment, Click on the Start Lab button.
- Please wait until the cloud environment is provisioned. It will take less than a minute to provision.
- Once the Lab is started, you will be provided with IAM user name, Password, Access Key, and Secret Access Key.
Note : You can only start one lab at any given time
Lab guide
Lab Steps
Task 1: Sign in to AWS Management Console
- Click on the Open Console button, and you will get redirected to AWS Console in a new browser tab.
- On the AWS sign-in page,
- Leave the Account ID as default. Never edit/remove the 12 digit Account ID present in the AWS Console. otherwise, you cannot proceed with the lab.
- Now copy your User Name and Password in the Lab Console to the IAM Username and Password in AWS Console and click on the Sign in button
Task 2: Create a Security Group for Launch template
- Make sure you are in the N.Virginia Region.
- Navigate to EC2 by clicking on the Services menu available under the Compute section.
- On the left panel menu, select the security group under the Network & Security section.
- Click on the Create Security Group.
-
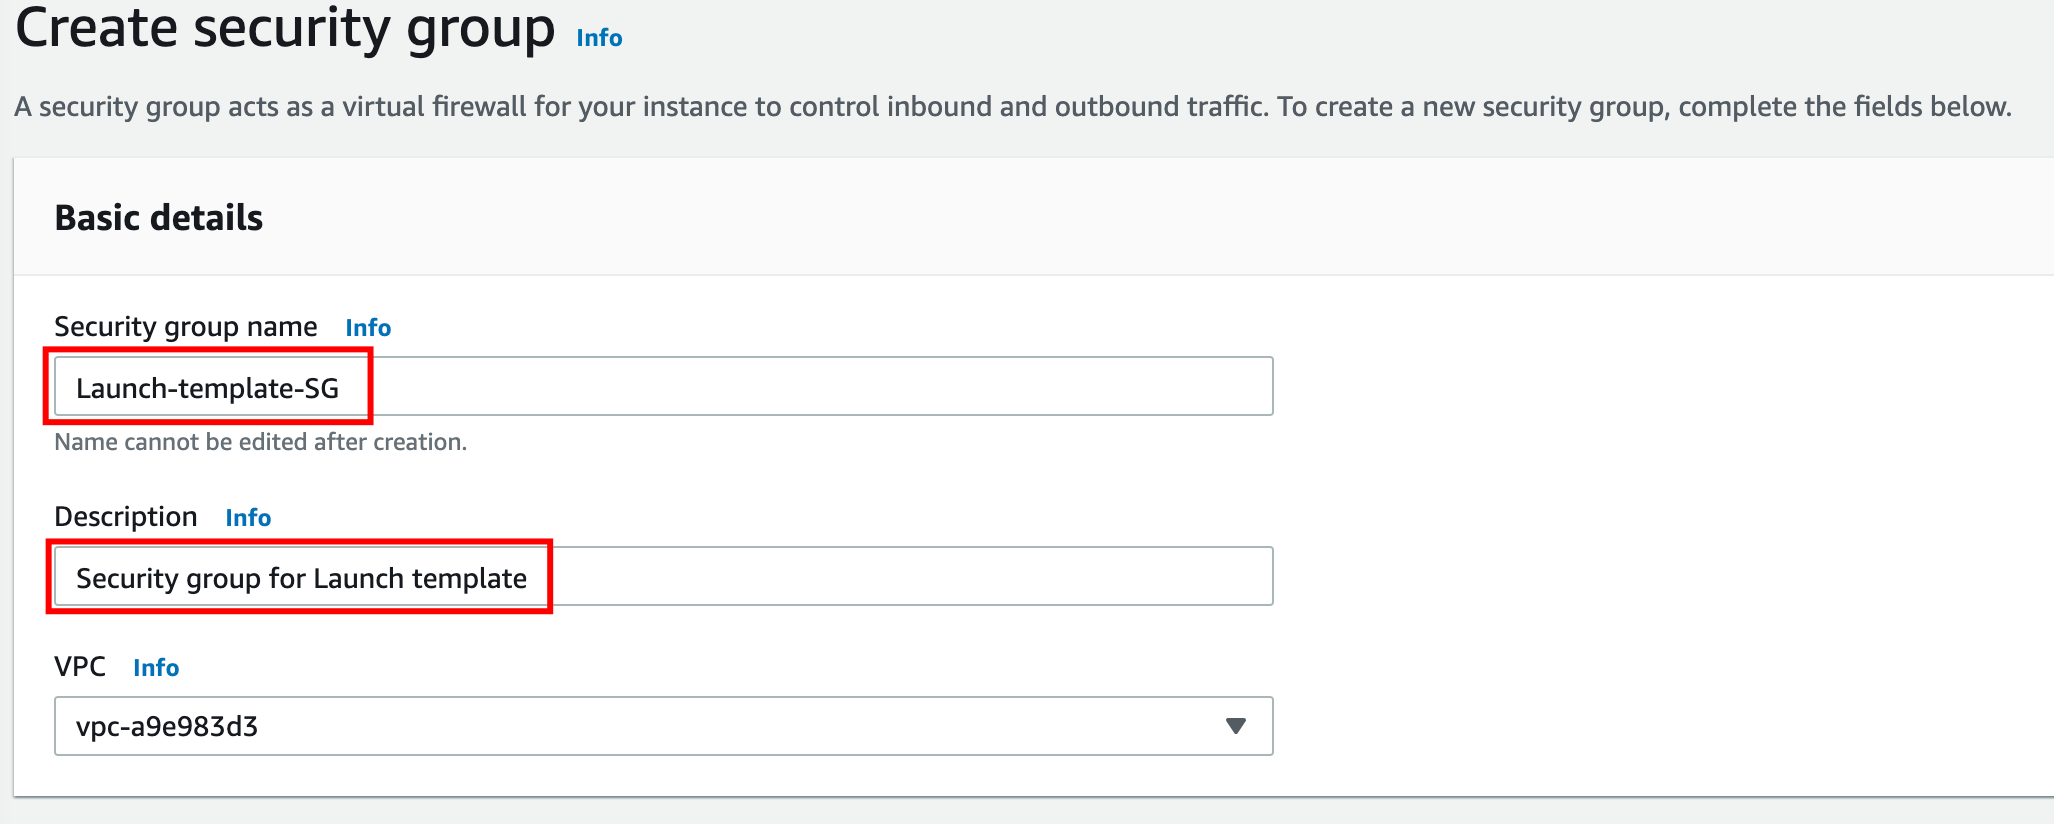
We are going to create a Security group for the Launch template with port 80 number enabled.
- Security group name: Enter Launch-template-SG
- Description: Enter Security group for Launch template
- VPC: Select Default VPC
-
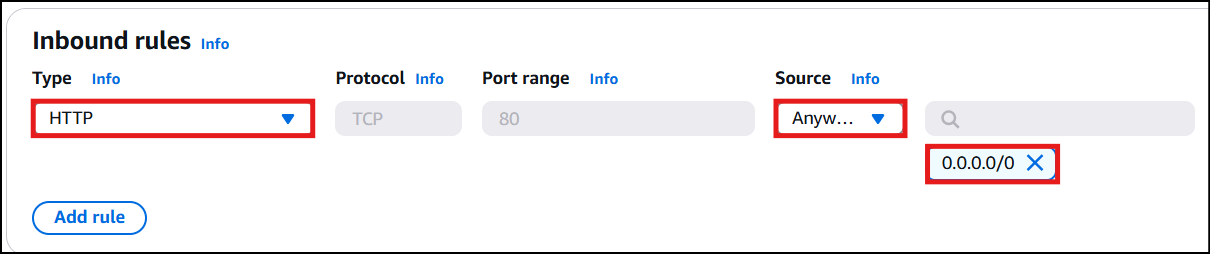
Click on the Add rule under Inbound rules.
- Type : Select HTTP
- Source : Select Anywhere-IPv4
-
In the textbox add 0.0.0.0/0
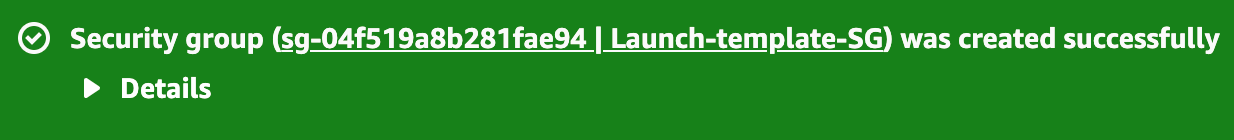
- Leave everything as default and click on the Create Security Group.
Task 3: Create a Key pair for the Launch template
- In the left navigation pane (scroll down) within Network & Security, click on the Key Pairs.
- To create a new key pair, click on the Create Key Pair.
-
Fill in the details below:
- Name: Enter WhizKeyPair
- File format: pem (Linux & Mac Users) or ppk (Windows users)
- Leave other options as default.
-
Click on the Create Key Pair.
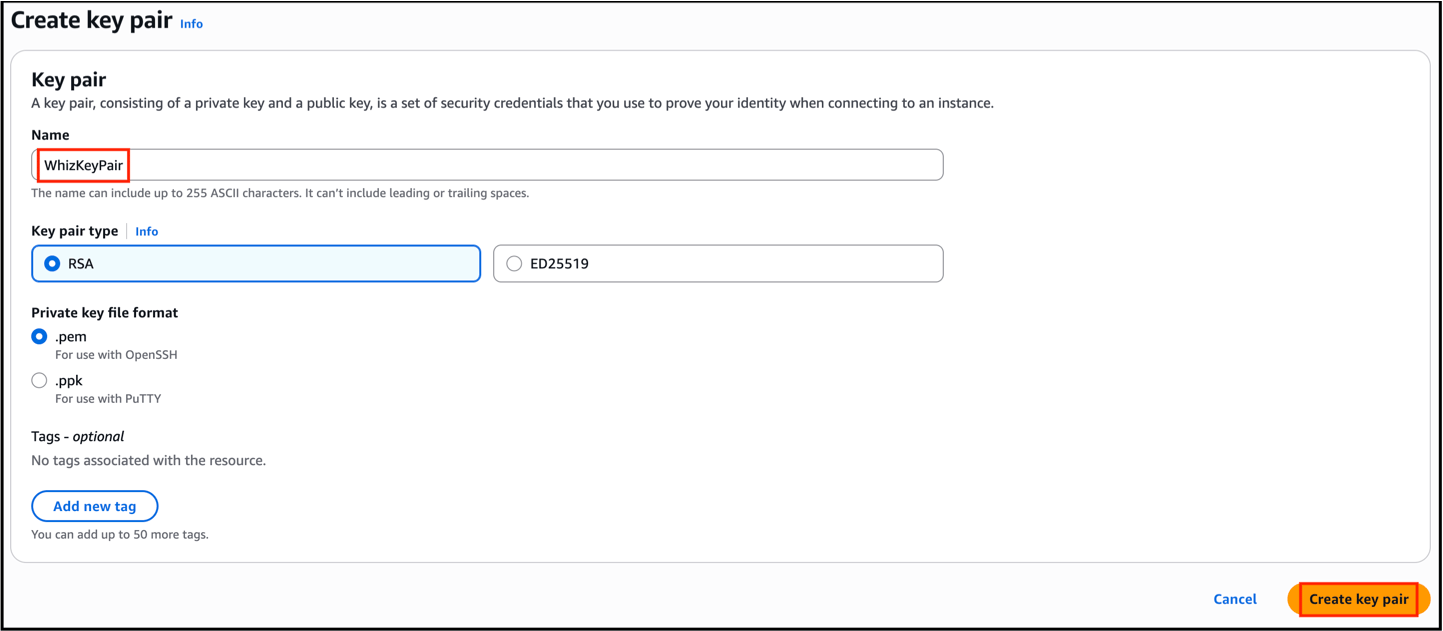
- Key pair will be created.
Task 4: Creating a Launch template
- In the left navigation pane (scroll down) within Instances, click on the Launch Templates
- Click on the Create Launch Template
-
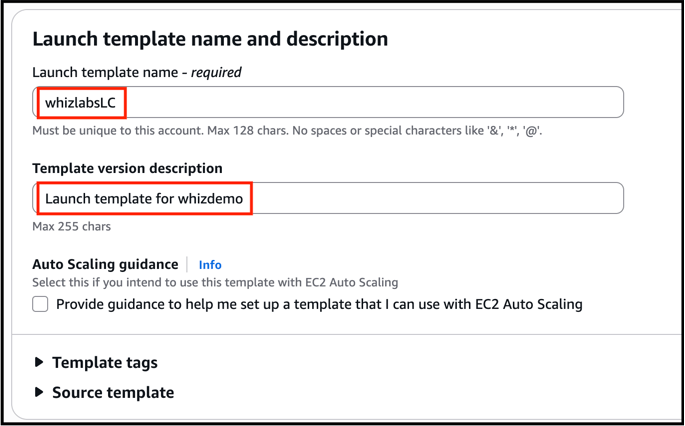
Under Launch template name and description section:
- Launch template name: Enter whizlabsLC
- Template version description: Type Launch template for whizdemo
-
Leave other options as default.
-
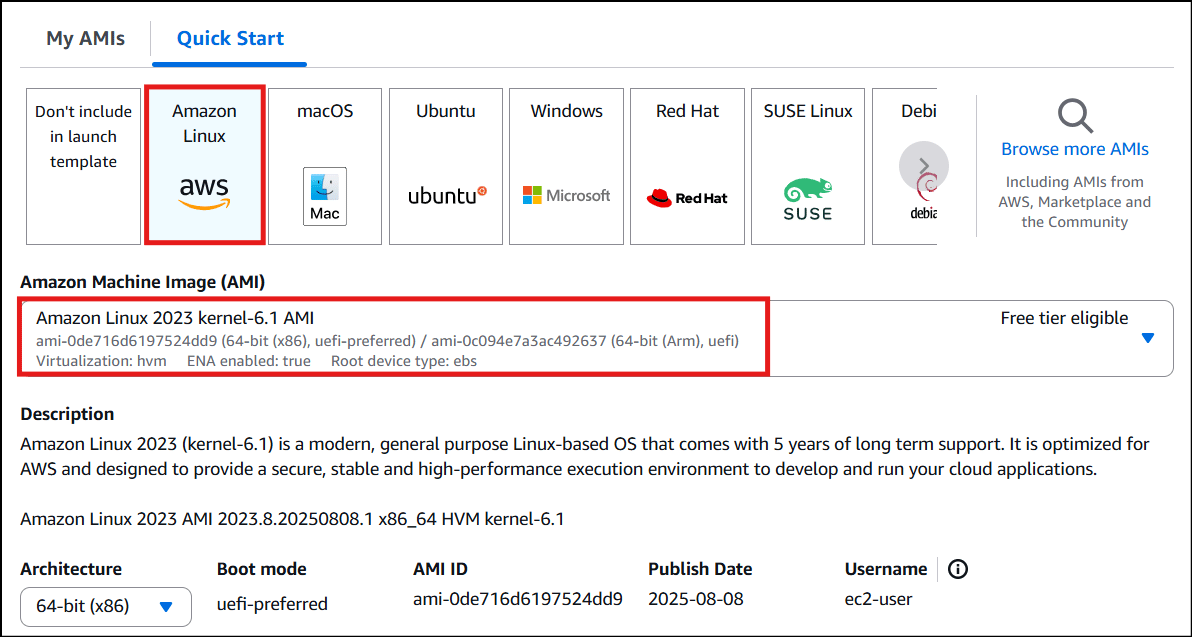
Under Launch template contents:
-
Amazon machine image (AMI): Select Amazon Linux 2023 kernel-6.1 AMI.
-
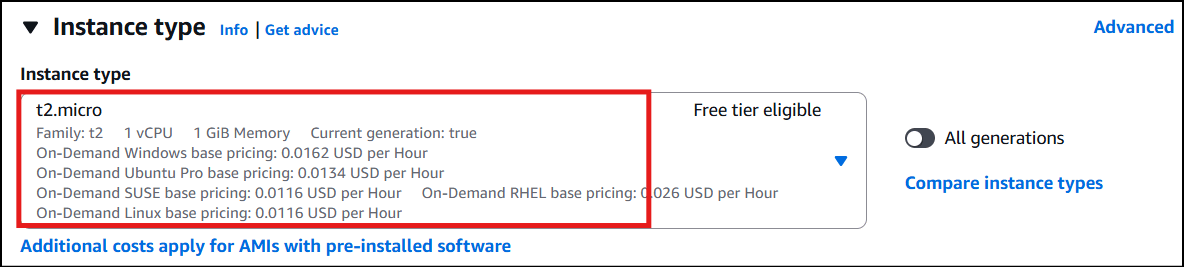
Under Instance type:
-
Select t2.micro from the below list.
-
Select t2.micro from the below list.
-
Amazon machine image (AMI): Select Amazon Linux 2023 kernel-6.1 AMI.
-
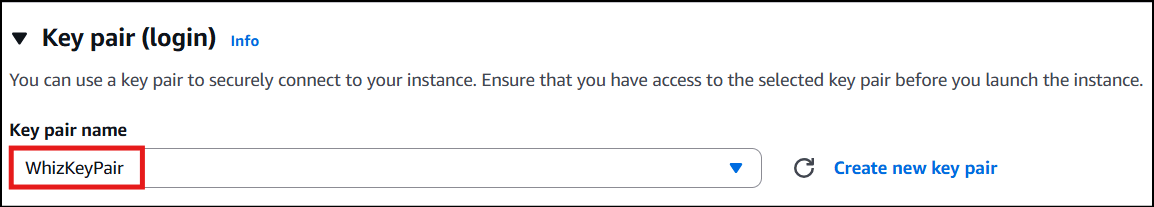
Key pair (Login): Select WhizKeyPair
-
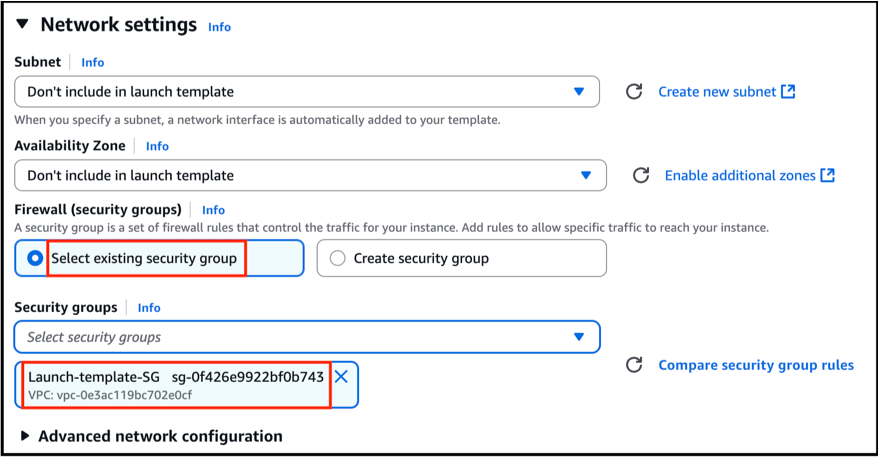
Networking settings:
- Firewall(security groups): Select Select existing security group
- Security groups: Select Launch-template-SG from the drop-down
- Leave all other options as default.
- Expand the option of Advance details, Go to the User data at the bottom of the page and paste the below script.
-
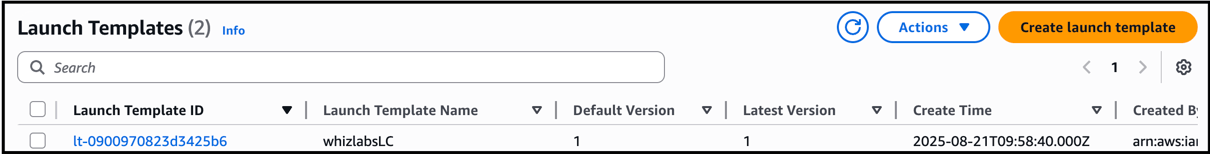
To create, click on the Create launch template. Upon successful creation, it will create a Launch template. Click on View launch templates button.
Task 5: Create an Auto Scaling Group
- An Auto Scaling group is a scalable collection of EC2 instances. When you create an Auto Scaling group, you include information such as the subnets for the instances and the number of instances the group must maintain at all times.
- Go to the left menu under EC2 and choose Auto Scaling Groups under Auto Scaling.
- Click on the Create Auto Scaling Group.
-
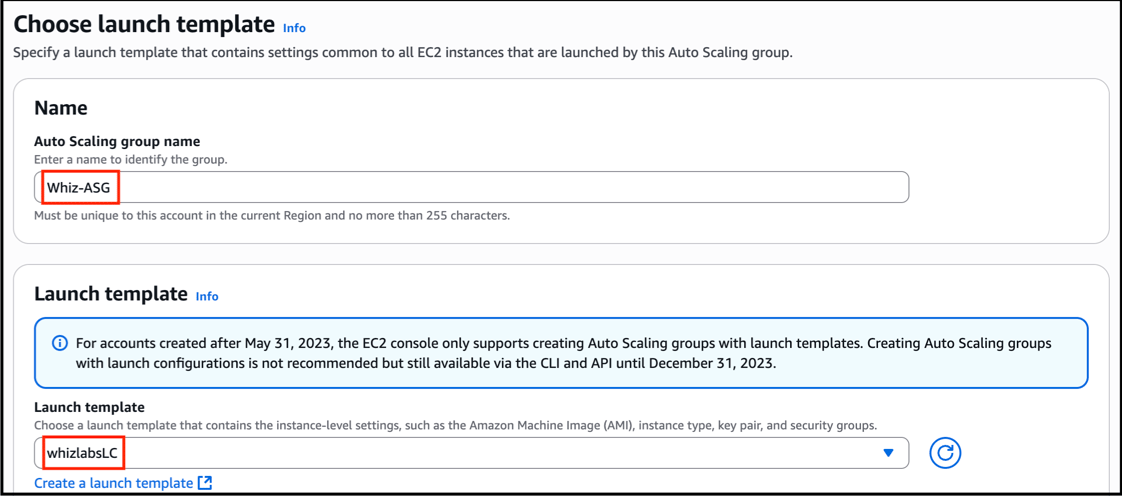
Step 1 : Choose launch template
- Auto Scaling group name : Enter Whiz-ASG
-
Select the Launch template whizlabsLC from the list. Leave everything as default and click on the Next
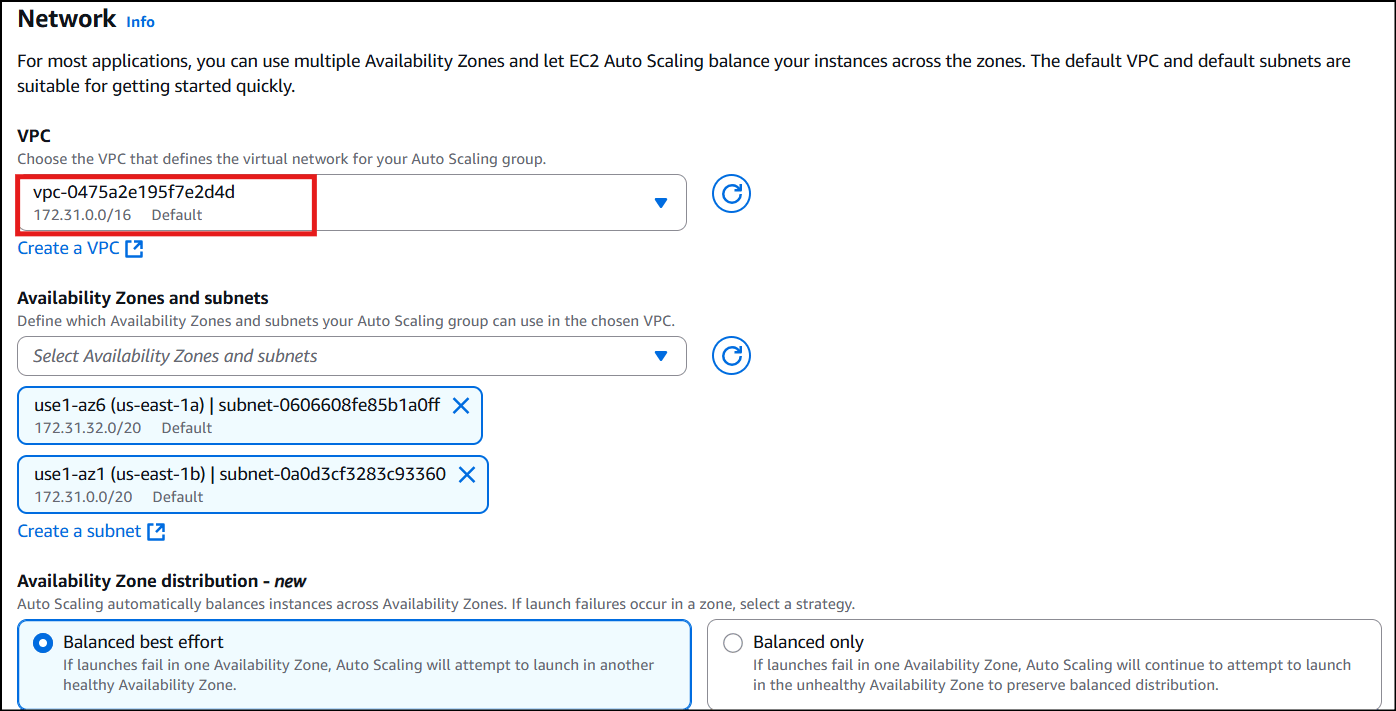
- Step 2: Choose instance launch options
- VPC: Select the Default VPC from the list.
- Subnet: Select any two subnets for your Auto Scaling instances.
-
Click on the Next
- Step 3: Integrate with other services
- No changes needed in this page, click on the Next
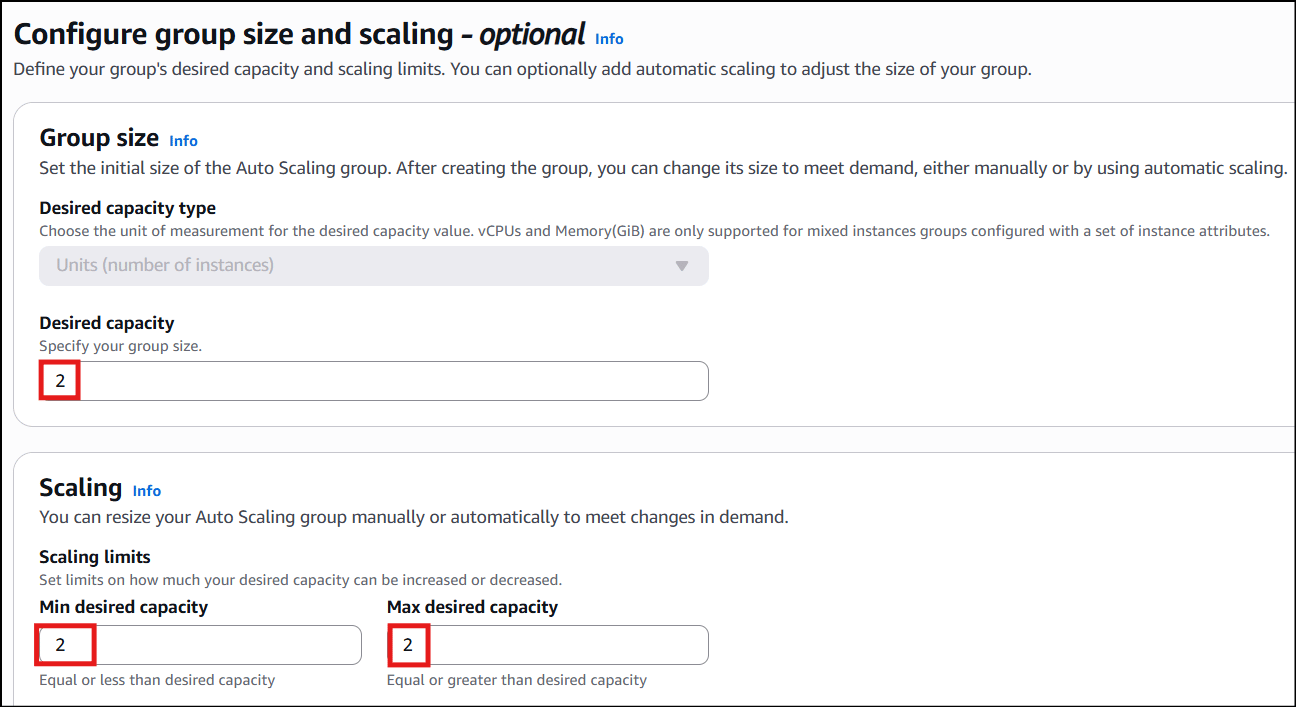
- Under Group size - optional
- Desired capacity : Enter 2
- Under Scaling:
- Minimum capacity : Enter 2
- Maximum capacity : Enter 2
-
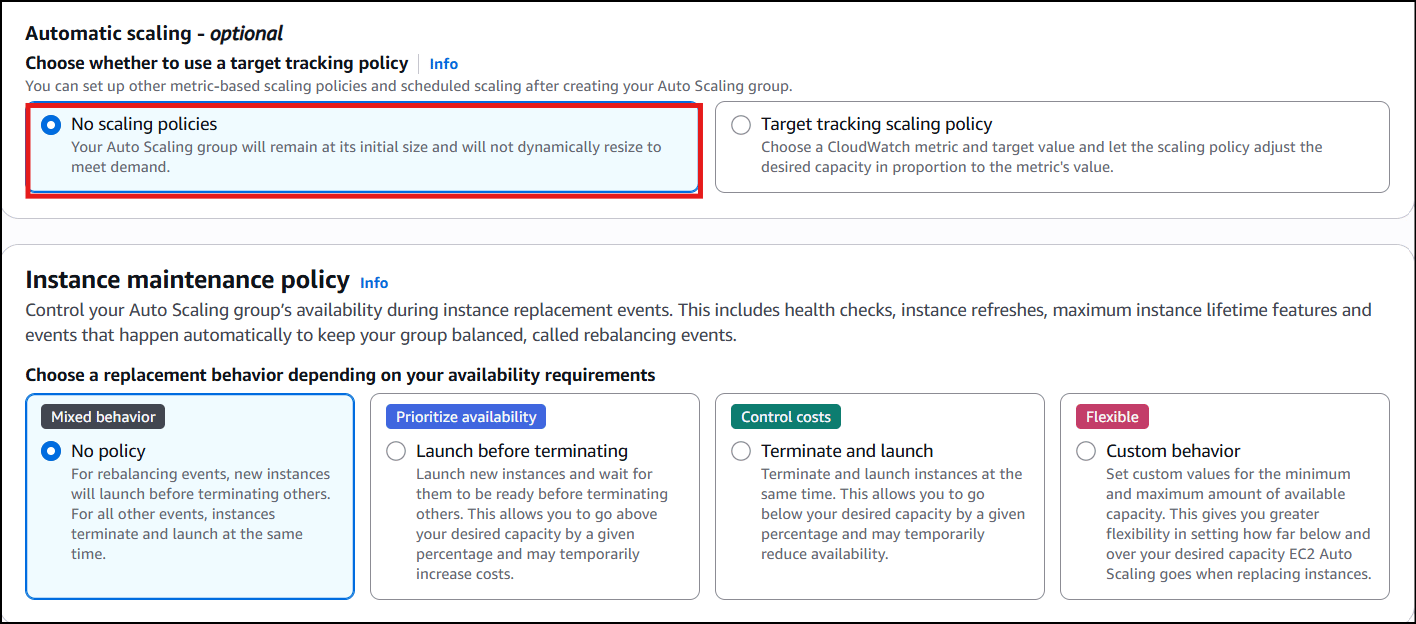
Under Automatic Scaling - optional
-
Select No scaling policies
-
Select No scaling policies
-
Under Instance scale-in protection
- No changes are needed, click on the Next
-
Step 5: Add notifications
- No changes are needed in this page, click on the Next
-
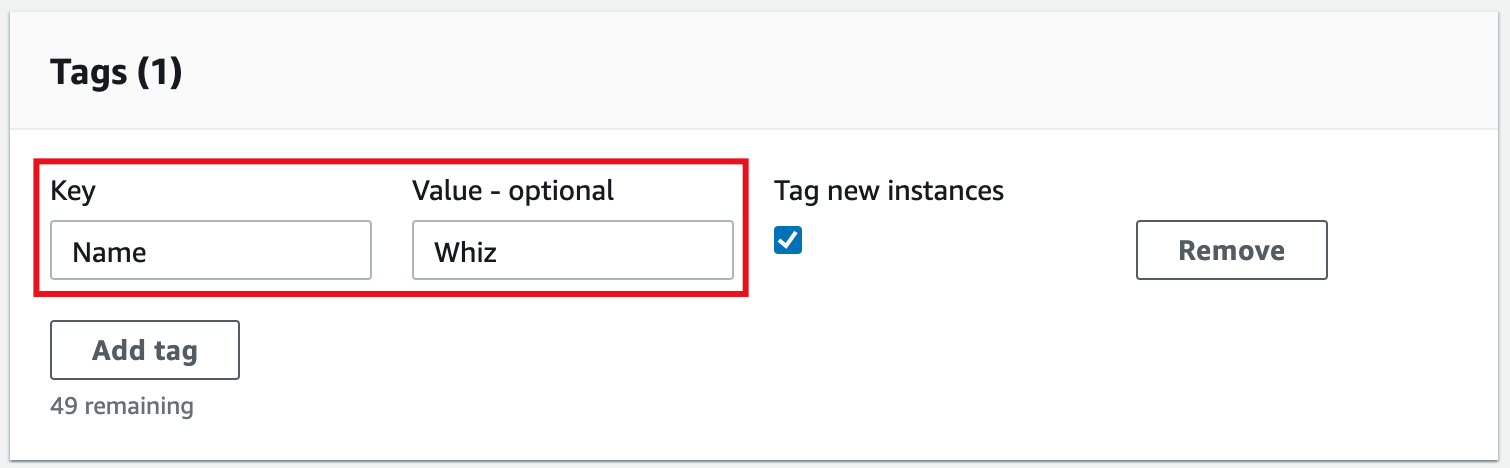
Step 6: Add tags
-
Enter tags in key-value pairs to identify your auto scaling group instances.
- Key : Enter Name
-
Value : Enter Whiz
- Click on the Next
-
Enter tags in key-value pairs to identify your auto scaling group instances.
- Now Review, scrolldown and click on the Create Auto Scaling Group.
-
You will be redirected to the autoscaling group page, you will be able to see that two instances are launched by the autoscaling groups
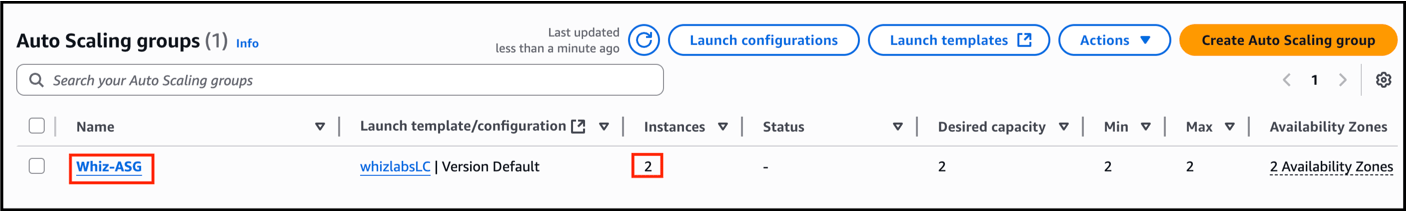
- Now go to the EC2 instances list. You will see that there are two new running instances (which were created by your autoscaling group) You can confirm this from their tag name, which you gave at the time of creating the autoscaling group.
- You have successfully created an autoscaling group with a policy to a minimum of 2 and a maximum of 2 instances.
Task 6: Test Auto Scaling Group
- For testing the auto-scaling policy, go to the EC2 instance list and select one of your instances.
-
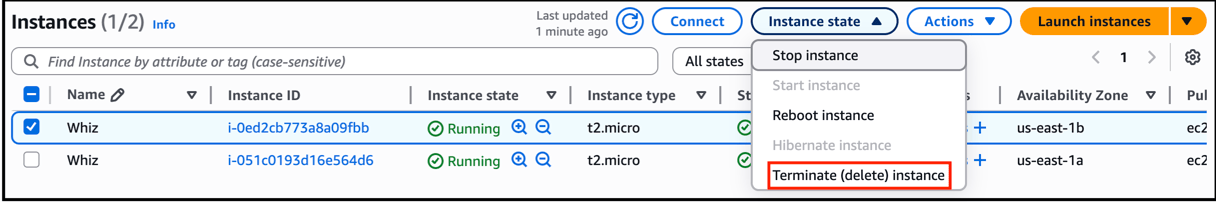
To terminate the EC2 instances manually:
- Select one of the instances randomly
- Click on the Instance state
-
Choose to terminate the instance by clicking on Terminate instance.
-
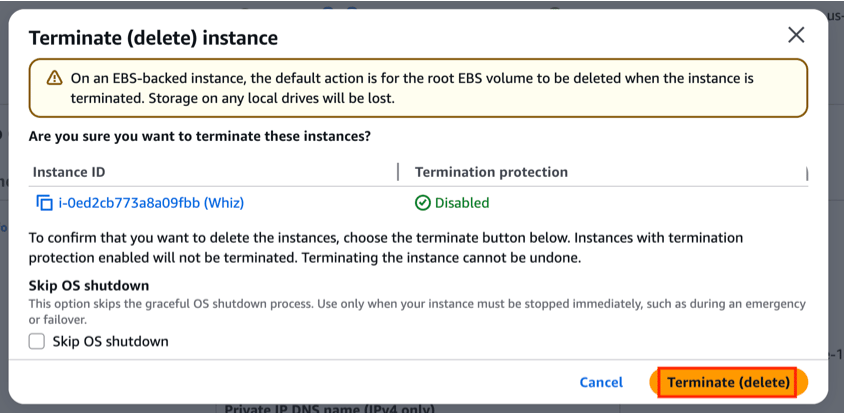
Confirm the termination by clicking on the Terminate button.
-
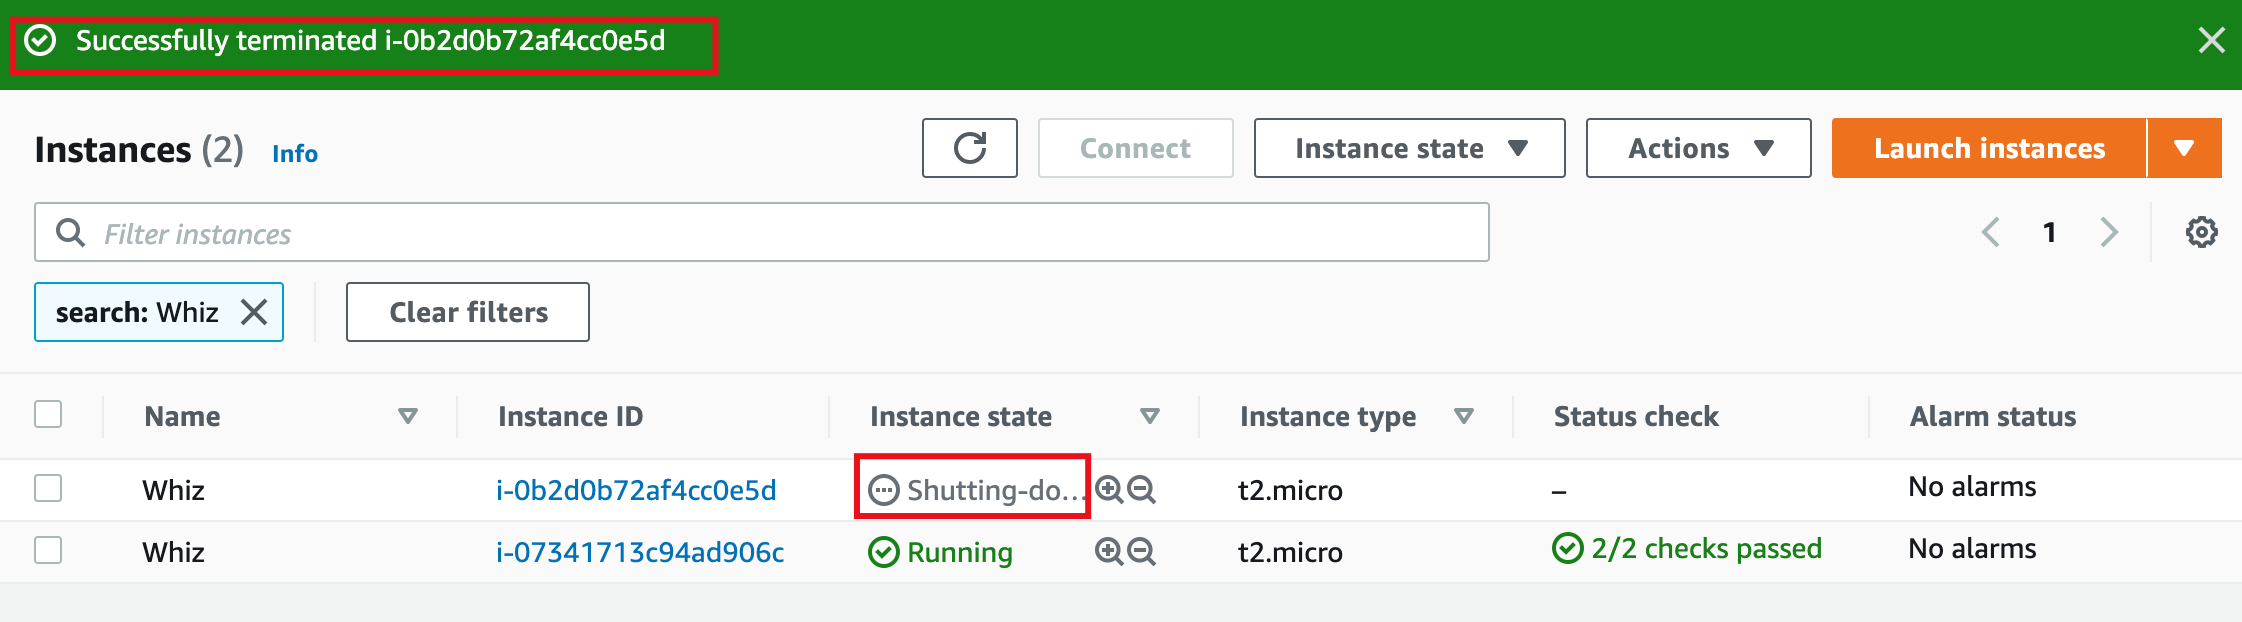
This will terminate your instance.
-
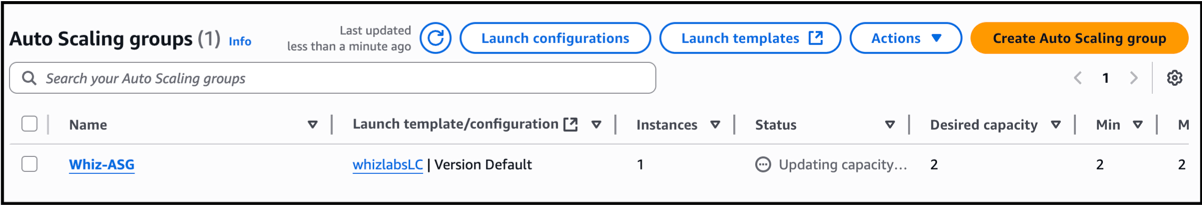
Once your instance is terminated. You can go to the Auto scaling groups page and see the Instances is 1 and the Status is Updating capacity
- Alternatively, you can look for the Activity history under Activity of your Auto scaling group to see what happened.
-
Meanwhile, A new instance will be launched to fulfill the policy condition.
A sample screenshot is provided below:
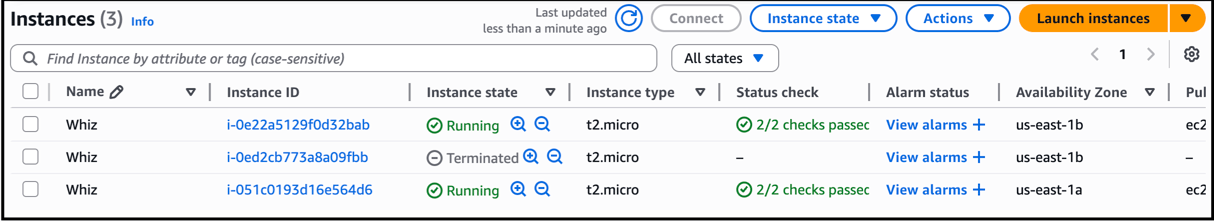
Note: Launching a new instance may take up to 5 minutes, you can refresh the page to view the new instance.
Do you Know ? Launch templates support versioning, allowing you to create and manage multiple versions of a template. This enables you to easily roll back to previous configurations or test new settings without impacting existing Auto Scaling groups.
-
Once the lab steps are completed, please click on the Validation button on the left side panel.
Completion and Conclusion
- You have created a security group and key pair for the Launch template.
- You created a Launch template and Auto Scaling.
- You have launched two EC2 instances through Auto scaling.
- You have tested the Auto scaling by terminating one of the instances manually.
End Lab
- Sign out of the AWS Account
- You have successfully completed the lab.
- Once you have completed the steps, click on End Lab from the IP Lab Portal dashboard.
What gets checked
When you press Check my work, the platform verifies each of these:- Launch an EC2 Instance — Check whether an EC2 Instance is launched or not.
- Create Amazon EC2 Auto Scaling Group — Check whether an Auto Scaling Group is created or not.
- Create Amazon EC2 Launch Template — Check whether an EC2 Launch Template is created or not.