

Overview
Project Details
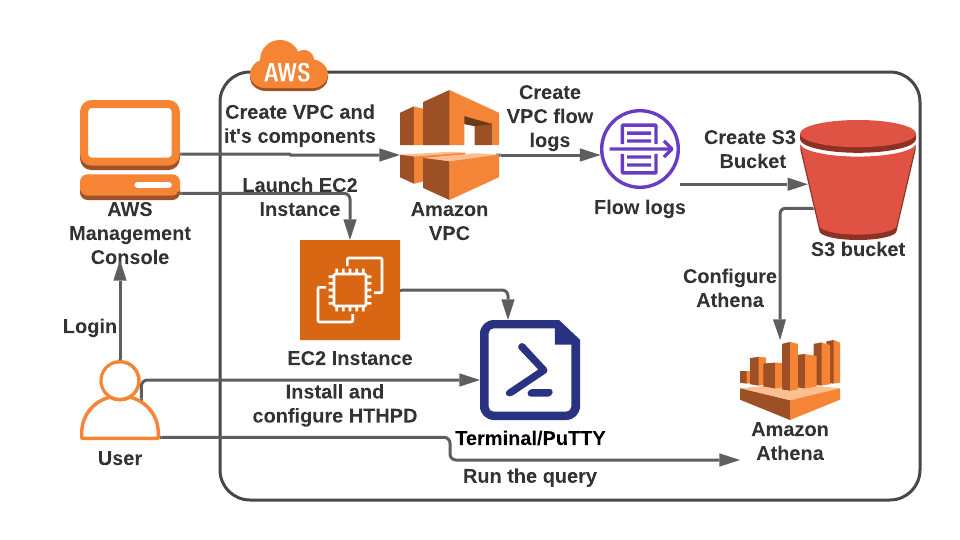
- This project walks you through the steps to create S3 Bucket, VPC with its components, and VPC flow logs.
- You will practice using EC2 Instance by running the commands to install HTTPD to generate traffic. You will also, send the logs to the S3 bucket and query them using Amazon Athena.
- Duration: 1 hour
- AWS Region: US East (N. Virginia) us-east-1
Architecture Diagram
Task Details
- Sign into the AWS Management Console
- Create S3 Bucket and add a bucket policy
- Create a VPC
- Create and attach an Internet Gateway with custom VPC
- Create a Public Subnet
- Configure the Public subnet to enable auto-assign public IPv4 addresses
- Create a Public Route Table
- Create a VPC Flow log
- Launching an EC2 Instance to generate traffic
- SSH into EC2 Instance
- Generate logs that will be sent to S3 Bucket
- Setup Amazon Athena to query the log data
- Run SQL query against the table
Launching Project Environment
- To launch the project environment, Click on the Start Project button.
- Please wait until the cloud environment is provisioned. It will take less than a minute to provision.
- Once the project is started, you will be provided with IAM user name, Password, Access Key, and Secret Access Key.
Note : You can only start one project at any given time
Lab guide
Project Steps
Task 1: Sign in to AWS Management Console
- Click on the Open Console button, and you will get redirected to AWS Console in a new browser tab.
-
On the AWS sign-in page,
- Leave the Account ID as default. Never edit/remove the 12 digit Account ID present in the AWS Console. otherwise, you cannot proceed with the project.
- Now copy your User Name and Password in the Project Console to the IAM Username and Password in AWS Console and click on the Sign in button.
- Once Signed In to the AWS Management Console, Make the default AWS Region as US East (N. Virginia) us-east-1.
Task 2: Create S3 Bucket and add a bucket policy
- Make sure you are in US East (N. Virginia) us-east-1 Region.
- Navigate to S3 by clicking on the Services menu in the top, then click on S3 in the Storage section.
-
On the S3 Page, click on Create Bucket and fill in the bucket details.
-
Bucket name: Enter athena-whizlabs
- Note: S3 bucket name is globally unique, choose a name that is available.
- Region: Select US East (N. Virginia) us-east-1
-
Uncheck the option**, Block all public access,** and check the acknowledge option.
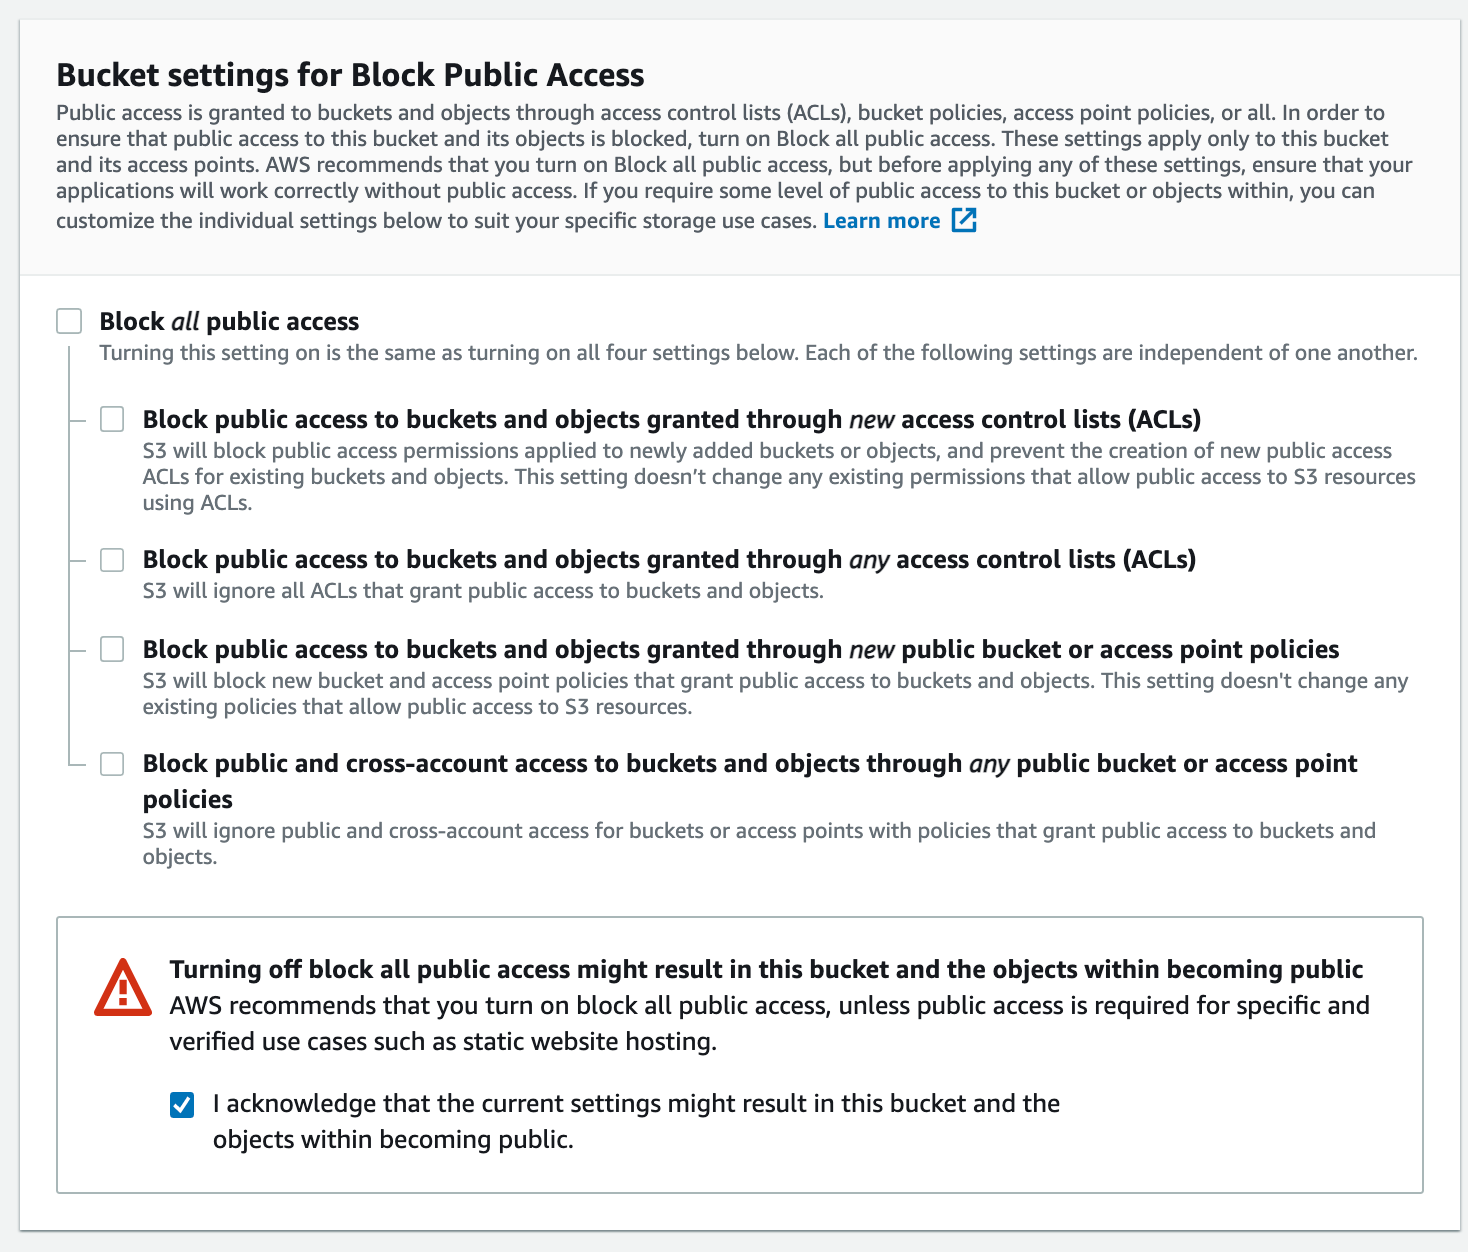
- Leave other settings as default.
- Click on Create Bucket.
-
Bucket name: Enter athena-whizlabs
-
The S3 bucket is created.
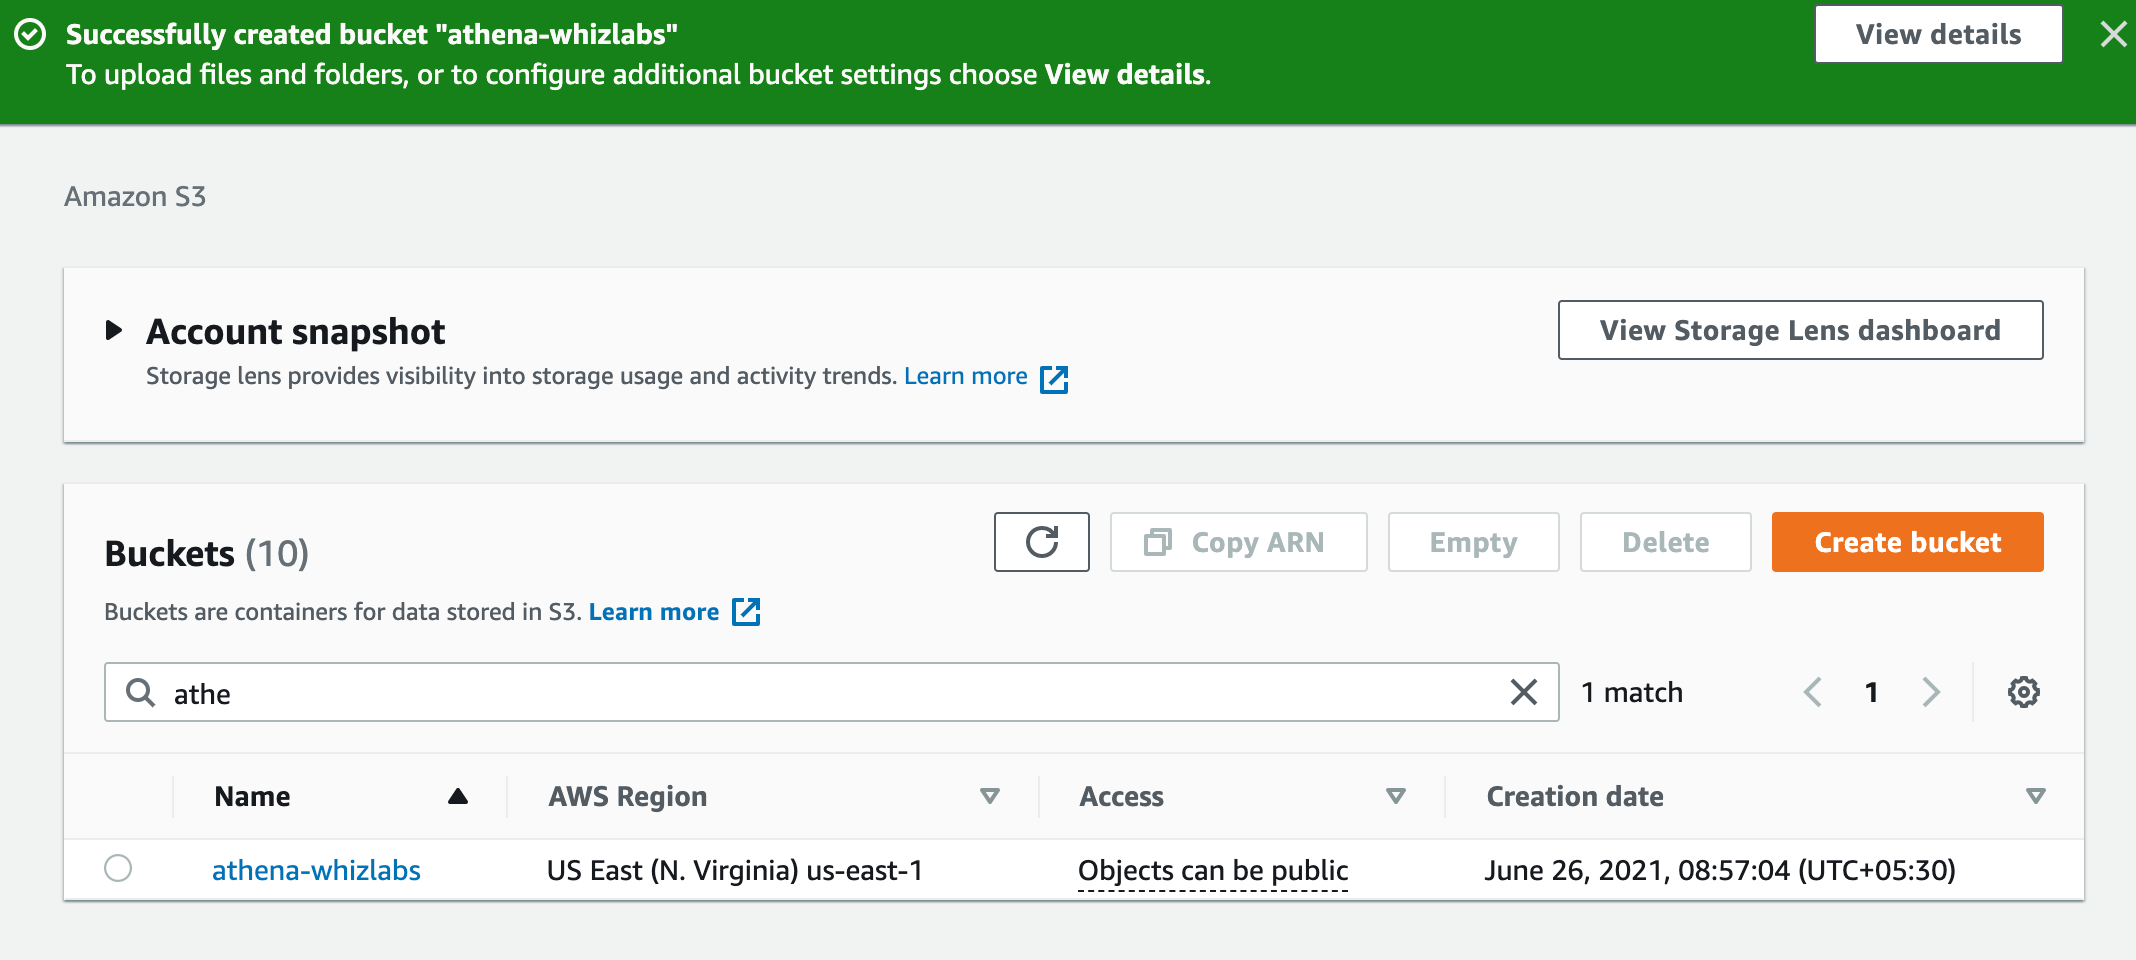
-
Select the Bucket and click on the Copy ARN Button, save it to notepad. You will need this for future steps.
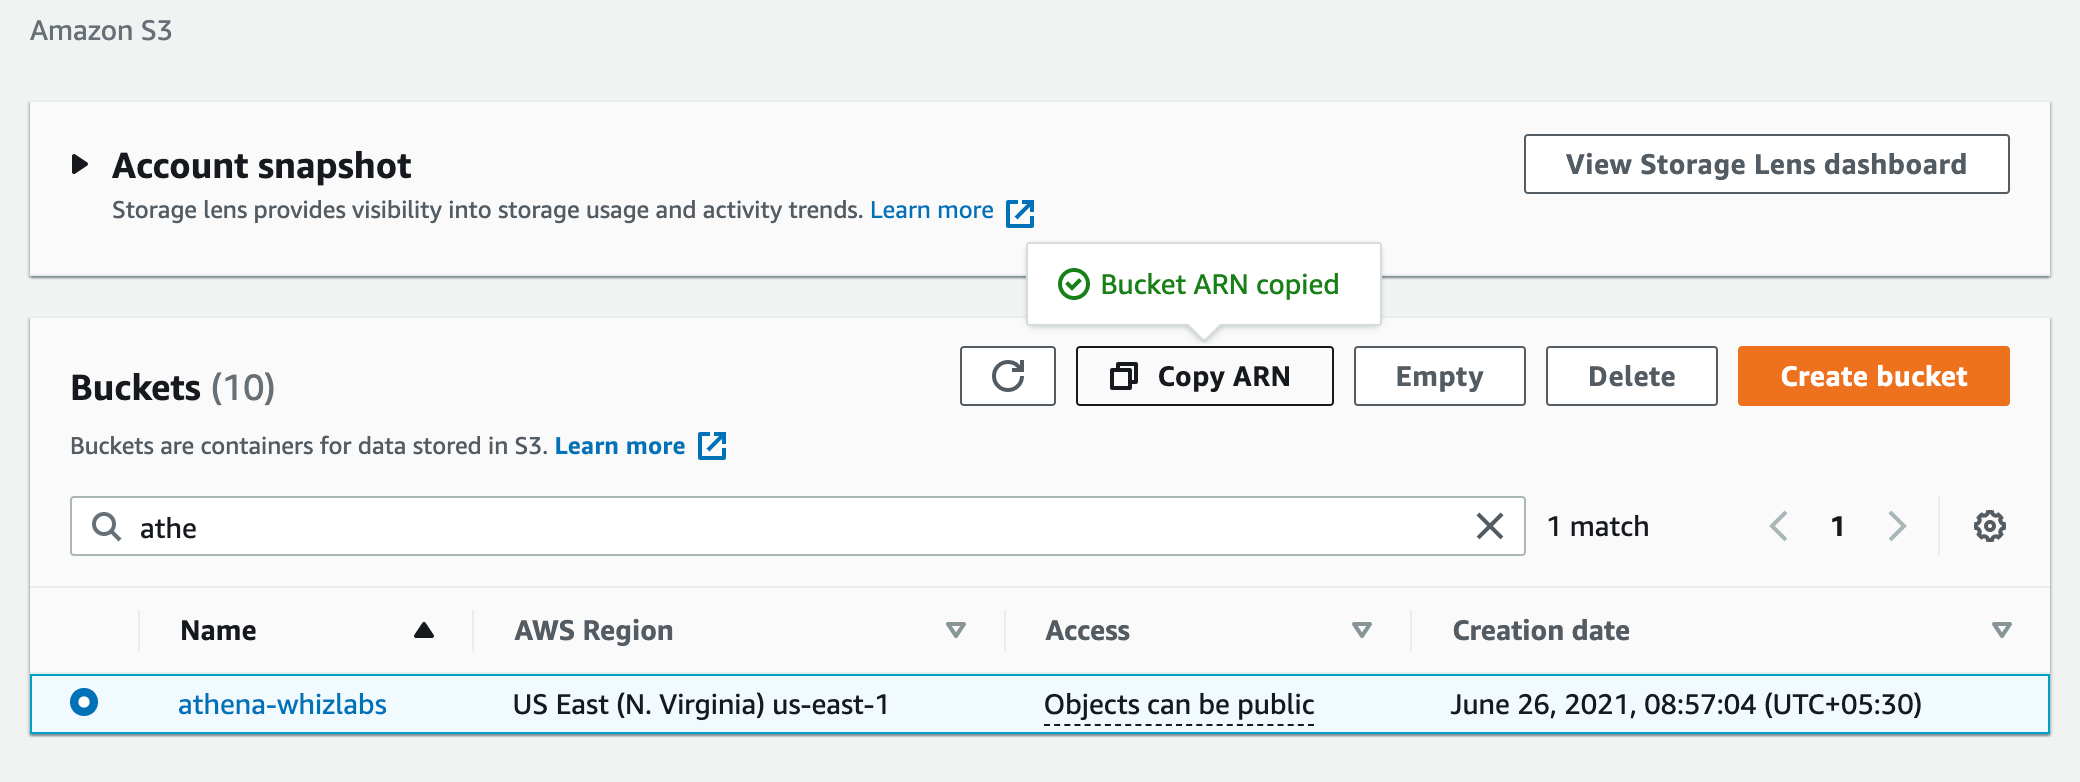
- Modify the S3 Bucket policy to allow incoming logs from VPC flow logs.
- Click on the Bucket name and switch to the Permissions tab.
- Scroll to the Bucket policy section and click on the Edit button.
- Paste the below policy. and replace the bucket ARN in the Resource section below and click on Save changes button.
Task 3: Create a VPC
- Make sure you are in US East (N. Virginia) us-east-1 Region.
- Navigate to VPC by clicking on the Services menu at the top, then click on VPC in the Networking & Content Delivery section.
- To create a VPC click on Your VPCs the present in the VIRTUAL PRIVATE CLOUD section on the left sidebar.
-
Create a new VPC by clicking on the Create VPC.
- Select VPC only
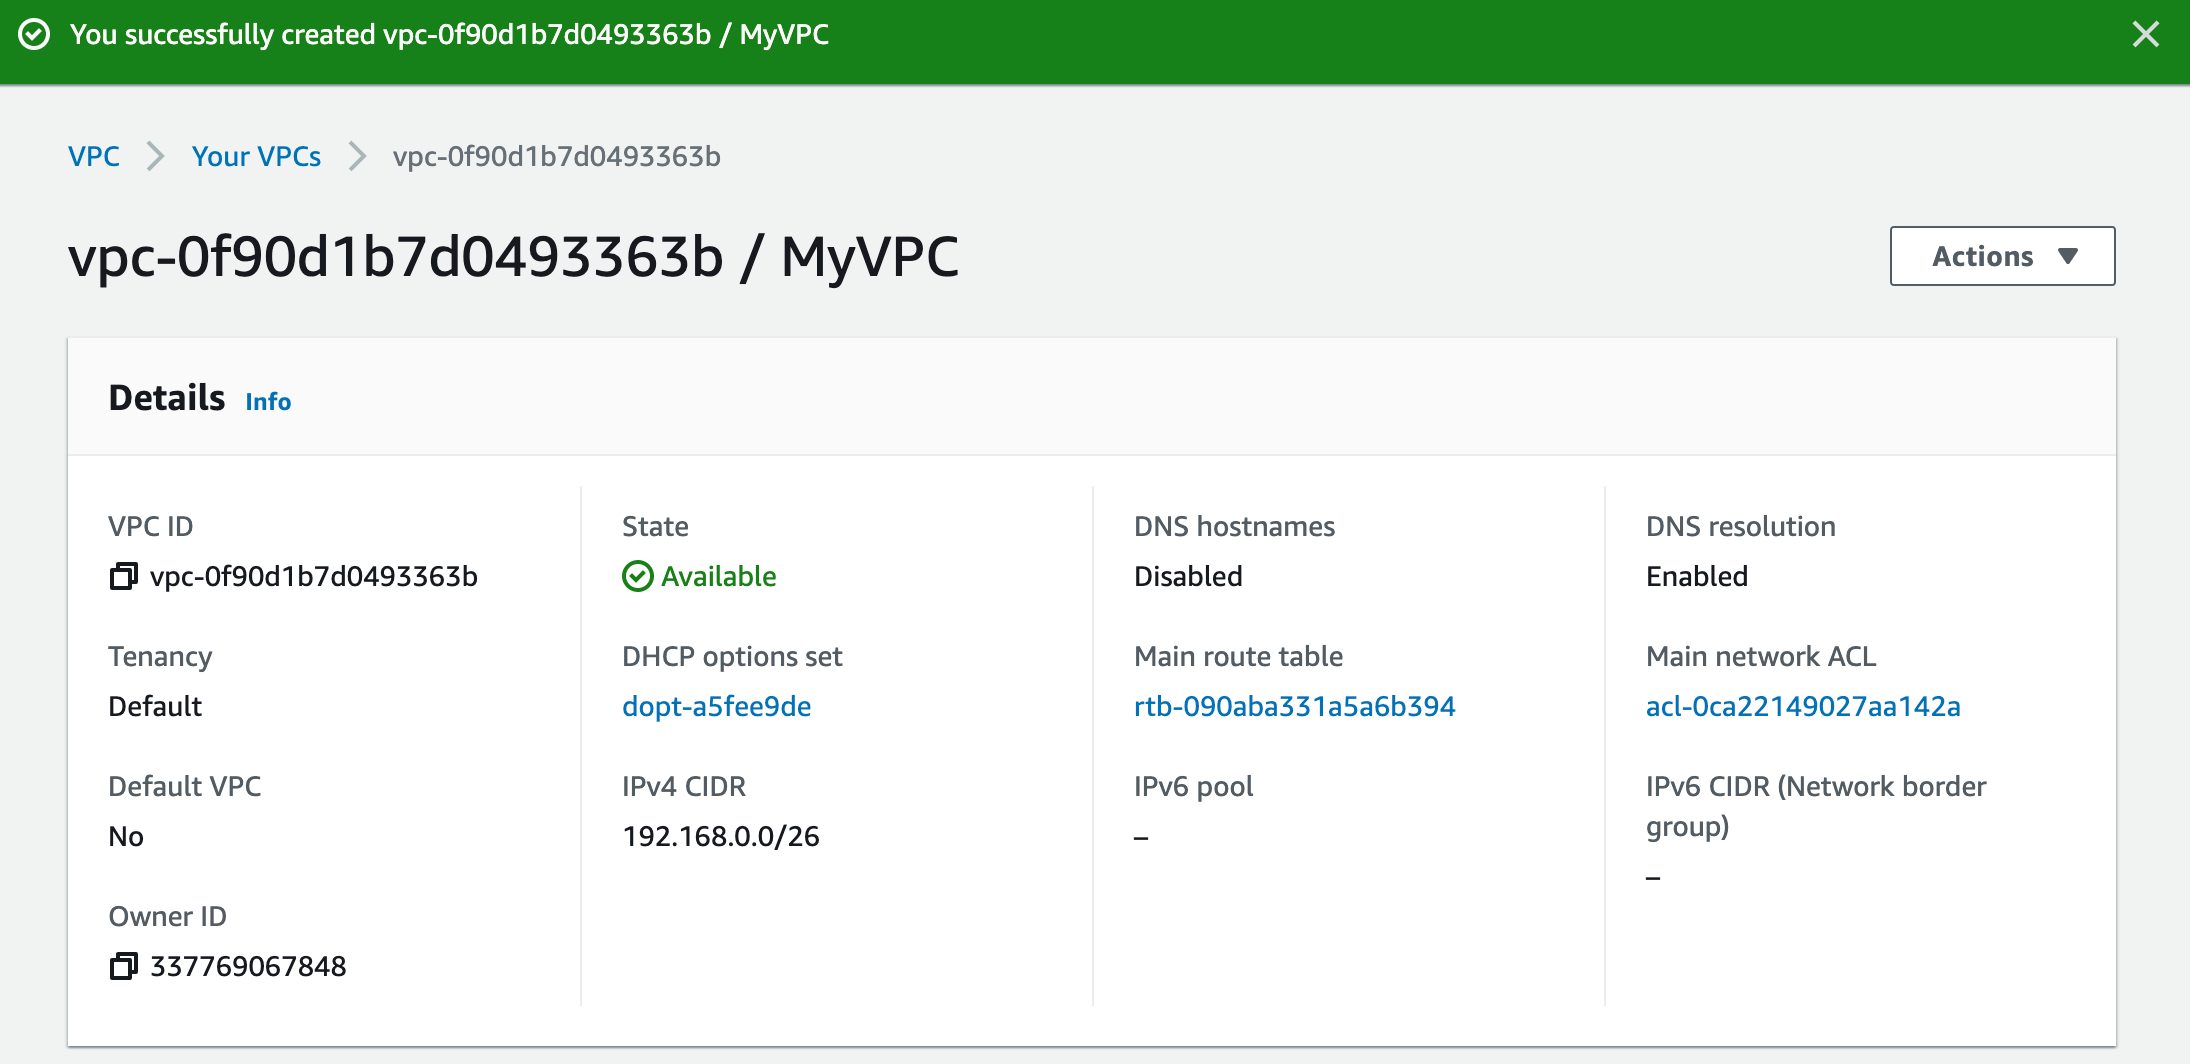
- Name tag - optional_:_ Enter MyVPC
- IPv4 CIDR block: Enter 192.168.0.0/26
- IPv6 CIDR block: Select No IPv6 CIDR block
- Tenancy: Default
- Click on the Create VPC button to create the MyVPC.
- VPC is now created.
Task 4: Create and attach an Internet Gateway with custom VPC
- By default, instances that are launched in a VPC cannot communicate with the Internet. To enable Internet access, an Internet gateway needed to be attached to the VPC.
-
Click on Internet Gateways from the left menu and click Create Internet Gateway.
- Name Tag : Enter MyInternetGateway
- Click on Create Internet Gateway.
-
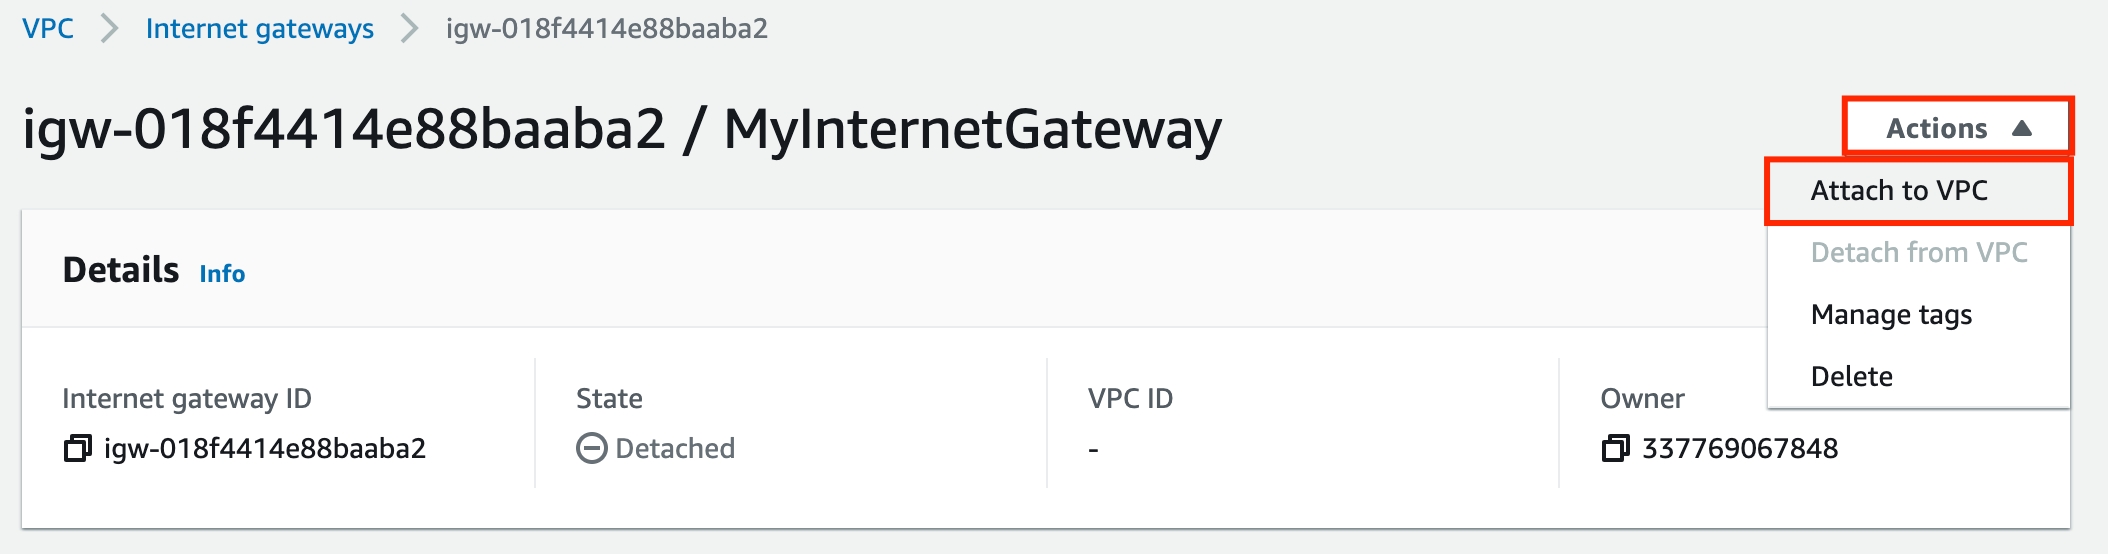
Select the Internet gateway you created from the list.
- Click on Actions.
-
Select Attach to VPC.
-
Available VPCs: Select MyVPC
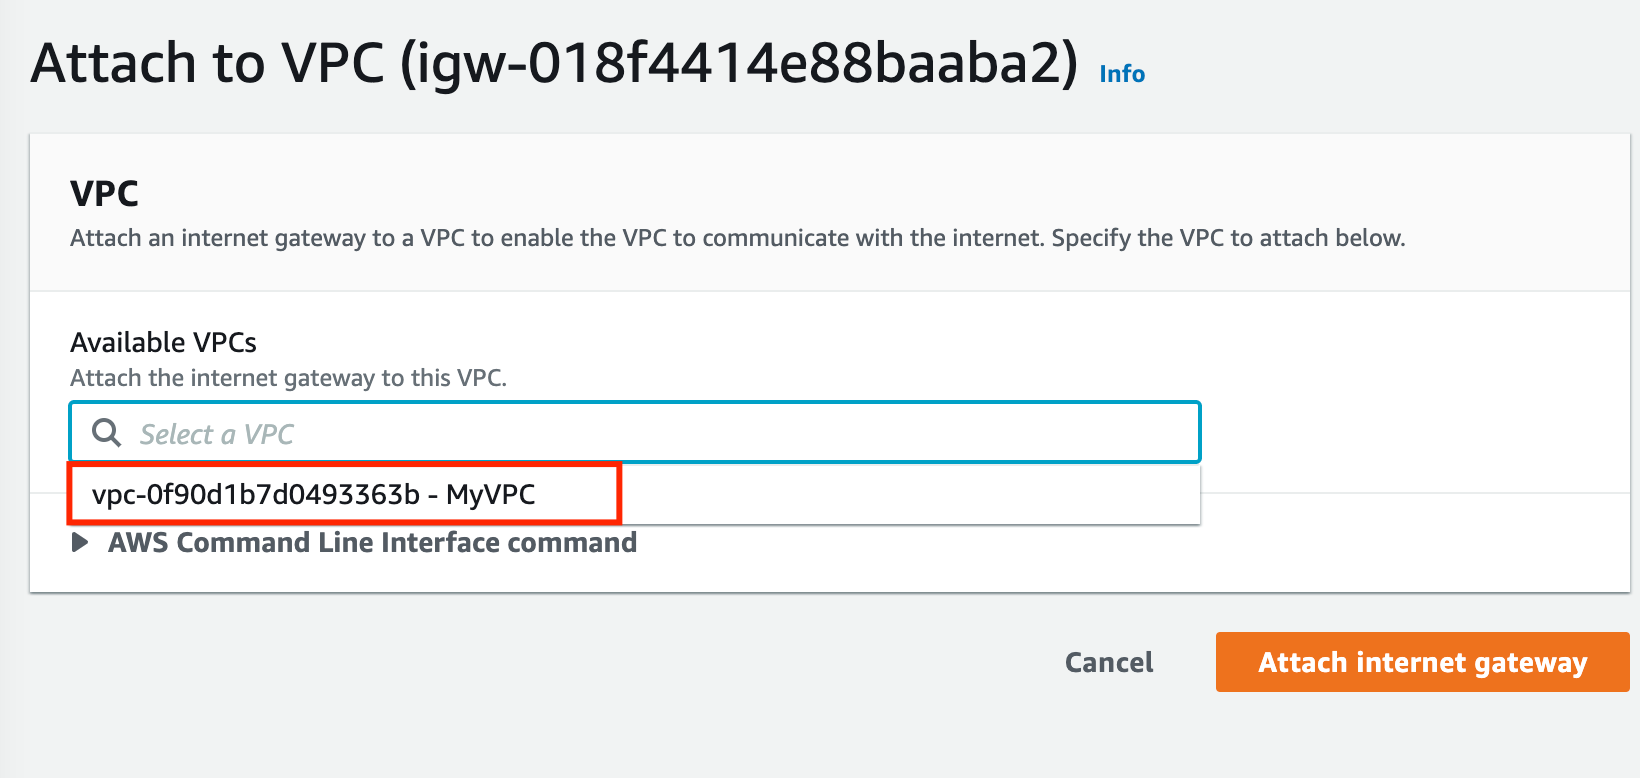
- And click on the Attach internet gateway button.
-
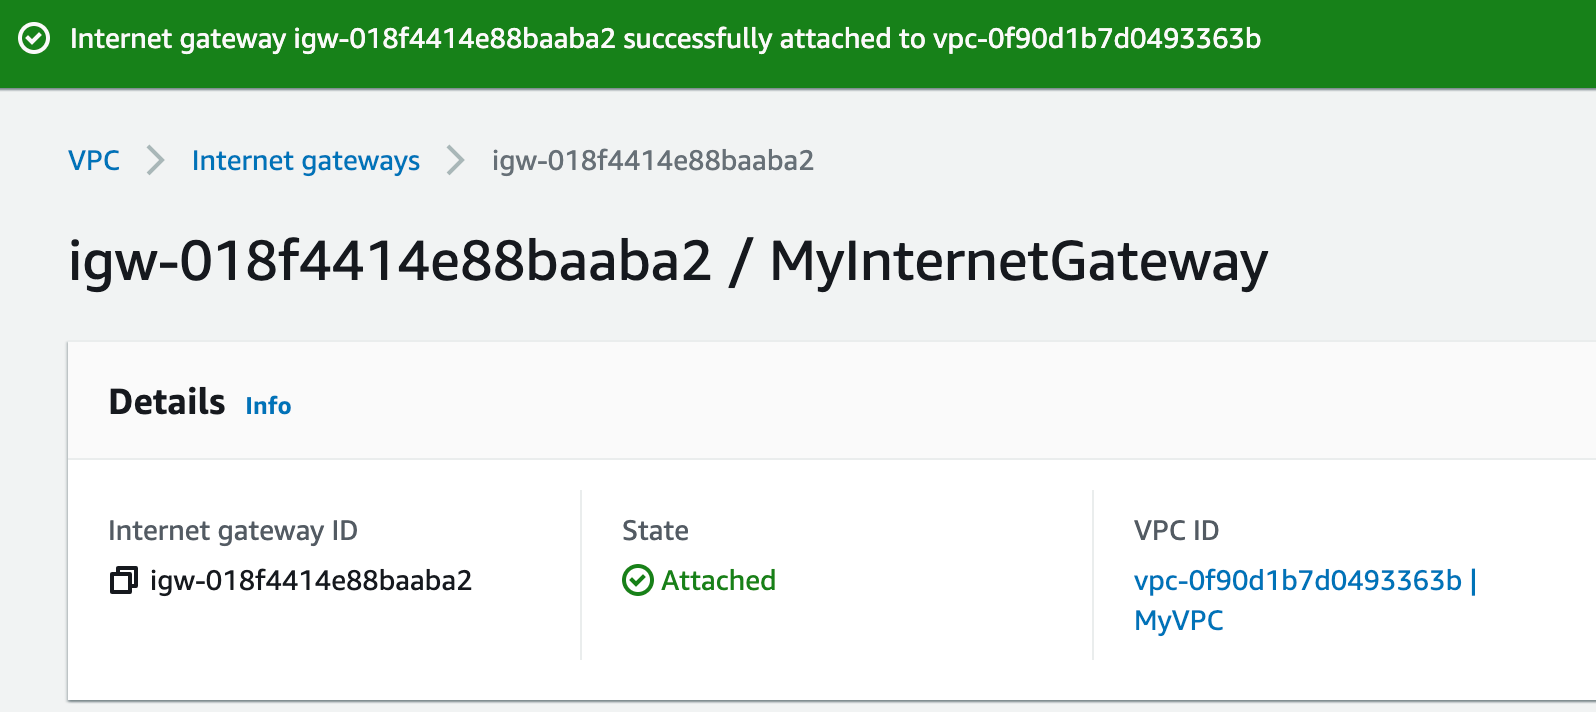
The Internet gateway is now attached with MyVPC.
Task 5: Create a Public Subnet
- To create a subnet click on Subnets the present in the VIRTUAL PRIVATE CLOUD section on the left sidebar.
- Click on the Create Subnet.
-
In the VPC ID, select the MyVPC.
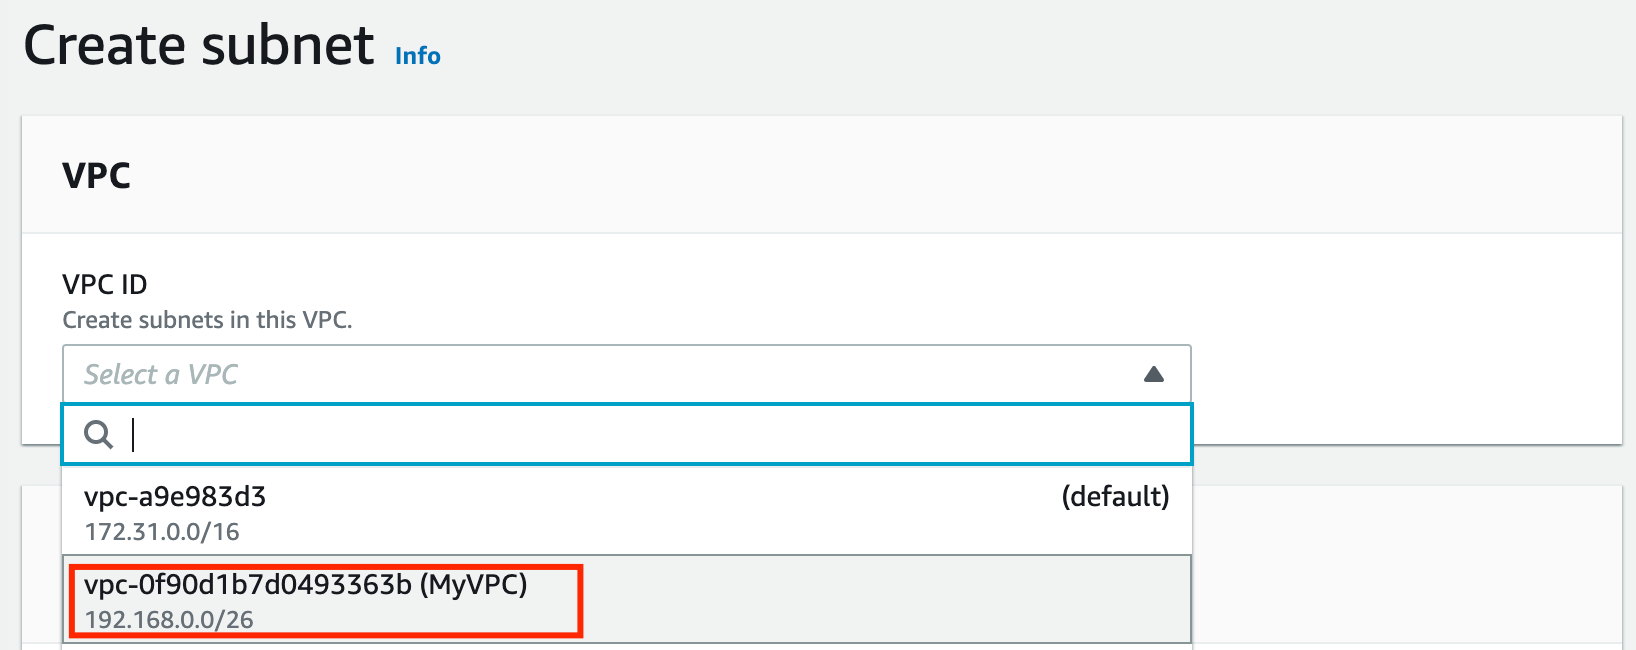
-
Create the first subnet, you will use this subnet to launch public instances, this subnet will be associated with the main route table of the VPC:
- Subnet name: Enter Public subnet
- Availability Zone: Select US East (N. Virginia) / us-east-1a
- IPV4 CIDR block: Enter 192.168.0.1/27
- Finally, click on the Create Subnet to create a subnet.
- A subnet is now created.
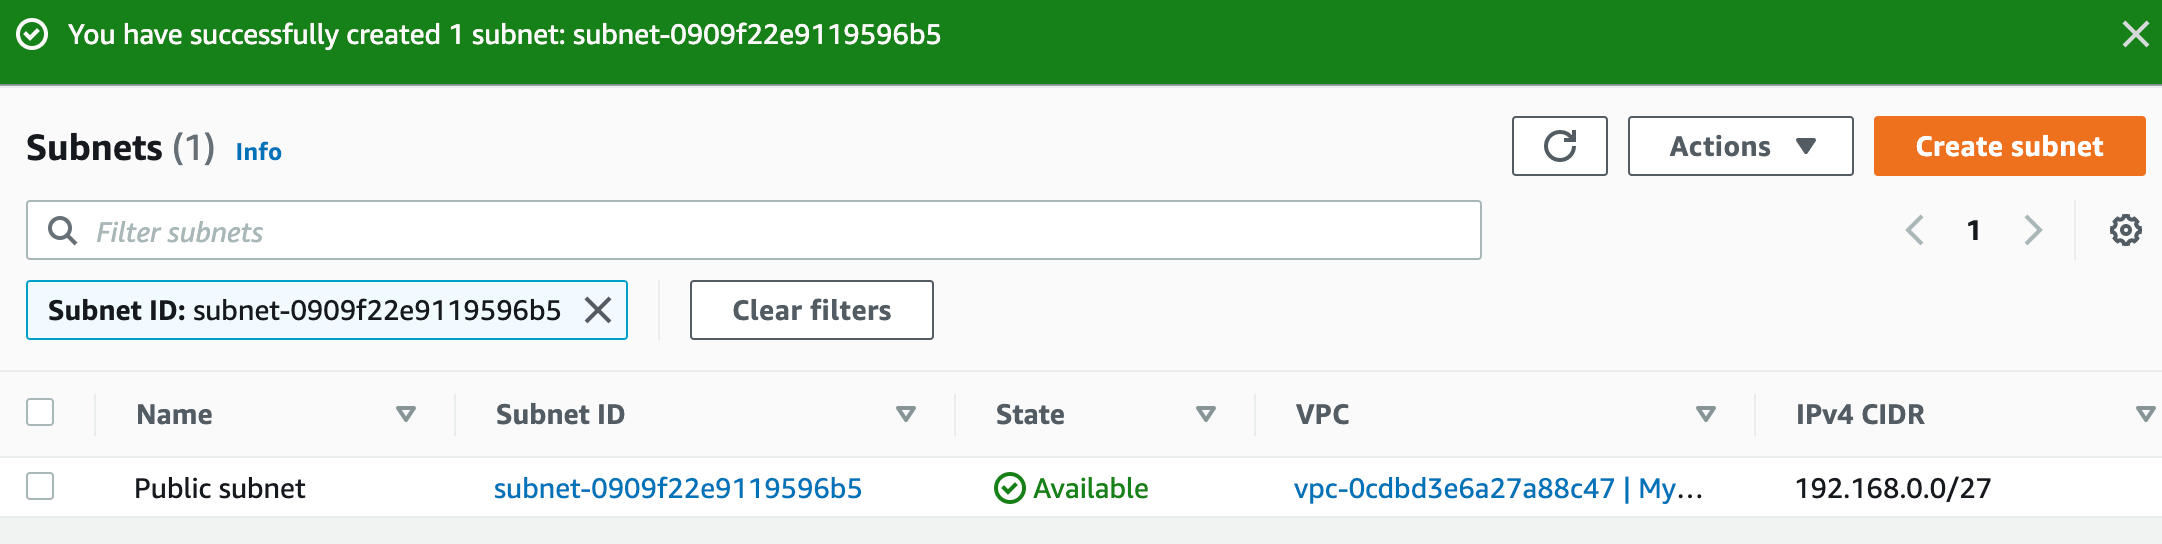
Task 6: Configure the Public subnet to enable auto-assign public IPv4 address
-
To modify the auto-assign IP settings for the Public subnet, do the following:
- Select the Public subnet
- Click on the Actions button
- Choose Edit subnet settings from the options.
-
Check the option Enable auto-assign public IPv4 address under Auto-assign IP settings and click on Save button.
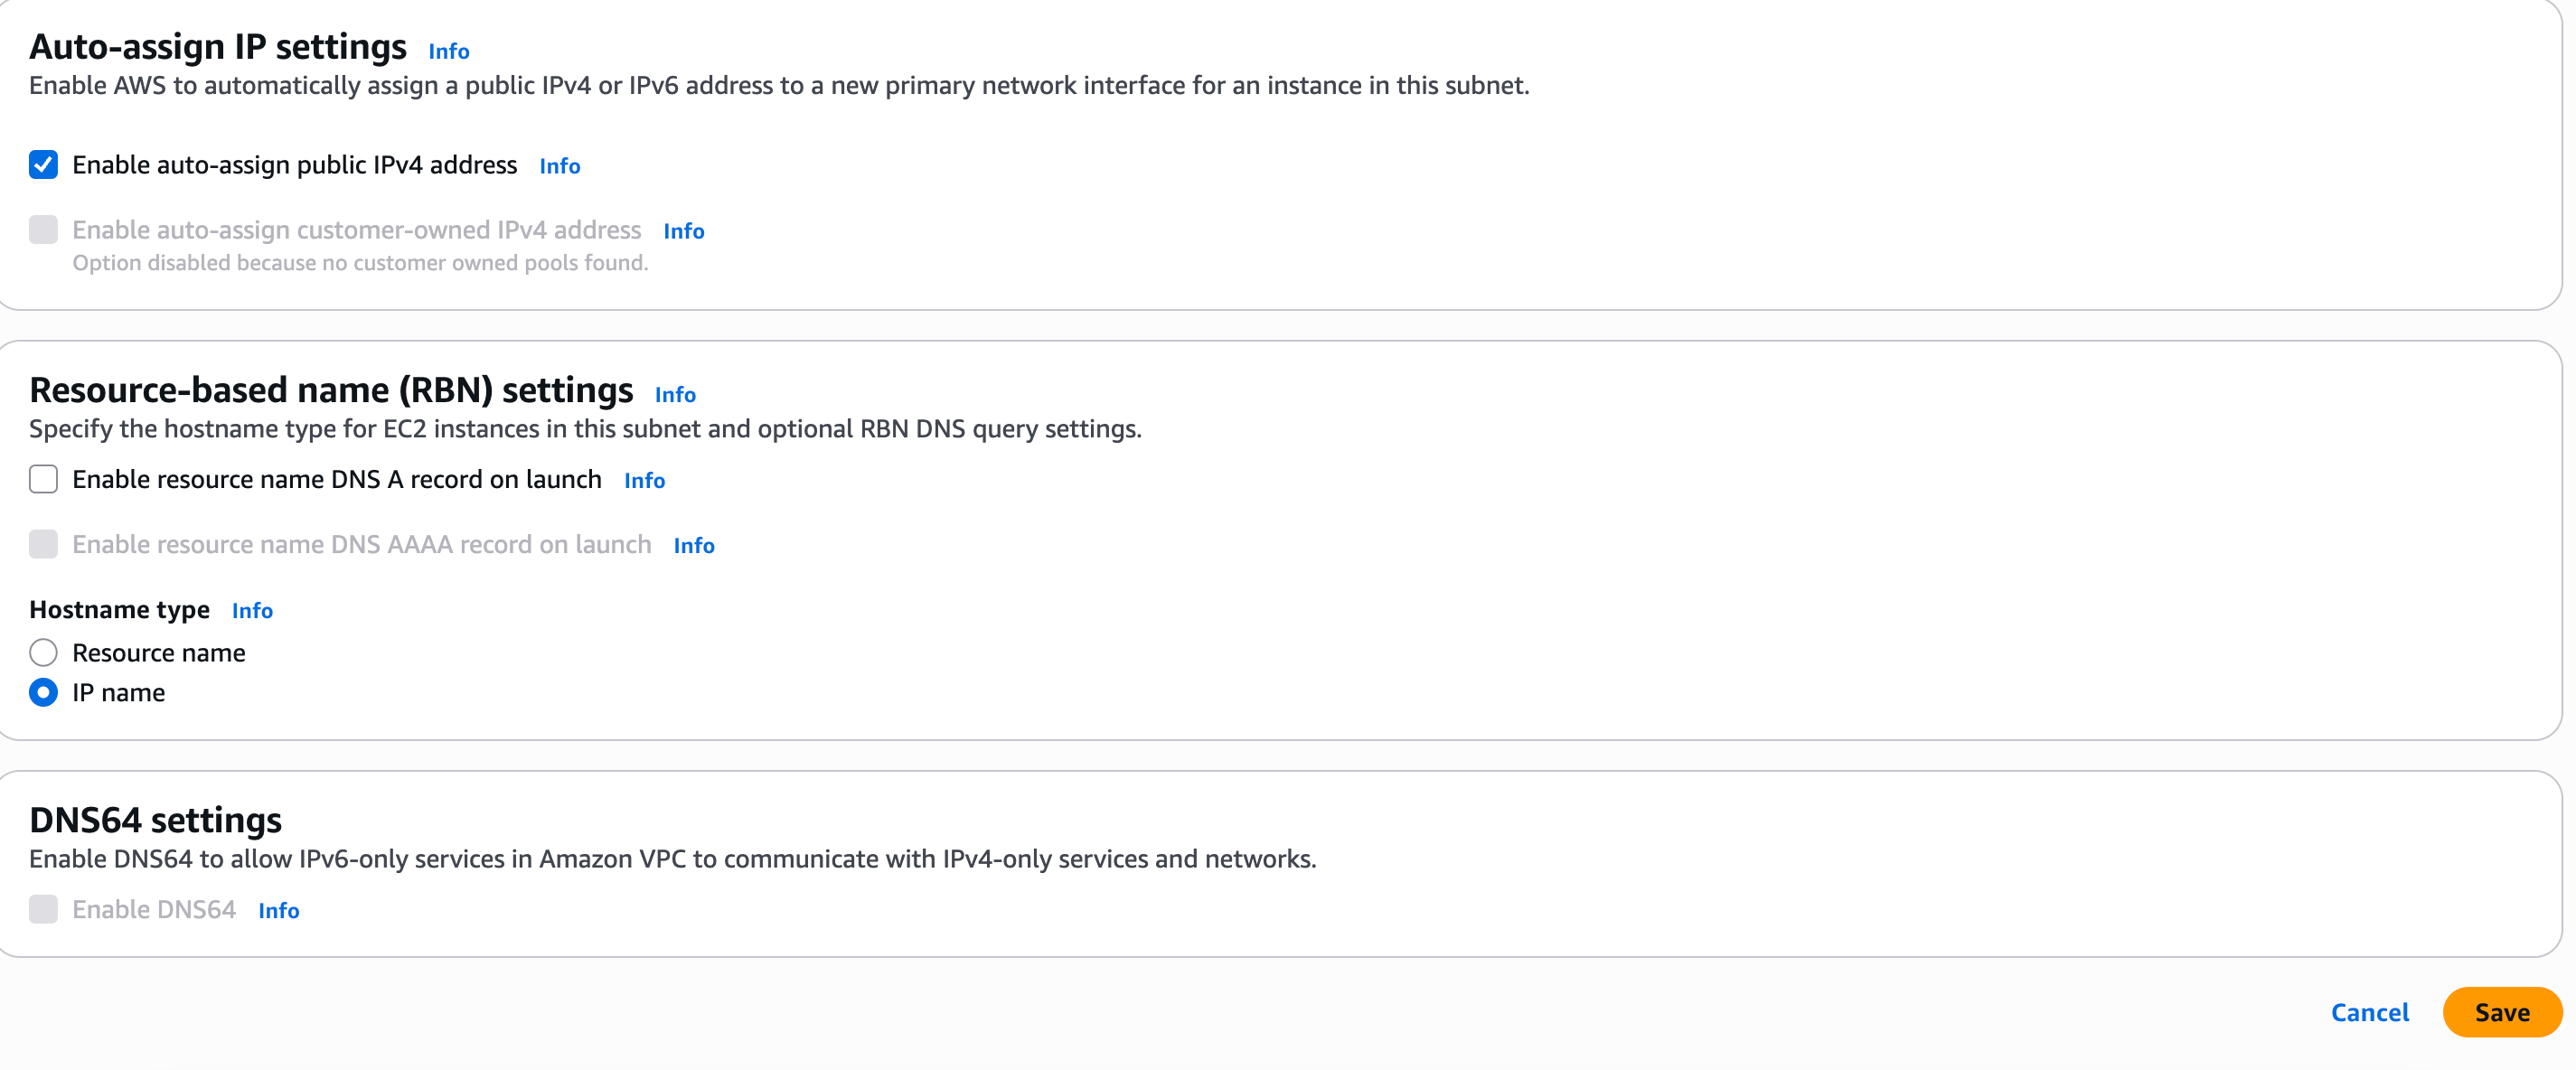
-
Modification is done now.
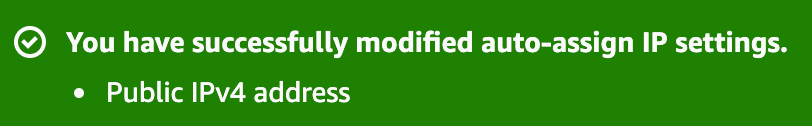
Task 7: Create a Public Route Table
-
Go to Route Tables from the left menu and click on Create route table button.
- Name: Enter PublicRouteTable
- VPC: Select MyVPC from the list.
- Click on Create route table button.
-
Select the PublicRouteTable and go to the Subnet Associations tab.
- Click on Edit subnet associations.
- Select Public Subnet from the list.
- Click on Save associations button.
- Select the PublicRouteTable from the left panel.
- On the Edit routes page, Click on the Add route button.
-
Add the Destinations as 0.0.0.0/0 and Select the Internet gateway present.
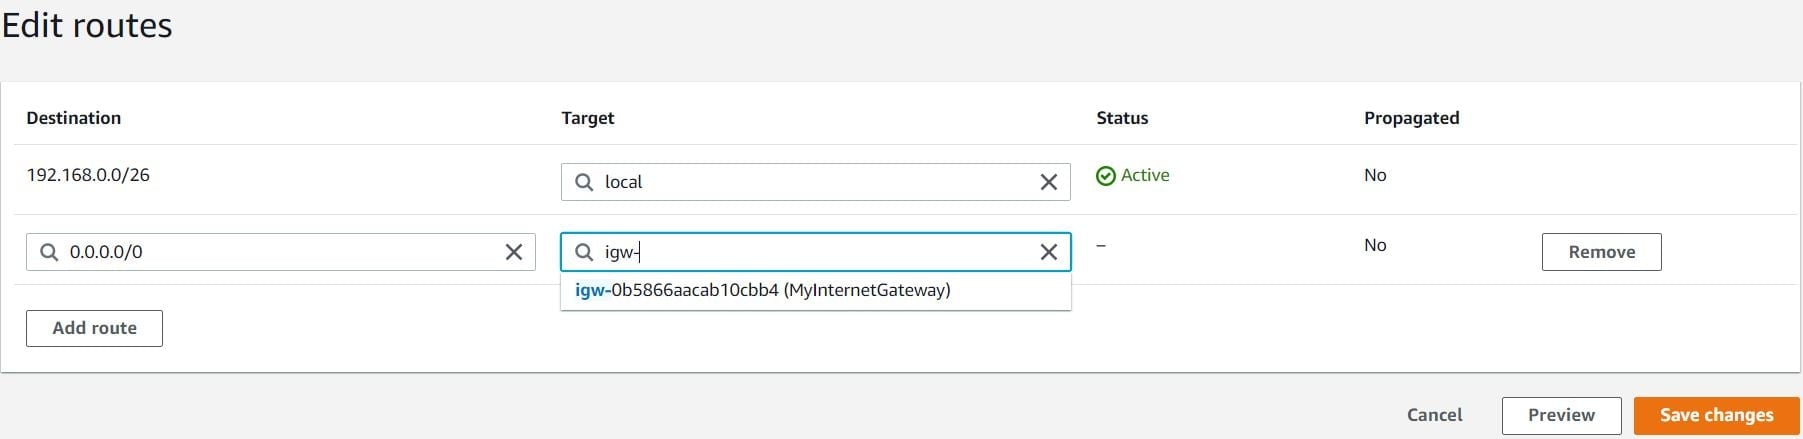
- Click on the Save changes button.
Task 8: Create a VPC Flow log
- Navigate to the VPC you just created, click on Actions then select Create Flow Log.
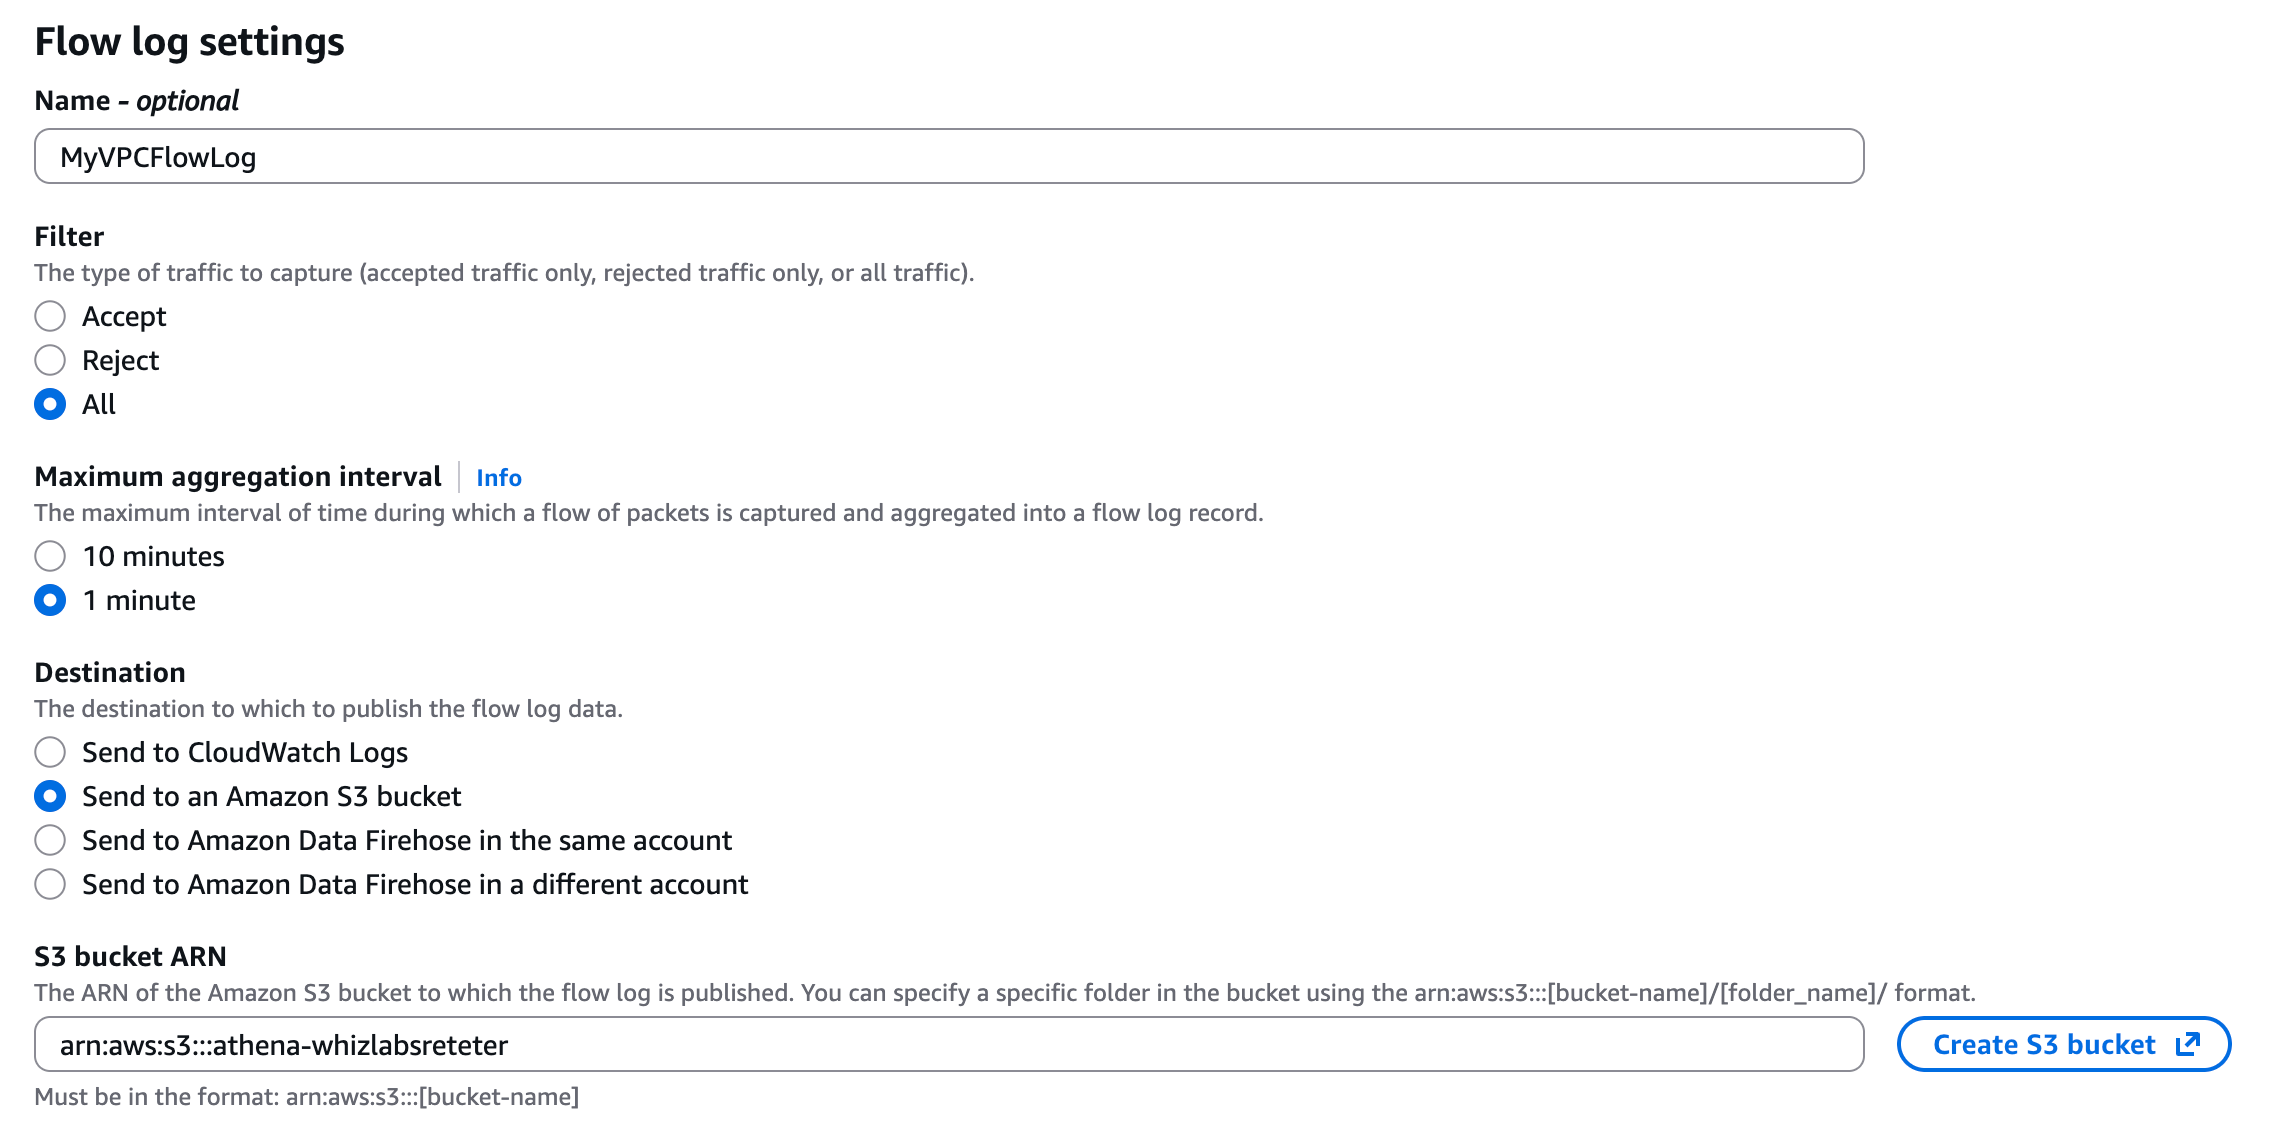
- Enter the name as MyVPCFlowLog**,**
- Select All in filter options and then set the Maximum Aggregation Interval to 1 minute.
- Select as Send to Amazon S3 Bucket as the Destination.
-
Paste the copied S3 Bucket’s ARN in the S3 Bucket ARN field.
- Log record format: Select AWS default format
- Tags: Keep it as default.
- Click on the Create flow log button.
- Once the flow logs are created, head back to the AWS VPC service, select it, and click on Flow Logs.
Task 9: Launching an EC2 Instance to generate traffic
- Make sure you are in the N. Virginia(us-east-1) Region.
- Navigate to EC2 by clicking on the Services menu in the top left, then click on EC2 in the Compute section.
- Navigate to Instances from the left side menu and click on Launch Instances button.
-
Under the Name and tags section :
- Name : MyEC2Instance
-
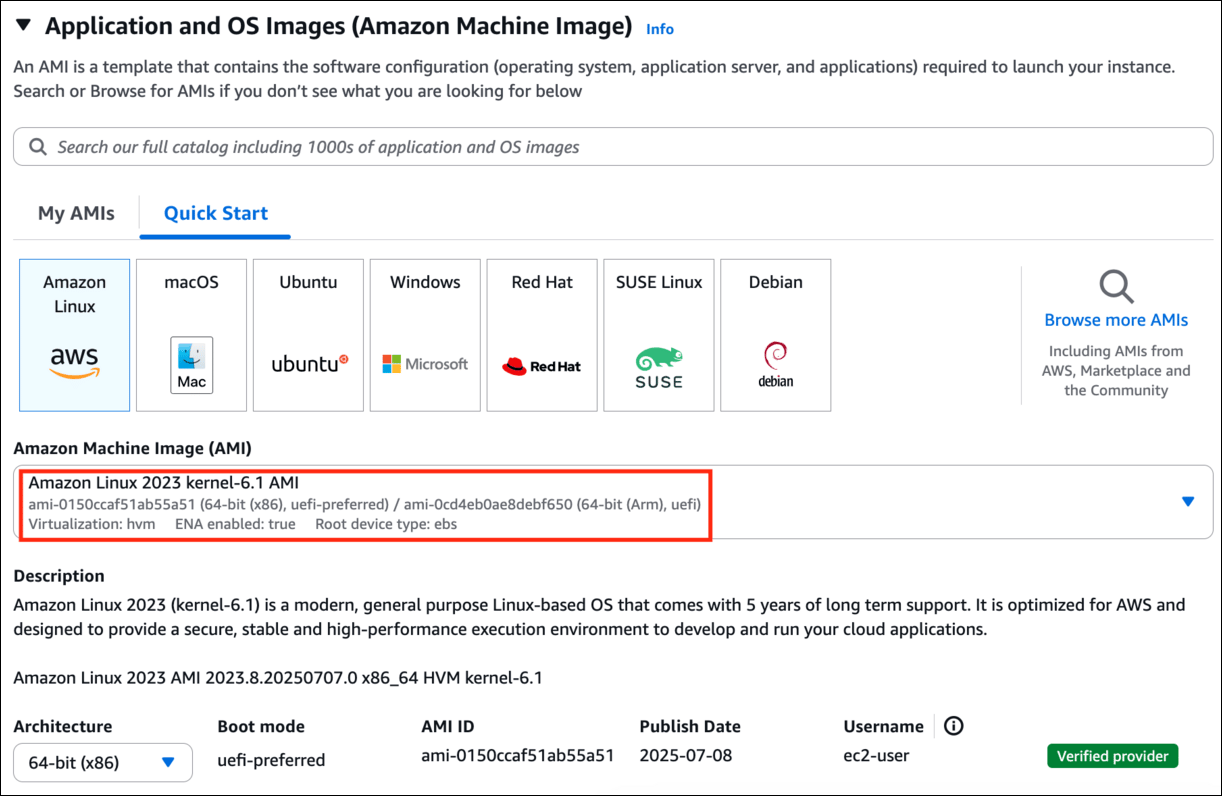
Under the Application and OS Images (Amazon Machine Image) section :
- Select Quick Start tab and Amazon Linux under it
- Amazon Machine Image (AMI) : select Amazon Linux 2023 AMI
-
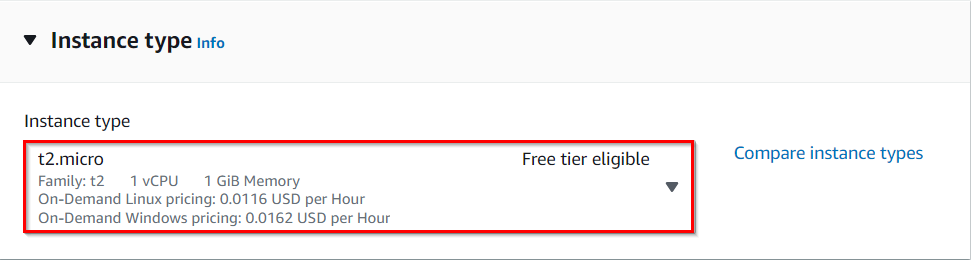
Under the Instance Type section :
- Instance Type : Select t2.micro
-
Under the Key Pair (login) section :
- Click on Create new key pair hyperlink
- Key pair name: MyEC2FLowLogsKey
- Key pair type: RSA
- Private key file format: .pem or .ppk
- Click on Create key pair and select the created key pair
-
Under the Network Settings section :
- Click on Edit button
- VPC : select MyVPC
- Subnet : select Public Subnet
- Auto-assign public IP: select Enable
- Firewall (security groups) : Select Create a new security group
- Security group name : Enter FlowLog-SG
- Description : Enter Security group for VPC Flow Logs
-
To add SSH:
- Choose Type: SSH
- Source: Anywhere (From ALL IP addresses accessible).
-
For HTTP, click on Add security group rule,
- Choose Type: HTTP
- Source: Anywhere (From ALL IP addresses accessible).
- Keep everything else as default and click on the Launch instance button.
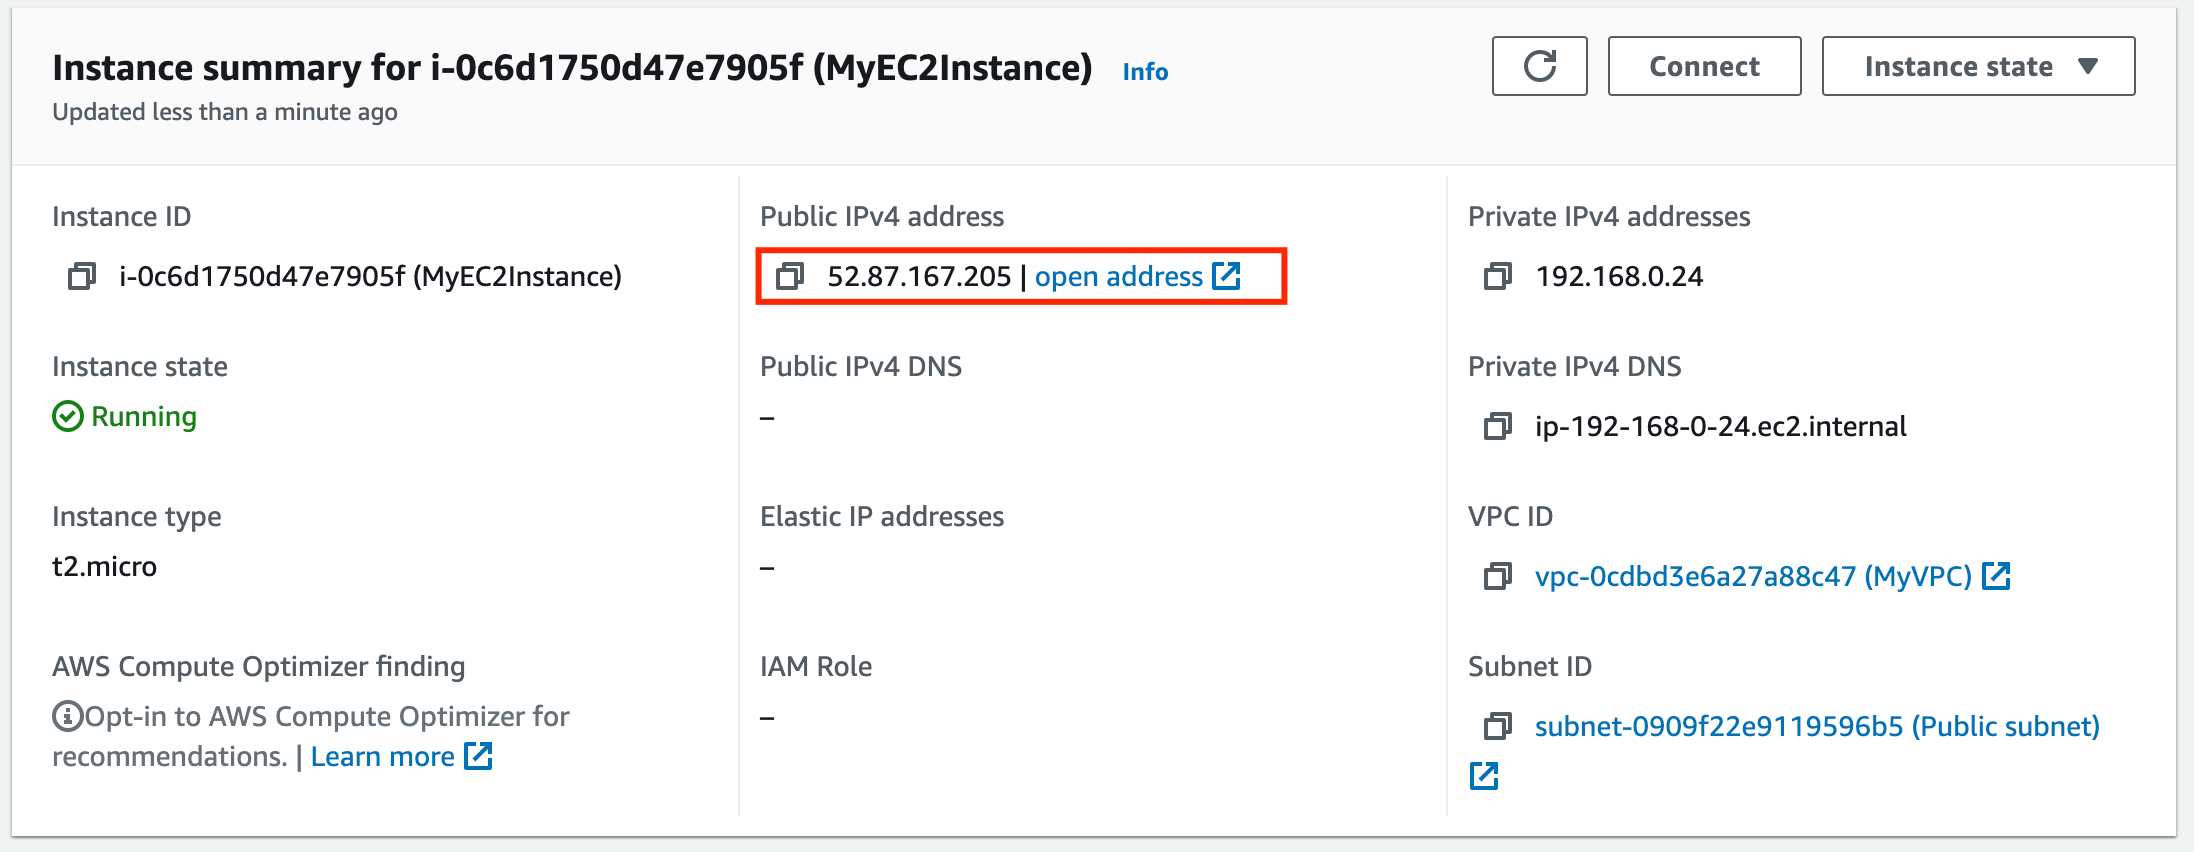
- Launch Status: Your instance is now launching, Navigate to Instances page from the left menu and wait until the status of the EC2 Instance changes to running.
- Note down the IPv4 Public IP Address of the EC2 instance. A sample is shown in the screenshot below.
Task 10: SSH into EC2 Instance
- Please follow the steps in SSH into EC2 Instance.
Task 11: Generate logs that will be sent to S3 Bucket
- Once you SSH into the instance, install an Apache Server. To install it, follow the below steps. Run these commands one-by-one.
-
Copy your instance’s Public IP, paste it into your browser, and hit enter.
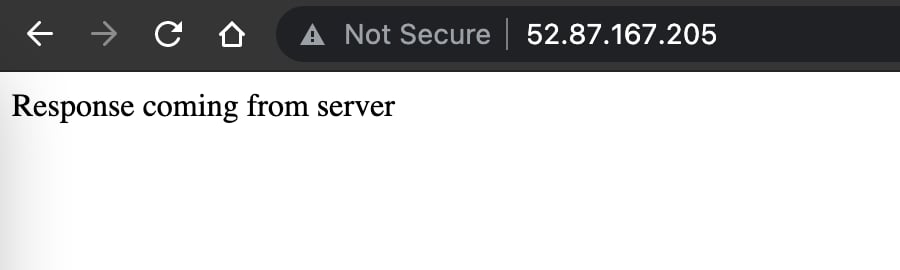
- By Running these commands manually and pasting the Public IP in the Browser, we have generated some traffic.
- Logs will be stored in S3 Bucket at an Interval of 5 minutes.
- Refresh the S3 Bucket and go to the folder AWSLogs/<12 Digit Account number>/vpcflowlogs/us-east-1/<Year>/<Month>/<Date>/. Note: Wait for at least 5 minutes, if you don’t see the folder or the logs inside the folders.
-
Logs will be present. Click on the Copy S3 URI button.
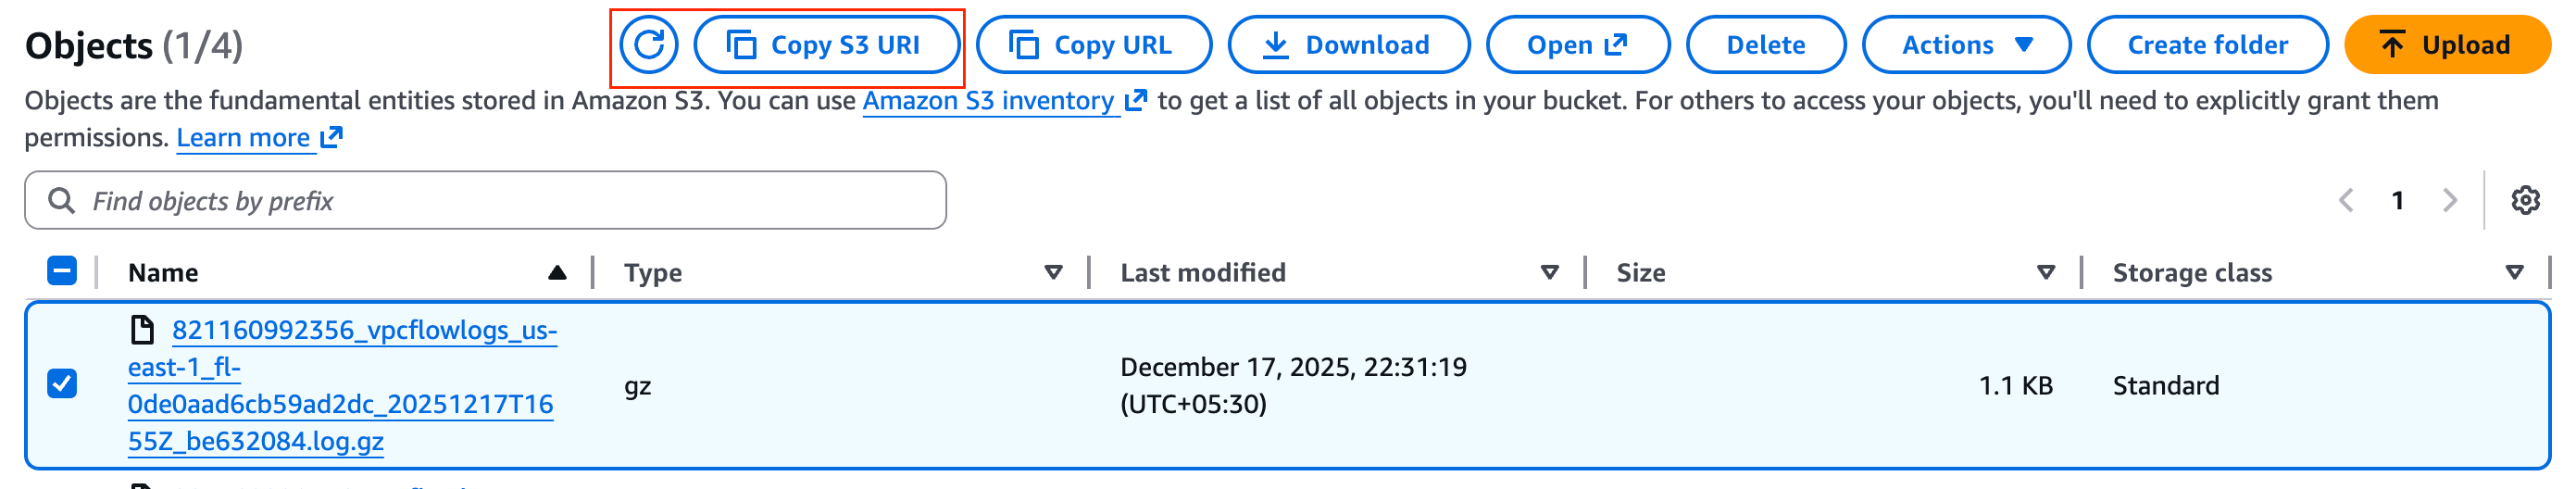
- To Copy the current location of the log file, click on the Copy S3 URI button.
Task 12 : Create Database from Amazon Glue
- Make sure you are in the US East (N. Virginia) us-east-1 Region.
- Navigate to Services menu in the top, then search for AWS Glue and click on it.
- From the left side panel under Data Catalog click on Databases.
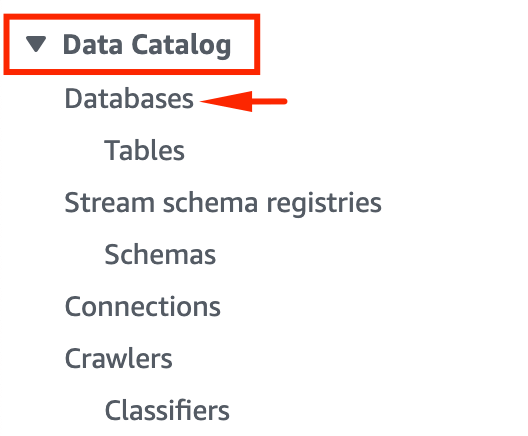
- Click on Add Database button.
- Under database details enter database name as : whizdb
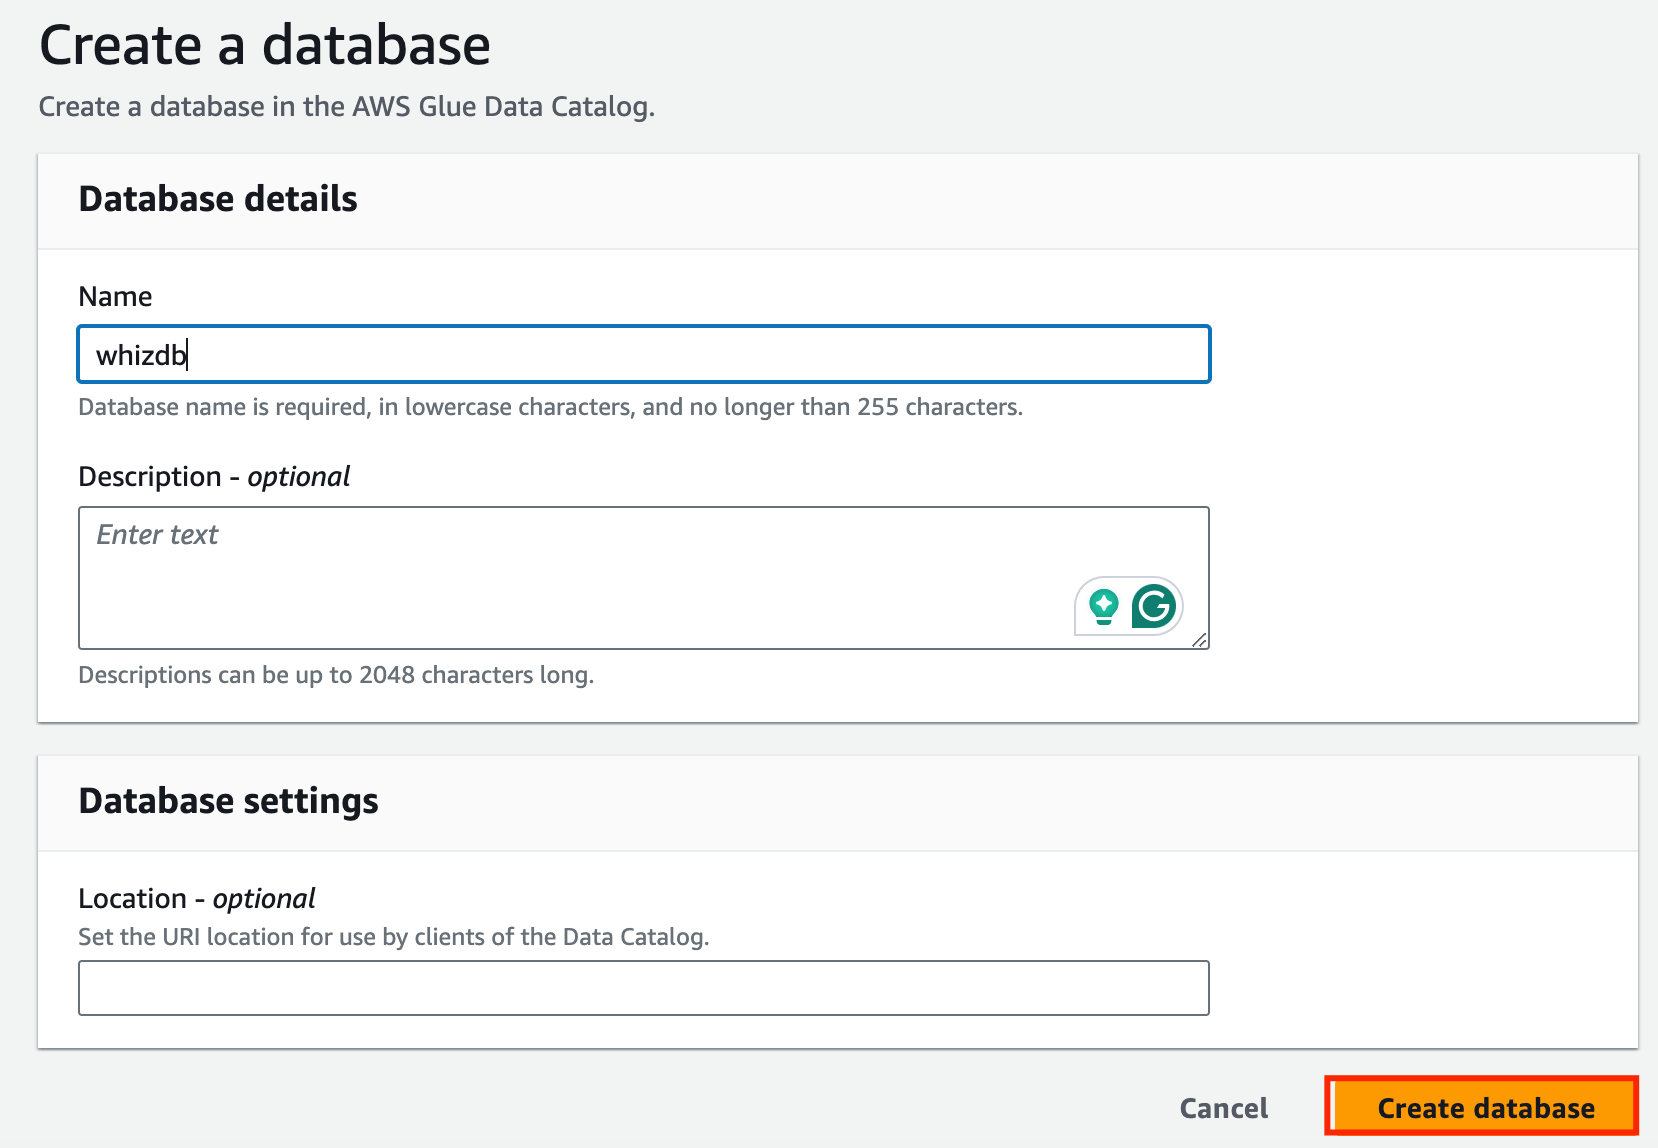
- Now, click on Create database button.
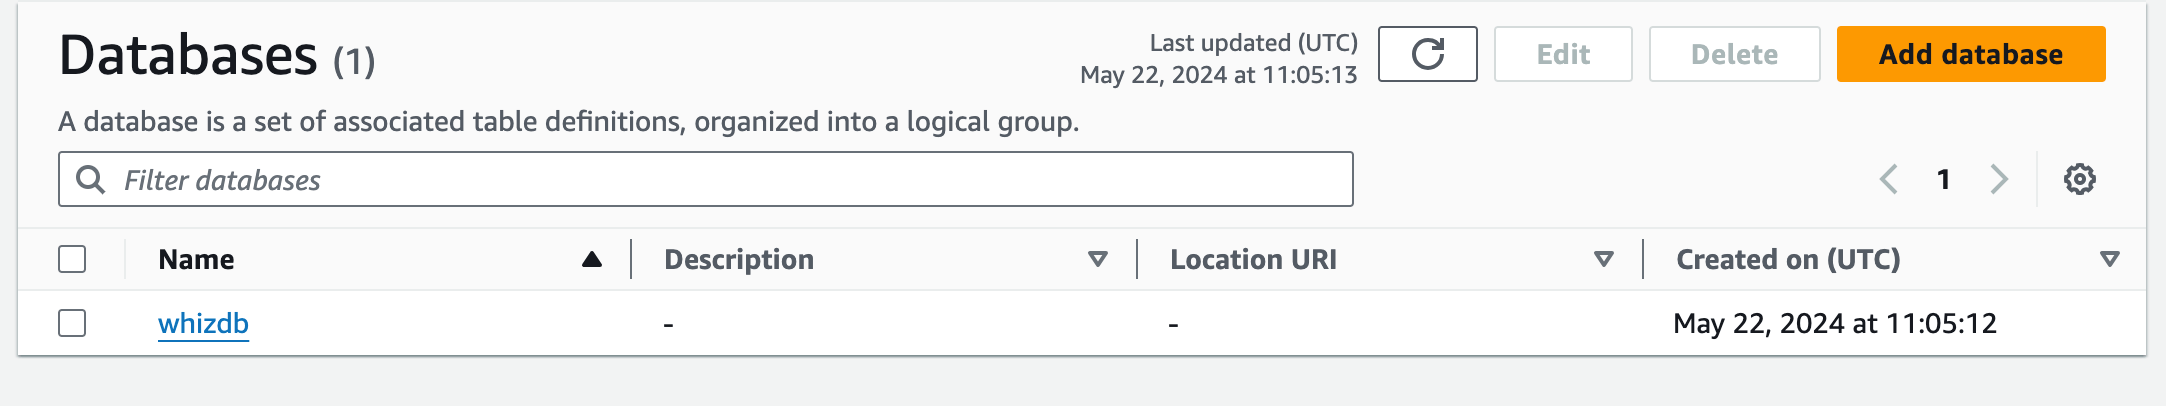
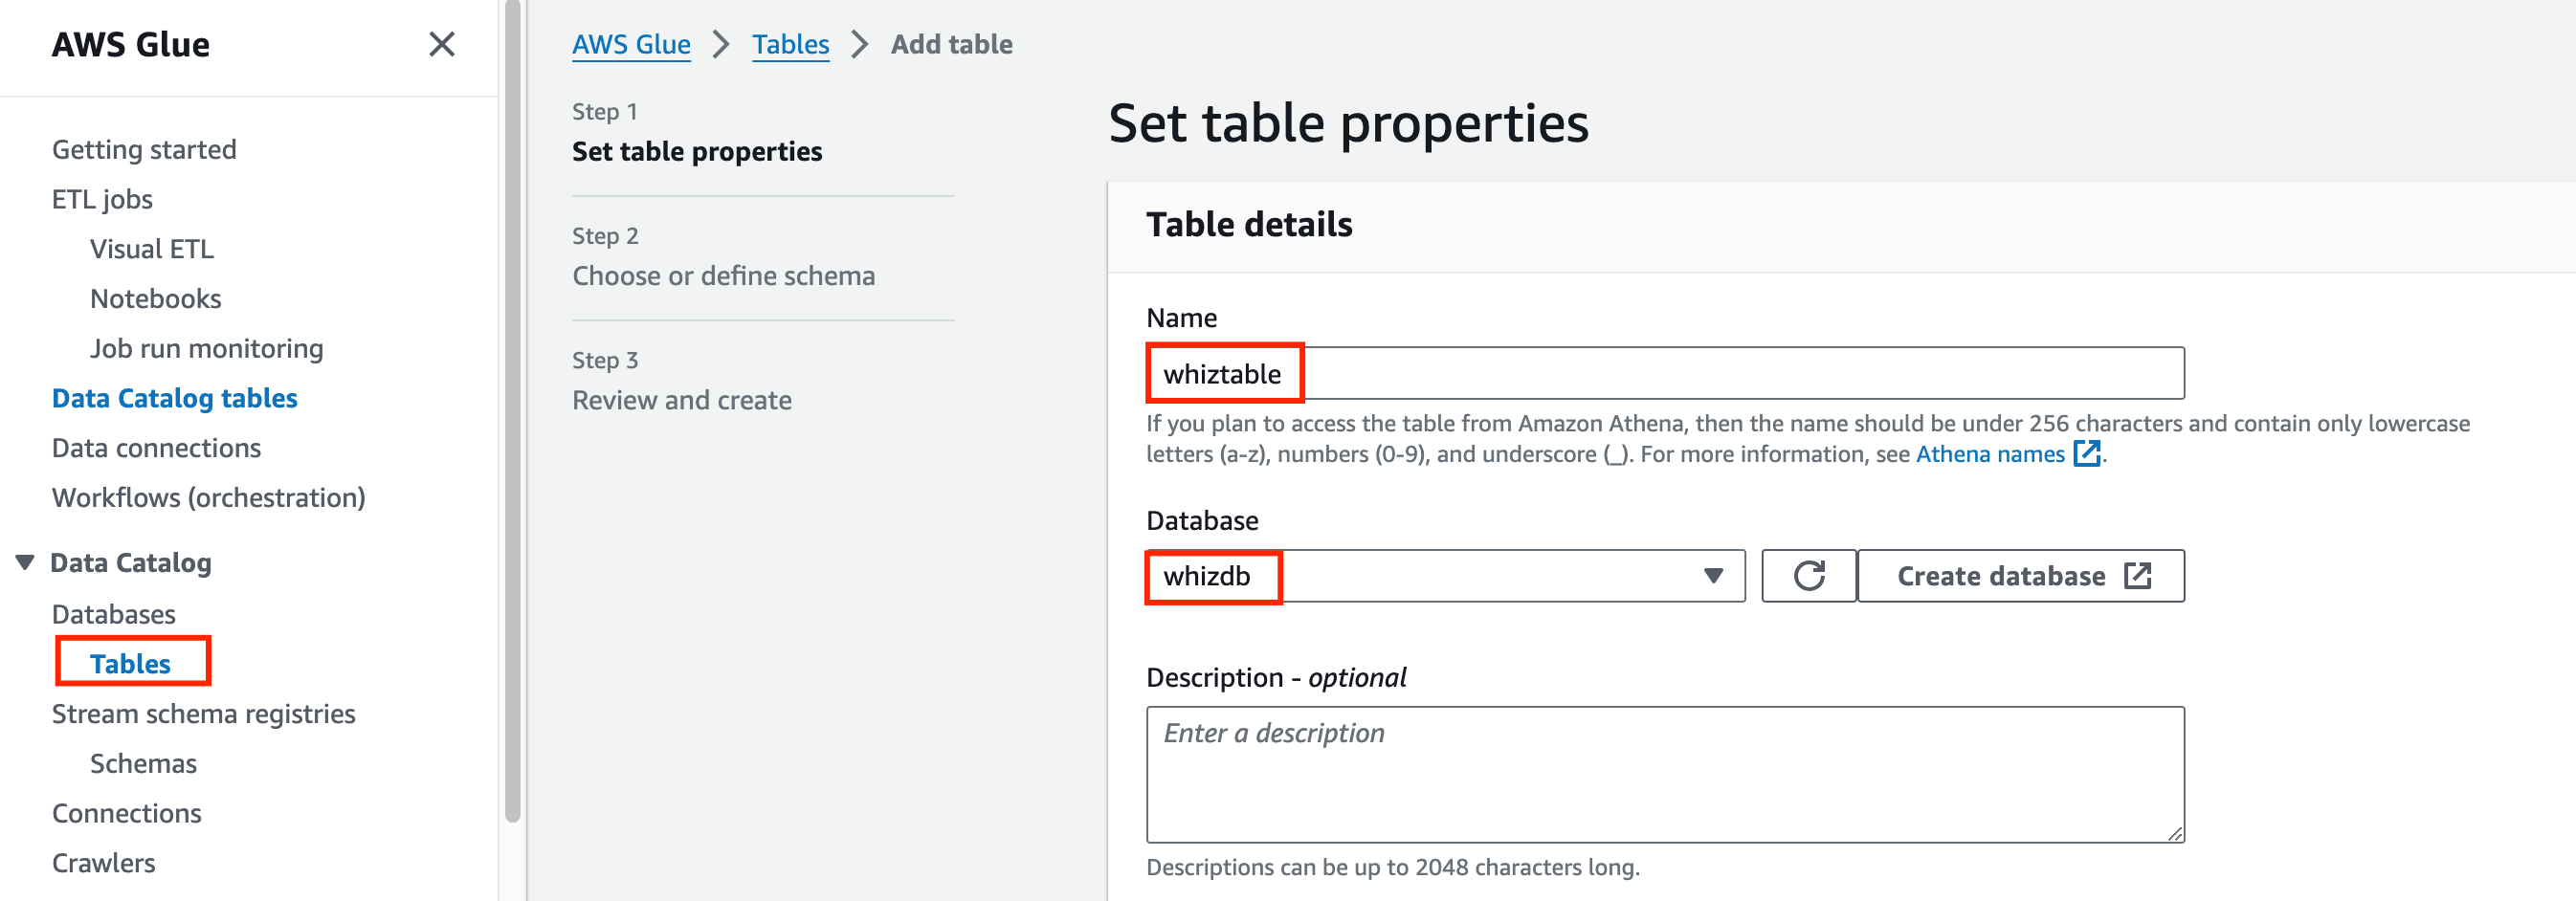
- Now expand the left panel and click on Tables, you will be redirected to set tablet properties.
- Under table details add :
- Name : whiztable
- Database : whizdb
- Inside Data store Include path of your created s3 bucket and leave other thing as default.
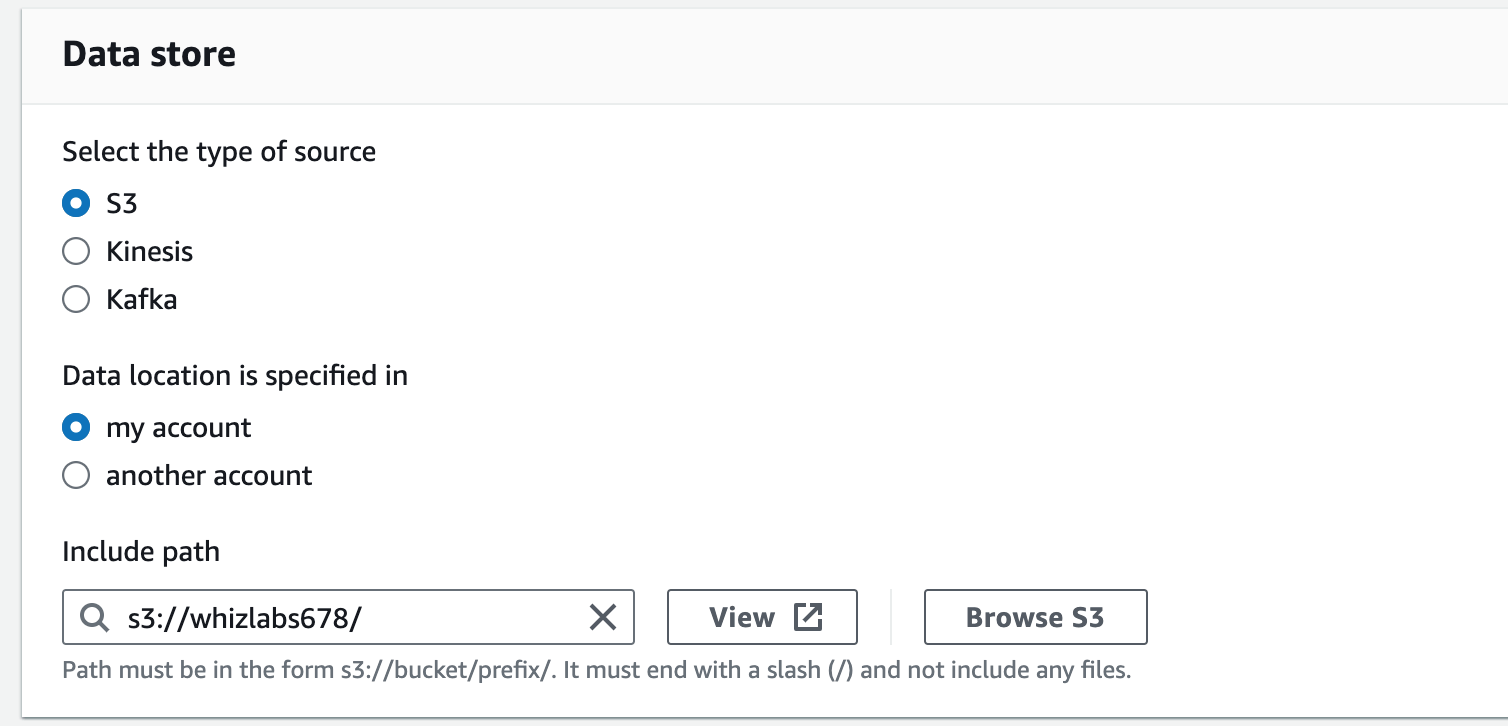
- Under Data format select csv, and click on the Next button**.**
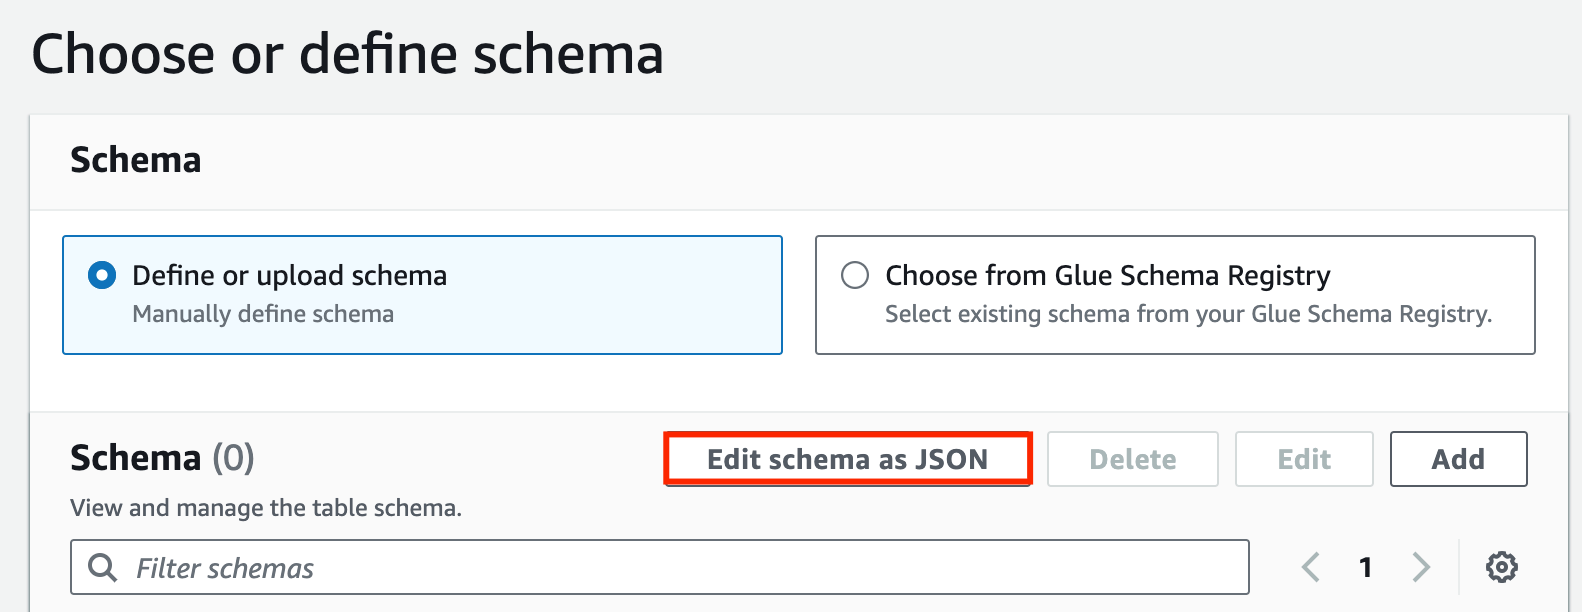
- Under choose of click on Edit schema as JSON button**.**
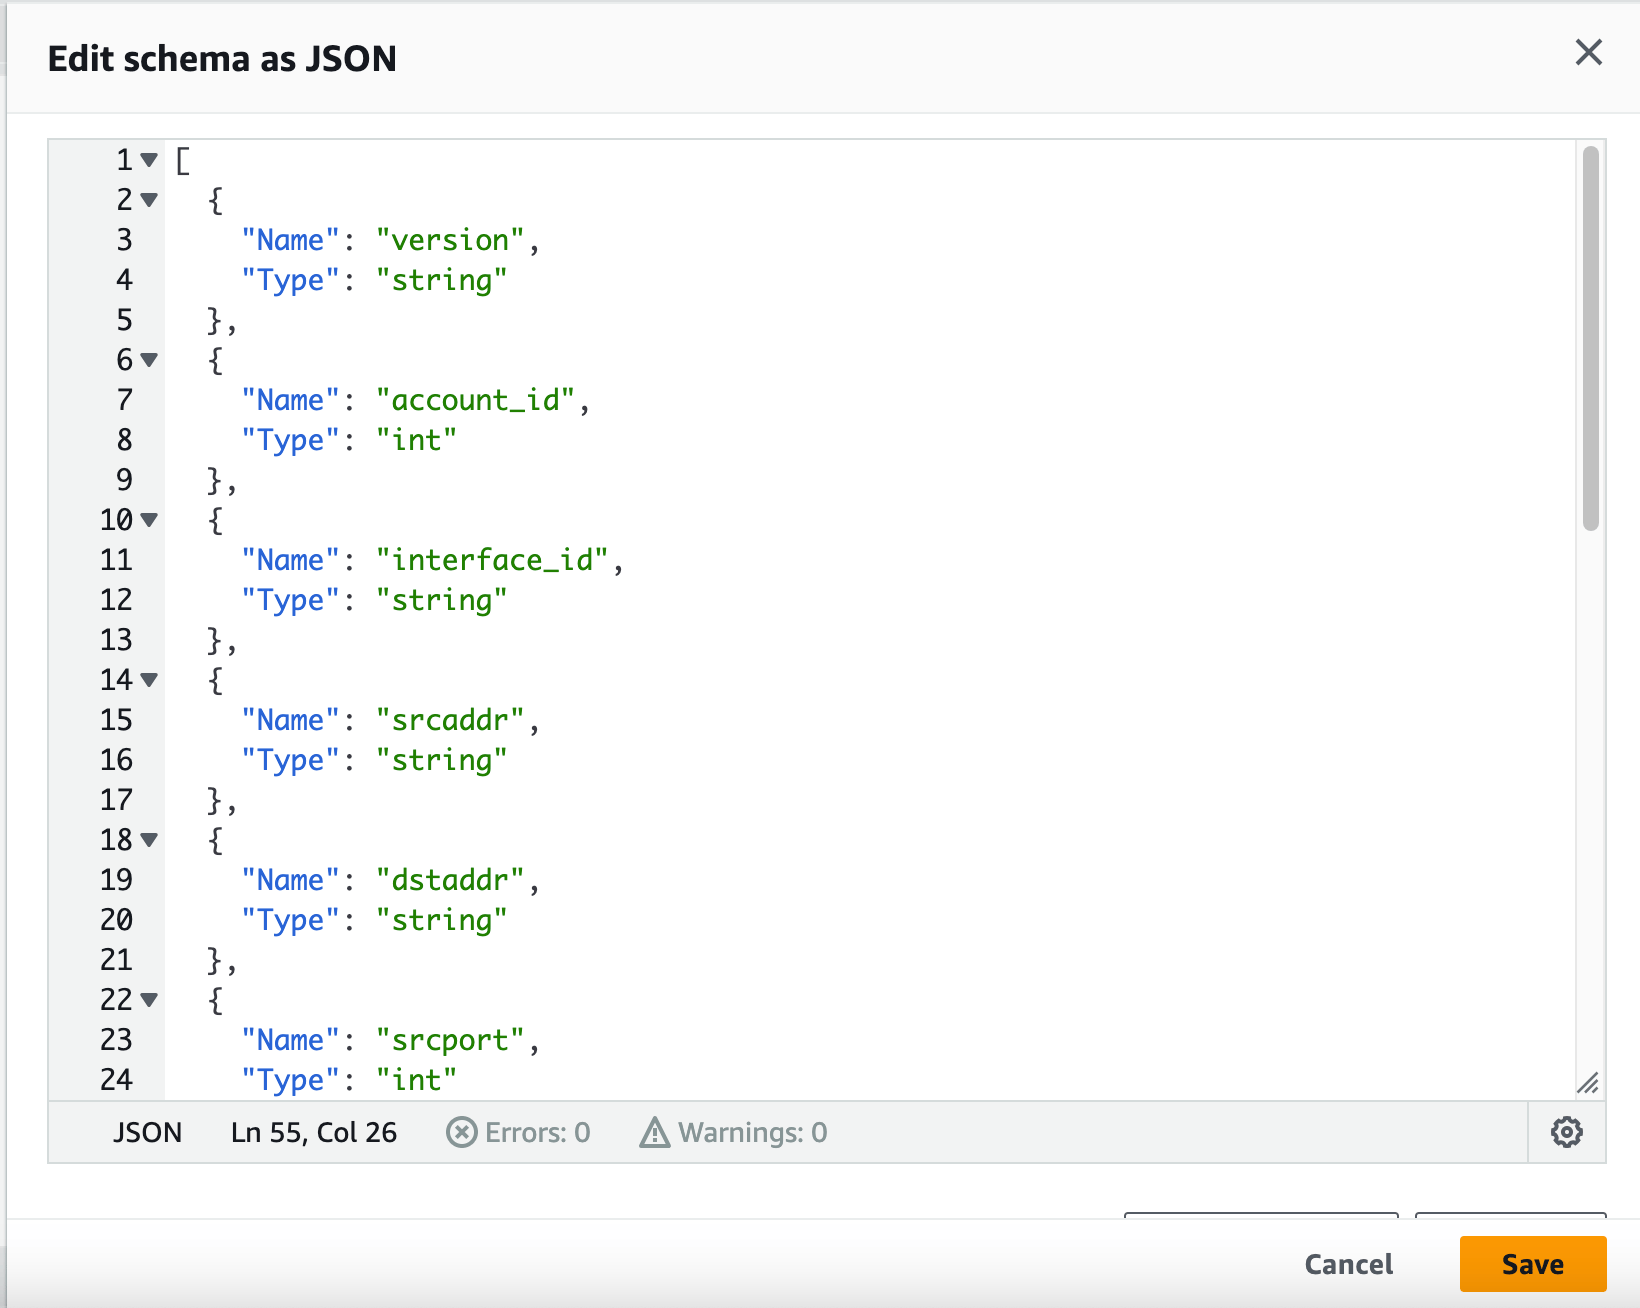
- Paste the given json code to the editor, and click on Save button.
- Now, Click on the Next button.
- Leave everything as default and click on the Create button.

Task 13 : Setup Amazon Athena to query the log data
- Make sure you are in the US East (N. Virginia) us-east-1 Region.
- Navigate to Services menu in the top, then search for Athena and click on it.
- Go to the Query Editor.
-
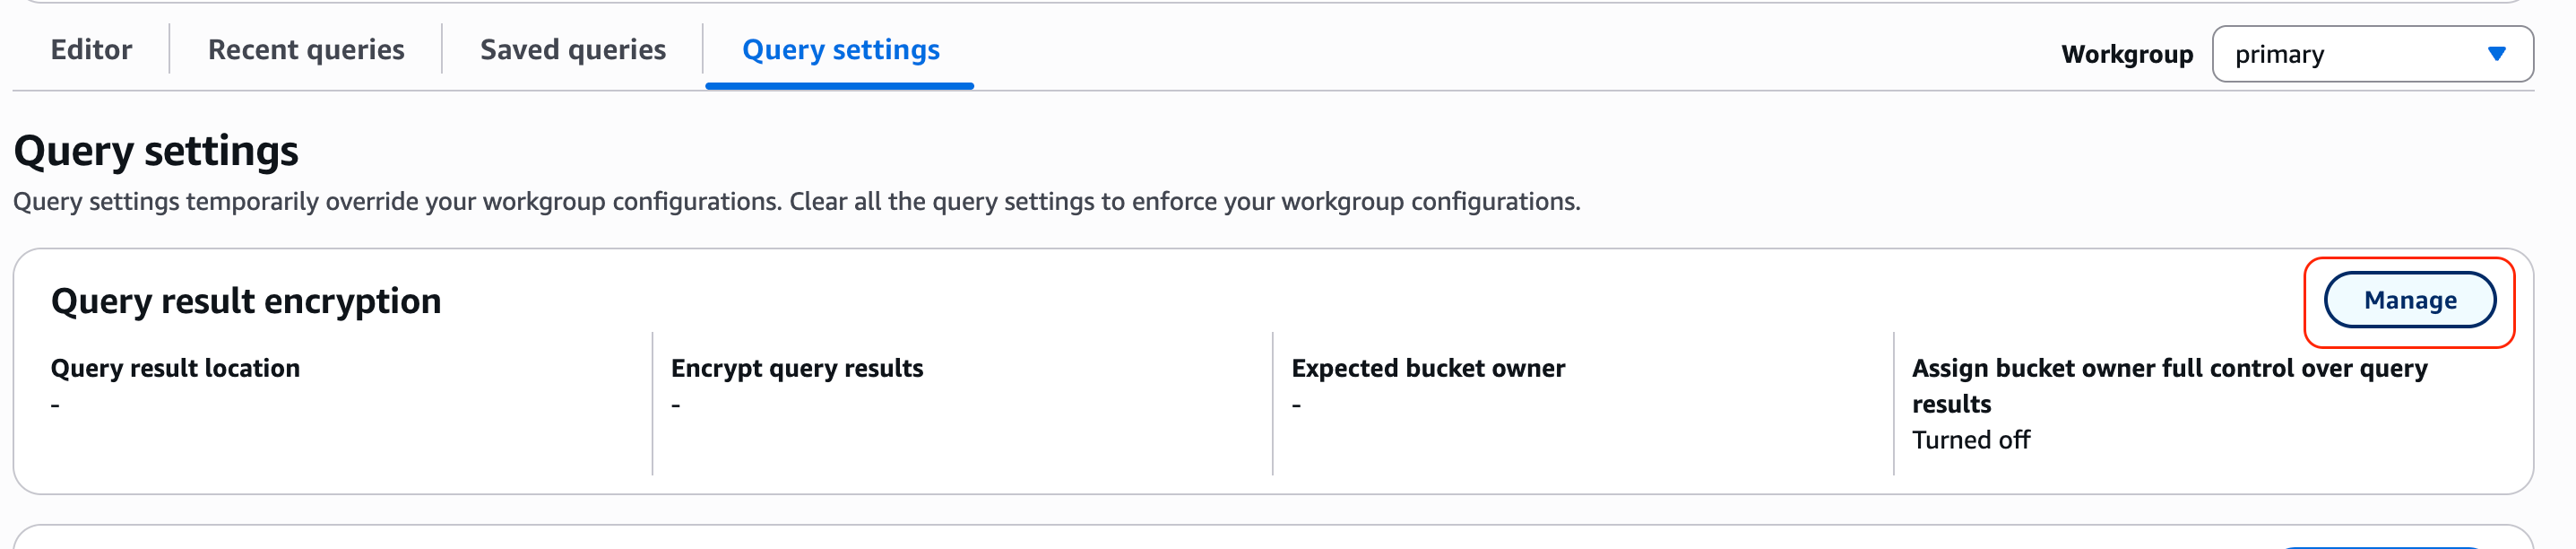
Click on the Query Settings button and then click on Manage button.
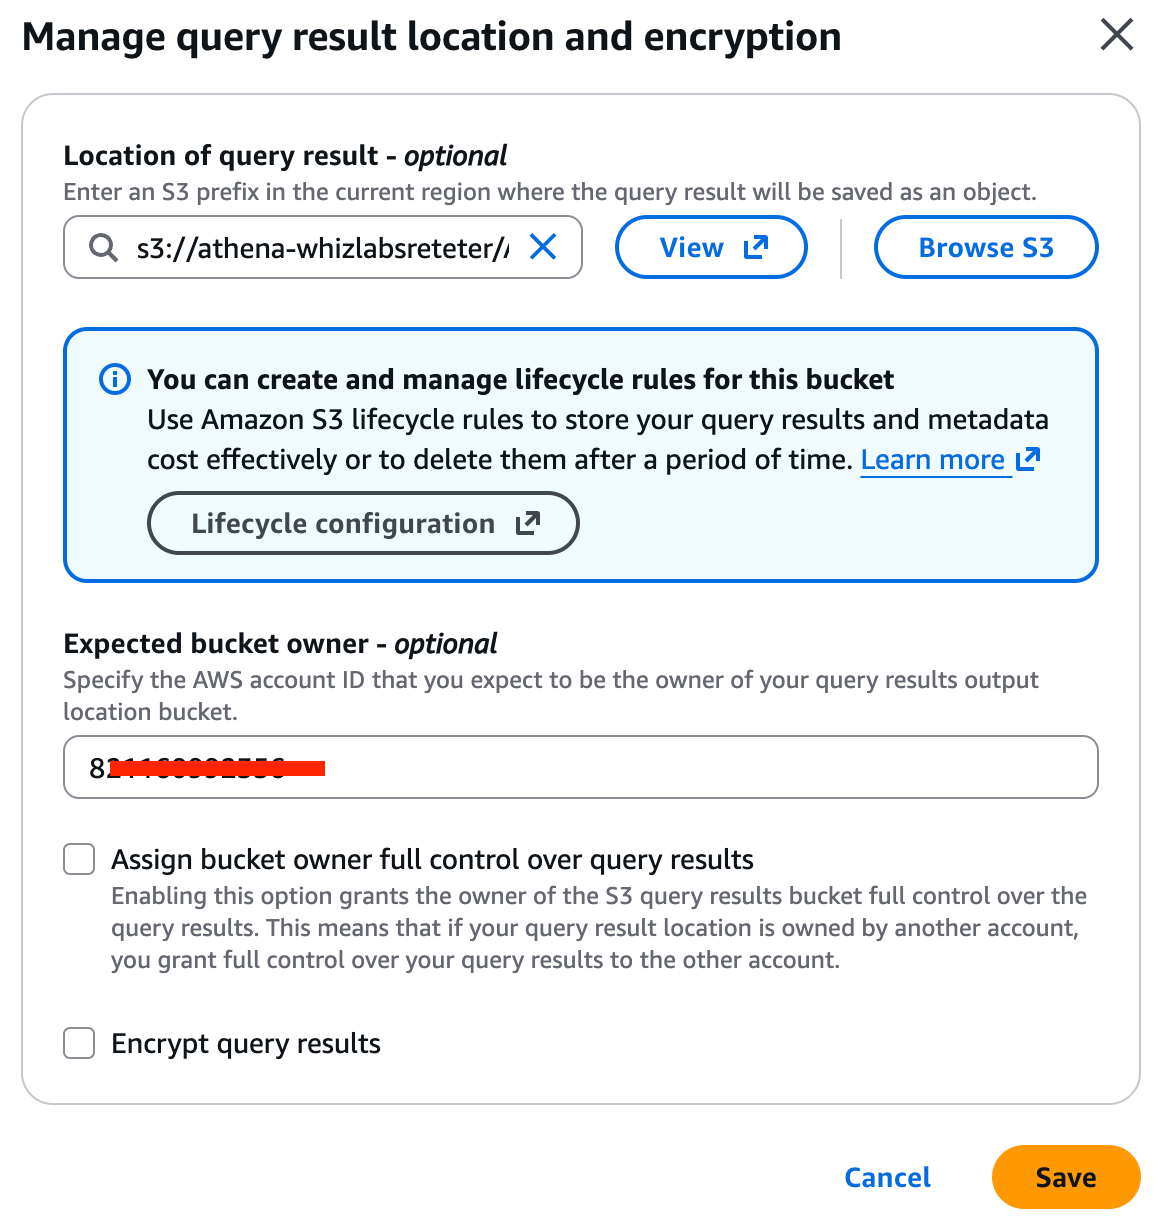
- Now, click on Browse S3 button, select the S3 Bucket created and click on choose button. In this bucket, you have stored the logs and you will run the SQL query.
- Location of query result: Enter s3://athena-whizlabs/AWS logs/ Note: This will same as the S3 Bucket name that we created. Note: If there is any other bucket selected, remove the entry and select the newly created bucket.
-
Expected bucket owner: Enter your account ID [Similar to 9287085xxxxx]
- Now, Click on Save button.
Task 14: Run SQL queries against the table.
- Come Back to Query Tab and Click on the + option to get a new and fresh query editor.
- Paste the below query, to the editor:
- Click on the Run button and the output will show the total number of records present in the WhizTable.
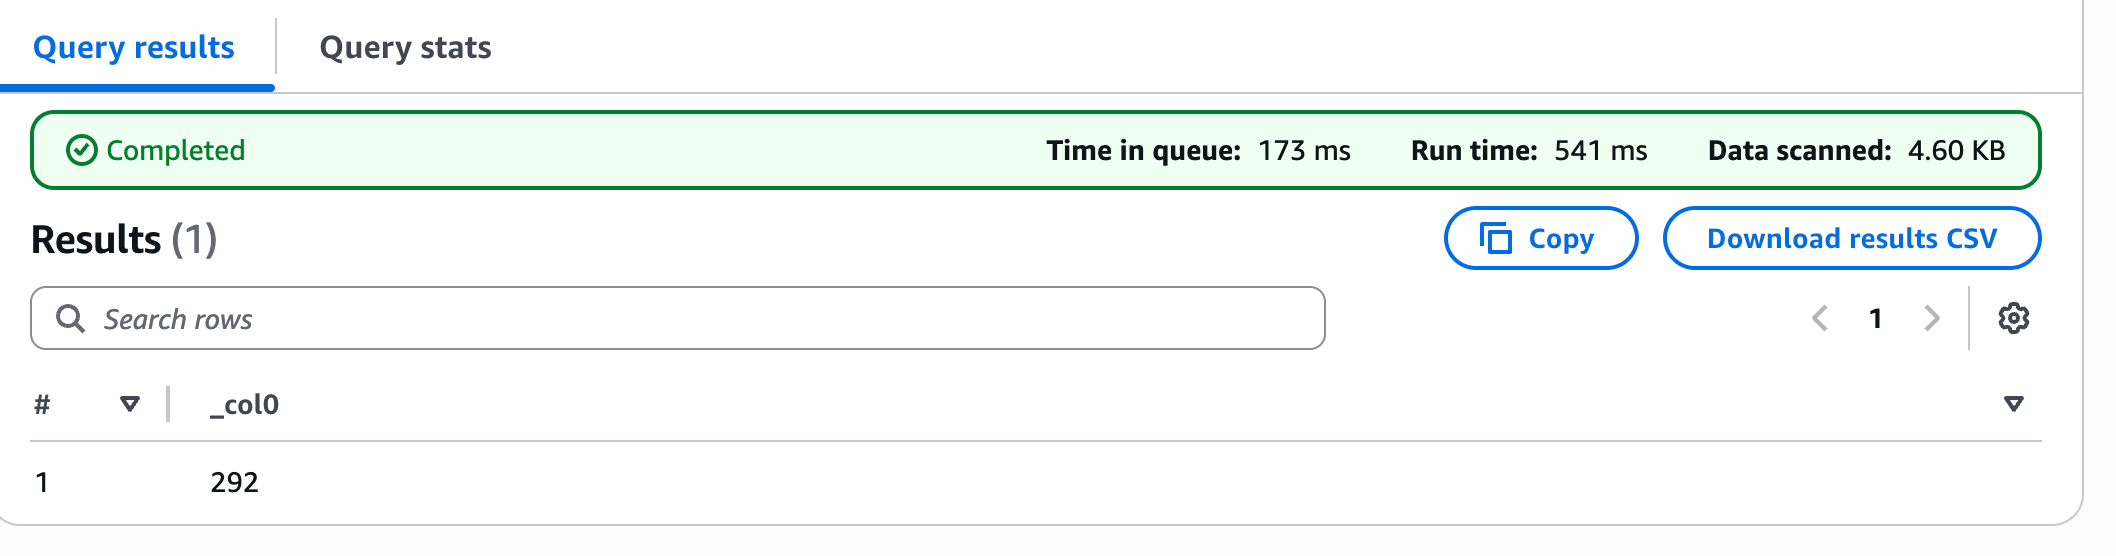
- Click on the + option to get a new and fresh query editor.
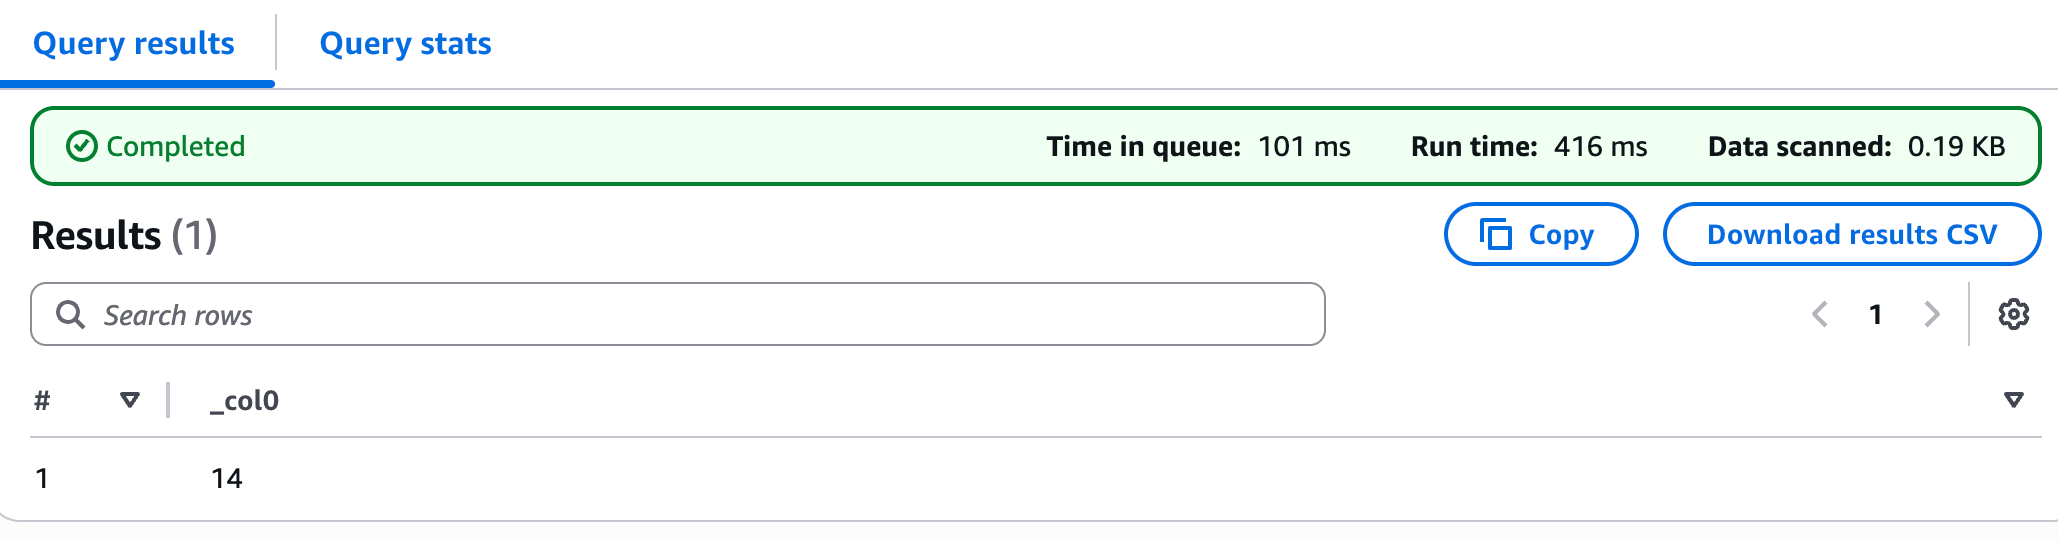
- Find the total number of columns present in the table.
-
There is a total of 14 columns present in the table.
- Once the project steps are completed, please click on the Validation button on the right side panel.
Completion and Conclusion
- You have successfully created S3 Bucket.
- You have successfully created the VPC and its components.
- You have successfully created the VPC Flow Logs.
- You have successfully created an EC2 Instance.
- You have successfully created Subnets that should be separate then generated some site traffic.
- You have successfully analyzed the S3 Bucket’s data using Amazon Athena.
End Project
- Sign out of AWS Account.
- You have successfully completed the project.
- Once you have completed the steps click on End Project from the IP Lab Portal dashboard.
What gets checked
When you press Check my work, the platform verifies each of these:- Run Athena Query — Check whether an Athena query is executed and status is success or not.
- Create Public AWS S3 Bucket — Check whether a Public S3 Bucket created or not
- Create a Glue Database — Check whether a Glue Database is created or not.
- Create a Glue Table — Check whether an AWS Glue Table exists in any database or not