

Overview
Lab Details
- This lab walks you through the steps to create an unencrypted instance with the Encrypt option.
- You will practice this lab by not enabling the encryption of DB Instance while creating.
- Duration: 1 hour 20 minutes
- AWS Region: US East (N. Virginia) us-east-1
Introduction
- Amazon RDS can encrypt your Amazon RDS DB Instances.
- When the encrypt option is enabled for the AWS RDS Resources, we are able to encrypt DB Instances, Automated Backups, Read replicas, Snapshots and Logs.
- Amazon RDS encrypted DB instances use the AES-256 encryption algorithm to encrypt your data on the server that hosts your Amazon RDS DB instances.
- The Encrypt option can be enabled only when you are launching the DB instance, it cannot be enabled after launch. However, copies of unencrypted snapshots can be encrypted.
Architecture Diagram
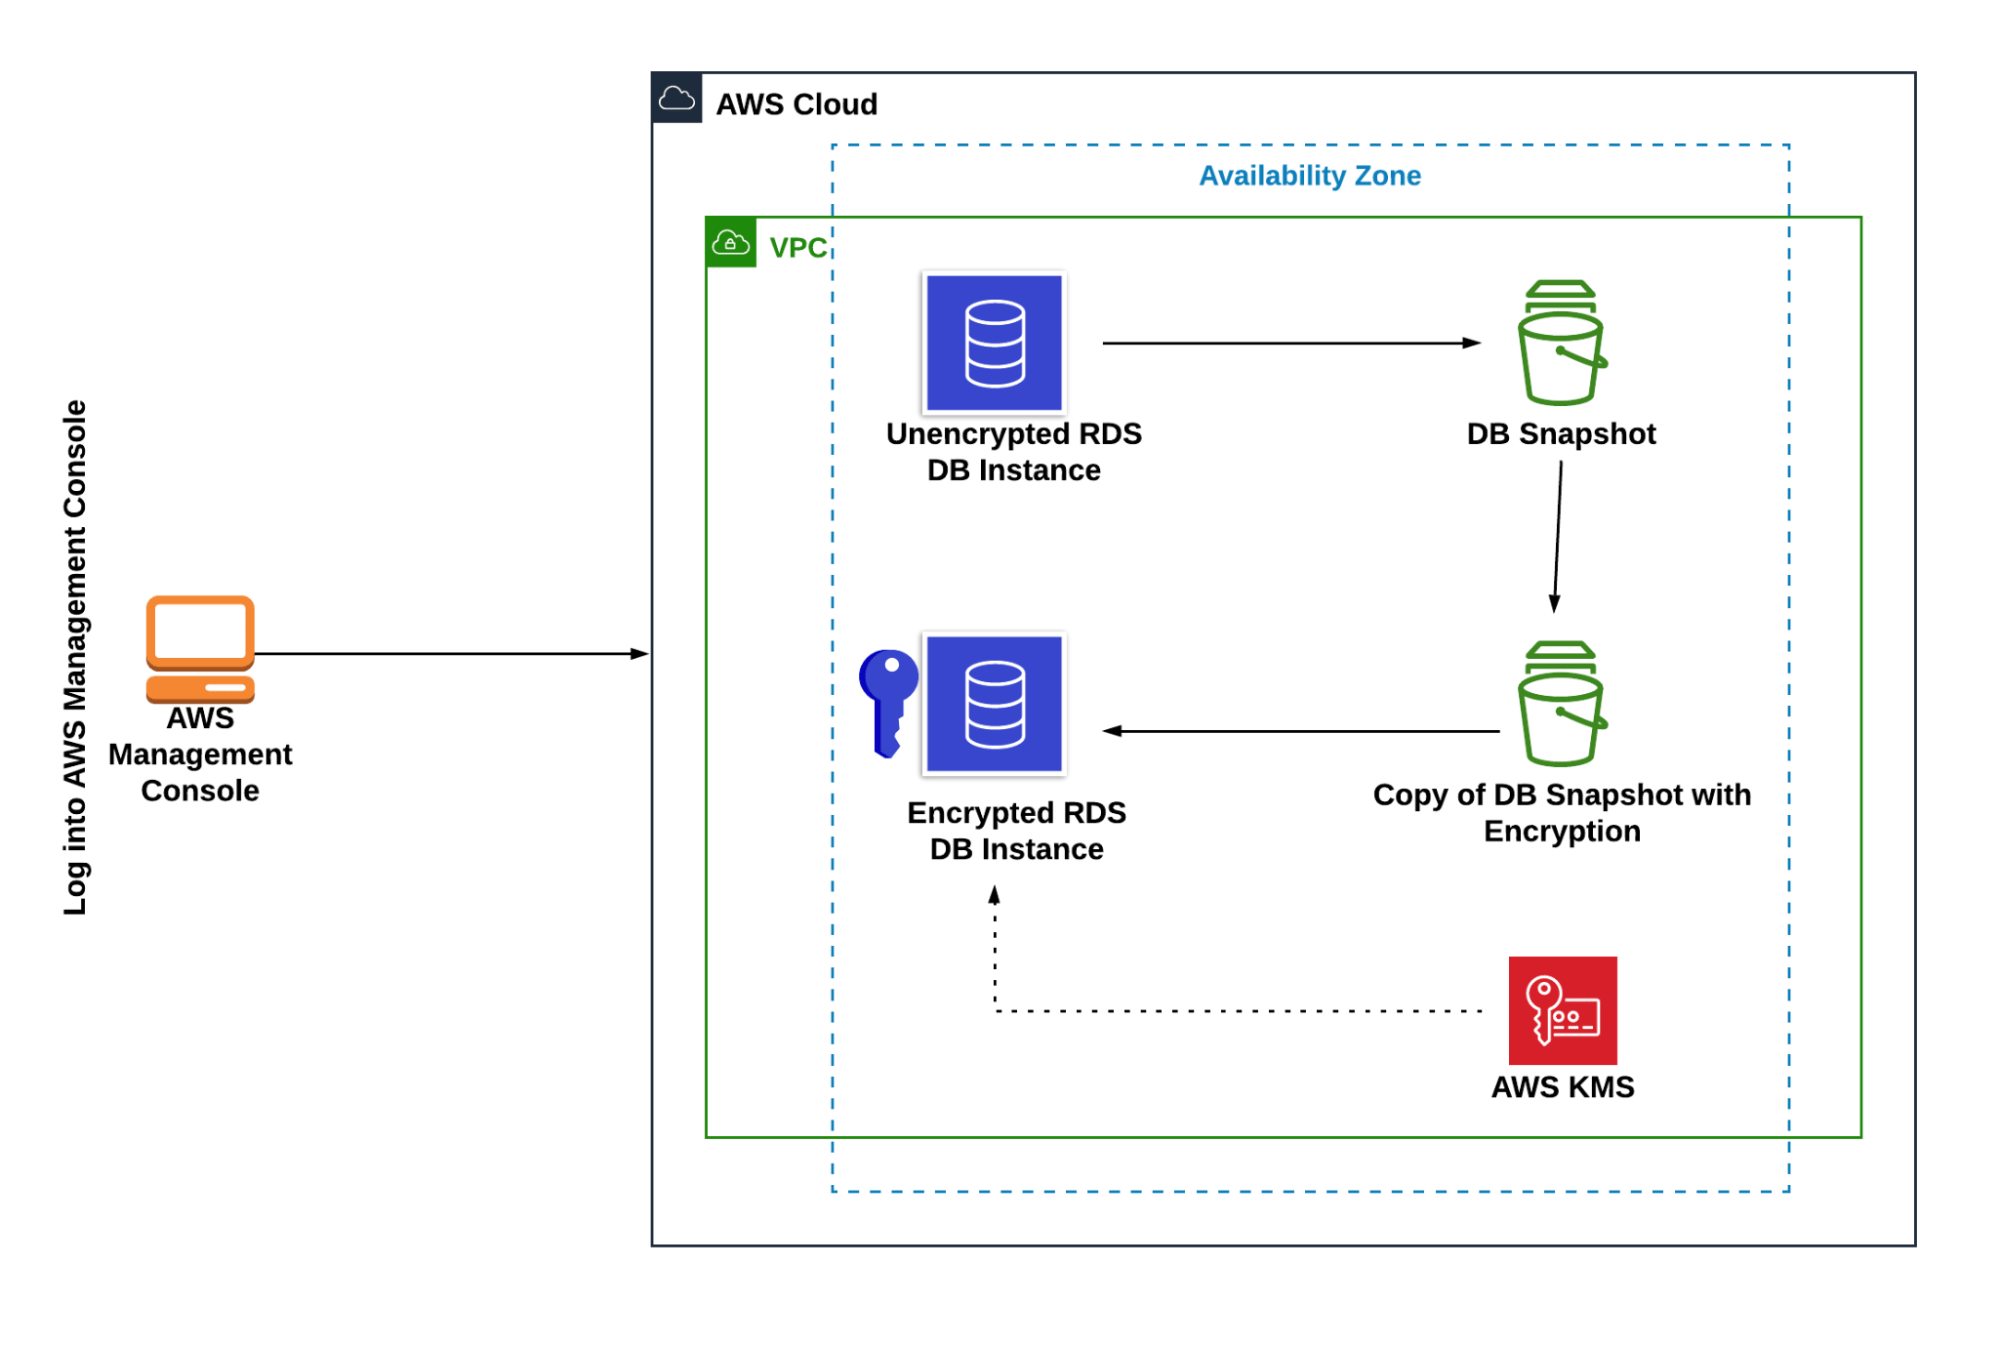
Task Details
- Sign in to AWS Management Console.
- Create an Amazon RDS DB Instance (without enabling encrypt option).
- Take a snapshot from an existing DB Instance.
- Make a copy of the snapshot and encrypt it.
- Restore DB Instance from the encrypted snapshot.
- Change the name of the original DB Instance.
- Change the name of the Restored DB Instance to the original DB Instance name.
- Delete the original RDS Instance and snapshot.
- Deleting AWS Resources
Case Study
- Suppose we have created an RDS DB Instance without enabling the encryption. As days passed by the project became bigger and began to store more sensitive data.
- As you are quite aware of security issues, you wanted to check on the AWS console that your database was well encrypted.
- Your database was totally Unencrypted. And when you check to encrypt the database, you have no option to encrypt the database.
Launching Lab Environment
- To launch the lab environment, Click on the Start Lab button.
- Please wait until the cloud environment is provisioned. It will take less than a minute to provision.
- Once the Lab is started, you will be provided with IAM user name, Password, Access Key, and Secret Access Key.
Note : You can only start one lab at any given time
Lab guide
Lab Steps
Task 1: Sign in to AWS Management Console
- Click on the Open Console button, and you will get redirected to AWS Console in a new browser tab.
-
On the AWS sign-in page,
- Leave the Account ID as default. Never edit/remove the 12 digit Account ID present in the AWS Console. otherwise, you cannot proceed with the lab.
- Now copy your User Name and Password in the Lab Console to the IAM Username and Password in AWS Console and click on the Sign in button.
- Once Signed In to the AWS Management Console, Make the default AWS Region as US East (N. Virginia) us-east-1.
Task 2: Create an RDS DB Instance (without enabling the Encryption)
- Navigate to the Services menu at the top left corner and click on RDS present under the Database section.
- Select the Database from the left panel.
- Click on Create Database and you are navigated to the page where you will provide all the required details to create a MySQL database.
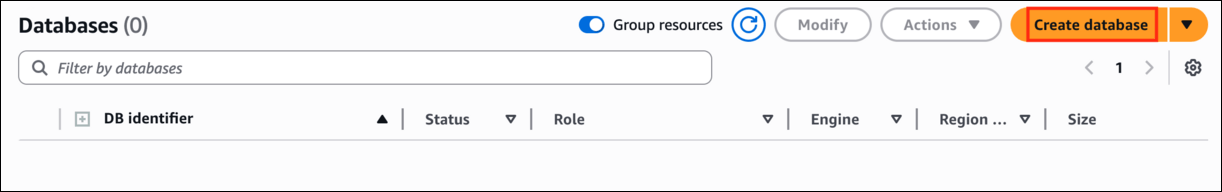
- On the page, click on the option Standard create a method for our lab requirement.

-
In the Engine options, select MySQL engine type.
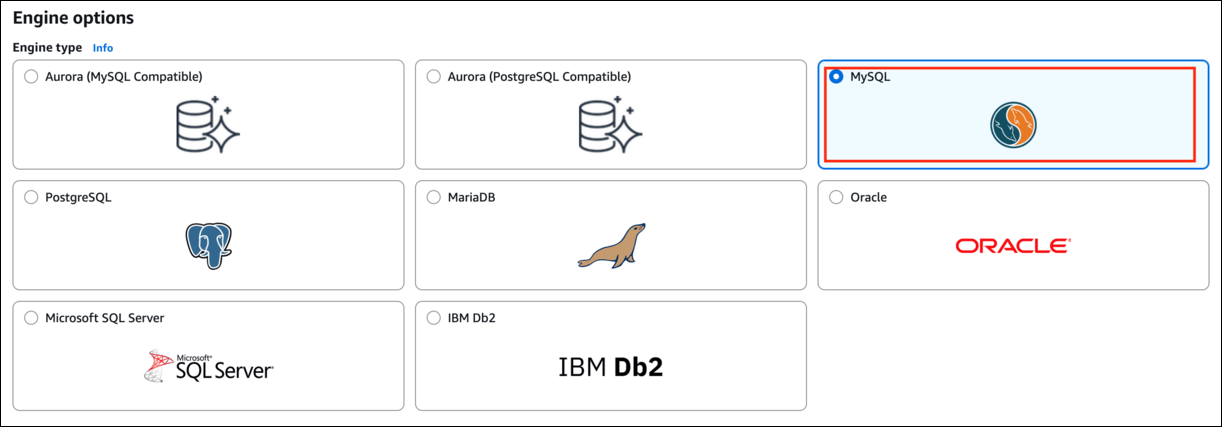
- Edition: Leave it as default
-
Under Templates, select the Sandbox option.
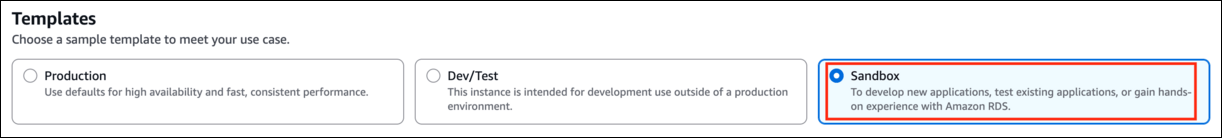
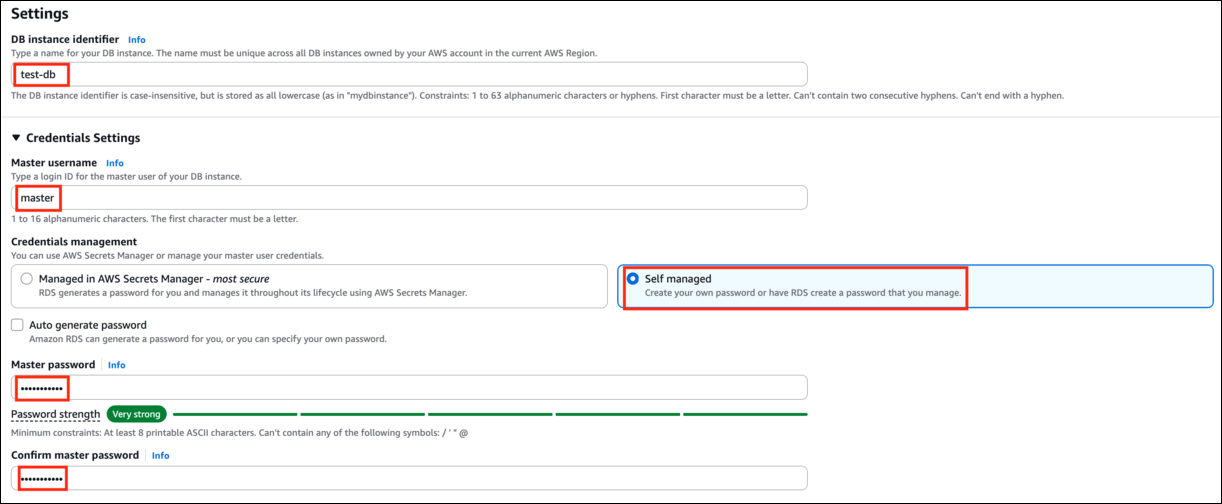
- Under Settings, provide the following details.
- DB cluster identifier: Enter test-db
- Master username: Enter master
- Credentials management: select Self managed
- Master password and Confirm master password: Enter Whizlabs123
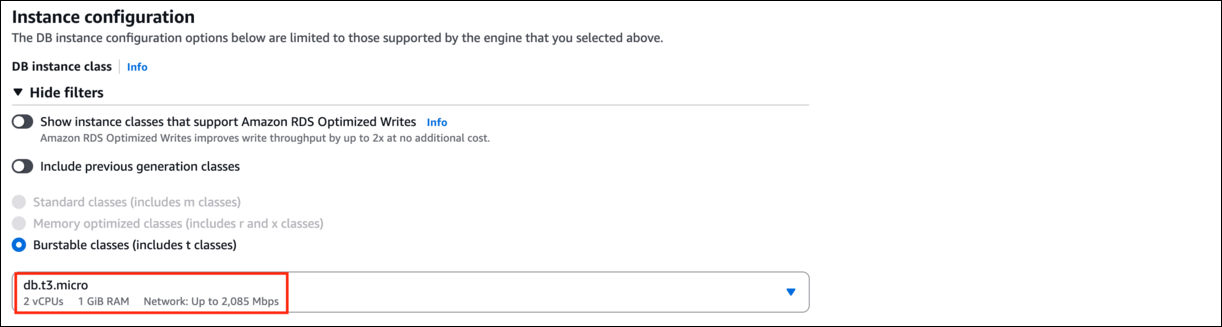
- Under DB instance class, select Burstable classes (includes t classes) and select db.t3.micro
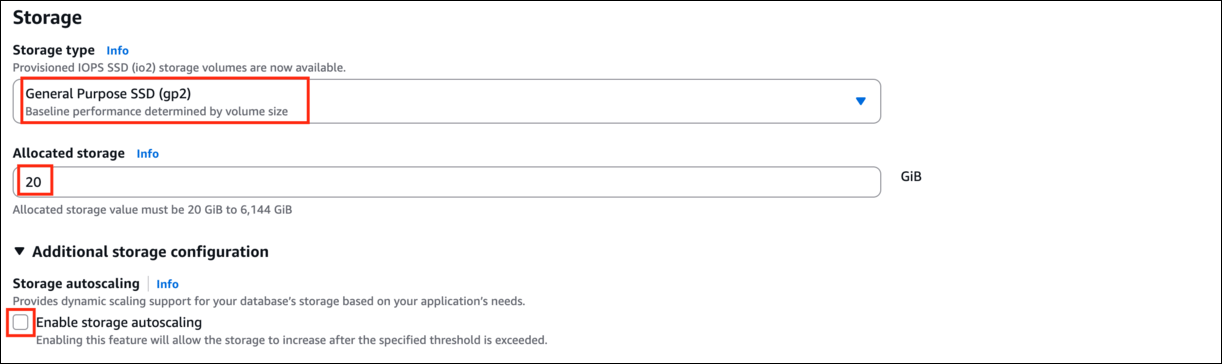
- Storage type : General Purpose (SSD)
- Allocated storage : 20
- Uncheck Enable storage autoscaling.
- Leave the Availability and durability as default.
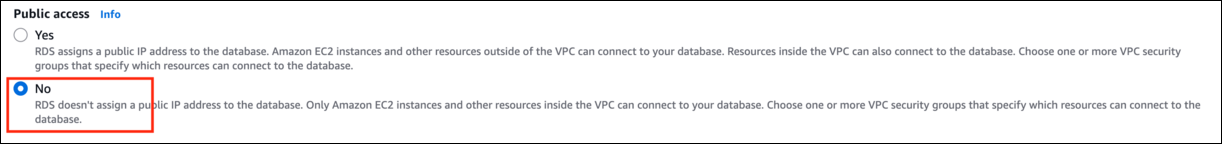
- Under Connectivity, make sure that Public access is No. Leave everything else as default.
- Uncheck Enhanced Monitoring option.
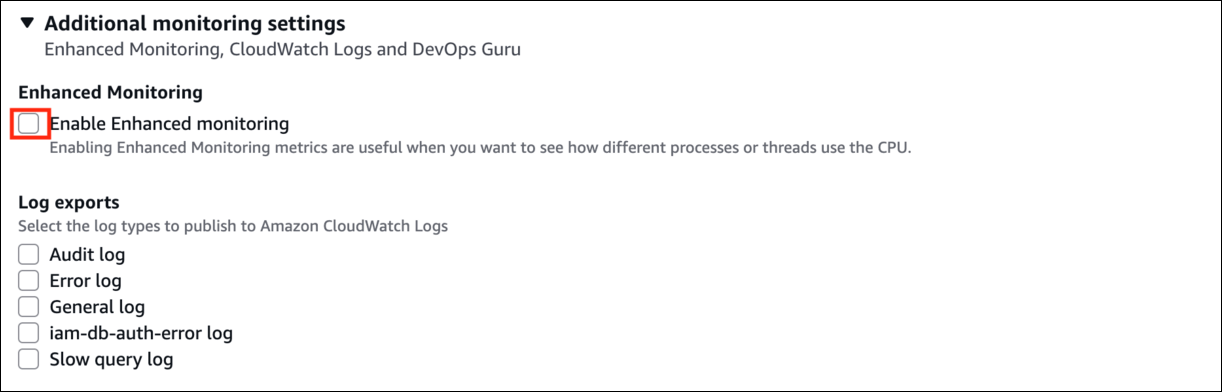
- Expand the Additional configuration.
- Initial database name : Enter projectdb
- Leave DB parameter group and Option group as default.
- Uncheck Enable automatic backups.
- Uncheck Enable encryption option.
- Uncheck Deletion protection.
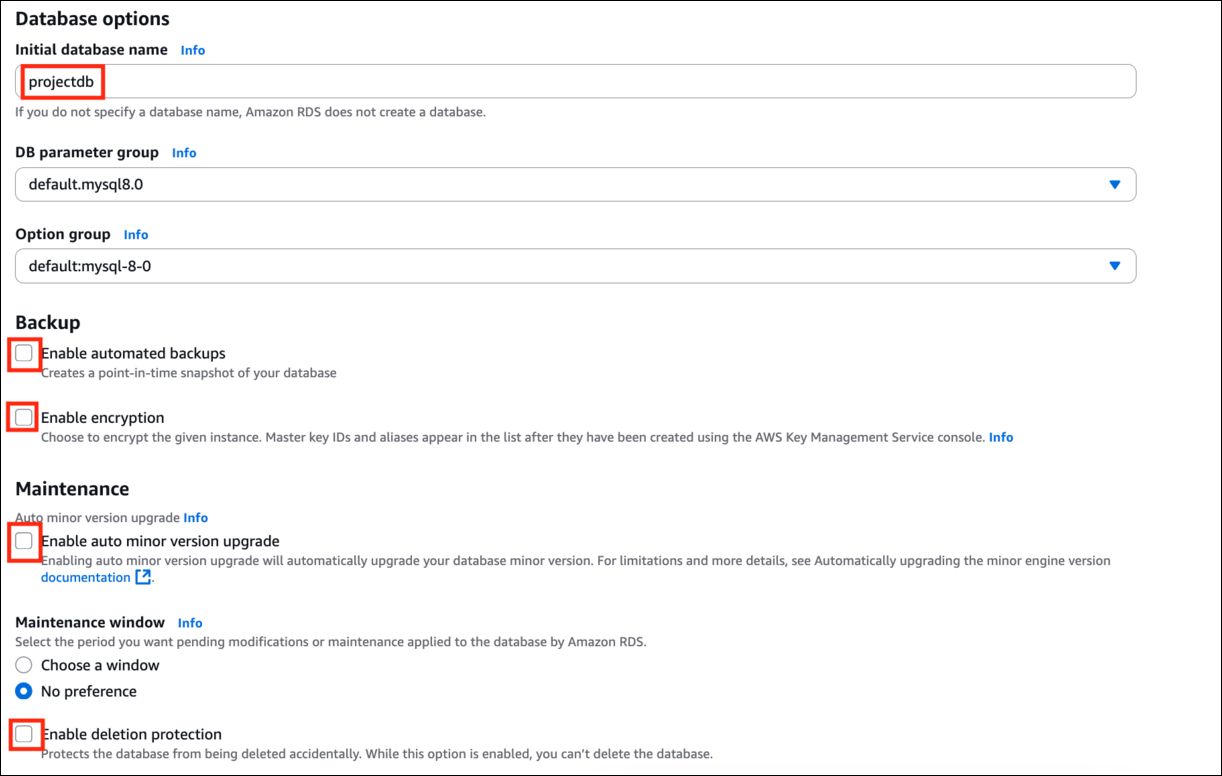
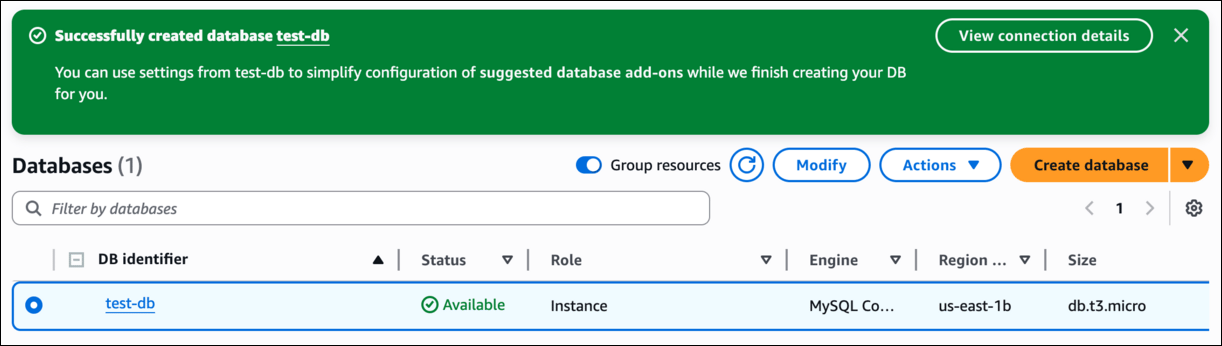
- Click on Create Database to create the database. This process does take time between 5-10 minutes.
- Once the database is created the status changes to Available.
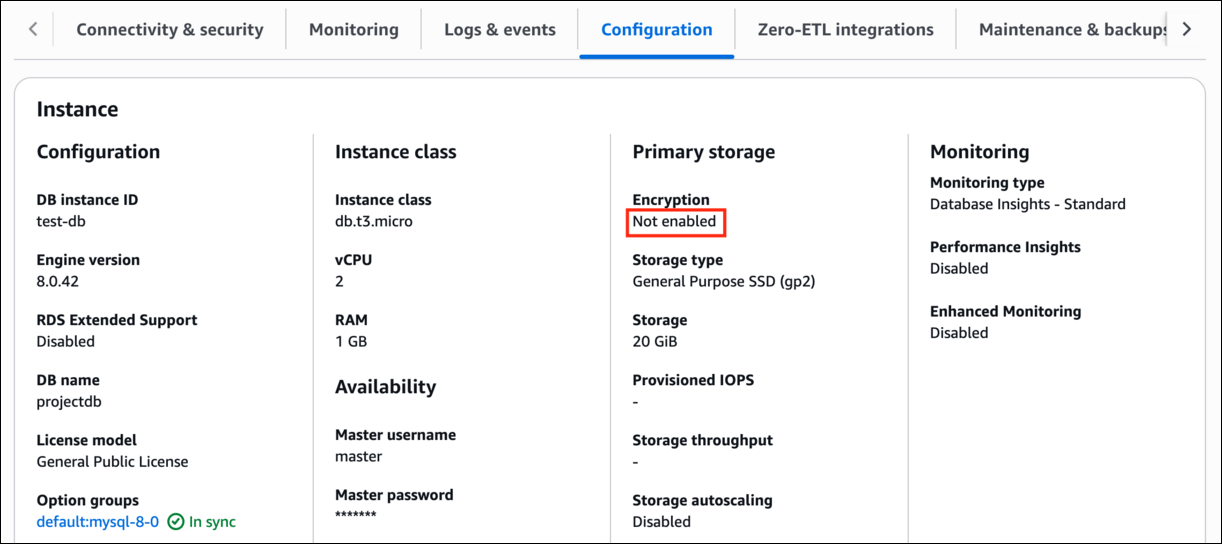
- Click on the database and navigate to the Configuration tab. You can notice that the Encryption is not enabled, as we wanted it to be.
- If we select the database and go to modify it, we will not find an option to Encrypt the database.
Task 3: Take a snapshot from the existing DB Instance
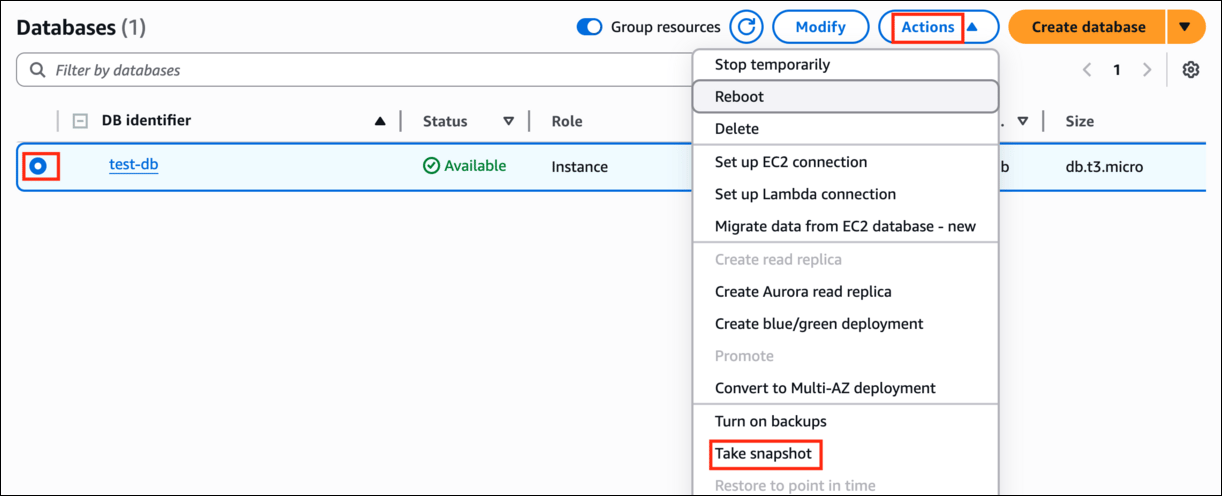
- Select the created DB Instance and click on Actions.
-
Click Take snapshot from the options.
-
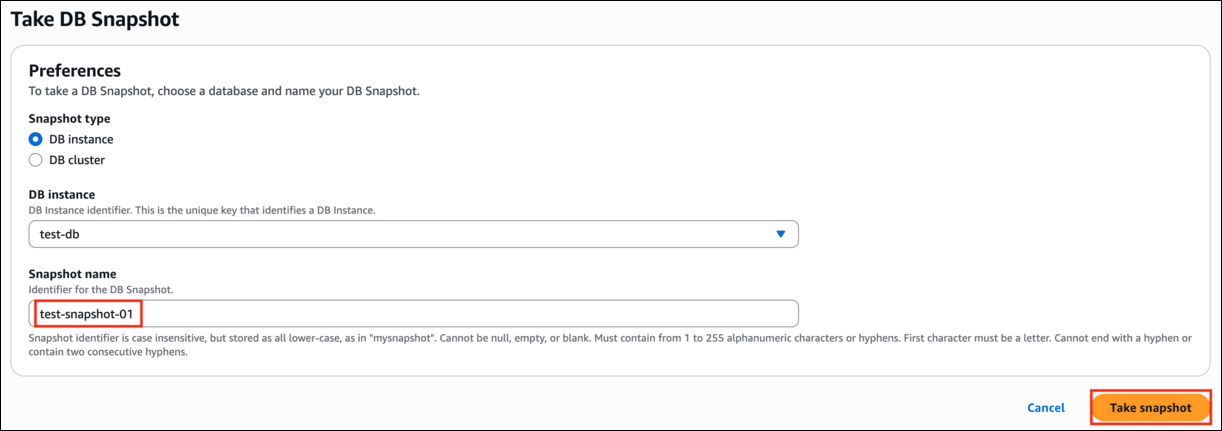
Give a name to the snapshot, test-snapshot-01 and click on the Take snapshot button.
-
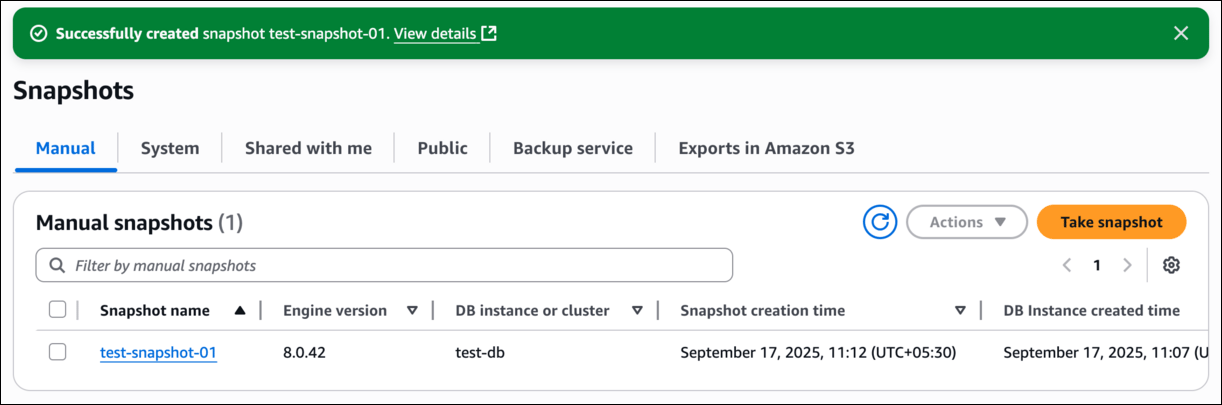
The snapshot creation takes 3-5 minutes. Refresh after some time, the snapshot creation status will be available.
Task 4: Make a copy of the snapshot and encrypt it
- It is not possible to encrypt the snapshot in this stage. We need to encrypt the snapshot while taking a copy of it.
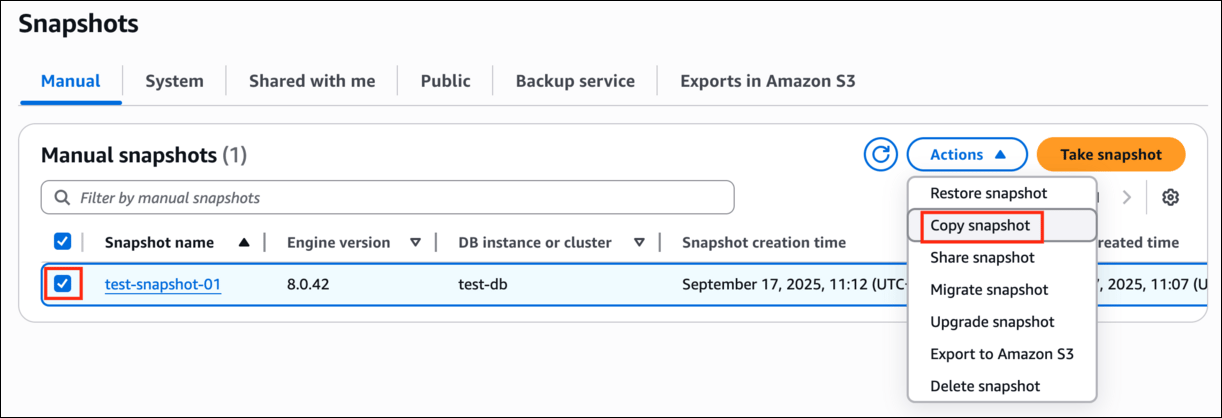
- Under the Manual snapshots, select the created snapshot and click on Actions.
-
Click Copy snapshot from the options.
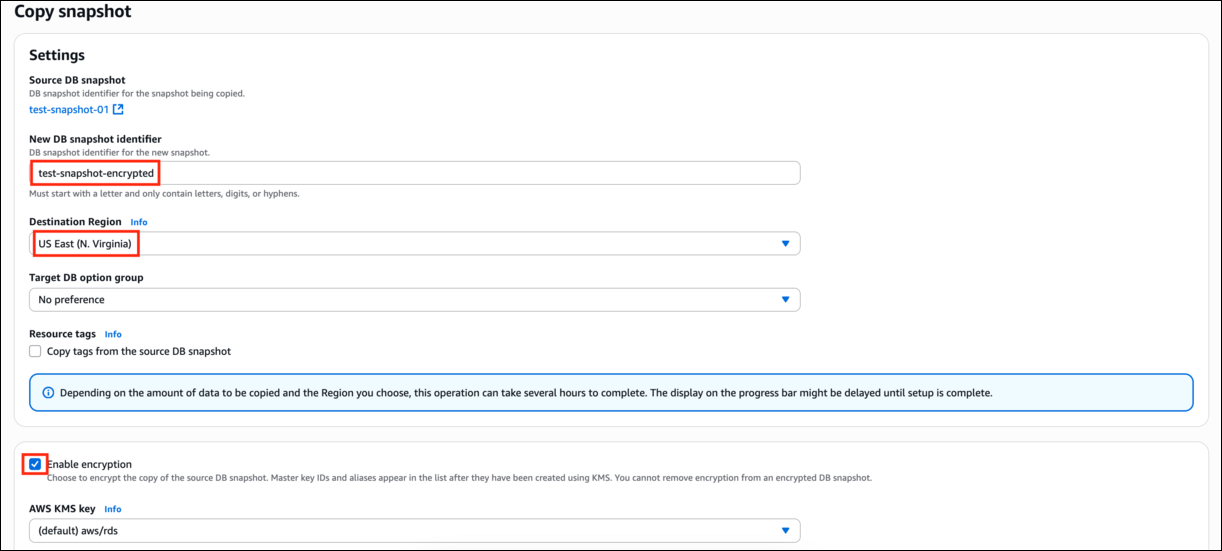
- Under settings, provide the following details.
- New DB Snapshot Identifier: Enter test-snapshot-encrypted
- Destination Region: Select US East (N.Virginia)
- Under Encryption, check Enable Encryption. Leave the master key as default.(IMPORTANT)
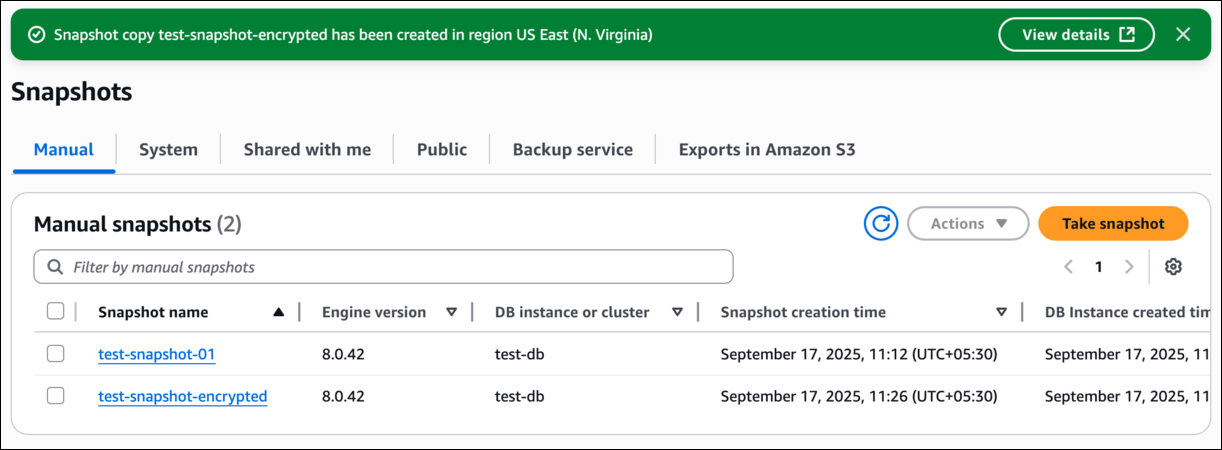
- Click on the Copy snapshot button. The snapshot will be created within 3 - 5 minutes.
Task 5: Restore DB Instance from the encrypted snapshot
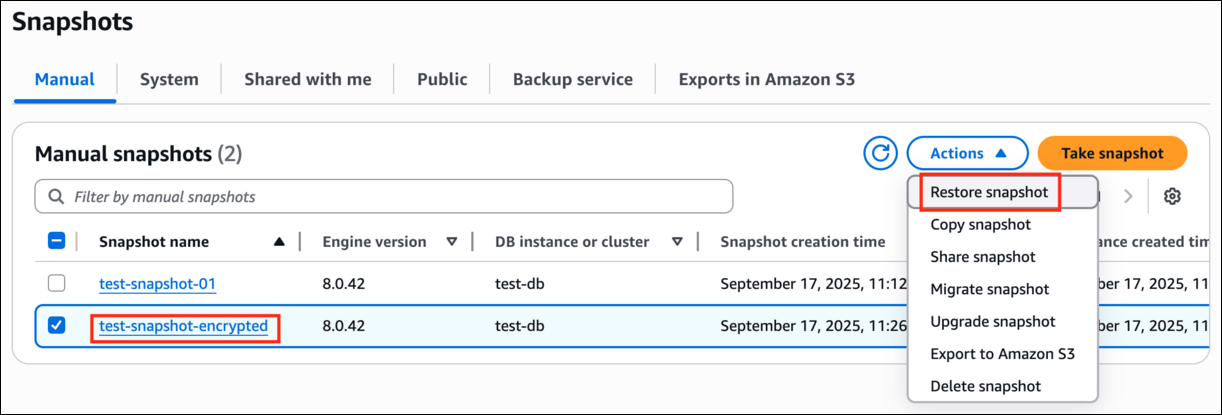
- Click on the encrypted snapshot and click on Actions.
-
Click on Restore snapshot from the options.
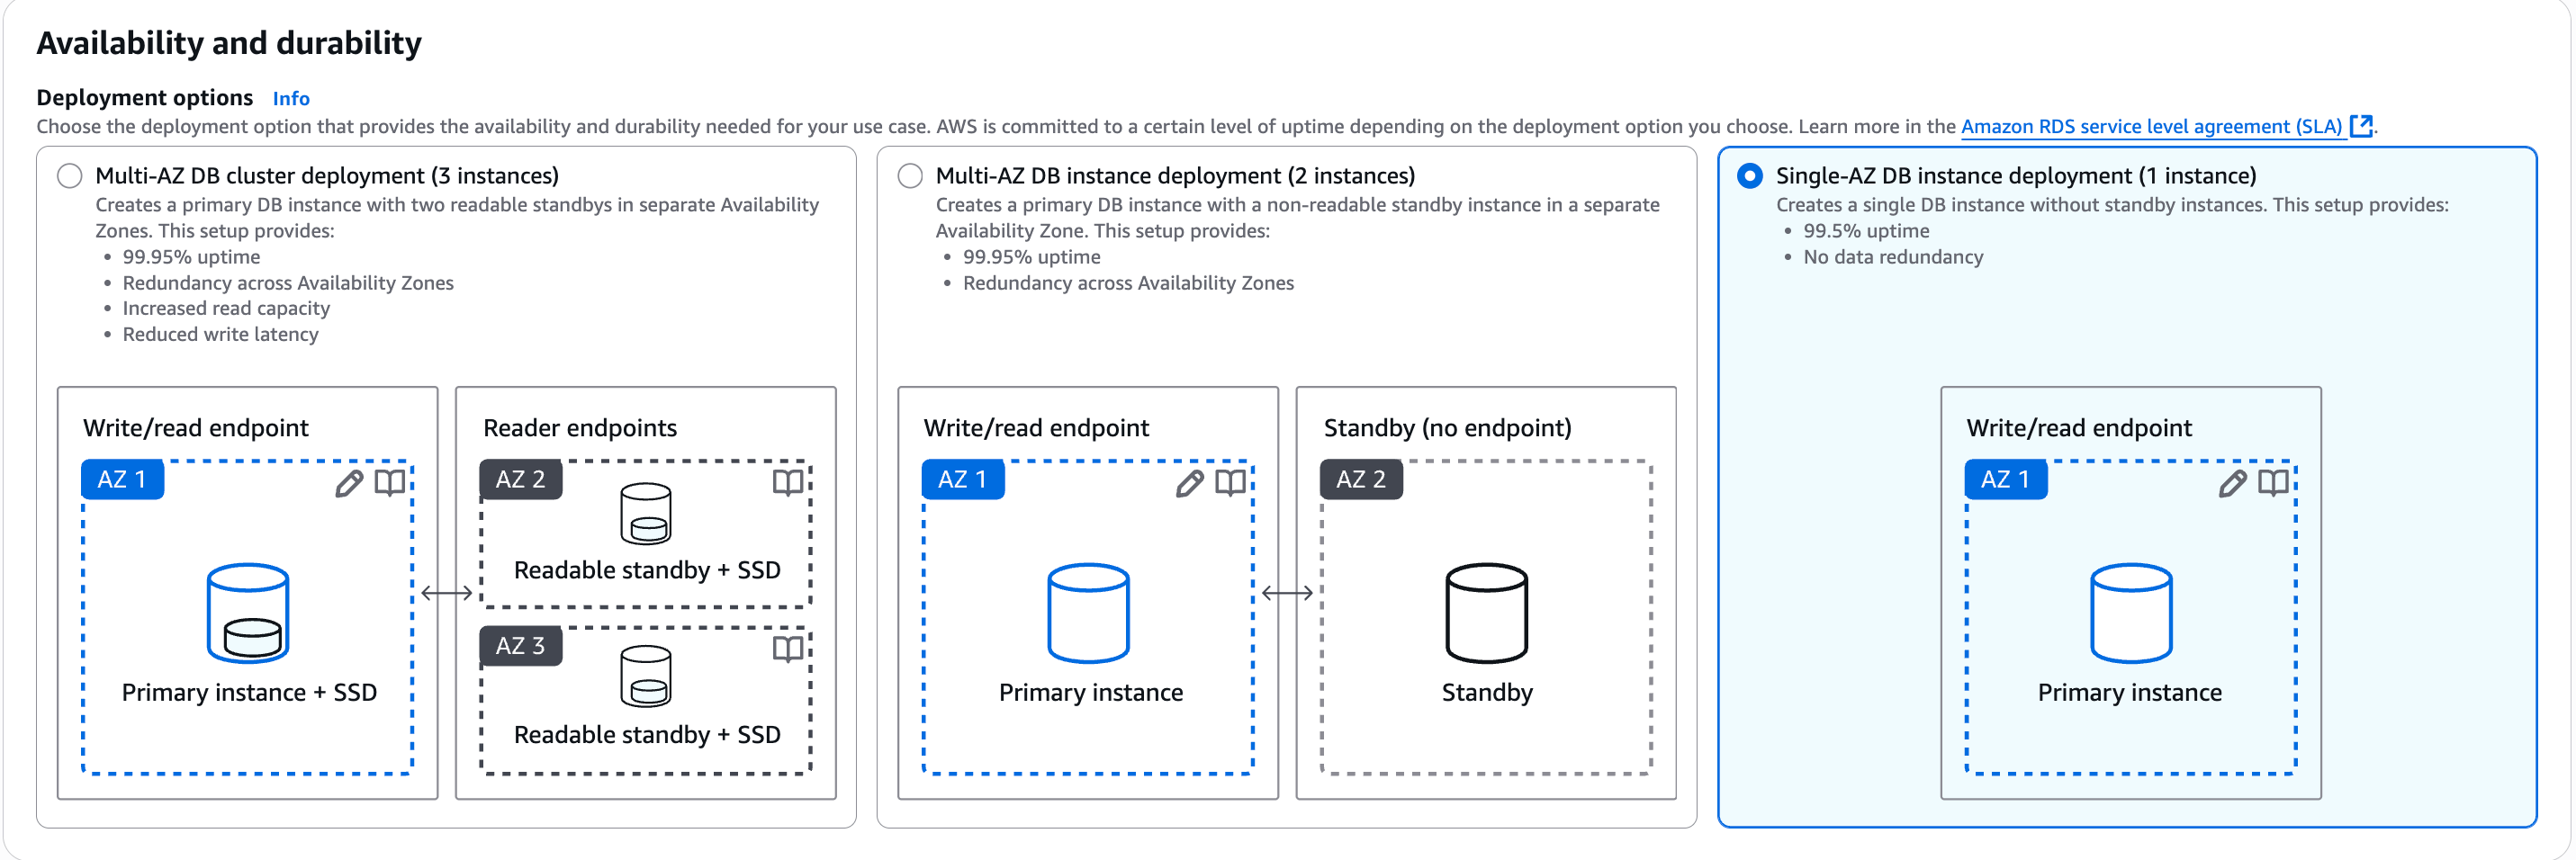
- Under Availability and Durability select Single DB Instance zone
- Settings, enter the name of DB Instance as test-db-encrypted.
- Make the other settings exactly as the original DB Instance.
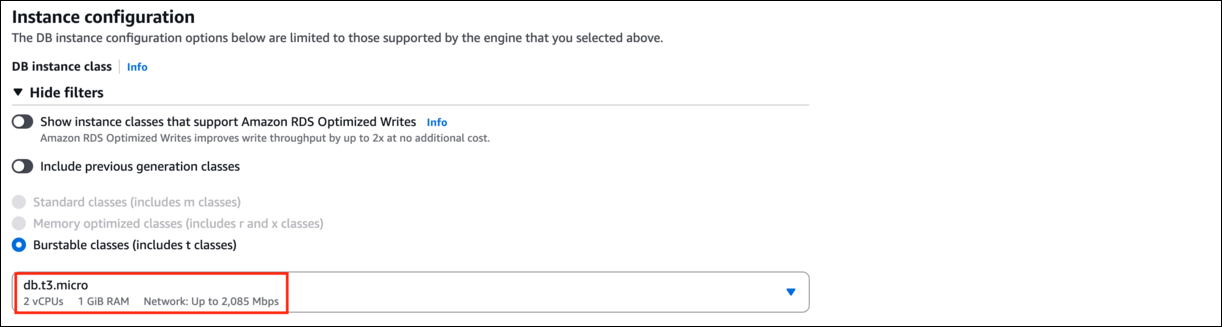
- Under the DB instance class, select Burstable classes (including t classes) and select db.t3.micro
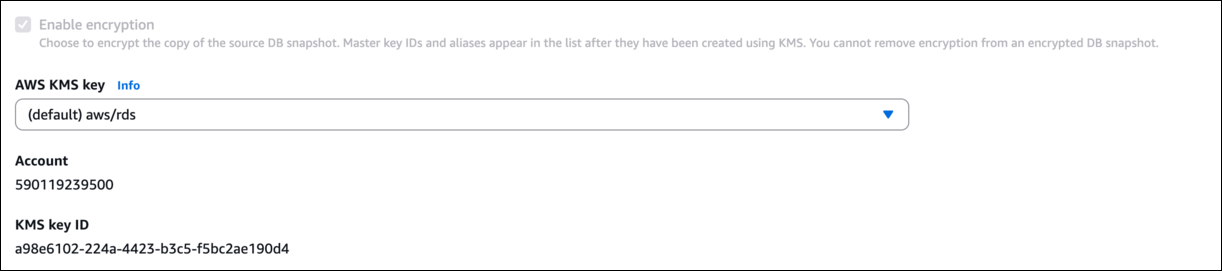
- Under Encryption, you can see the Enable Encryption is enabled and cannot make changes since the snapshot is encrypted.
- Leave DB parameter group and Option group as default.
- Click on Restore DB Instance button. The database creation takes around 5-10 minutes.
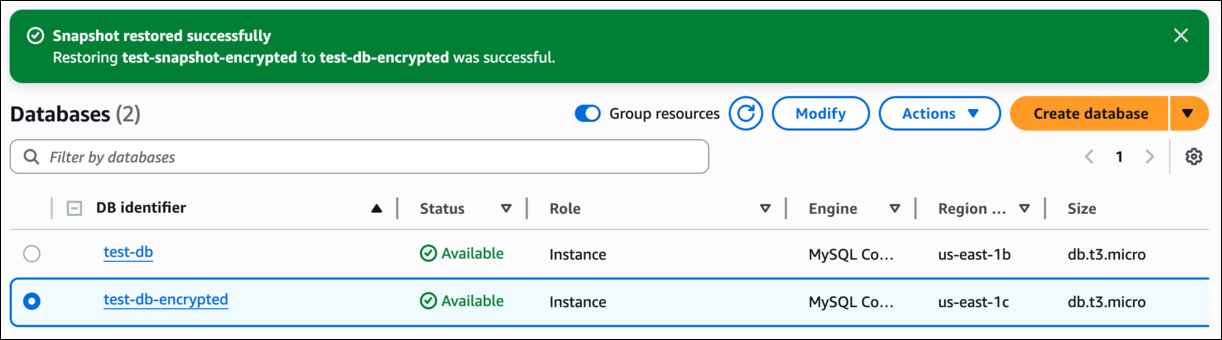
Task 6: Change the name of the original DB Instance
- We have to make sure that the Endpoint of the restored DB Instance should be the same as the original DB Instance.
- To do so, we have to change the names of the DB Instances as the names are unique.
-
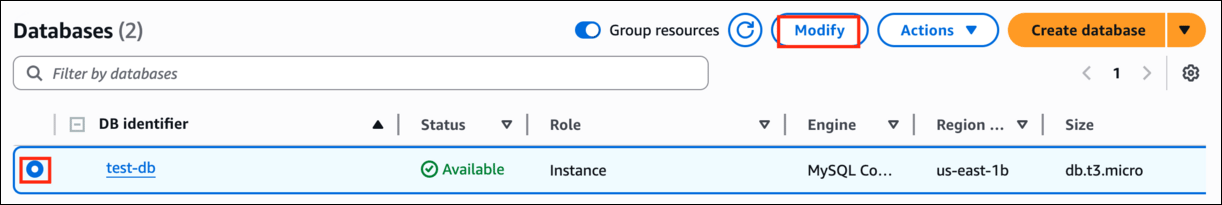
Select the original DB Instance and click on Modify.
-
Change the DB Instance Identifier to test-db-unencrypted.
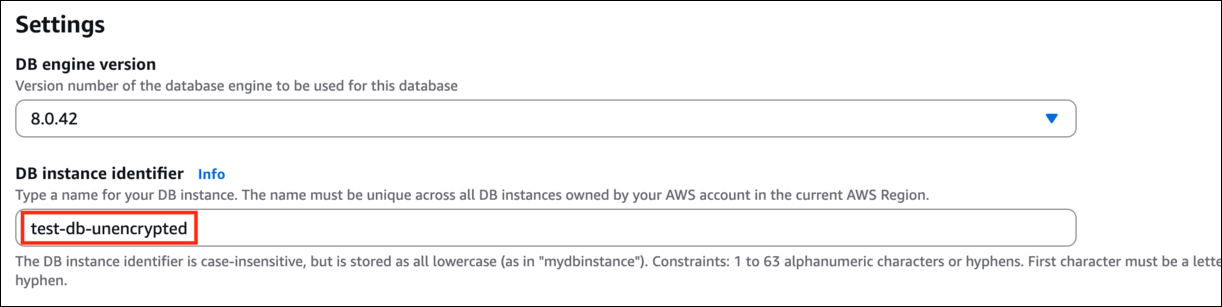
- Leave everything as default and click on Continue.
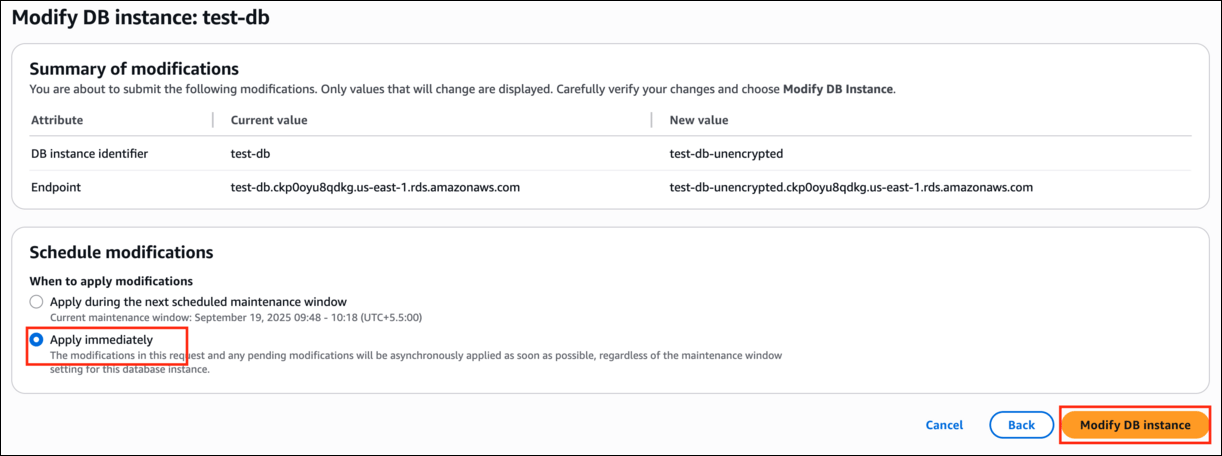
- Verify the new values of the DB Instance Identifier and the Endpoint.
-
Under Scheduling of modifications, select Apply Immediately and click on Modify DB Instance button.
-
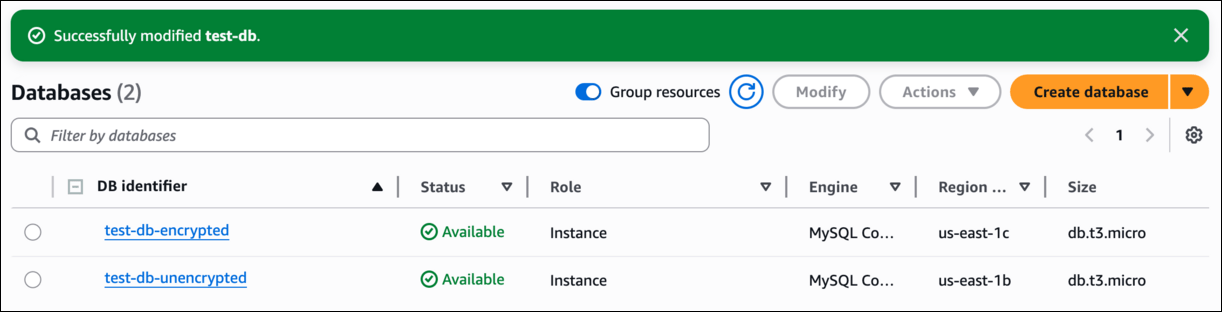
It might take some time to reboot the DB Instance. Press ctrl+R if you are not able to see the changes.
Task 7: Change the name of the Restored DB Instance to the original DB Instance name
-
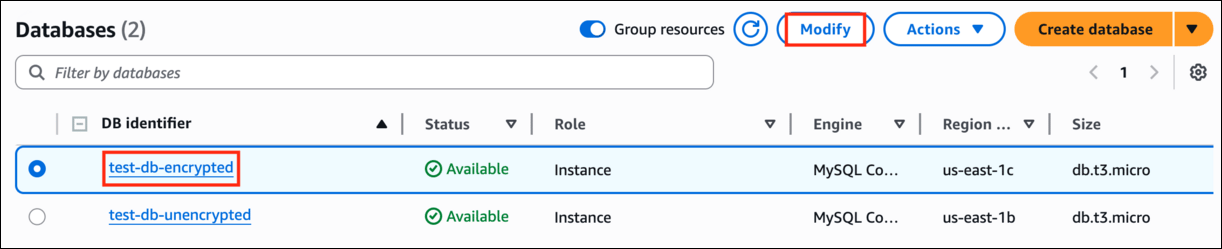
Select on the restored database and click on Modify.
-
Change the DB Instance Identifier to test-db.
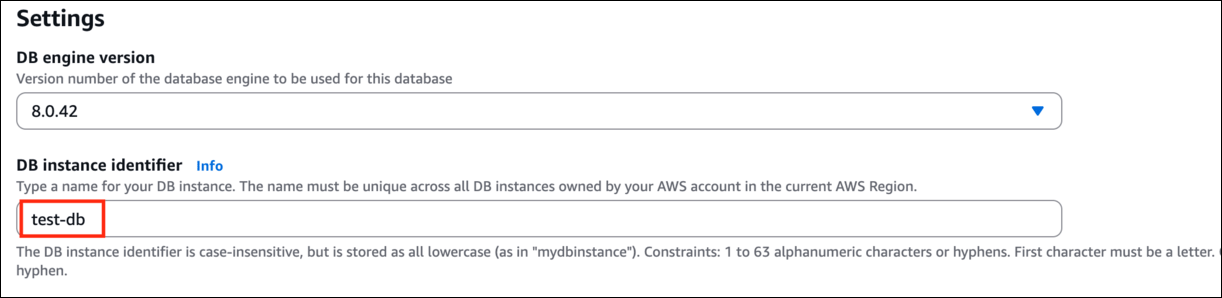
- Leave everything as default and click on Continue.
- Verify the new values of the DB Instance Identifier and the Endpoint.
-
Under Scheduling of modifications, select Apply Immediately and click on Modify DB Instance button.
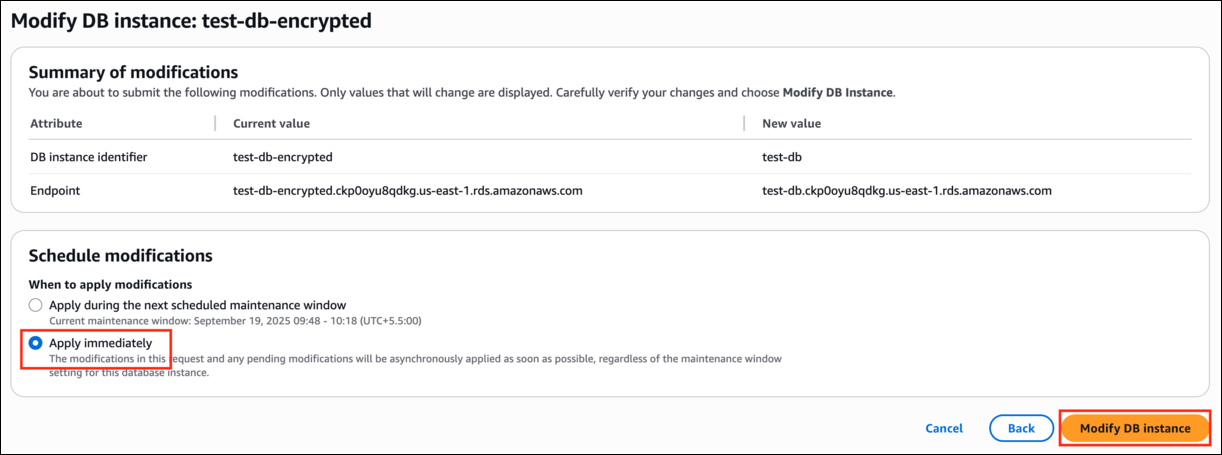
-
It might take some time to reboot the DB Instance. Press ctrl+R if you are not able to see the changes.
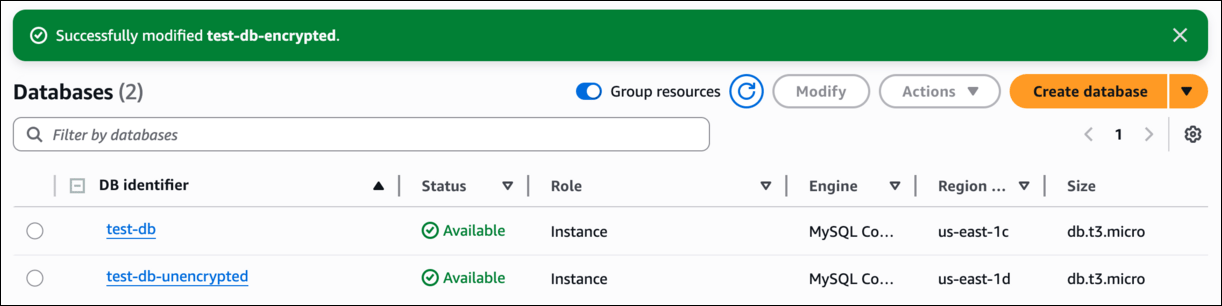
- Once the database is modified, click and open test-db i.e, the encrypted DB Instance.
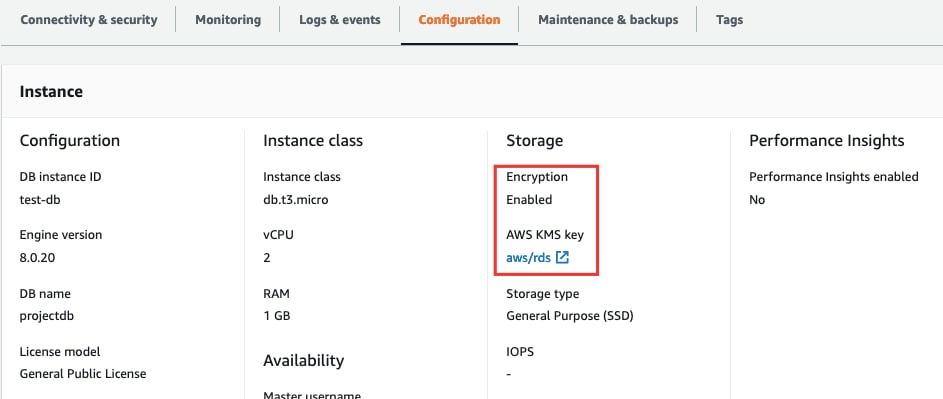
- Click on the database and navigate to the Configuration tab. You can notice that the Encryption is enabled.
Task 8: Delete the unencrypted RDS DB Instance and snapshot
- Since we have the encrypted DB Instance, we shall delete the unencrypted DB Instance and the snapshot associated.
- Click on Databases present to the left of the screen.
-
Select the Unencrypted DB Instance (i.e test-db-unencrypted) and click on Actions.
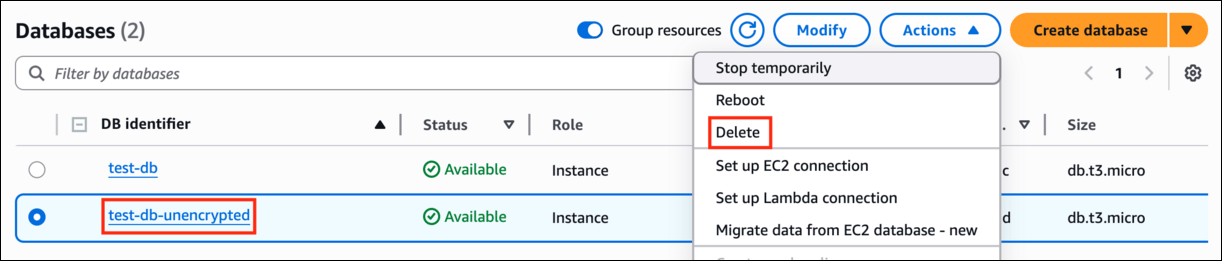
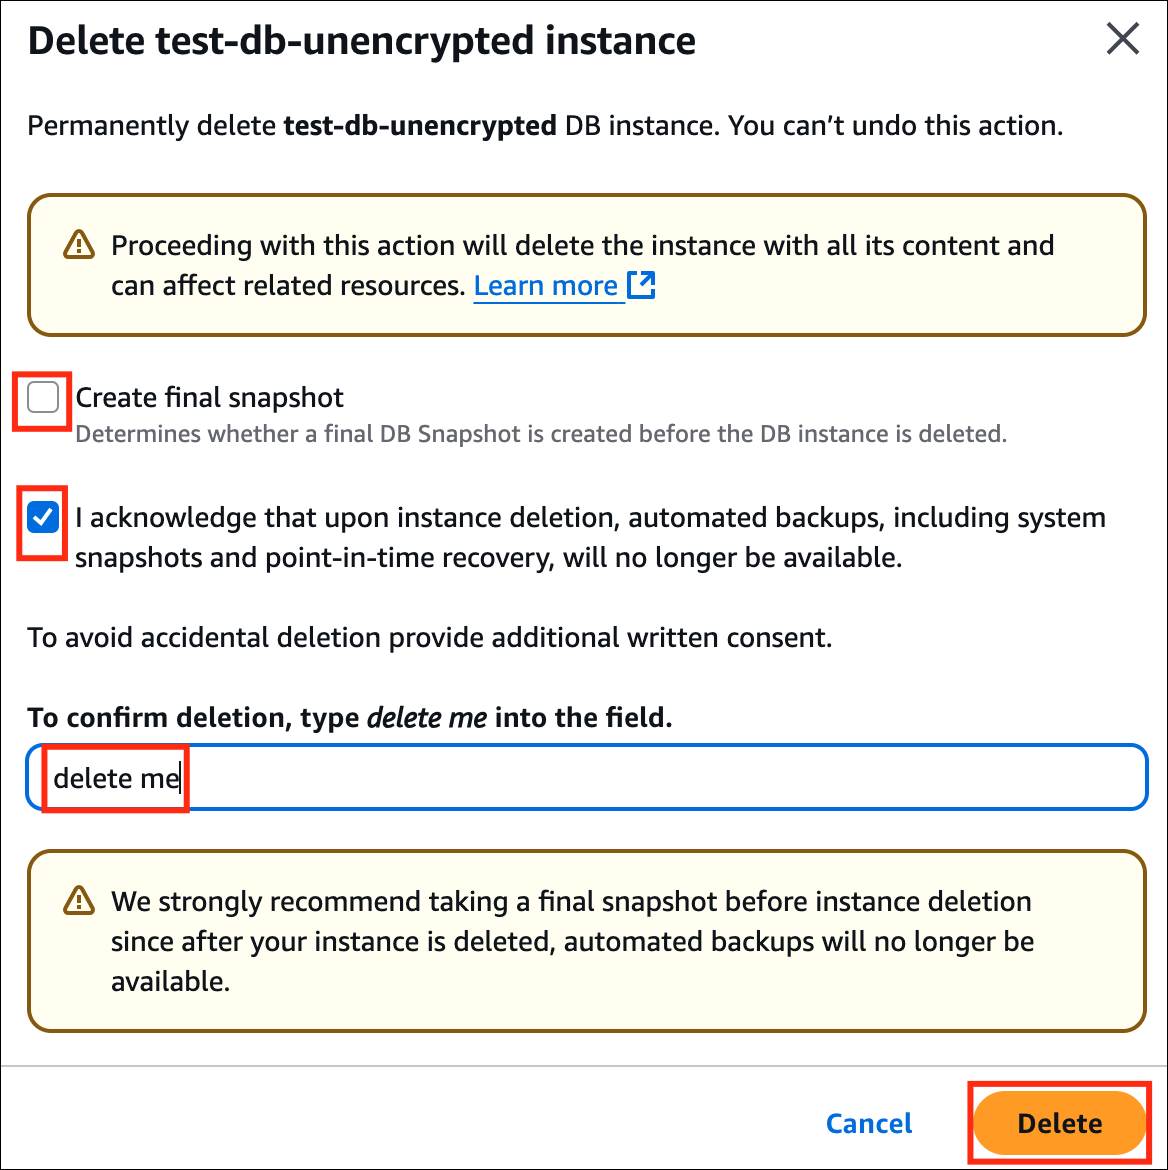
- Click on the Delete option.
- Uncheck the Create final snapshot option.
- Check the Acknowledge box.
-
Confirm the deletion by entering delete me and click on delete.
- Click on the Snapshots on the left of your screen.
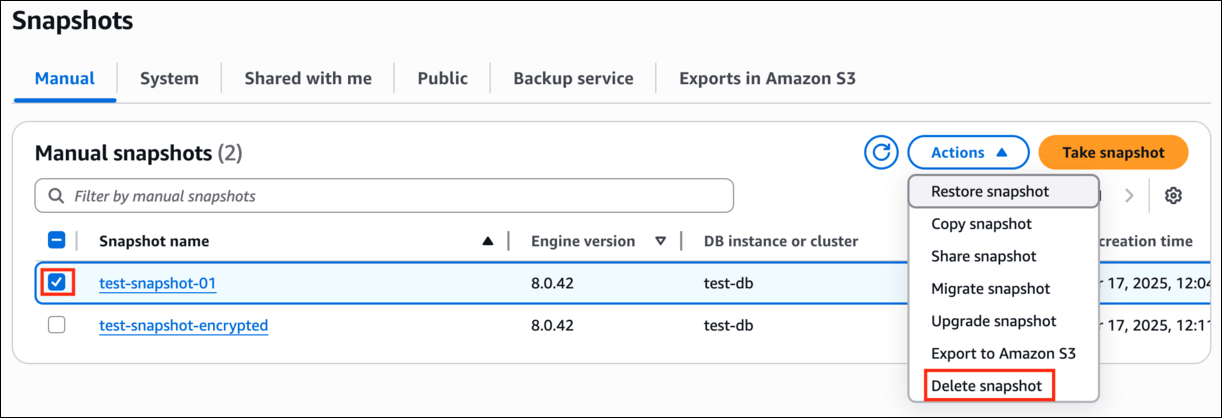
- Under Manual snapshots, select the unencrypted snapshot (i.e. test-snapshot-01) and click on Actions.
- Click on the Delete snapshot option.
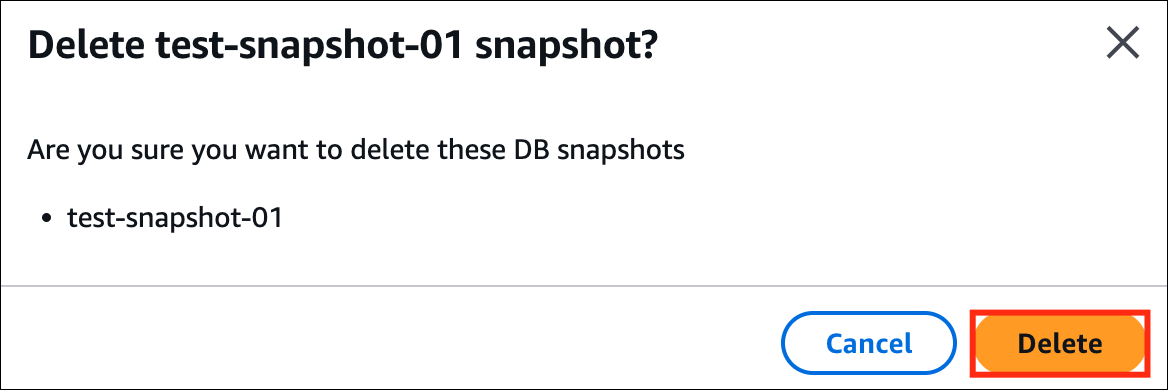
- Confirm by clicking on the Delete button.
- In this way, you can encrypt an unencrypted RDS DB Instance.
- Wait till both resources are completely deleted. This step is to avoid confusion in the validation report.
Do you know?
Database encryption is a critical component of a comprehensive security strategy. It helps protect data from unauthorized access, complies with regulatory requirements, mitigates the impact of data breaches, enhances cloud security, builds trust with customers, and mitigates insider threats.
- Once the lab steps are completed, please click on the Validation button on the right-side panel.
Task 9: Delete AWS Resources
Deleting the DB Instance
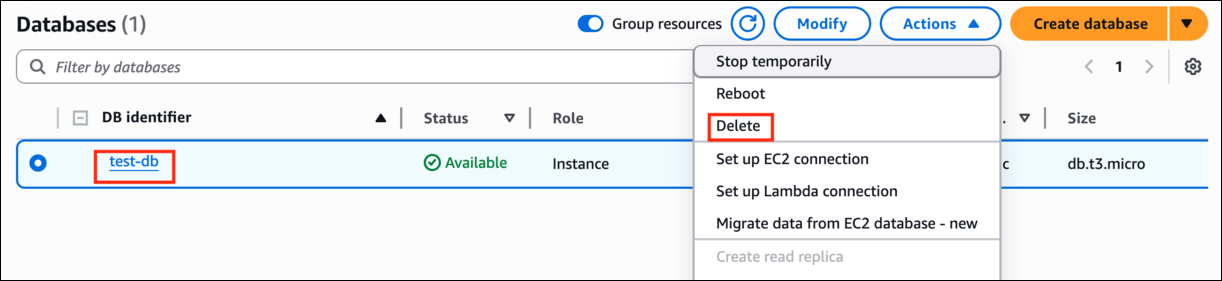
- Click on Databases present to the left of the screen.
- Select the DB Instance and click on Actions.
-
Click on the Delete option.
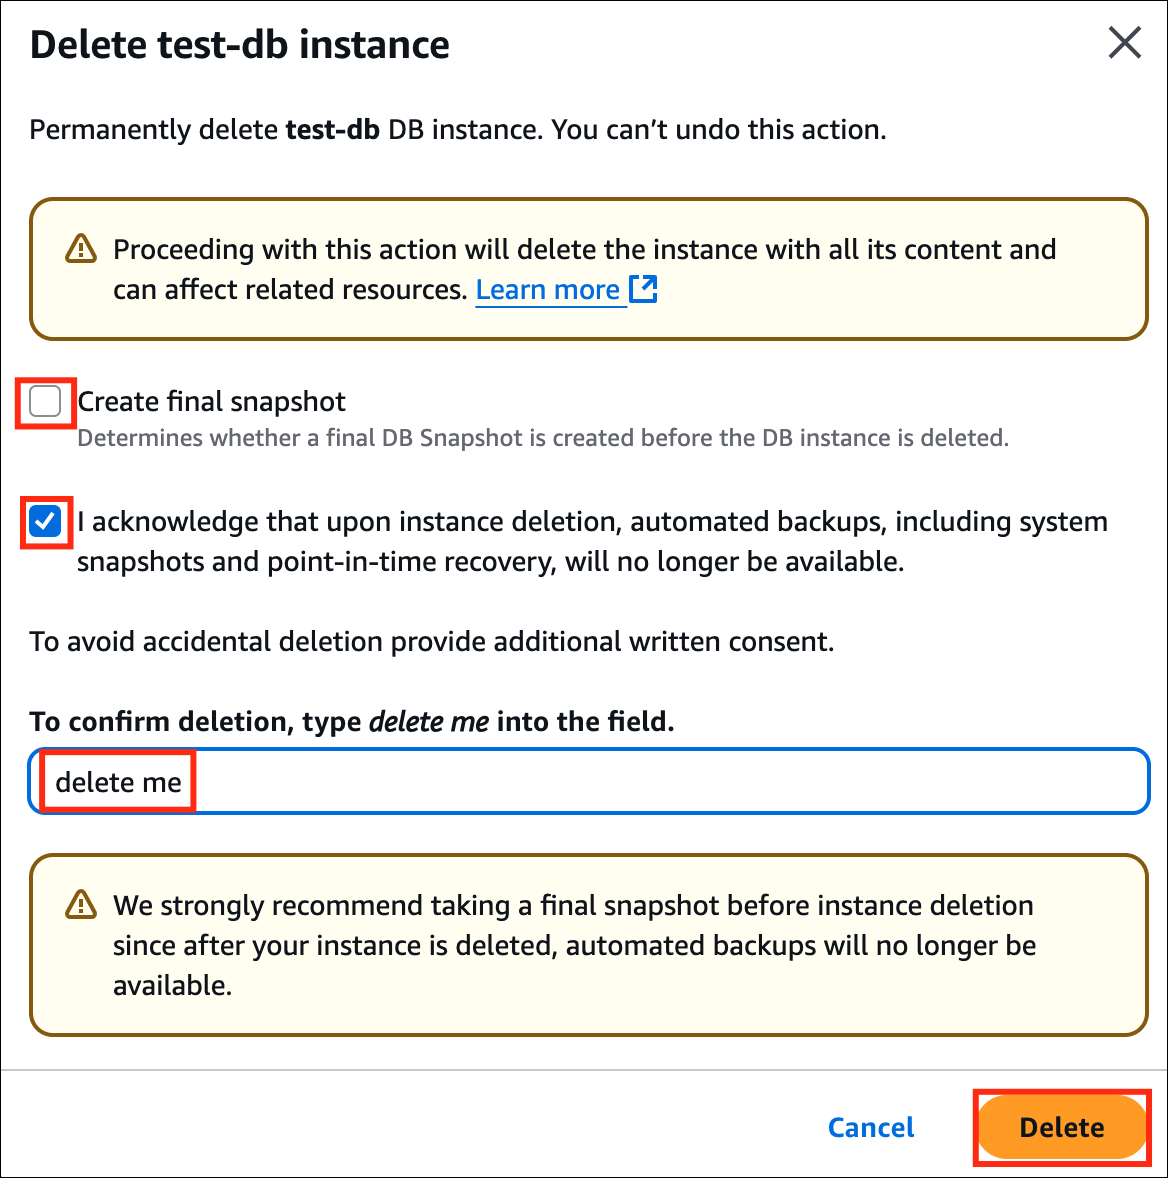
- Uncheck the Create final snapshot option.
- Check the Acknowledge box.
-
Confirm the deletion by entering delete me and click on delete.
- The status changes to Deleting and the DB Instance gets deleted.
- You can proceed to further steps even if it is in a deleting state.
Deleting the Snapshot
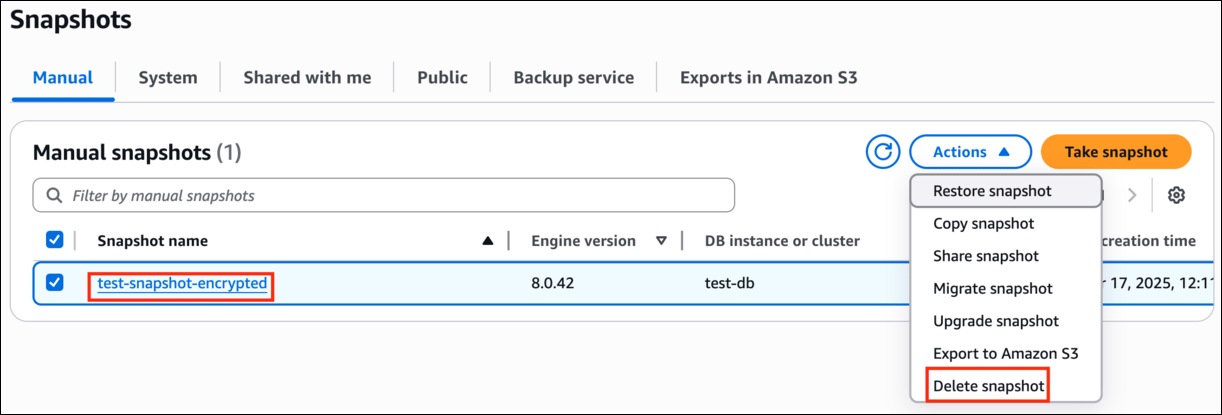
- Click on the Snapshots on the left of your screen. Under Manual snapshots, select the unencrypted snapshot and click on Actions.
-
Click on the Delete Snapshot option.
-
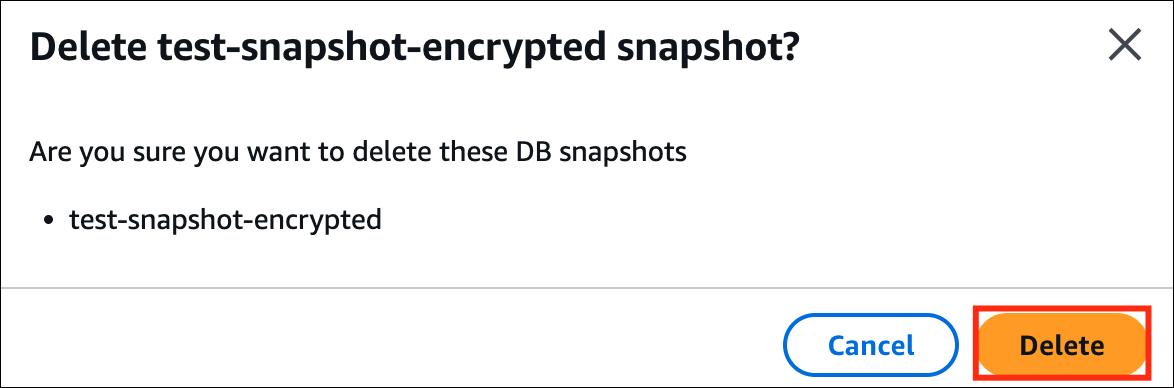
Confirm by clicking on the Delete button.
Completion and Conclusion
- You have created an unencrypted Amazon RDS DB Instance.
- You have taken the snapshot of the DB Instance.
- You have made a copy of the snapshot and encrypted it.
- You have restored the DB Instance with the copied snapshot.
- You have changed the names of the original and restored DB instances.
- You have made sure that the Endpoint of the restored database is the same as the originally created DB Instance.
- You have deleted the Unencrypted DB Instance and snapshot.
End Lab
- Sign out of AWS Management Console.
- You have successfully completed the lab.
- Once you have completed the steps, click on End Lab from your IP Lab Portal and wait till the process gets completed.
What gets checked
When you press Check my work, the platform verifies each of these:- Launch RDS instance — Check whether an RDS Instance is created or not
- Create RDS Snapshot — Check whether an RDS Snapshot is created or not.